

objection
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
android-securitydynamic-analysis-sandboxingexploitation+9
9.5k
sensepost/objectionFrida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 the404hacking/androrat
AndroRAT | Remote Administrator Tool for Android OS Hacking
 nfcgate/nfcgate
An NFC research toolkit application for Android
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 0x1ca3/adbnet
A tool that allows you to search for vulnerable android devices across the world and exploit them.
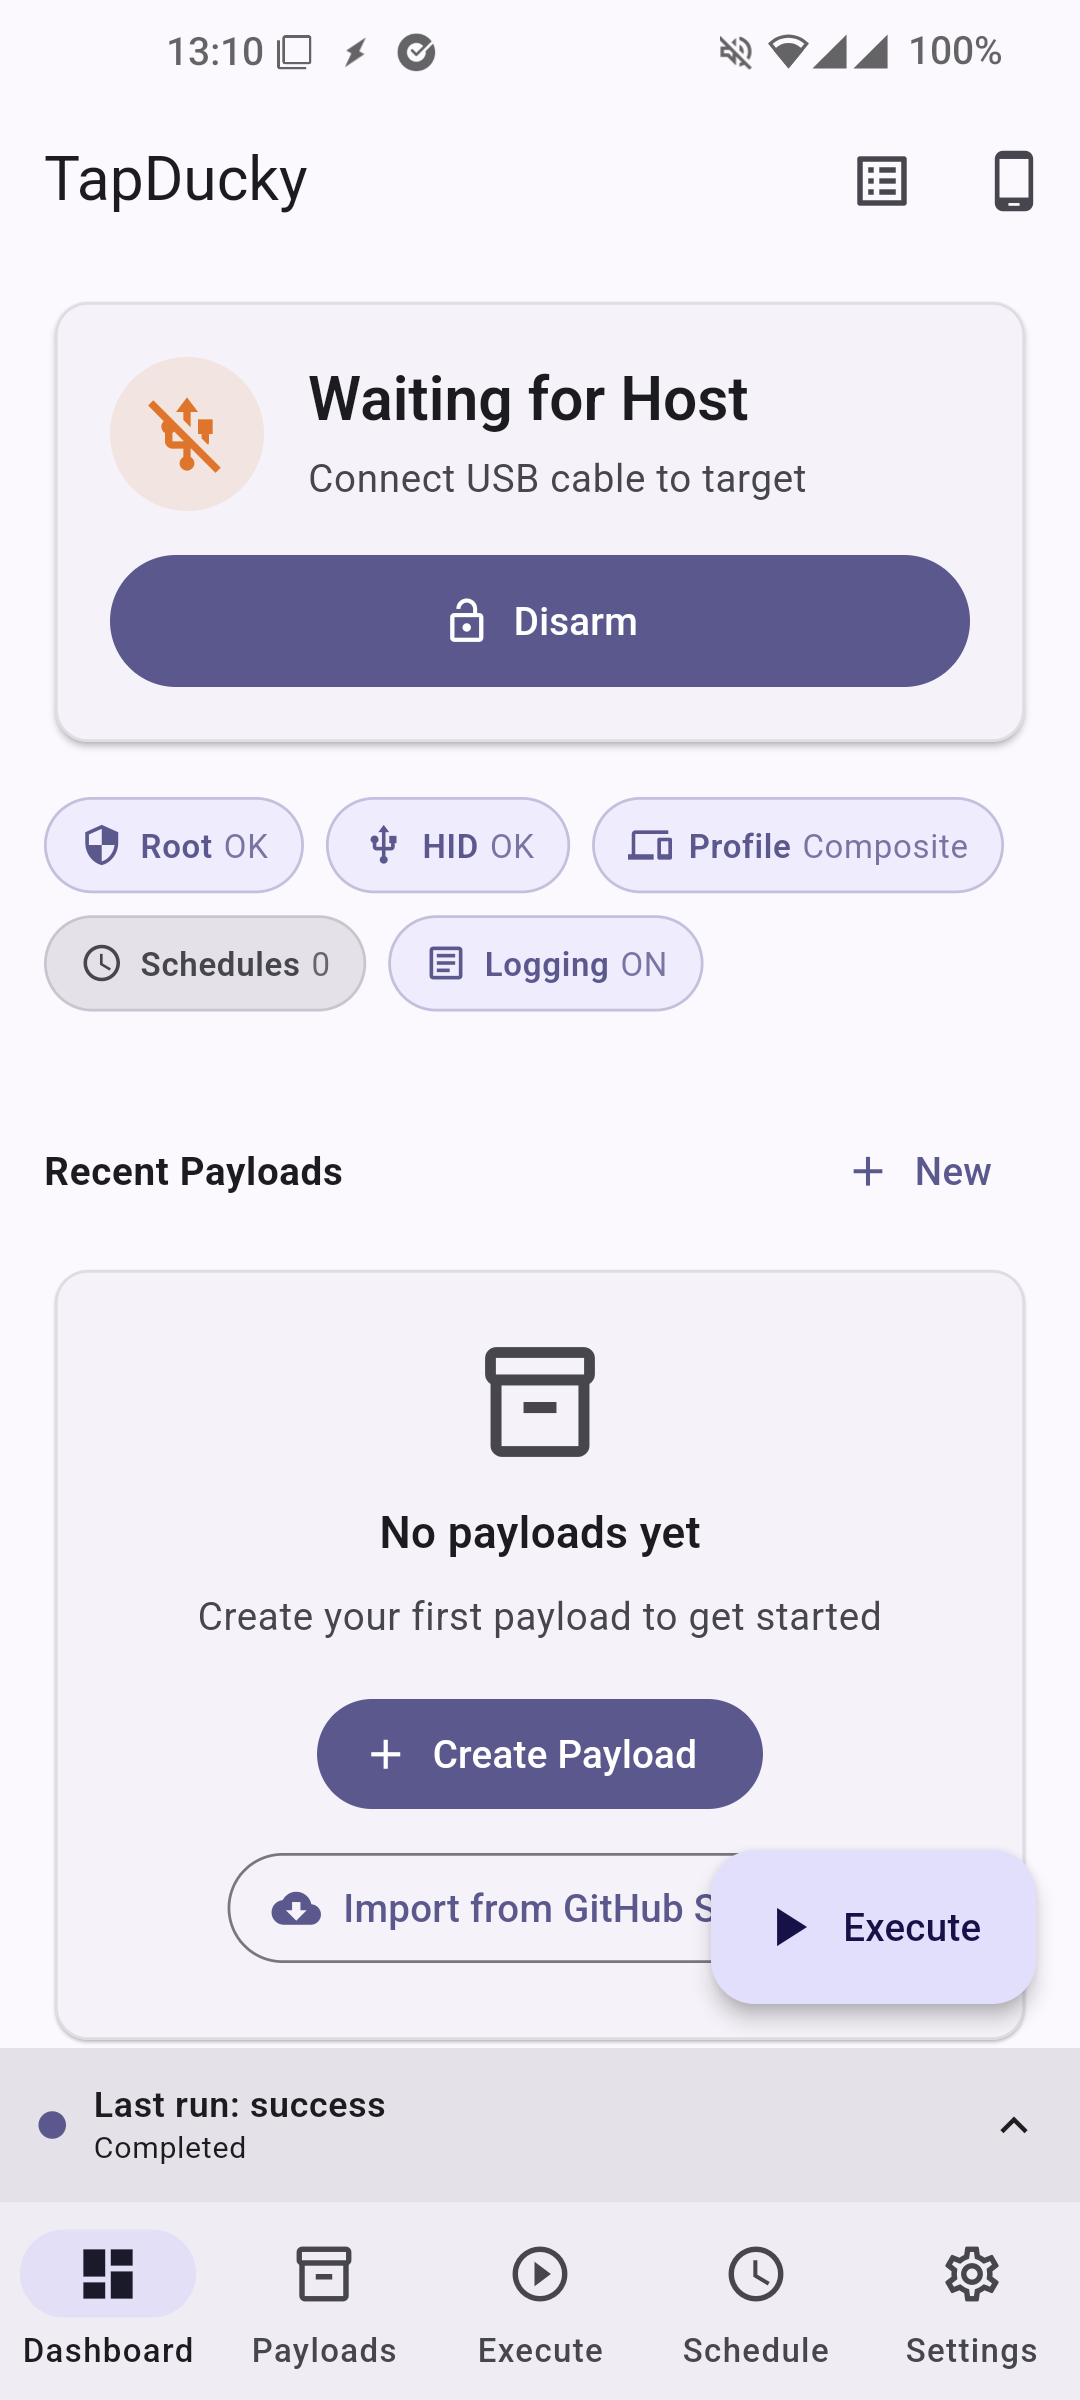 iodn/tap-ducky
Turns any rooted phone into the legendary USB Rubber Ducky. Android USB HID Keystroke Injector
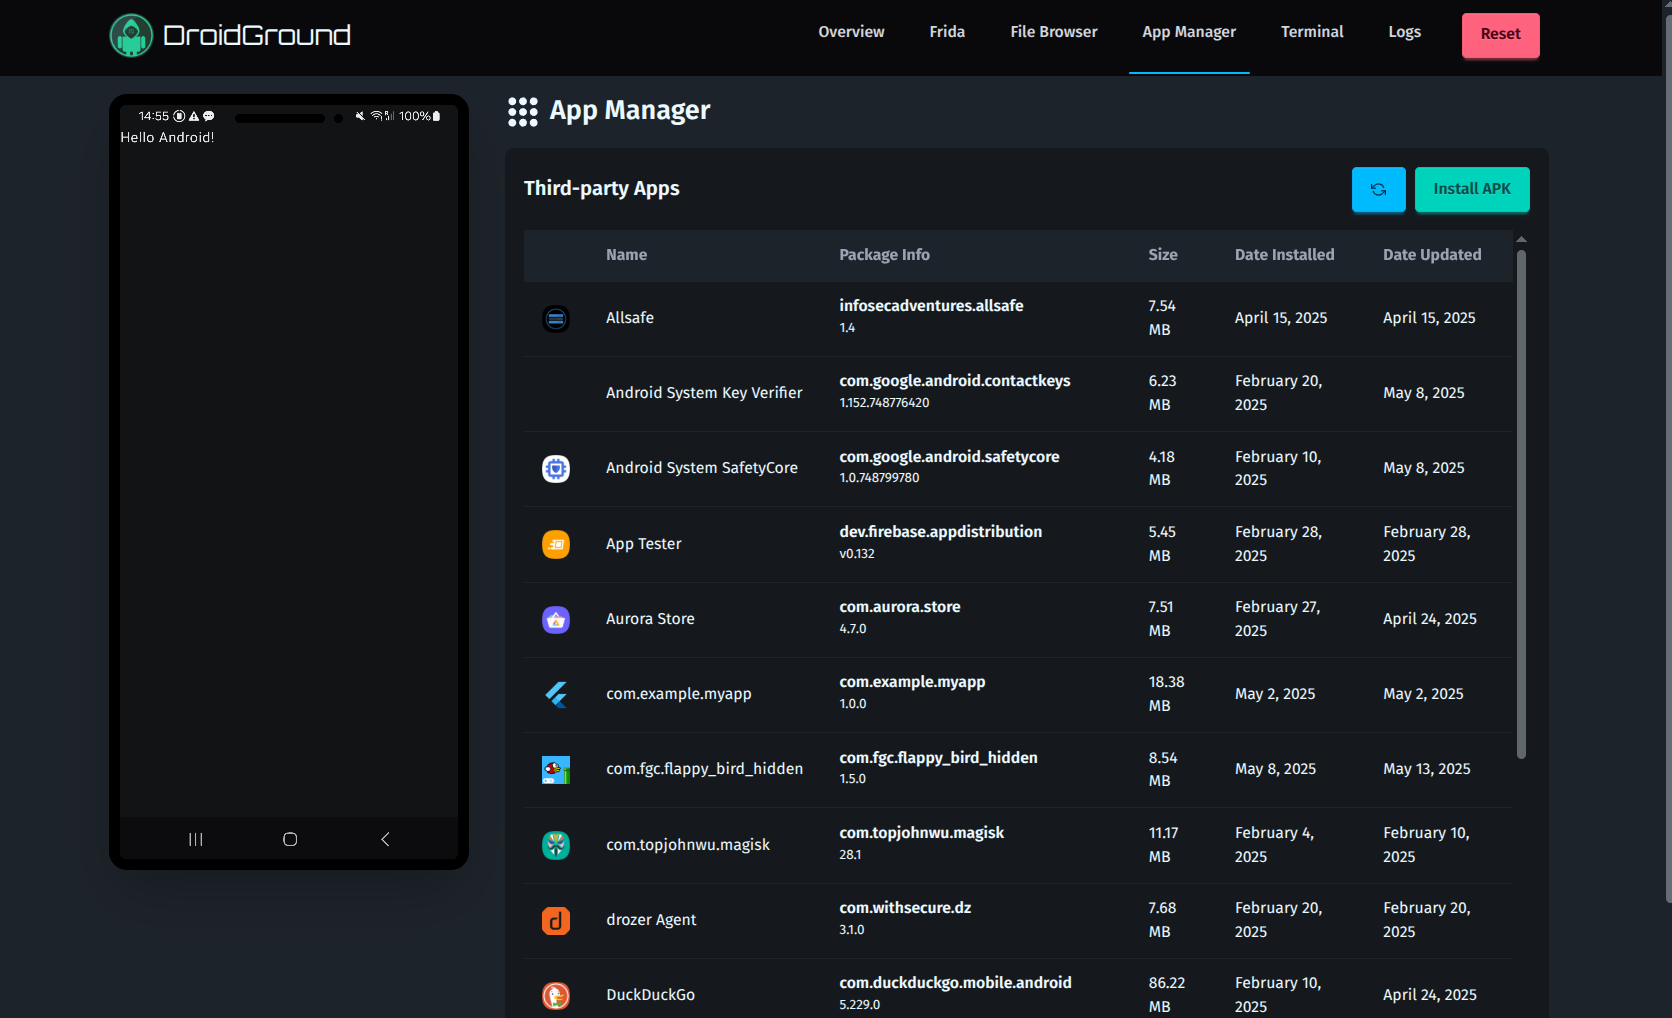 secforce/droidground
A flexible playground for Android CTF challenges.
 quarkslab/cve-2020-0069_poc
Proof-of-concept exploit for CVE-2020-0069 on Mediatek Android devices, enabling kernel memory read/write and syscall hooking for privilege…
 gmh5225/androiddrivesignity
AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
 wtrwx/smt878u-ionstack-poc
UNFINISHED/WIP - CVE-2026-43499 (IonStack/GhostLock) research POC for Samsung SM-T878U / gts7l. Trigger + geometry verified, NO working root yet.
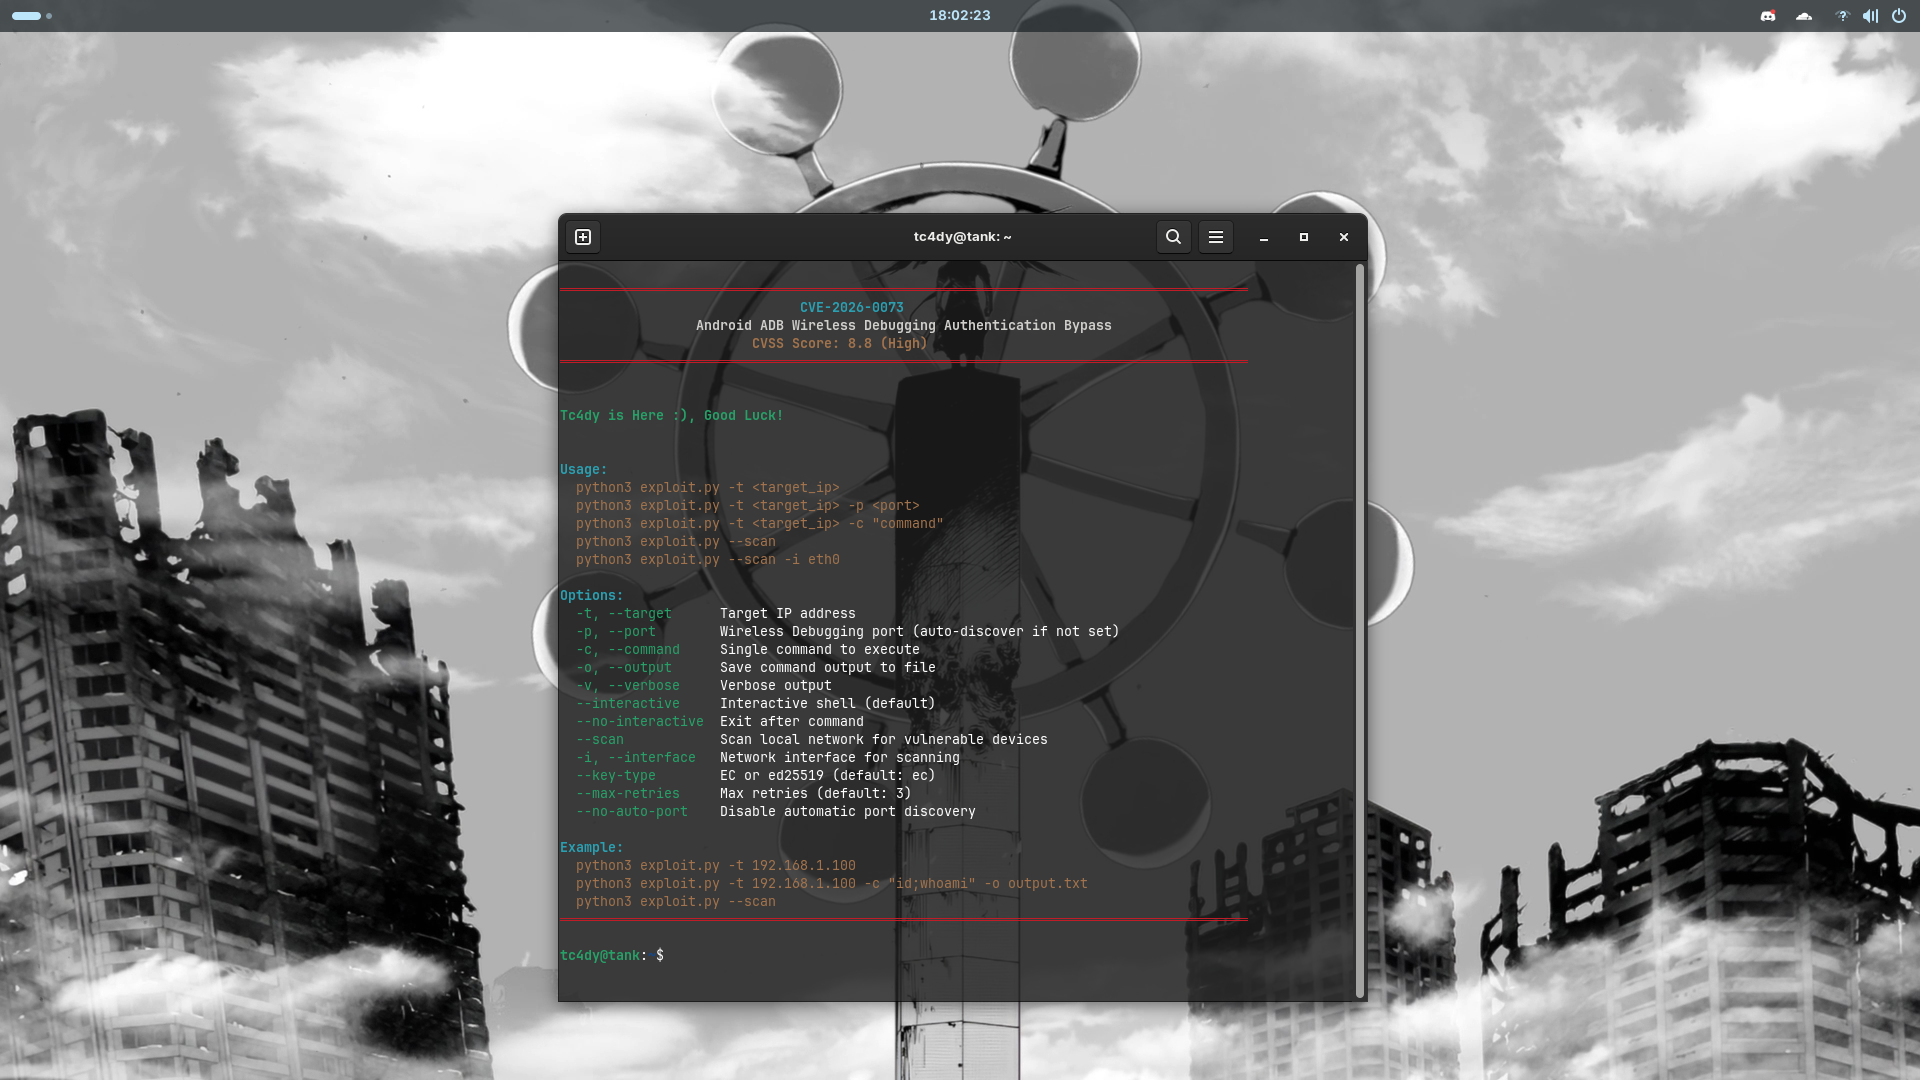 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
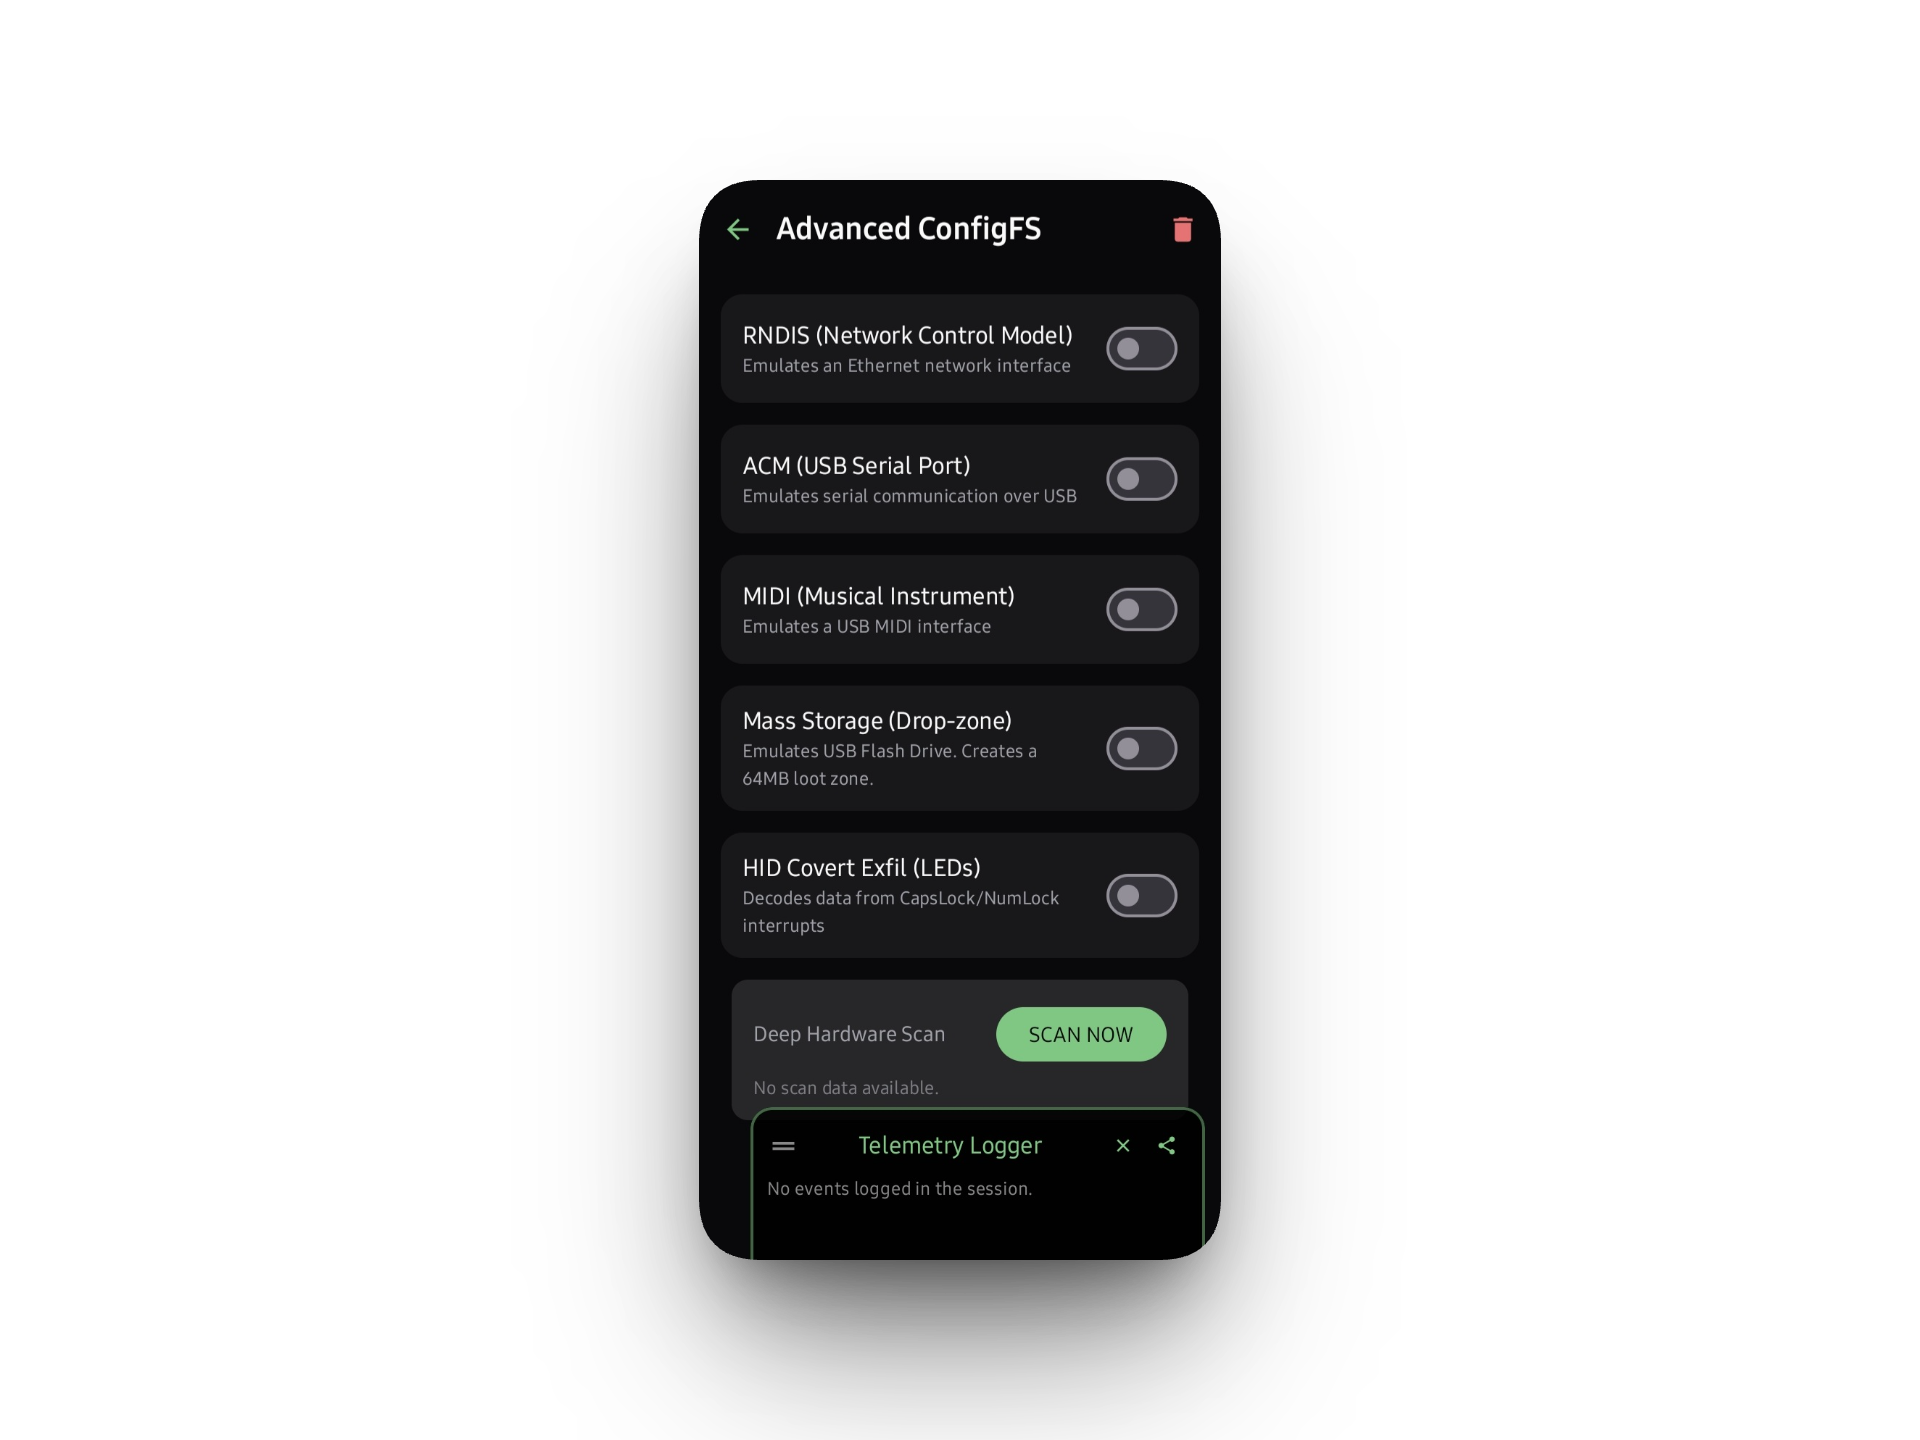 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
 1ndevelopment/ghostlock-s26
GhostLock (CVE-2026-43499) app for the Galaxy S26 series
 a2333c/dfroot
Android root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…
 demining/pixnapping-attack-on-android
Pixnapping Attack: Compromising private keys and seed phrases through vulnerability CVE-2025-48561 represents a new critical threat to the Bitcoin…