
CVE-2022-4510
 electr0sm0g/cve-2022-4510
Exploit for CVE-2022-4510 enabling remote command execution in Binwalk firmware analysis tool. Provides proof-of-concept code for security testing…
binary-analysisexploitationfirmware-analysis+2
9
electr0sm0g/cve-2022-4510Exploit for CVE-2022-4510 enabling remote command execution in Binwalk firmware analysis tool. Provides proof-of-concept code for security testing…
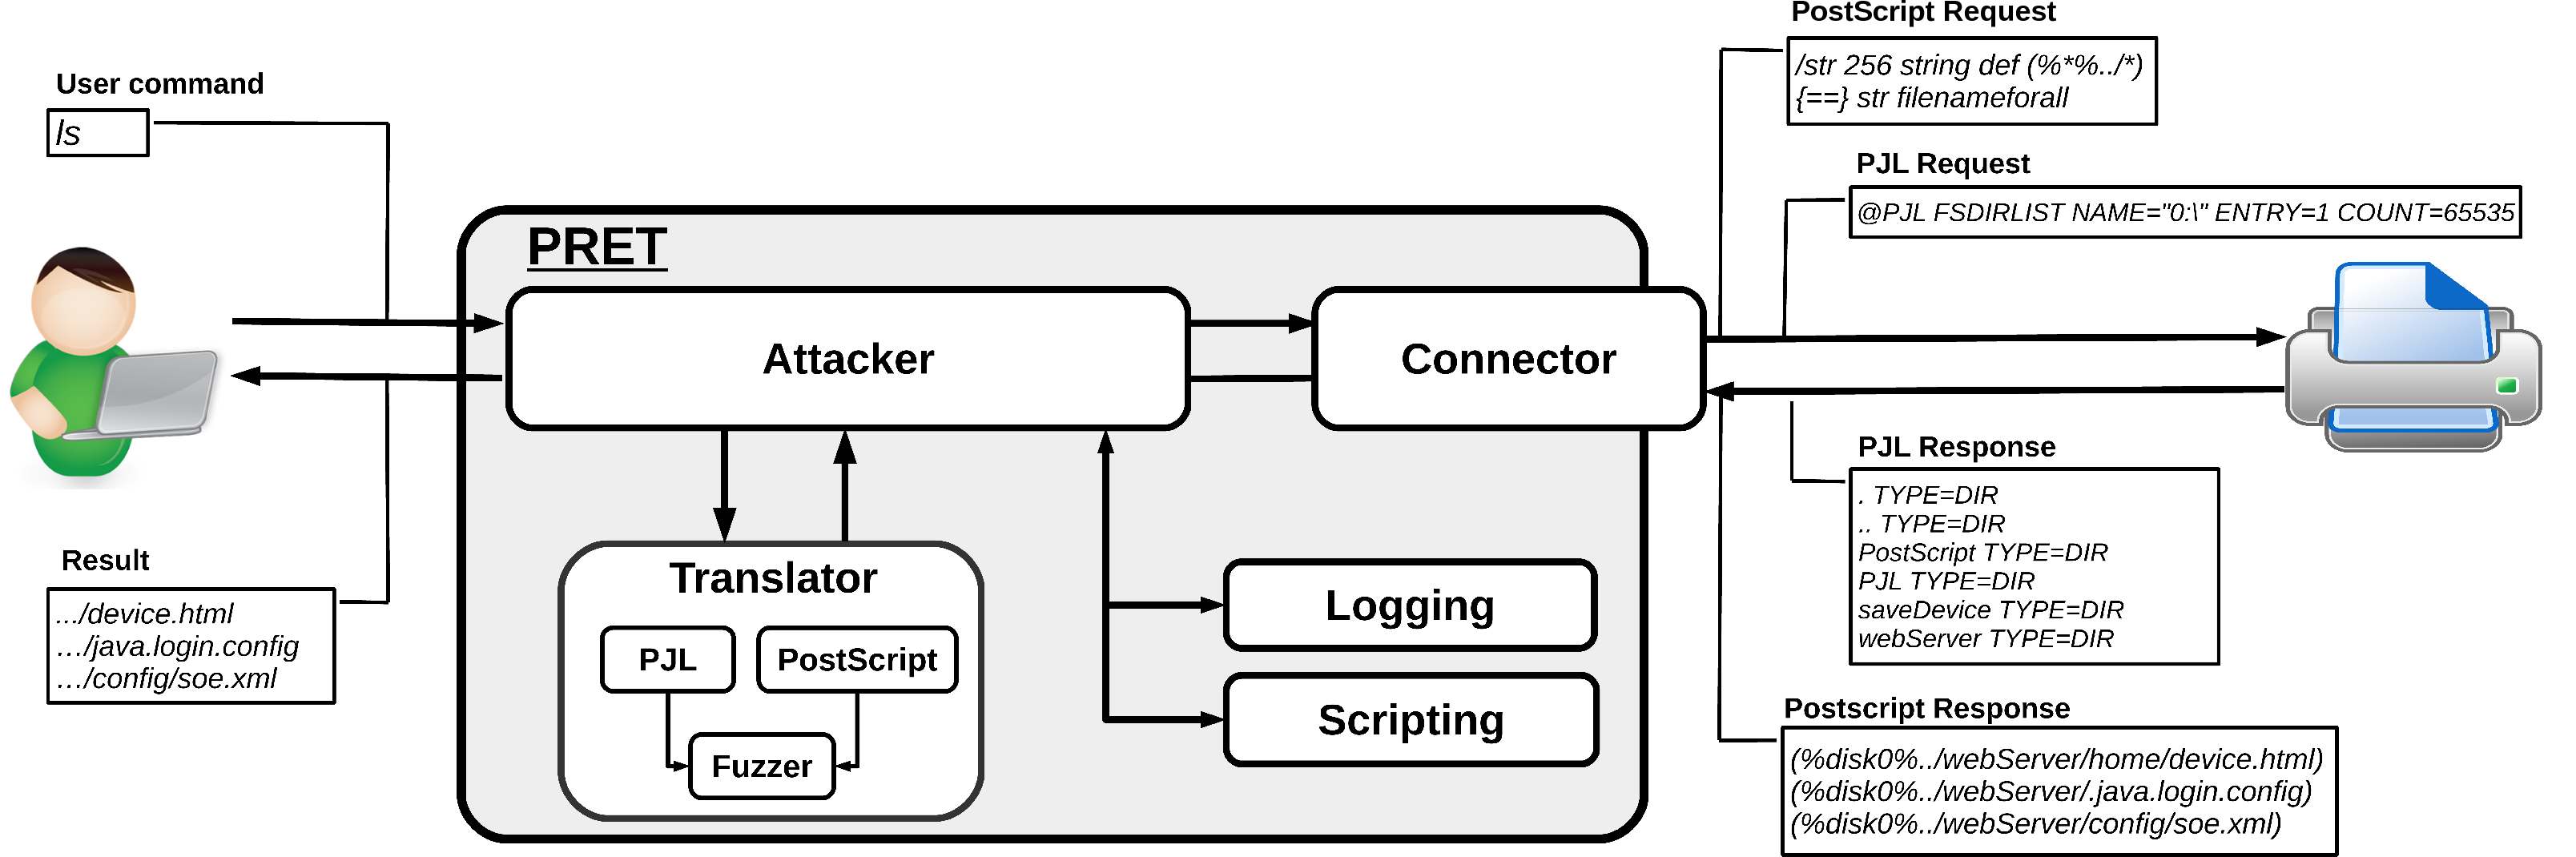 rub-nds/pret
Printer Exploitation Toolkit - The tool that made dumpster diving obsolete.
 thewhiteh4t/killcast
Manipulate Chromecast Devices in your Network
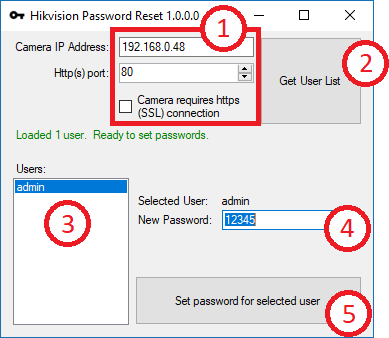 bp2008/hikpasswordhelper
A tool which exploits a backdoor in Hikvision camera firmwares circa 2014-2016 to help the owner change a forgotten password.
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 kkamagui/napper-for-tpm
TPM vulnerability checking tool for CVE-2018-6622. This tool will be published at Black Hat Asia 2019 and Black Hat Europe 2019
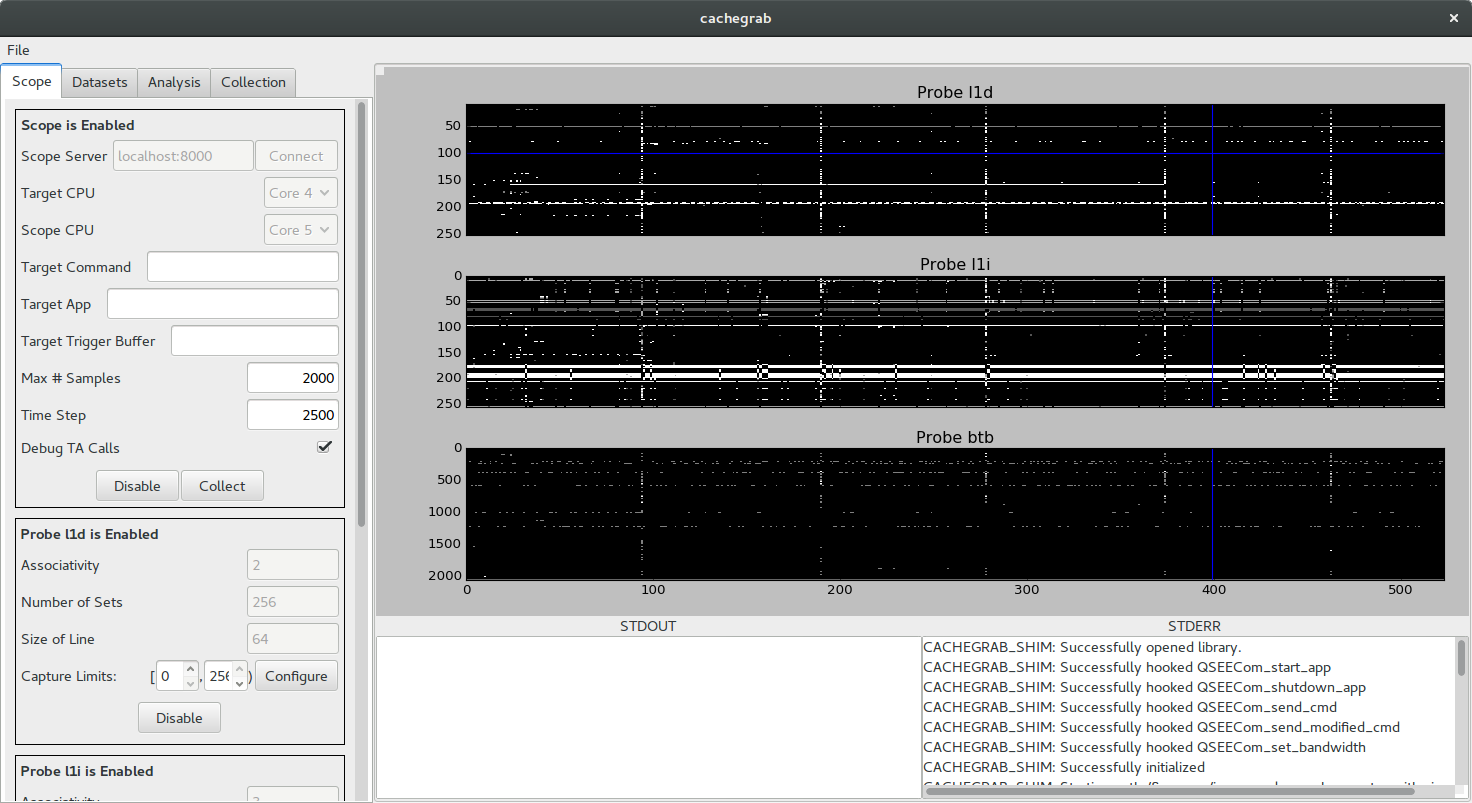 nccgroup/cachegrab
a tool designed to help perform and visualize trace-driven cache attacks against software in the secure world of TrustZone-enabled ARMv8 cores
 jimilinuxguy/lrs-pager-systems-bruteforce
Long Range Pager Systems pagers and coasters URH and YS1 (yardstick one / cc11xx) information and brute force tool
 axcheron/crestron_getsudopwd
Tool to exploit CVE-2018-13341 and recover hidden account password on Crestron devices
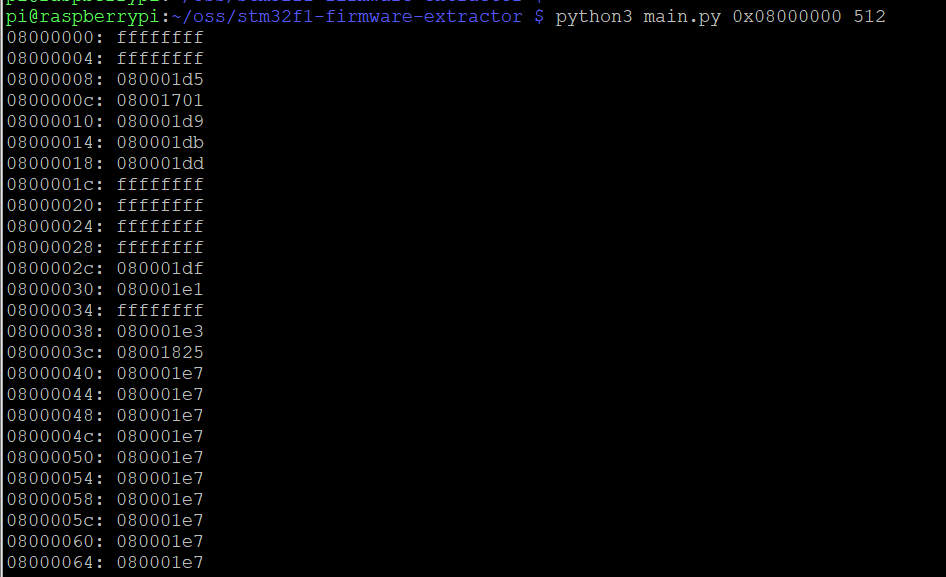 wuxx/cve-2020-8004
Exploit tool for CVE-2020-8004 targeting STM32F1 microcontrollers, enabling firmware extraction via OpenOCD and Python scripts to bypass readout…
 finngineering/apxutil
A tool to manipulate Schneider Electric PLC archive files
 nikameru/nxboot
Payload injection tool for Nintendo Switch consoles vulnerable to CVE-2018-6242 ("Fusée Gelée")
 nikitapbst/cve-2019-6260
Low-level hardware debugging and security assessment tool for ASPEED BMC AHB interfaces. Probes PCIe, LPC, and UART interfaces to read/write…
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 haingn/hik-cve-2021-36260-exploit
Go-based brute-force exploit tool targeting Hikvision cameras vulnerable to CVE-2021-36260, with multi-threaded scanning and configurable…
 lequockhanh2k/tool_exploit_password_camera_cve-2018-9995
Exploit tool for CVE-2018-9995 that extracts credentials from vulnerable DVR devices via Google dorking and direct IP access.
 leonardobg/cve-2023-36143
Proof-of-concept exploit for CVE-2023-36143 demonstrating command injection in Maxprint Maxlink 1200G v3.4.11E via the diagnostic tool web interface.
 rajchowdhury240/cve-2018-13341
This Tool Aims to Exploit the CVE-2018-13341