
CVE-2025-6218_WinRAR
 speinador/cve-2025-6218_winrar
Educational lab demonstrating CVE-2025-6218 path traversal in WinRAR. Includes a malicious RAR file and step-by-step guide to observe file overwrite…
binary-exploitationeducationexploitation+3
speinador/cve-2025-6218_winrarEducational lab demonstrating CVE-2025-6218 path traversal in WinRAR. Includes a malicious RAR file and step-by-step guide to observe file overwrite…
 xdezen/cve-2025-8110
Python proof-of-concept for CVE-2025-8110, demonstrating arbitrary file write to RCE in Gogs via symlink and API, with educational lab usage.
 fevar54/proof-of-concept-poc---cve-2026-49975-http-2-bomb-
Proof-of-concept exploit for CVE-2026-49975 (HTTP/2 Bomb), a remote denial-of-service vulnerability affecting major web servers via HPACK bomb and…
 d3fudd/cve-2017-7494_sambacry
SambaCry (CVE-2017-7494) exploit for Samba | bind shell without Metasploit
 ull0a/cve-2026-50751
Bypass de autenticación por certificado en la VPN Remote-Access de Check Point (IKEv1).

 javaamo/cve-2021-41773
Fixed shell exploit for Apache HTTP Server 2.4.49 CVE-2021-41773 path traversal and remote code execution vulnerability. Reads arbitrary files and…
 yukafake/cve-2024-32002-reverse-shell
Este script demuestra cómo explotar la vulnerabilidad CVE-2024-32002 para obtener una reverse shell, proporcionando acceso remoto al sistema…
 007criptografia/c-cve-2024-0044
CVE-2024-0044: uma vulnerabilidade de alta gravidade do tipo "executar como qualquer aplicativo" que afeta as versões 12 e 13 do Android
 chernandez321/cve-2025-9074-docker-escape
Este script es para uso educativo y en entornos autorizados como HackTheBox. El uso contra sistemas sin permiso explícito es ilegal.
 maur0amaya/escalamiento-de-privilegios-usando-el-kernel-exploit-dirty-cow
Este proyecto tiene como objetivo demostrar de forma práctica el funcionamiento del exploit Dirty COW (CVE-2016-5195), una vulnerabilidad crítica del…
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 igonzalez357/cve-2021-4034-pwnkit-
Este repositorio muestra cómo explotar la vulnerabilidad CVE-2021-4034.
 germarr93/cybersecurity-pentest-lab
CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab
 pithase/asm-copyfail
CVE-2026-31431 (Copy Fail) — Análisis y desarrollo en Ensamblador x86-64 | Analysis and development in x86-64 Assembly
 moften/cve-2023-44487-http-2-rapid-reset-attack
HTTP/2 Rapid Reset Exploit PoC
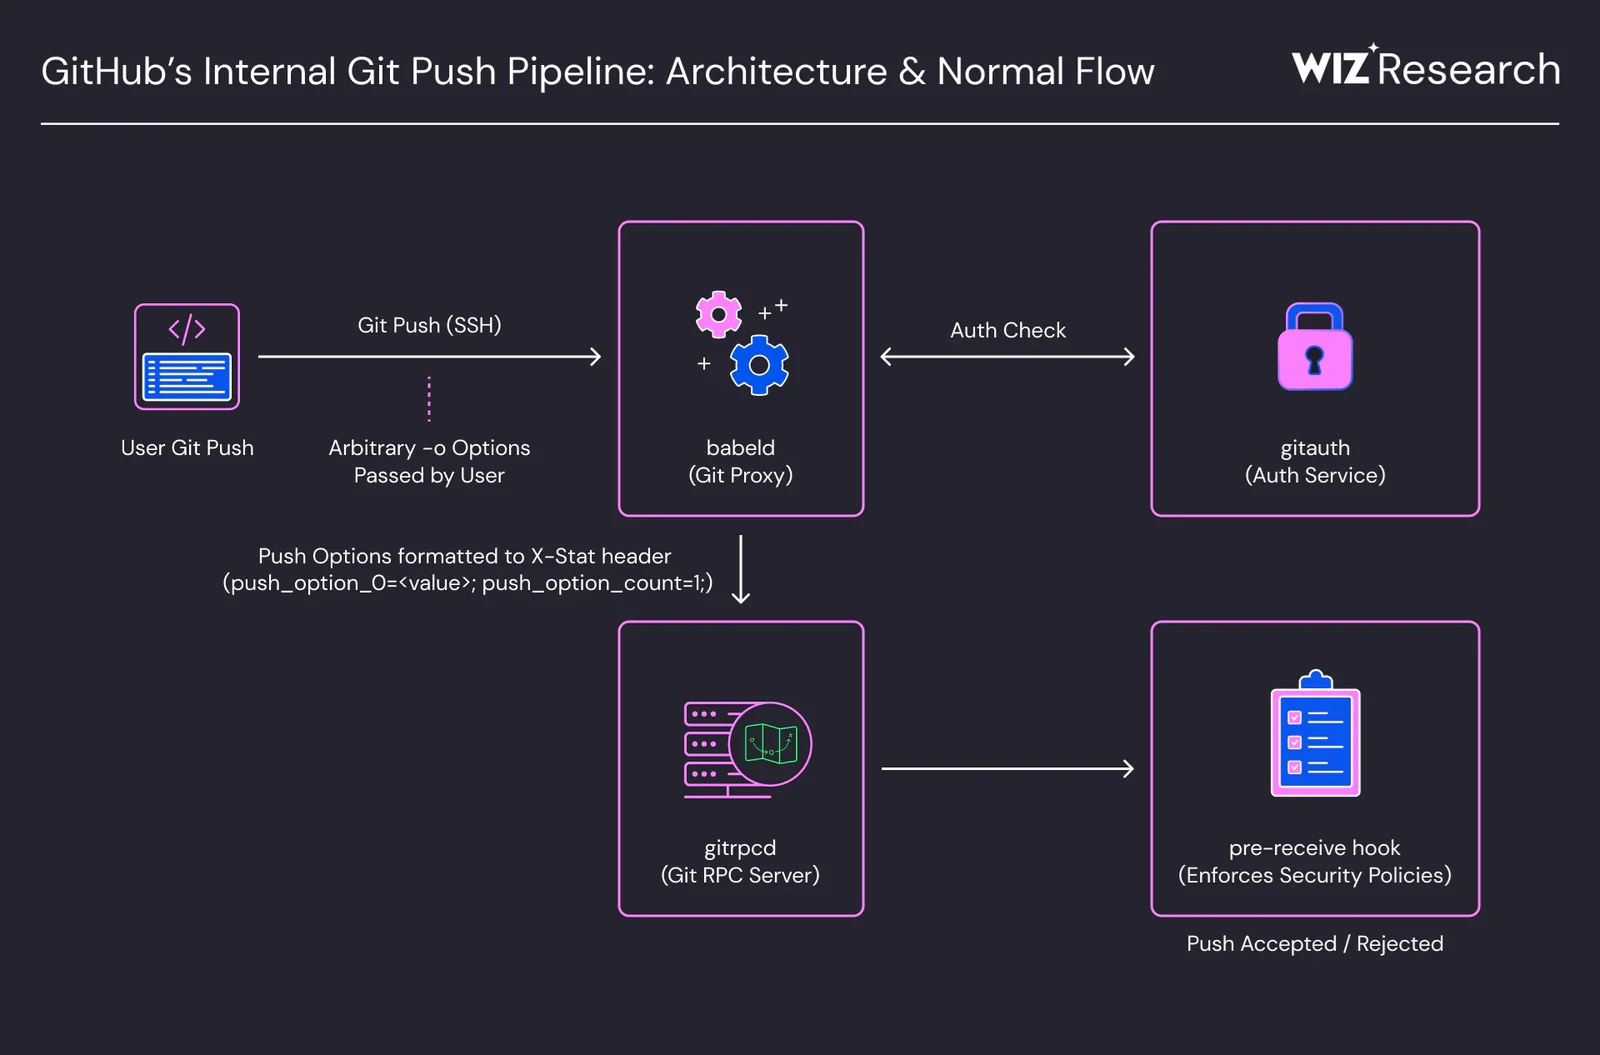 5kr1pt/cve-2026-3854
Technical breakdown of CVE-2026-3854, a GitHub RCE via header injection in git push, explaining the vulnerability, exploitation technique, and…
 jeanback1/cve-2023-30253-exploit
CVE-2023-30253 — Dolibarr ERP/CRM 17.0.0 RCE via PHP code injection (exploit educativo)