
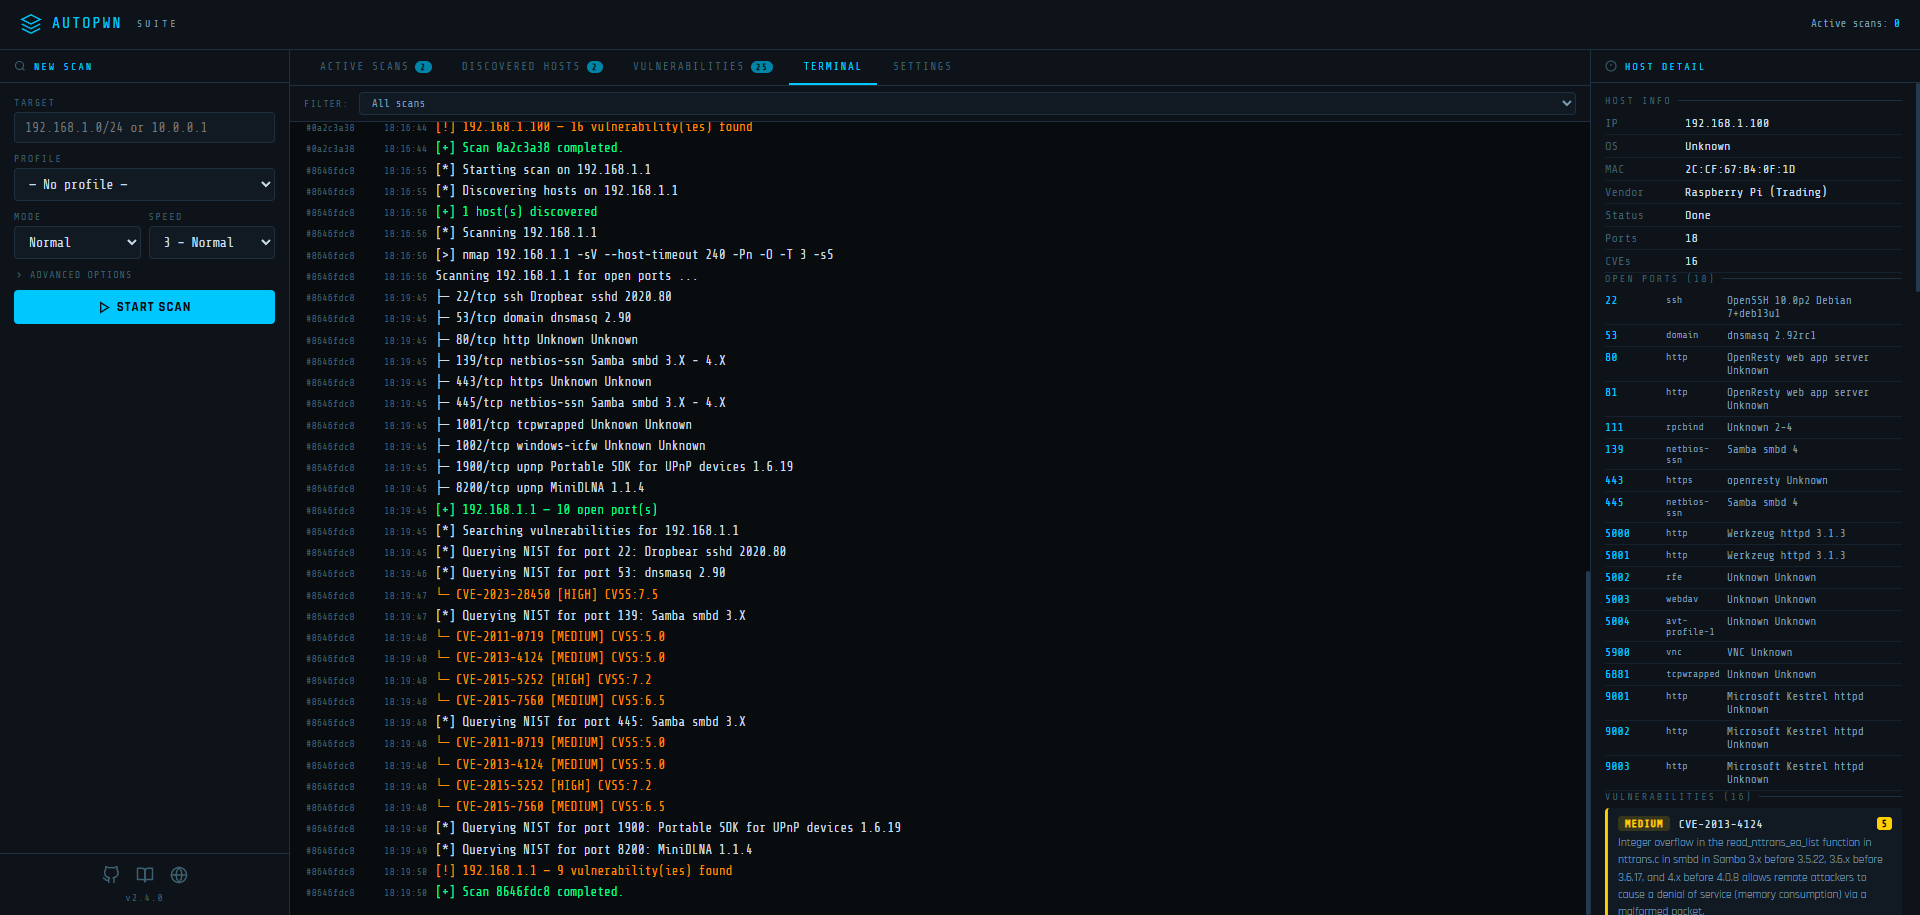
AutoPWN-Suite
 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
exploitationinformation-gatheringnetwork-security+5
1.1k
gamehunterkaan/autopwn-suiteAutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
 heptagrams/heptagram
This project is used to collect the EXP/POC disclosed on the Internet and provide project support for Heptagram security team.
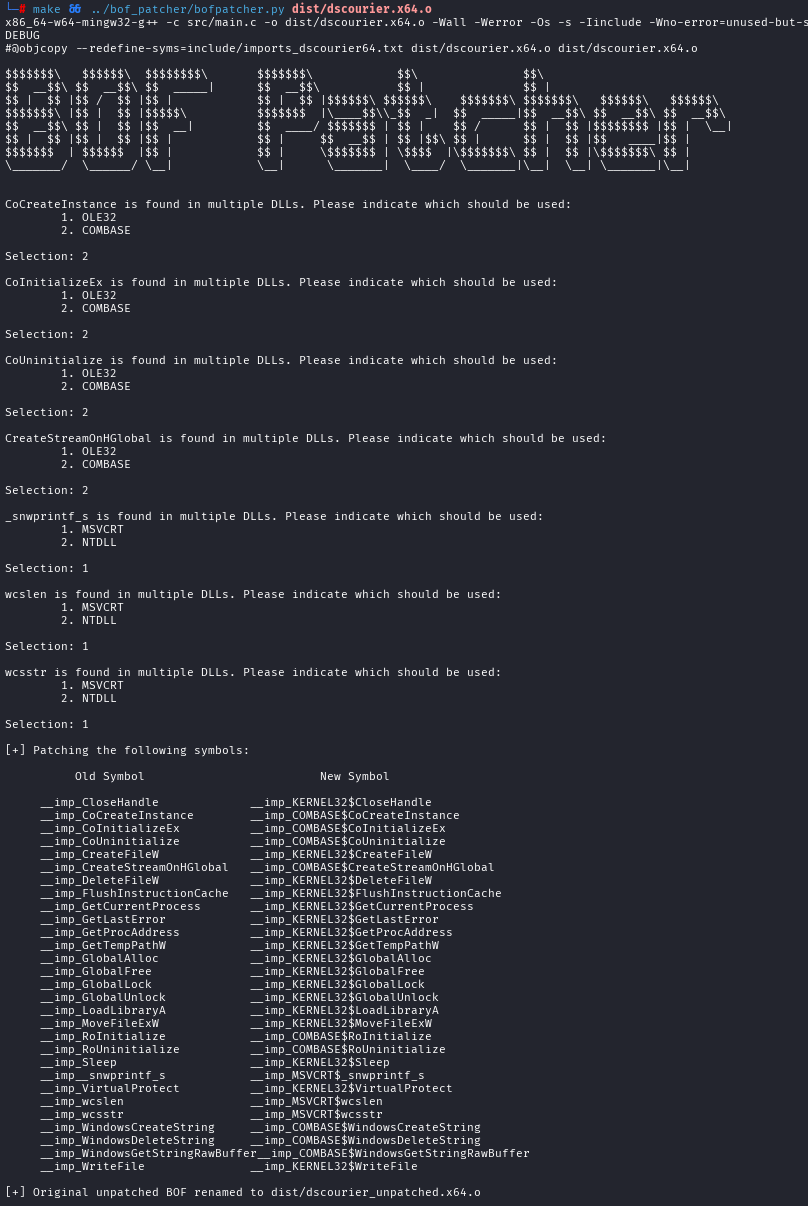 octoberfest7/dscourier_bof
BOF POC of the DSCourier project / invoking WinGet via COM
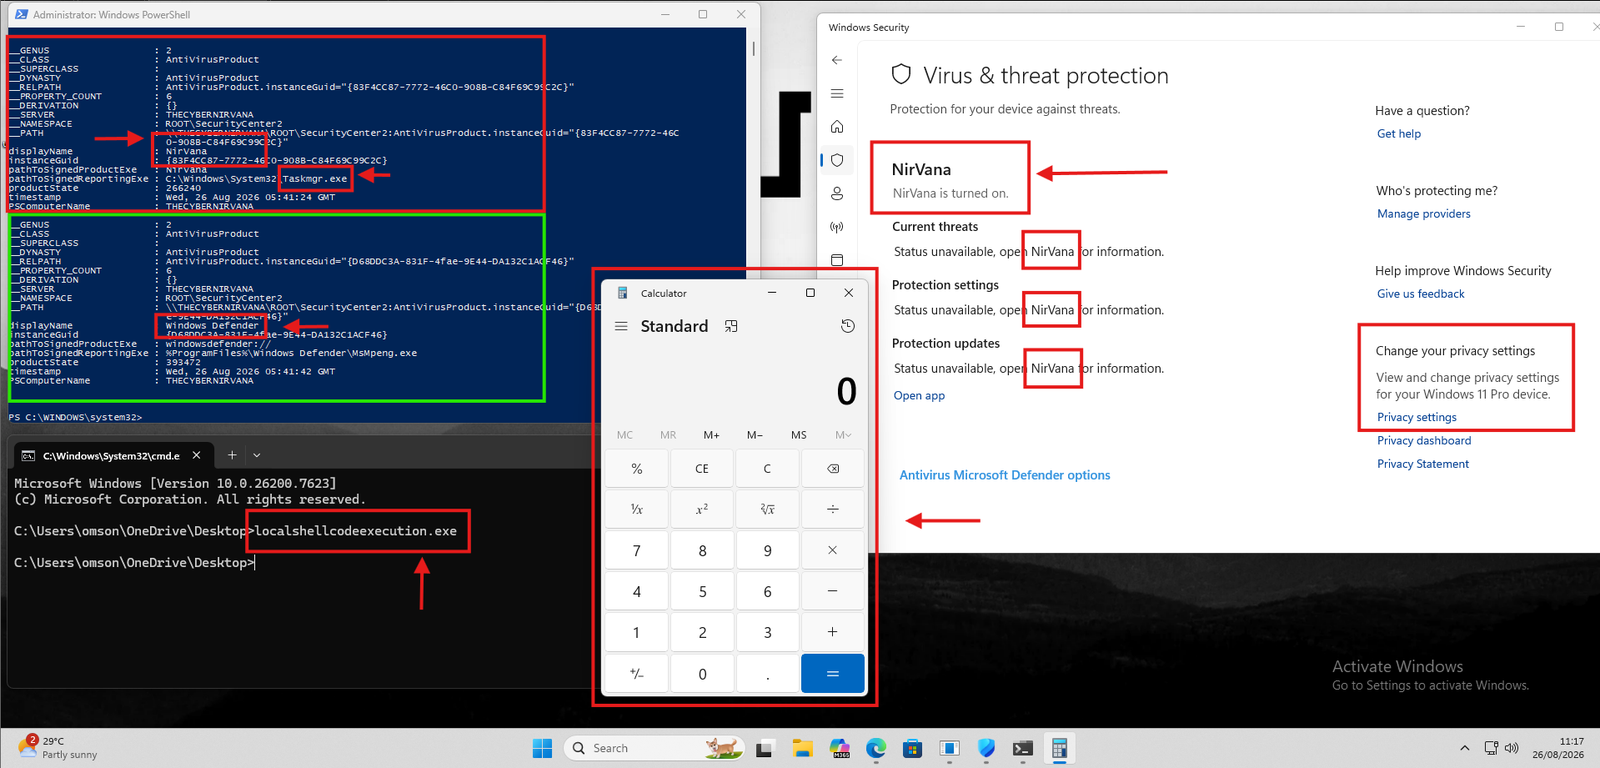 nirvanaon/own-defender
Research project reverse-engineering Windows Security Center COM interfaces to trace AV registration through ATL, vtable, WSCAPI, and RPC, with…
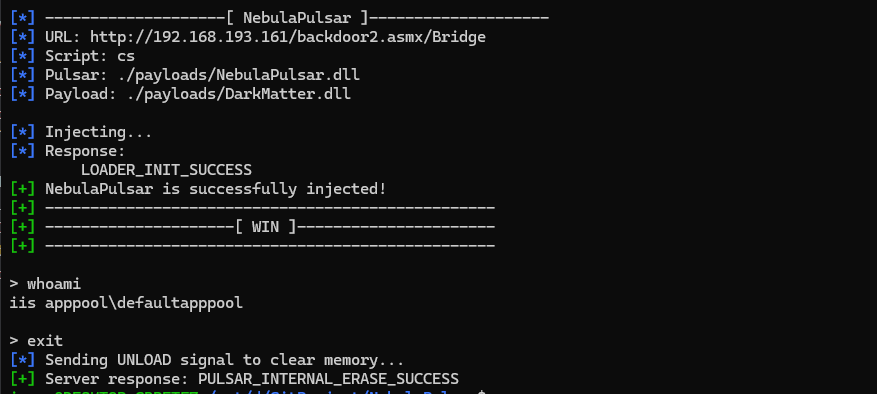 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 chacka0101/exploits
Exploits project Hacking Command Center
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
 geosn0w/cve-2025-24203-ios-exploit-with-error-logging
Slightly improved exploit of the CVE-2025-24203 iOS vulnerability by Ian Beer of Google Project Zero
 traitimtrongvag/android-imgui-template
A complete Android ImGui menu template project.
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
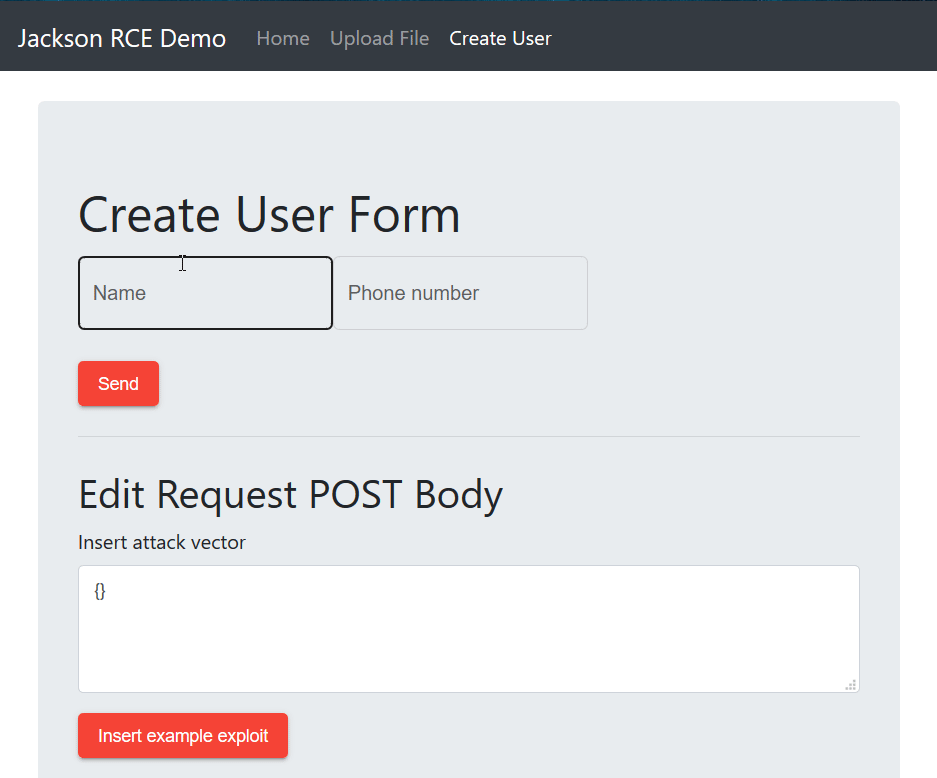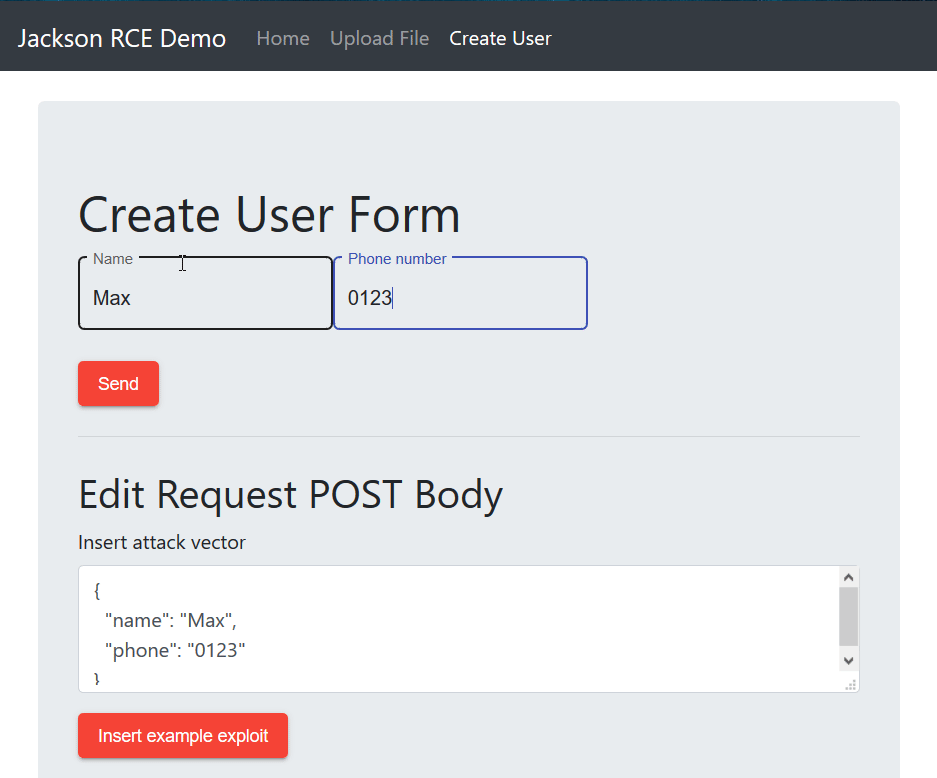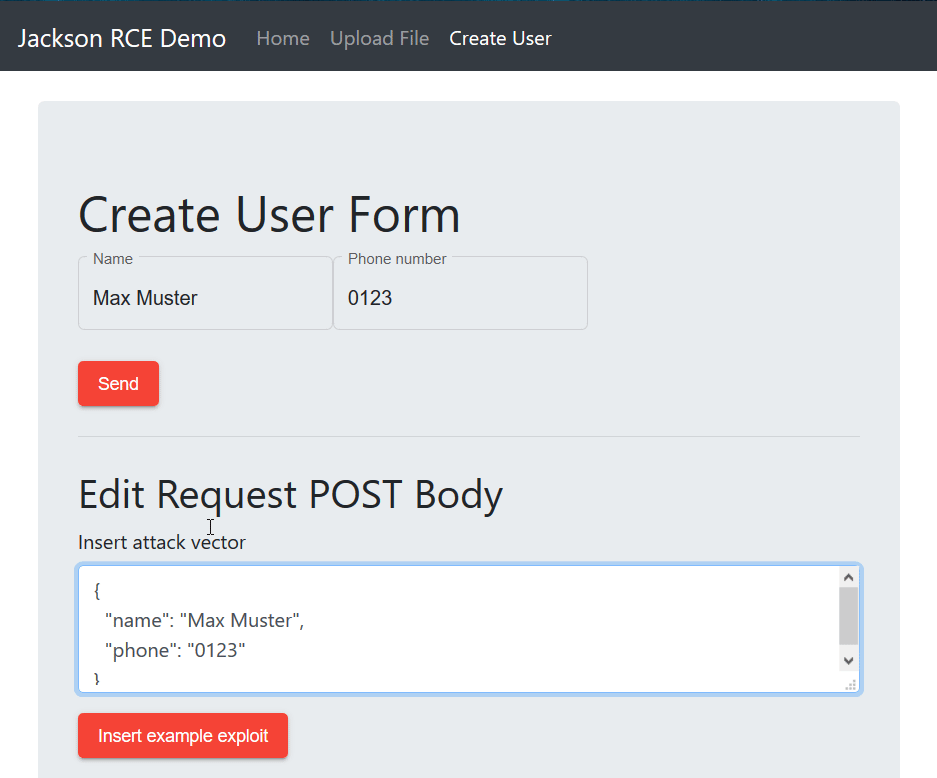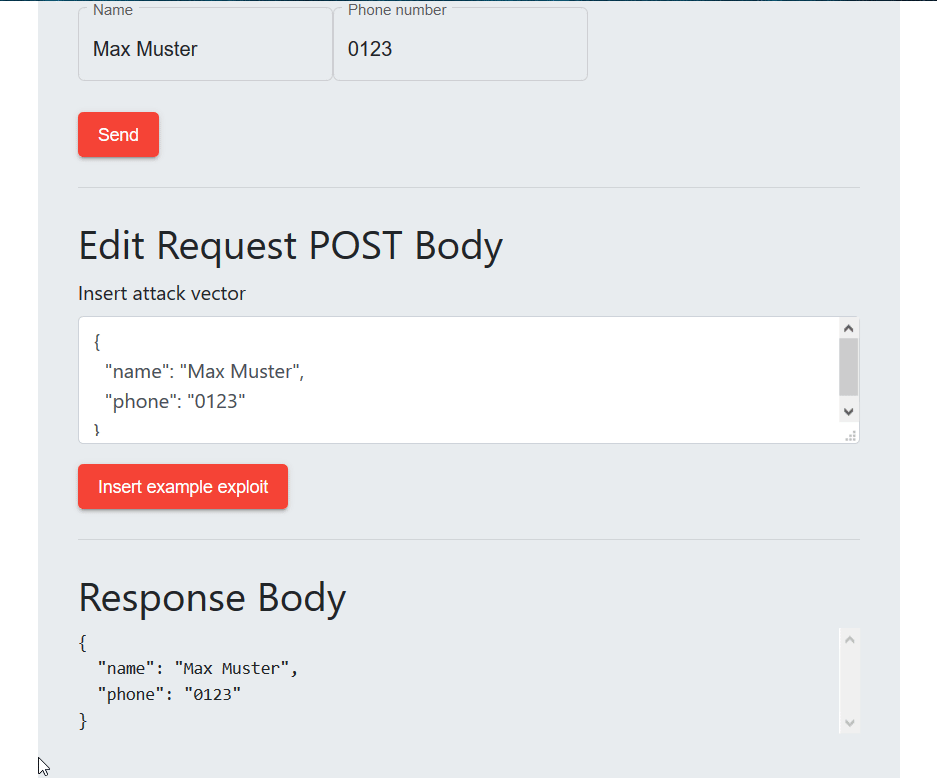 javanxd/demo-exploit-jackson-rce
Exploiting CVE-2017-7525 demo project with Angular7 frontend and Spring.
 snyk-labs/pdfjs-vuln-demo
This project is intended to serve as a proof of concept to demonstrate exploiting the vulnerability in the PDF.js (pdfjs-dist) library reported in…
 dickens88/cve-2020-0796-scanner
This project is used for scanning cve-2020-0796 SMB vulnerability
 canomer/cve-2025-54110-kernel-eop-poc
Project Date : Oct 2025 / PoC implementation for CVE-2025-54110 a Kernel-Level Integer Overflow Vulnerability in the Windows `NtQueryDirectoryObject`…
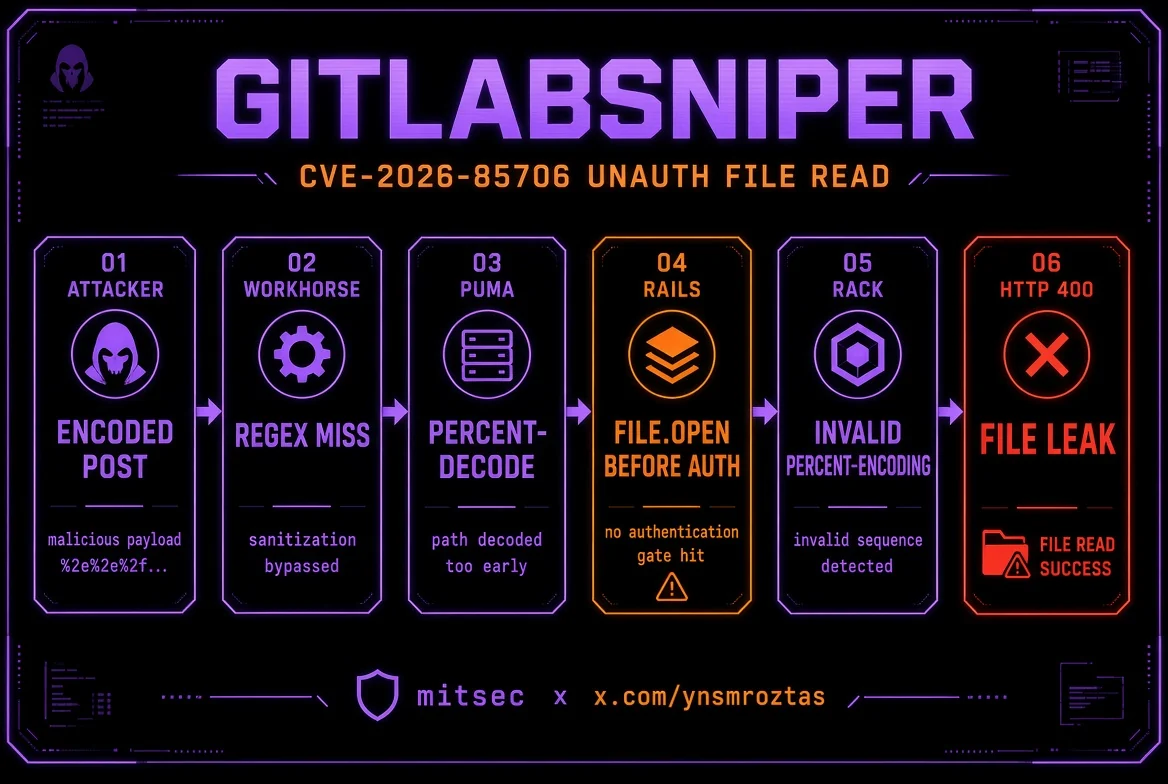 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 bit4woo/cve-2020-13925
Proof-of-concept exploit for CVE-2020-13925, a command injection vulnerability in Apache Kylin's diagnostic API, allowing remote code execution via…