
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
139 results
CVE-2021-40444 preview

CVE-2021-40444

GitHublockedbyte/cve-2021-40444

Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office RCE) with a hosted server for DLL payload delivery, based on…
exploitationmalware-analysispayload-generation+1
1.8k
5 years ago
CVE-2021-40444 preview

CVE-2021-40444

GitHubtiagob0b/cve-2021-40444

Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…

binary-exploitationexploitationpayload-generation+3
5 years ago
CVE-2018-8440 preview

CVE-2018-8440

GitHubsourceincite/cve-2018-8440

CVE-2018-8440 standalone exploit
binary-exploitationexploitationexploit-frameworks+3
808 years ago
RottenPotatoNG preview

RottenPotatoNG

GitHubbreenmachine/rottenpotatong

New version of RottenPotato as a C++ DLL and standalone C++ binary - no need for meterpreter or other tools.
exploitationpenetration-testingpost-exploitation+1
9748 years ago
Koppeling preview

Koppeling

GitHubmonoxgas/koppeling

Adaptive DLL hijacking / dynamic export forwarding
binary-exploitationexploitationpayload-development+1
8196 years ago
faxhell preview

faxhell

GitHubionescu007/faxhell

A Bind Shell Using the Fax Service and a DLL Hijack
exploitationpayload-developmentpost-exploitation+2
3346 years ago
Fritter preview

Fritter

GitHub0xrootpls/fritter

Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
binary-exploitationexploitationpayload-development+5
2483 months ago
CdpSvcLPE preview

CdpSvcLPE

GitHubsailay1996/cdpsvclpe

Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
exploitationpayload-developmentpenetration-testing+3
2564 years ago
LdrShuffle preview

LdrShuffle

GitHubrwxstoned/ldrshuffle

Code execution/injection technique using DLL PEB module structure manipulation
binary-exploitationcode-analysisexploitation+6
2891 year ago
DLLHijackingScanner preview

DLLHijackingScanner

GitHubsecuproject/dllhijackingscanner

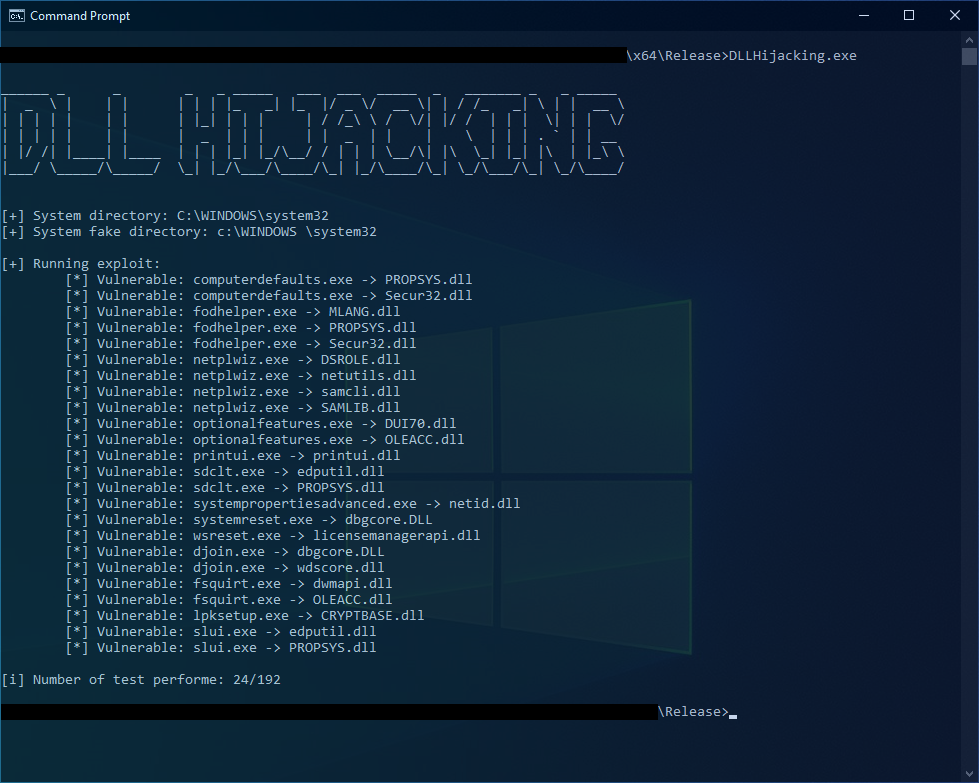
This is a PoC for bypassing UAC using DLL hijacking and abusing the "Trusted Directories" verification.
exploitationprivilege-escalationvulnerability-scanners
2835 years ago
koppeling-p preview

koppeling-p

GitHubklezvirus/koppeling-p

Adaptive DLL hijacking / dynamic export forwarding - EAT preserve
binary-exploitationexploitationpayload-development+3
792 years ago
wptsextensions.dll preview

wptsextensions.dll

GitHubphackt/wptsextensions.dll

WptsExtensions.dll for exploiting DLL hijacking of the task scheduler.

exploitationpayload-developmentpersistence-mechanisms+3
575 years ago
CVE-2021-40444 preview

CVE-2021-40444

GitHubk8gege/cve-2021-40444

Exploit toolkit for CVE-2021-40444 MSHTML remote code execution, featuring DLL payload generation, Office document crafting, and lateral movement…
command-and-controlexploitationlateral-movement+3
225 years ago
CVE-2019-18935-memShell preview

CVE-2019-18935-memShell

GitHubdust-life/cve-2019-18935-memshell

C++ memshell DLL generator for CVE-2019-18935, enabling in-memory web shell deployment via Telerik UI deserialization with Assembly.Load and IJW…
exploitationpayload-developmentpenetration-testing+2
131 year ago
CVE-2010-5301 preview

CVE-2010-5301

GitHublem0nsec/cve-2010-5301

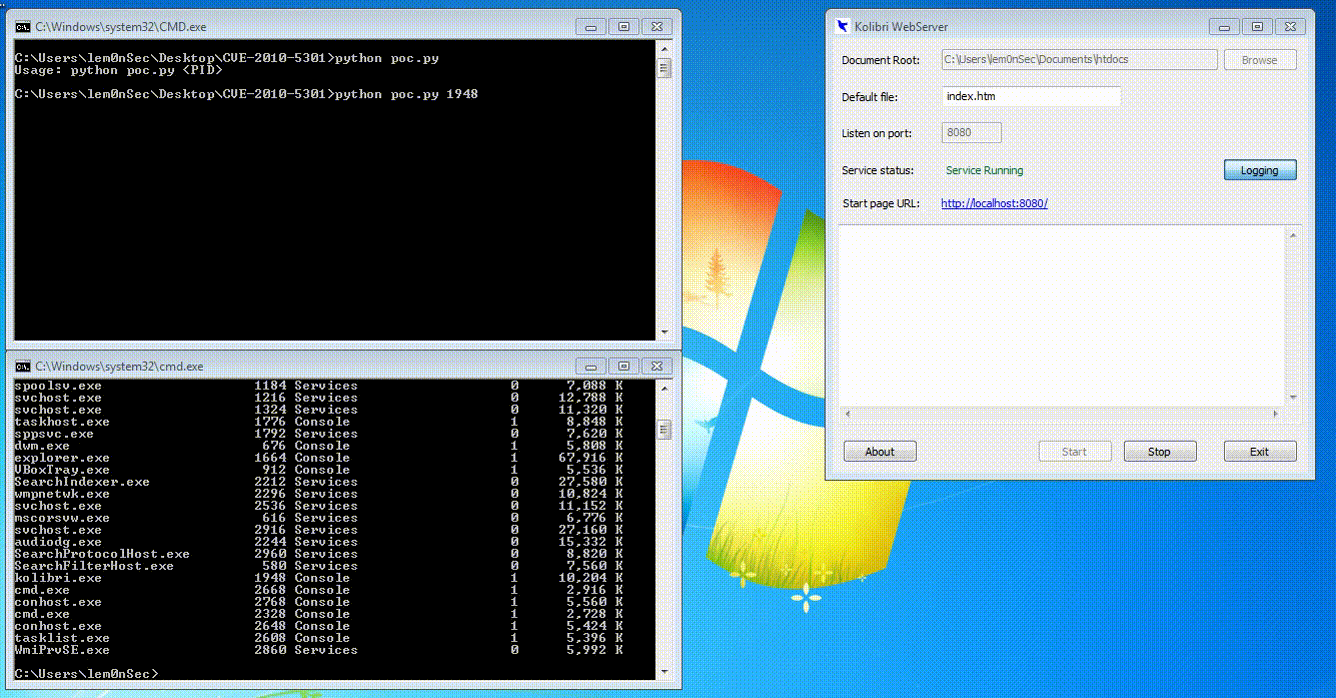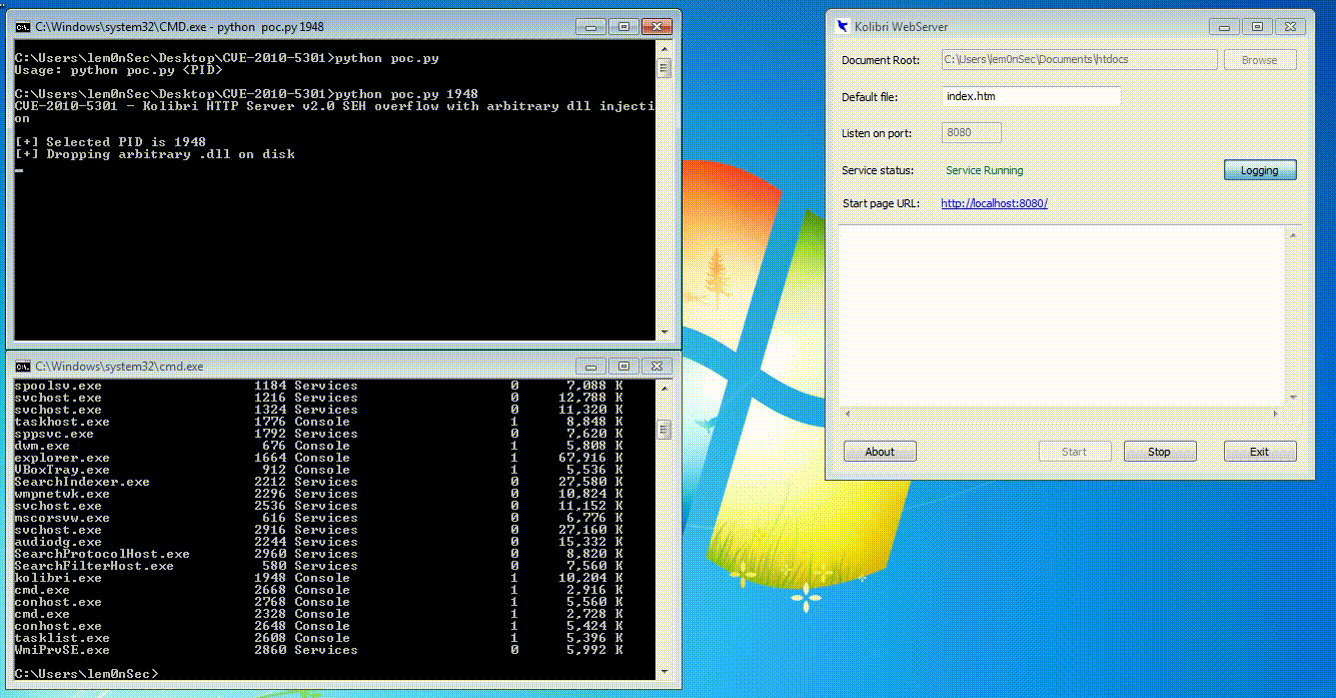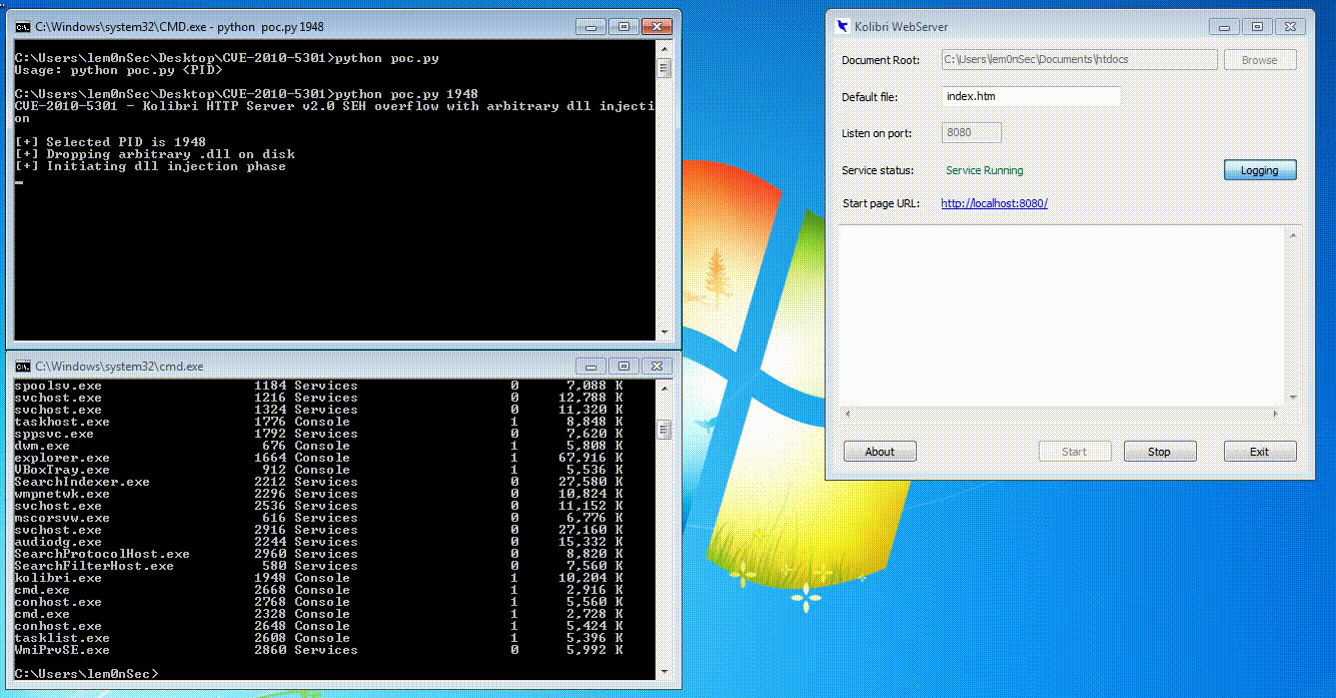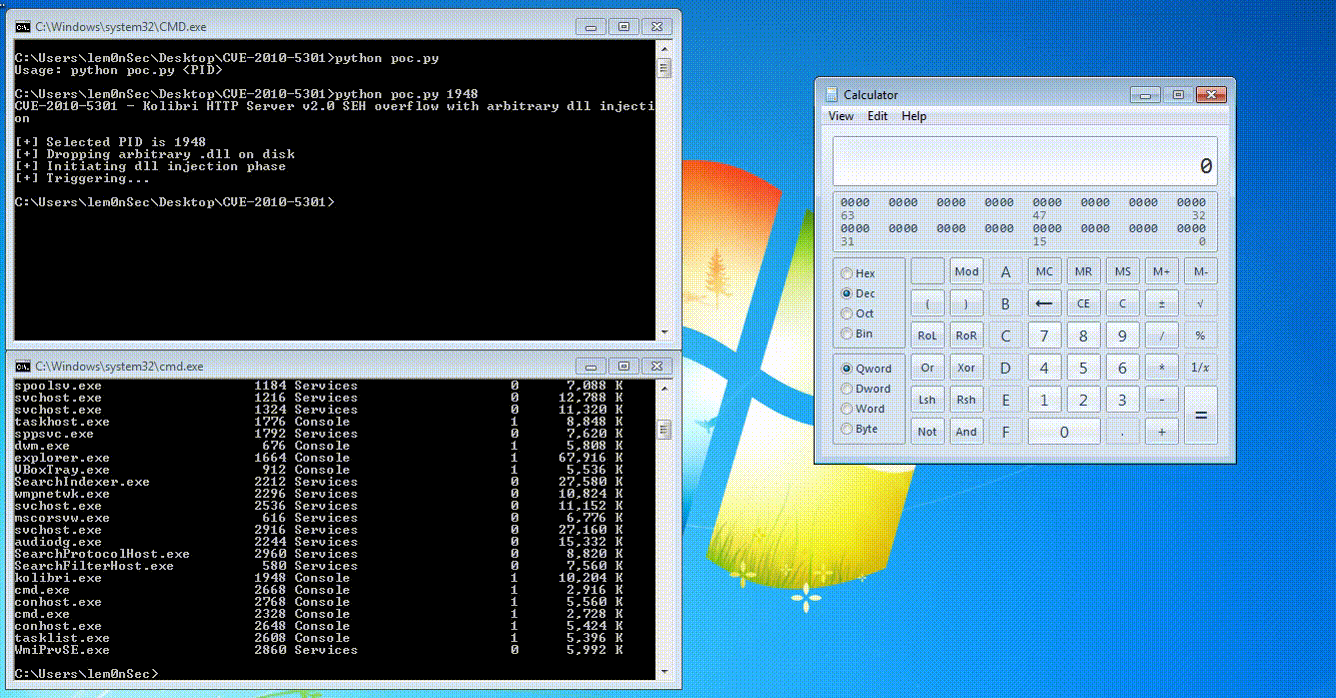
A proof of concept of an SEH overflow with arbitrary dll injection

binary-exploitationexploitationpayload-development+3
14 years ago
CVE-2021-36934-DLL-Hijacking-DFIR-Investigation preview

CVE-2021-36934-DLL-Hijacking-DFIR-Investigation

GitHubduyduongduyduong/cve-2021-36934-dll-hijacking-dfir-investigation

DFIR investigation resources for CVE-2021-36934, covering DLL hijacking, privilege-escalation detection, and forensic analysis of affected Windows…
digital-forensicsexploitationincident-response+2
2 months ago
chimera preview

chimera

GitHub1neptune/chimera

Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence

binary-exploitationexploitationpayload-development+4
4 months ago
CVE-2021-1675 preview

CVE-2021-1675

GitHubwinter3un/cve-2021-1675

Remote privilege escalation exploit for CVE-2021-1675 (PrintNightmare) with DLL injection and port forwarding support for remote execution.

exploitationpenetration-testingprivilege-escalation+1
15 years ago
Previous1…678Next