

CVE-2022-23046
 jcarabantes/cve-2022-23046
Proof-of-concept exploit for CVE-2022-23046, an authenticated SQL injection in PhpIPAM v1.4.4. Extracts server info, SMTP settings, user hashes, and…
exploitationinformation-gatheringpenetration-testing+2
1
jcarabantes/cve-2022-23046Proof-of-concept exploit for CVE-2022-23046, an authenticated SQL injection in PhpIPAM v1.4.4. Extracts server info, SMTP settings, user hashes, and…
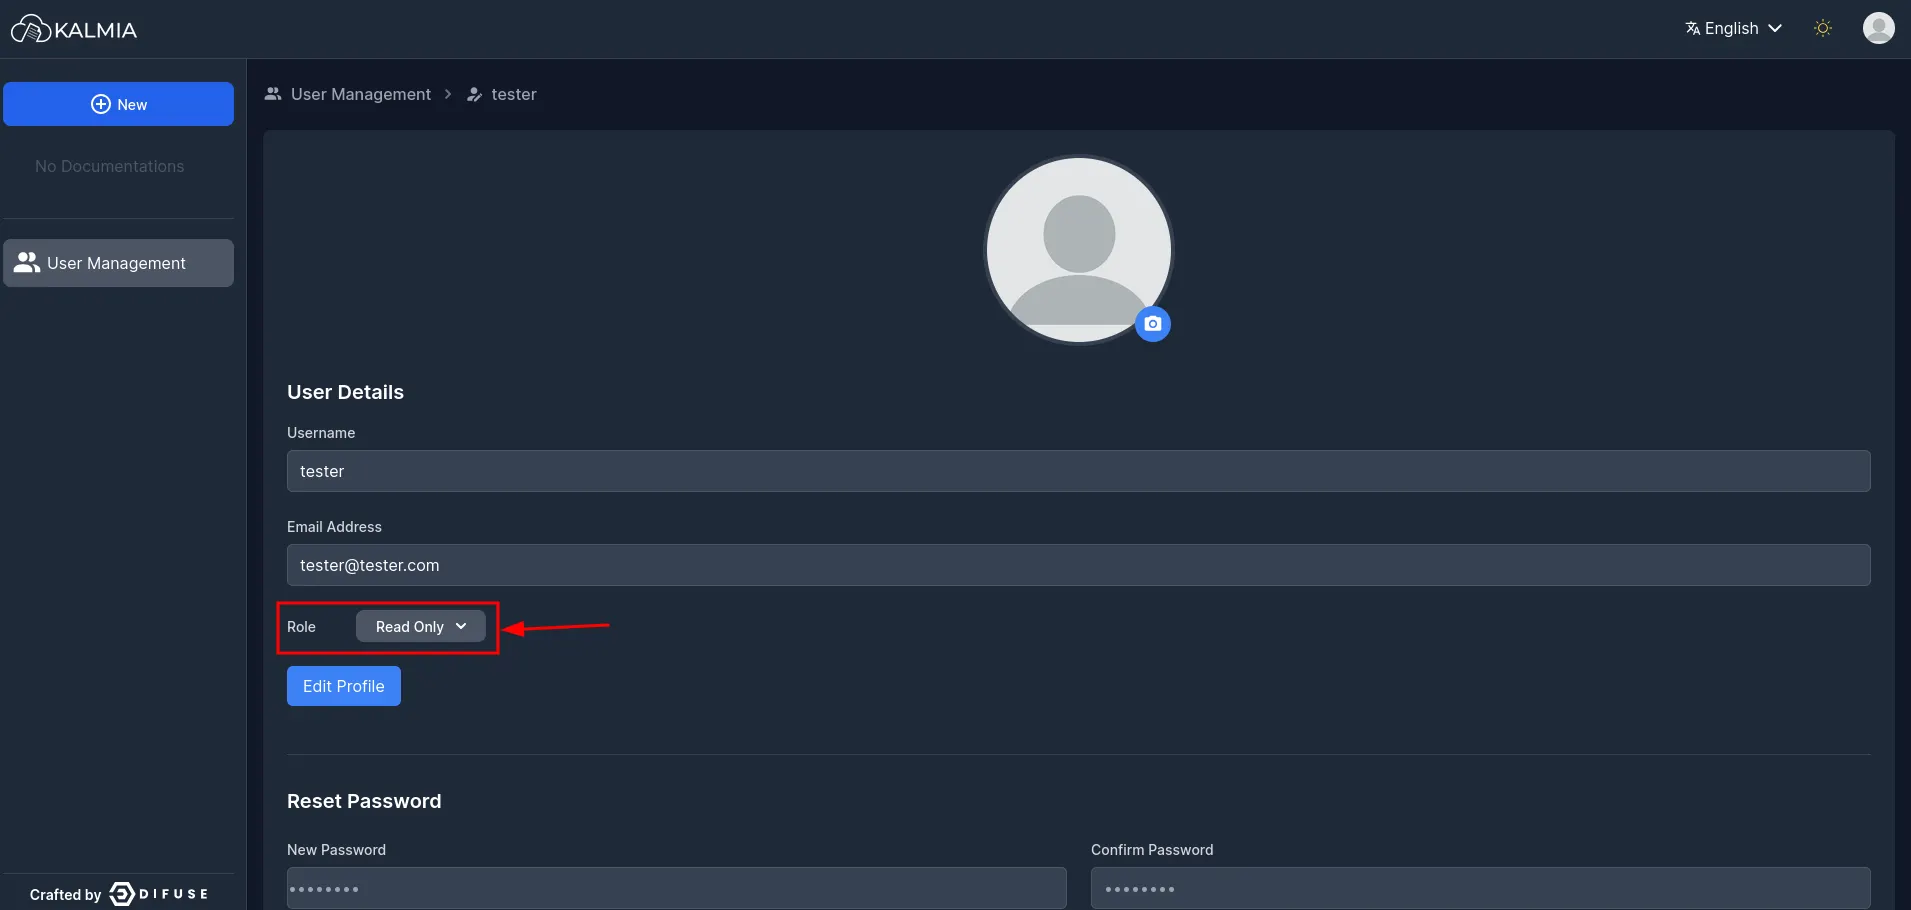 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 f4dee-backup/cve-2025-24071
Exploit script for CVE-2025-24071 that leaks NTLM hashes from Windows by extracting a crafted ZIP/RAR file, exploiting .library-ms file handling.…
 ethancunt/cve-2022-45599
Proof-of-concept for CVE-2022-45599: PHP type juggling vulnerability in Aztech WMB250AC router login.php allowing admin authentication bypass via…
 g4sp4rcs/cve-2023-32784-password-combinator-fixer
After using the KeePass password dumper maybe some character parsed as ● is incorrect and you want to know the real character
 mishakorzik/allhackingtools
All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
 wiire-a/cve-2017-9476
Hidden AP with Deterministic Credentials
 grepstrength/cve-2026-92680
Proof-of-concept decrypting Araxis Merge's DPAPI-protected server credentials (CVE-2026-92680), demonstrating insufficiently protected credential…
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 midpipps/cve-2020-1472-easy
A simple implementation/code smash of a bunch of other repos
 x3rx3ssec/cve-2025-2011
Exploit for CVE-2025-2011
 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC
 z-bool/venom-jwt
针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)
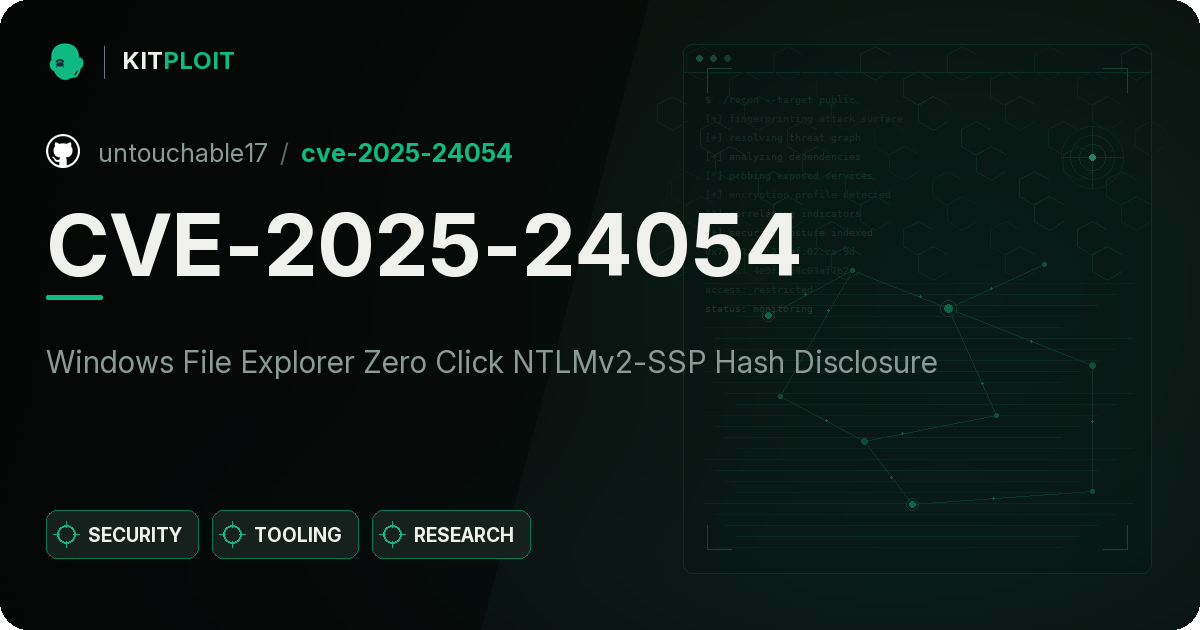
 mstxq17/cve-2020-1472
cve-2020-1472 复现利用及其exp
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)