
CVE-2024-21378
 d0rb/cve-2024-21378
This repository contains an exploit for targeting Microsoft Outlook through Exchange Online, leveraging a vulnerability to execute arbitrary code via…
educationemail-securityexploitation+4
9
d0rb/cve-2024-21378This repository contains an exploit for targeting Microsoft Outlook through Exchange Online, leveraging a vulnerability to execute arbitrary code via…
 noraj/atmail-exploit-toolchain
AtMail Email Server Appliance 6.4 - Exploit toolchain (XSS > CSRF > RCE)
 blackhatexploitation/exploit-for-cve-2026-18963
Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…
 romain-deperne/cve-2026-33715
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
 0xdims/cve-2019-16759
This tools will extracts and dumps Email + SMTP from vBulletin database server
 feartheploto/gitlab-cve-2023-7028
Mock vulnerable GitLab instance reproducing CVE-2023-7028 password reset hijack. Demonstrates array-based email parameter exploitation and account…
 pog007/cve-2023-5561-poc
WordPress does not properly restrict which user fields are searchable via the REST API, allowing unauthenticated attackers to discern the email…
 joesmithjaffa/cve-2017-14322
CVE-2017-14322 Interspire Email Marketer (emailmarketer) Exploit
 h4md153v63n/cve-2022-40348_intern-record-system-cross-site-scripting-v1.0-vulnerability-unauthenticated
CVE-2022-40348: Intern Record System - 'name' and 'email' Cross-site Scripting (Unauthenticated)
 h4md153v63n/cve-2022-40347_intern-record-system-phone-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40347: Intern Record System - 'phone', 'email', 'deptType' and 'name' SQL Injection (Unauthenticated)
 duy-31/cve-2023-7028
An issue has been discovered in GitLab CE/EE affecting all versions from 16.1 prior to 16.1.6, 16.2 prior to 16.2.9, 16.3 prior to 16.3.7, 16.4 prior…
 blue-chocolates/cve-2016-10033
Exploit for CVE-2016-10033, a remote code execution vulnerability in PHPMailer, enabling unauthenticated attackers to execute arbitrary code via…
 chsxthwik/cve-2024-2876
Proof-of-concept exploit for CVE-2024-2876, an unauthenticated SQL injection vulnerability in the Email Subscribers plugin for WordPress, enabling…
 segunakinsoyinu/cve-2024-42009-roundcube-xss
Stored XSS exploit for Roundcube Webmail ≤1.6.6 (CVE-2024-42009) with zero-click email exfiltration via CSS animation event handlers. Includes SMTP…
 rootxsushant/cve-2023-5561-poc-updated
Updated POC for Unauth Post Author Email Disclosures WordPress CVE-2023-5561
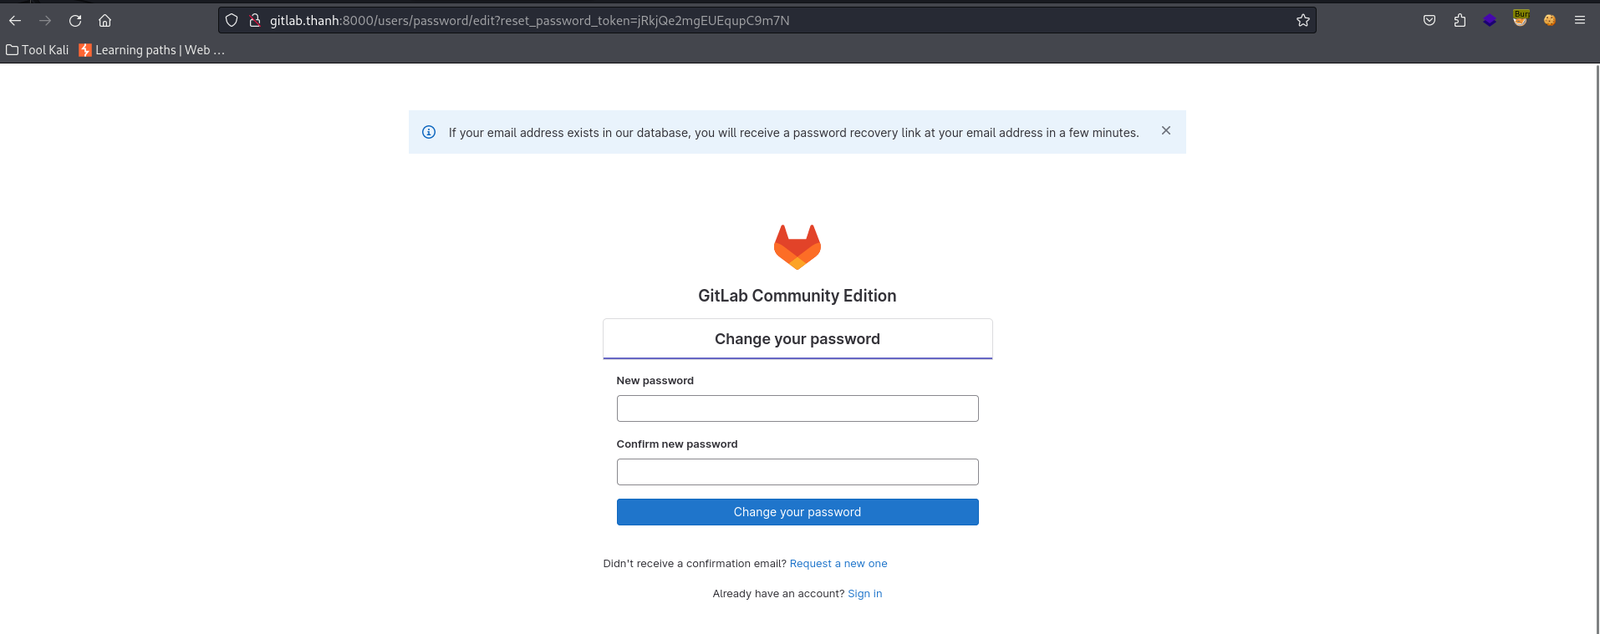 thanhlam-attt/cve-2023-7028
Exploit for GitLab account takeover via CVE-2023-7028, demonstrating password reset bypass by injecting attacker email to receive reset token.
 hackeremmen/gitlab-exploit
Exploit for GitLab CVE-2023-7028: password reset bypass via dual email verification, allowing unauthorized account takeover. Includes affected…
 0x00phantom-hat/cve-2026-12400-exploit
Authenticated WordPress IDOR exploit for CVE-2026-12400; enumerates FlowForms REST form IDs and modifies form content or hijacks email notifications.