
CVE-2026-24055-OAuth-Langfuse
 imzanggg/cve-2026-24055-oauth-langfuse
api-security-testingeducationexploitation+3
imzanggg/cve-2026-24055-oauth-langfuse bandit92/cve2022-1388_testapi
A Test API for testing the POC against CVE-2022-1388
 loneyers/spring4shell
Spring4Shell , Spring Framework RCE (CVE-2022-22965) , Burpsuite Plugin
 passwa11/cve-2024-26026
CVE-2024-26026: BIG-IP Next Central Manager API UNAUTHENTICATED SQL INJECTION
 0xmaximus/apache-commons-text-cve-2022-42889
Burp Bounty profile for detecting Apache Text4Shell (CVE-2022-42889), an RCE in Commons Text 1.5-1.9, by scanning HTTP requests.
 null200ok/cve-2026-27944
CVE-2026-27944 - Nginx UI Unauthenticated Backup Download & Decryption
 kabiri-labs/cve-2024-40094
This script exploits the CVE-2024-40094 vulnerability in graphql-java
 punitdarji/gitlab-cve-2026-19478
Dockerized exploit lab and script for CVE-2026-19478, a critical unauthenticated GitLab GraphQL code injection enabling arbitrary Ruby method calls,…
 sevdakhidirova/cve-2025-32375-poc
Python proof-of-concept exploit for CVE-2025-32375 in BentoML, demonstrating and validating the vulnerability against affected deployments.
 loaxert/cve-2025-59528-poc
PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB
 george0papasotiriou/cve-2026-5432-graphql-batching-alias-confusion-sql-injection
Demonstrates a critical GraphQL batching alias-confusion SQL injection (CVE-2026-5432) with a vulnerable Node.js server and Python exploit for…
 biitts/cve-2026-54917-seaweedfs-cross-bucket-traversal
PoC + analysis for CVE-2026-54917 — SeaweedFS S3 gateway cross-bucket path traversal (CVSS 10.0, <4.30). Read/write any bucket via .. in the object…
 hunt-benito/bring-your-own-key-cve-2026-73678-unauthenticated-rce-in-mindsdb-cowork
PoC exploit for CVE-2026-73678: unauthenticated RCE in MindsDB Cowork via attacker-supplied LLM key and unsandboxed scratchpad exec to run OS…
 cuteecat/cve-2026-9198
CVE-2026-9198利用代码
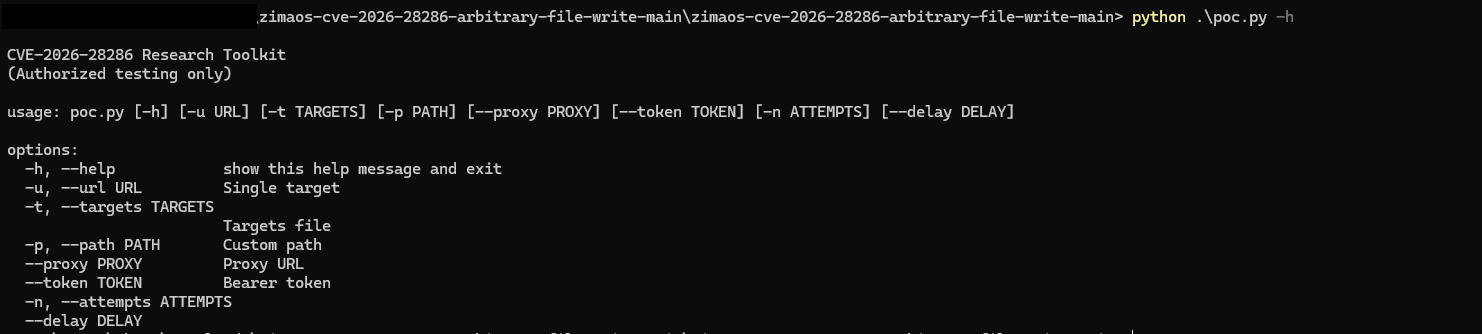 rushi9/zimaos-cve-2026-28286-arbitrary-file-write
PoC and verification toolkit for CVE-2026-28286, an arbitrary file write vulnerability in ZimaOS, exploiting API misconfiguration to write files…
 oscerd/cve-2026-48206
Reproducer for CVE-2026-48206: Apache Camel camel-jira IssueKey (and other non-Camel-prefixed) header injection driving arbitrary JIRA issue…
 oscerd/cve-2026-46592
Reproducer for CVE-2026-46592: Apache Camel camel-cxf operationName header injection redirecting the invoked SOAP operation (confused deputy) from a…
 foxer131/cve-2026-70481
Proof-of-concept exploit for an authorization flaw in Open WebUI that lets low-privileged users edit and delete other members' channel messages via…