
RedTeam_toolkit
 signorrayan/redteam_toolkit
Red Team Toolkit is an Open-Source Django Offensive Web-App which is keeping the useful offensive tools used in the red-teaming together.
exploitationinformation-gatheringpassword-attacks+5
572
signorrayan/redteam_toolkitRed Team Toolkit is an Open-Source Django Offensive Web-App which is keeping the useful offensive tools used in the red-teaming together.
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent
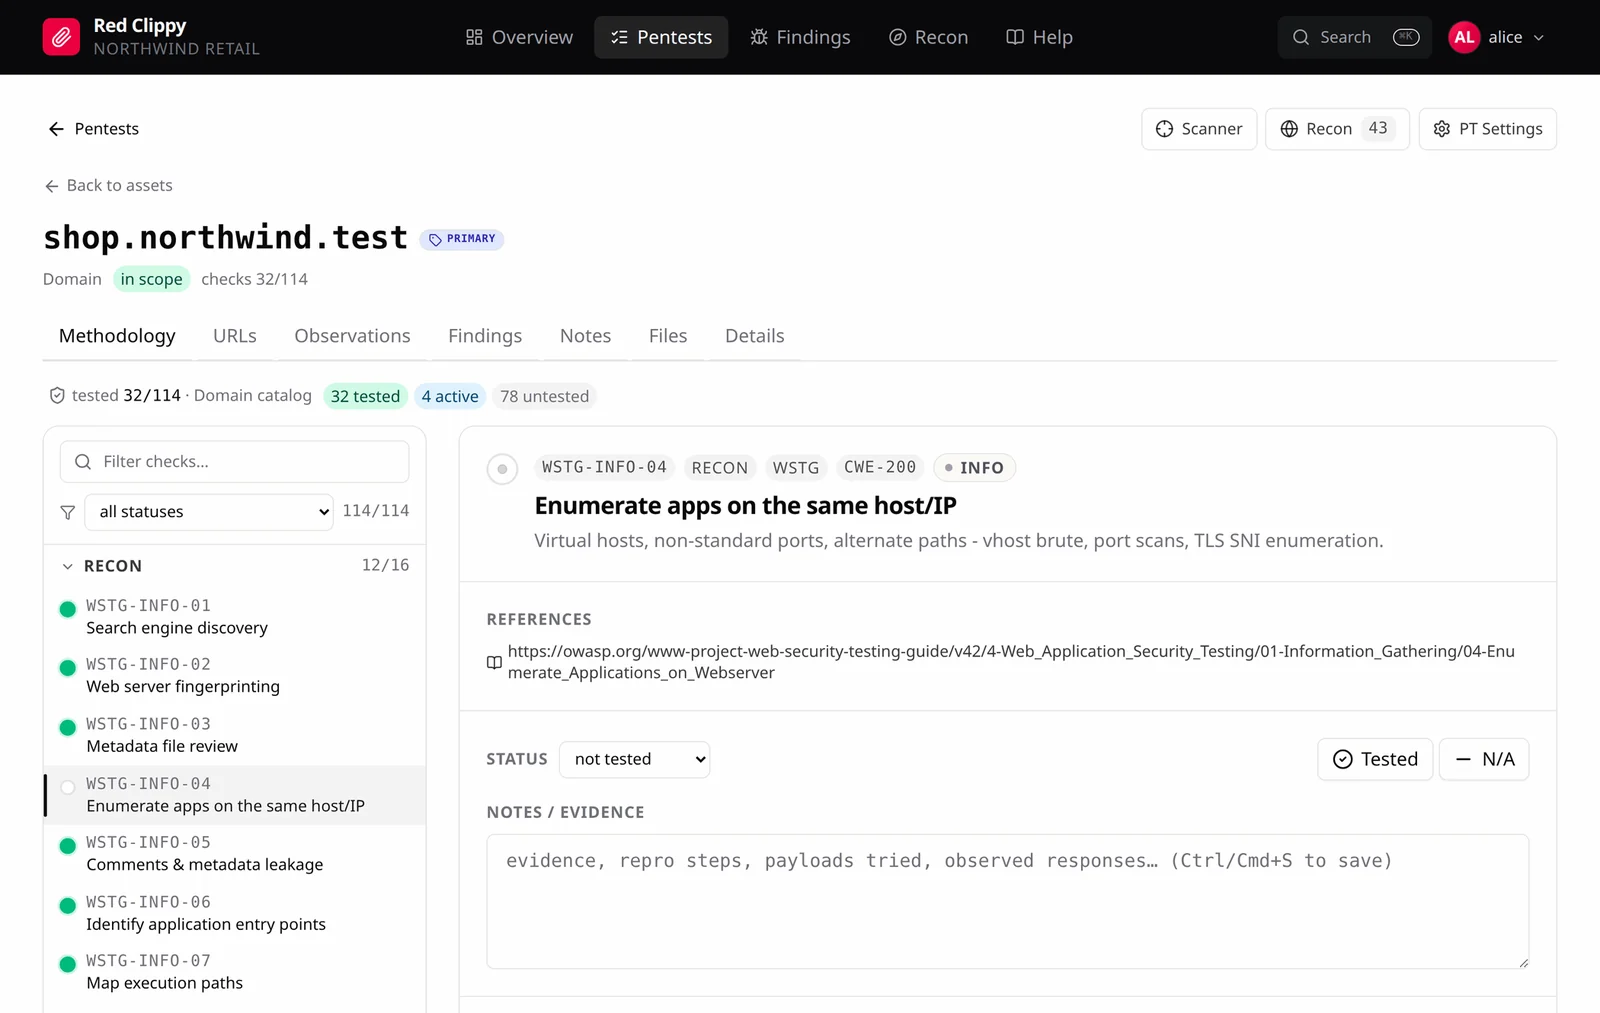 cspf-founder/red-clippy
open-source pentest management built to be operated by an AI agent
 649/pingpon-exploit
Exploit for Mass Remote Code Execution on GPON home routers (CVE-2018-10562) obtained from Shodan.
 tahtaciburak/cve-2021-41277
PoC for CVE-2021-41277
 llhala/cve-2021-21311
Proof-of-concept for CVE-2021-21311, a server-side request forgery in Adminer before 4.7.9, demonstrating SSRF exploitation in PHP database…
 gobysec/cve-2023-28432
Exploit for CVE-2023-28432, a sensitive information disclosure vulnerability in MinIO's verify interface, allowing attackers to read system…
 dimitrinl/ctx-cve-2020-7473
Citrix Sharefile vulnerability check and fast research details
 abraxas/gitea-restore-file-open
Proof-of-concept for a Gitea restore-repo file:// local file inclusion (CWE-73) that copies symlink targets outside an untrusted dump into release…
 abraxas/forgejo-restore-file-open
Forgejo 16.0.5 - High - Remote - File read - restore-repo follows dump-side file:// into attachments
 nurdilin/cve-2018-16706
Or how I turn off my TV via a cronjob
 gh-ost00/cve-2024-24809-proof-of-concept
Critical Flaws in Traccar GPS System Expose Users to Remote Attacks
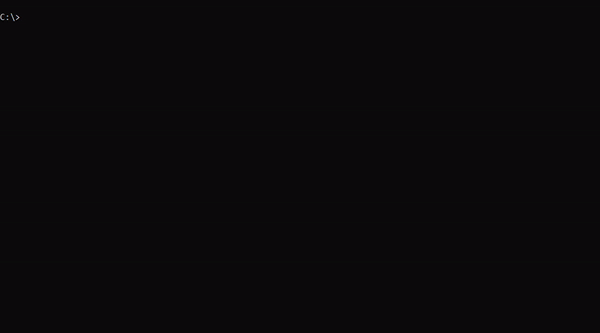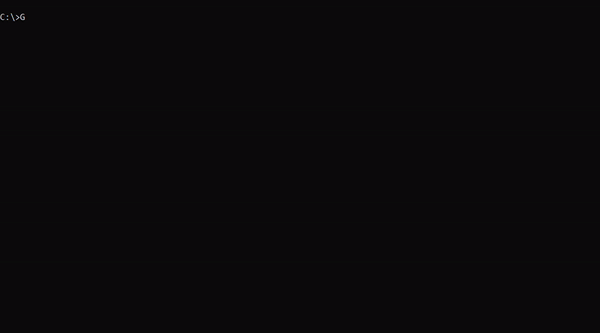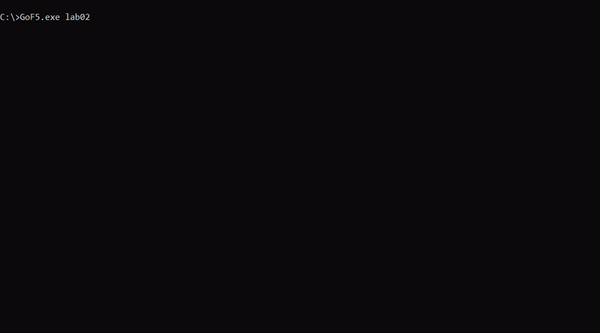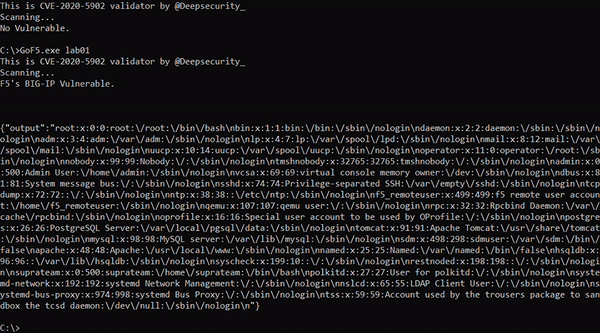 deepsecurity-pe/gof5-cve-2020-5902
Script para validar CVE-2020-5902 hecho en Go.
 0x0jackal/cve-2022-24716
Arbitrary File Disclosure Vulnerability in Icinga Web 2 <2.8.6, <2.9.6, <2.10
 itsshotgun/chrome_v8_cve_checker
Checks if your Chrome version is vulnerable to CVE-2025-5419, from the browser
 mrnazu/cve-2020-13405
MicroWeber Unauthenticated User Database Disclosure - CVE-2020-13405
 nxploited/cve-2026-39987
marimo is a reactive Python notebook. Prior to 0.23.0, Marimo has a Pre-Auth RCE vulnerability
 aymenbouferroum/cve-2021-43798_exploit
Exploit for Grafana directory traversal (CVE-2021-43798) allowing local file read via crafted plugin path. Includes usage instructions and references.