

CVE-2023-22974
 gbrsh/cve-2023-22974
Proof-of-concept exploit for CVE-2023-22974 enabling arbitrary file read in OpenEMR versions prior to 7.0.0. Useful for security testing and…
exploitationinformation-gatheringpenetration-testing+2
10
gbrsh/cve-2023-22974Proof-of-concept exploit for CVE-2023-22974 enabling arbitrary file read in OpenEMR versions prior to 7.0.0. Useful for security testing and…
 navreet1425/cve-2021-34621
Proof-of-concept exploit for CVE-2021-34621, demonstrating a specific vulnerability for security testing and validation purposes.
 mekoko/cve-2020-4276
Proof-of-concept exploit for CVE-2020-4276, targeting a specific vulnerability in affected software for security testing and validation.
 bigb0x/cve-2024-34470
POC and bulk scanner for CVE-2024-34470
 idkwim/cve-2018-8420
Proof-of-concept exploit for CVE-2018-8420, demonstrating remote code execution via a crafted web request. Intended for security testing and…
 xkore123/cpanel-cve-2023-29489
Proof-of-concept exploit for cPanel XSS vulnerability (CVE-2023-29489) with a ready-to-use payload for security testing and validation.
 itsgiddd/cve-2023-41991
Proof-of-concept exploit for CVE-2023-41991, demonstrating the vulnerability and providing a working exploit for security testing and validation.
 praveensutar/cve-2019-6263-joomla-poc
Proof-of-concept exploit for CVE-2019-6263 targeting Joomla CMS. Demonstrates remote code execution via crafted HTTP requests for security testing…
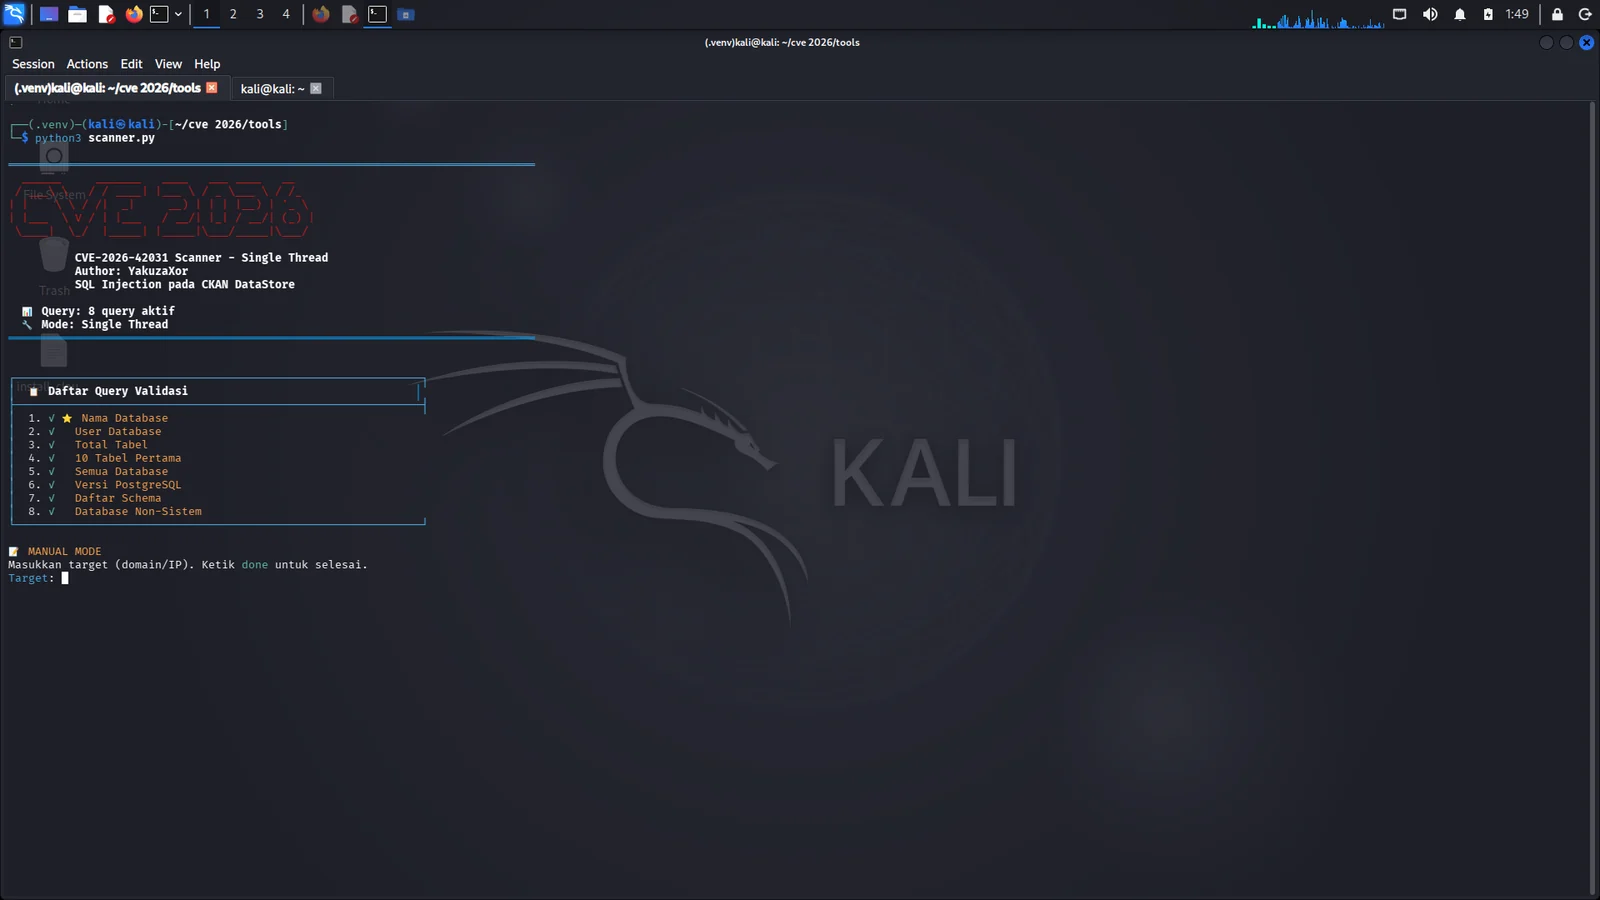 ddrvahandzo90-hue/cve-2026-42031-sql-injection-scanner
Automated SQL injection scanner for CKAN DataStore, detecting and validating CVE-2026-42031 with multi-target scanning, data dumping, and report…
 mr-r00t11/cve-2024-4879
CVE-2024-4879.py is a Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the…
 hexspectrum1/cve-2024-7014
Proof-of-concept exploit for CVE-2024-7014, demonstrating the vulnerability and providing a reference for security testing and patch validation.
 tiger-foxx/exploit-react-cve-2025-55182
This tool is a Proof of Concept (PoC) intended for security research and educational purposes only. Using this tool on systems without explicit…
 initroot/cve-2005-1794scanner
Scanner for network for CVE-2005-1794.
 cazzysoci/cve-2026-48908
Proof-of-concept exploit for CVE-2026-48908, demonstrating the vulnerability and providing a basis for security testing and patch validation.
 byte16384/cve-2026-49492-poc
Proof-of-concept exploit for CVE-2026-49492, demonstrating the vulnerability and providing a working exploit for security testing and validation.
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 dennywise/cve-2026-51833-public-disclosure
Technical advisory and proof-of-concept for CVE-2026-51833, detailing the vulnerability, exploitation vectors, and mitigation steps for security…
 shinthink/cve-2026-27966
Pre-auth RCE scanner for Langflow < 1.8.0 — Route Injection + Vertex Injection → Code Execution (CVSS 9.8)