CVE-2026-63030-CVE-2026-60137

Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…

Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…

PoC checker for CVE-2022-31749 exploiting a parameter injection vulnerability in WatchGuard SSH interface to exfiltrate hashed user passwords via FTP.

CVE-2022-21392: Local Privilege Escalation via NMR SUID in Oracle Enterprise Manager

Crestron AirMedia AM-100 Traversal and Hashdump Metasploit Modules

PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…

Proof-of-concept exploit for CVE-2025-24054, a Windows Library (.library-ms) NTLM hash disclosure vulnerability. Generates a malicious .library-ms…


Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…

Unauthenticated Sensitive Information Disclosure

CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.

Open Web Analytics 1.7.3 - Remote Code Execution

Writeup of TryHackMe's Moniker Link room, exploiting CVE-2024-21413 to bypass Outlook Protected View and capture NTLMv2 hashes via crafted Moniker…

Proof-of-concept exploit for CVE-2026-40083, a SQL injection in Cacti managers.php allowing authenticated users to extract MySQL databases, user…

Proof-of-concept exploit for CVE-2024-24919, a Check Point path traversal allowing arbitrary file read (e.g., /etc/shadow) via crafted HTTPS POST…

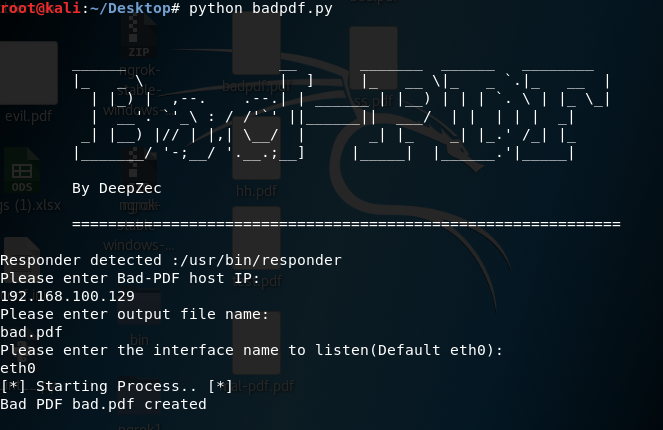
Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.

Initialized & connected PostgreSQL to Metasploit. Reconnoitered 10.1.16.0/24 with Nmap and imported results. Enumerated hosts/services using SYN, SMB…

Python 3 exploit for CVE-2019-9053, an unauthenticated time-based blind SQL injection in CMS Made Simple < 2.2.10, extracting admin credentials and…

This is an automated exploitation script for the Hack The Box machine *Titanic*. It extracts Gitea user hashes via LFI, assists in cracking them, and…