
CVE-2023-23397
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
email-securityexploitationpassword-attacks+3
132
trackflaw/cve-2023-23397Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
 eeenvik1/cve-2023-51764
Proof-of-concept exploit for CVE-2023-51764 SMTP smuggling vulnerability in Postfix, enabling email spoofing and message injection via crafted SMTP…
 romain-deperne/cve-2026-34975
CRLF email header injection in Plunk raw MIME construction — CVE-2026-34975 / CVSS 8.5
 dshabani96/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP email delivery, malicious RTF attachment generation, and optional…
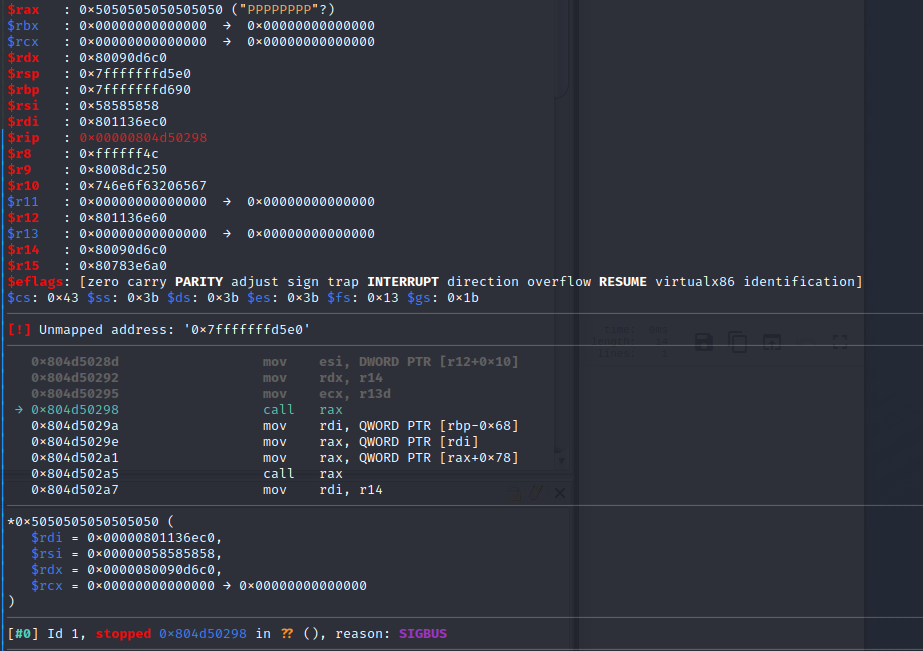 ly1g3/cisco-cve-2023-31488
Cisco Email Security Appliance: Email to zero-click RCE as root - Remote Code Execution/Memory Corruption/ROP-chain
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 0nyx-my7h/cve-2025-43920
PoC and technical write-up for CVE-2025-43920, a remote command injection in GNU Mailman 2.1.39's external archiver allowing unauthenticated code…
 networksecure/cve-2020-14066
Proof-of-concept exploit for CVE-2020-14066 targeting insecure permissions in Icewarp Email Server 12.3.0.1, enabling privilege escalation or…
 cscli/cve-2017-5223
Proof-of-concept exploit for CVE-2017-5223 demonstrating arbitrary file read via PHPMailer's attachment and email content injection.
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
 jacquesquail/cve-2023-23397
Proof-of-concept exploit for CVE-2023-23397, a Microsoft Outlook privilege escalation vulnerability. Sends a crafted email with a malicious UNC path…
 defrancescojp/cve-2013-2977
Proof-of-concept exploit for CVE-2013-2977: IBM Lotus Notes PNG integer overflow leading to arbitrary code execution when a malicious email is opened…
 gyaansastra/cve-2023-21716
A vulnerability within Microsoft Office's wwlib allows attackers to achieve remote code execution with the privileges of the victim that opens a…
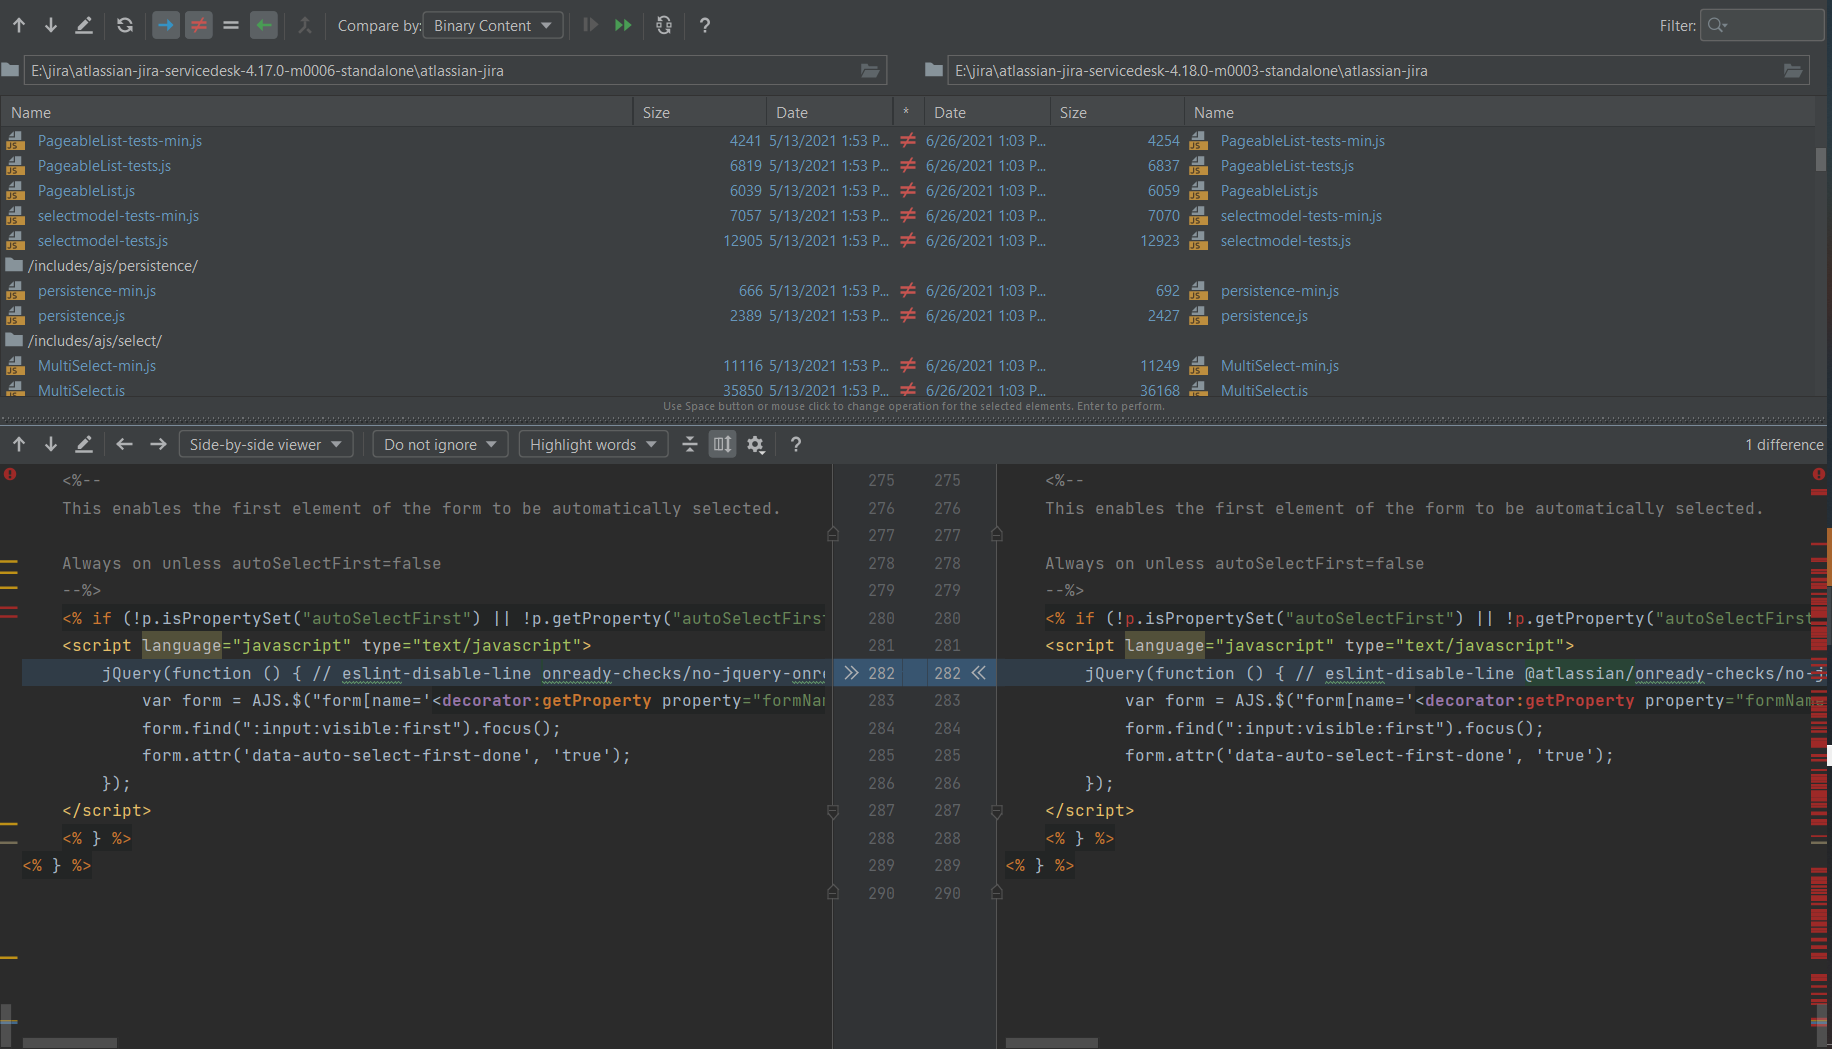 petrusviet/cve-2021-39115
Template Injection in Email Templates leads to code execution on Jira Service Management Server
 sofianeelhor/cve-2023-22621-poc
CVE-2023-22621: SSTI to RCE by Exploiting Email Templates affecting Strapi Versions <=4.5.5
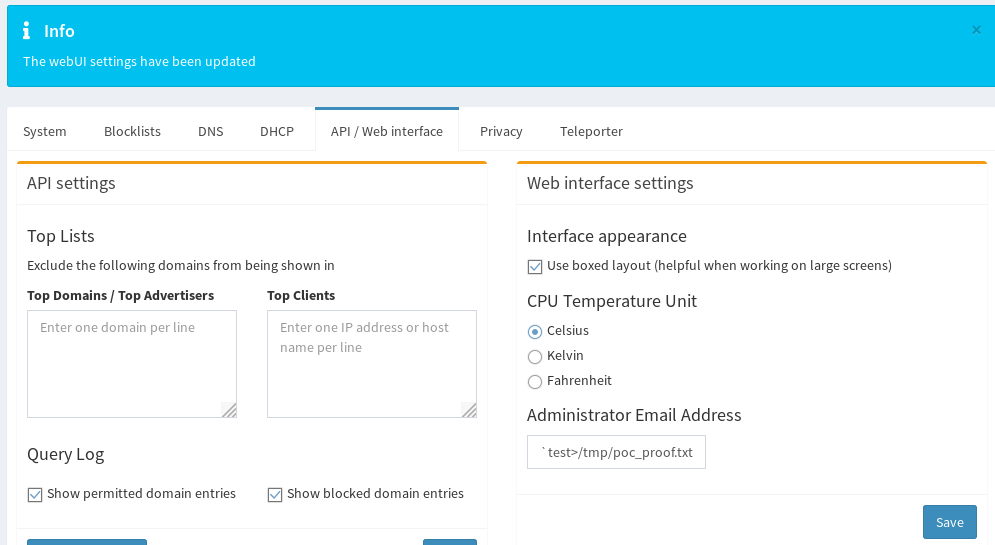 pr0tean/cve-2019-13051
Proof-of-concept exploit for Pi-Hole AdminLTE command injection (CVE-2019-13051) enabling remote root access via email field injection and cron-based…
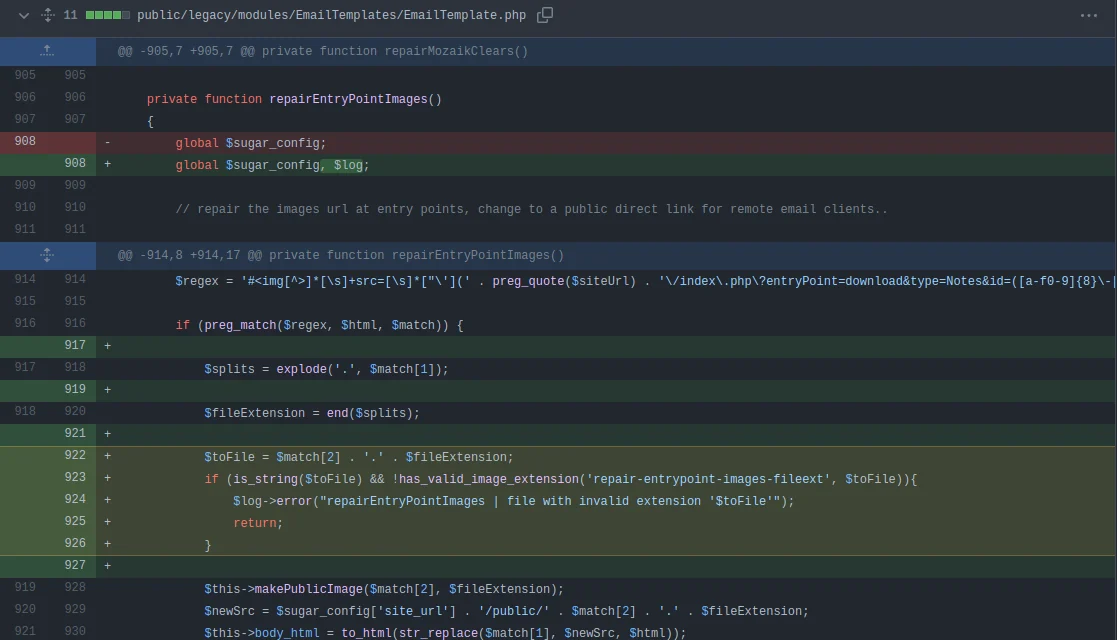 manuelz120/cve-2021-45897
Authenticated RCE exploit for SuiteCRM <= 8.0.1 via email template image upload, planting a PHP webshell for remote command execution.
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…