
CVE-2025-60787_PoC
 lil0xplorer/cve-2025-60787_poc
Authenticated RCE exploit for MotionEye <= 0.43.1b4 via client-side validation bypass on the image_file_name field. Includes reverse shell payload…
exploitationpenetration-testingred-teaming+3
2
lil0xplorer/cve-2025-60787_pocAuthenticated RCE exploit for MotionEye <= 0.43.1b4 via client-side validation bypass on the image_file_name field. Includes reverse shell payload…
 e1st/cve-2025-56015
Proof-of-concept exploit for CVE-2025-56015, a sandbox escape and RCE in GenieACS. Automates malicious provision creation, preset mapping, and…
 davuxvi/cve-2023-27163
Proof-of-concept exploit for CVE-2023-27163, a Server-Side Request Forgery (SSRF) vulnerability in request-baskets up to v1.2.1. Includes automated…
 charlesgargasson/cve-2023-41425
XSS-to-RCE exploit for Wonder CMS 3.2.0–3.4.2 with automated payload delivery, reverse shell, and cookie theft via malicious theme installation.
 lonehand/oracle-weblogic-cve-2017-10271-master
Exploit for Oracle WebLogic CVE-2017-10271 (wls-wsat RCE bypass) with PoC scripts for remote command execution and obtaining a cmd shell on…
 jaychouzzk/cve-2019-0193-exp
Proof-of-concept exploit for CVE-2019-0193 targeting Apache Solr's DataImportHandler, enabling remote code execution via crafted XML data sources…
 joeymeech/cve-2022-0847-exploit-implementation
Using CVE-2022-0847, "Dirty Pipe Exploit", to pop a reverse bash shell for arbitrary code execution on a foreign machine.
 darnabin/cve-2022-36446-webmin-rce
Authenticated remote code execution exploit for Webmin < 1.997 via the Software Package Updates module. Injects arbitrary commands as root through an…
 delt-a/cve-2024-36401-poc
Unauthenticated RCE exploit for GeoServer (CVE-2024-36401) via OGC filter XPath injection. Supports reverse shell and blind command execution with…
 fabse-hack/cve-2024-3829
Python exploit for CVE-2024-3829 targeting Qdrant snapshot import/export, enabling file read, file write, and reverse shell execution via symlink…
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 afifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744
Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.
 diamorphine666/cve-2026-33017-exploit
Exploit for unauthenticated remote code execution in Langflow <1.9.0 via the build_public_tmp endpoint, delivering a reverse shell for authorized…
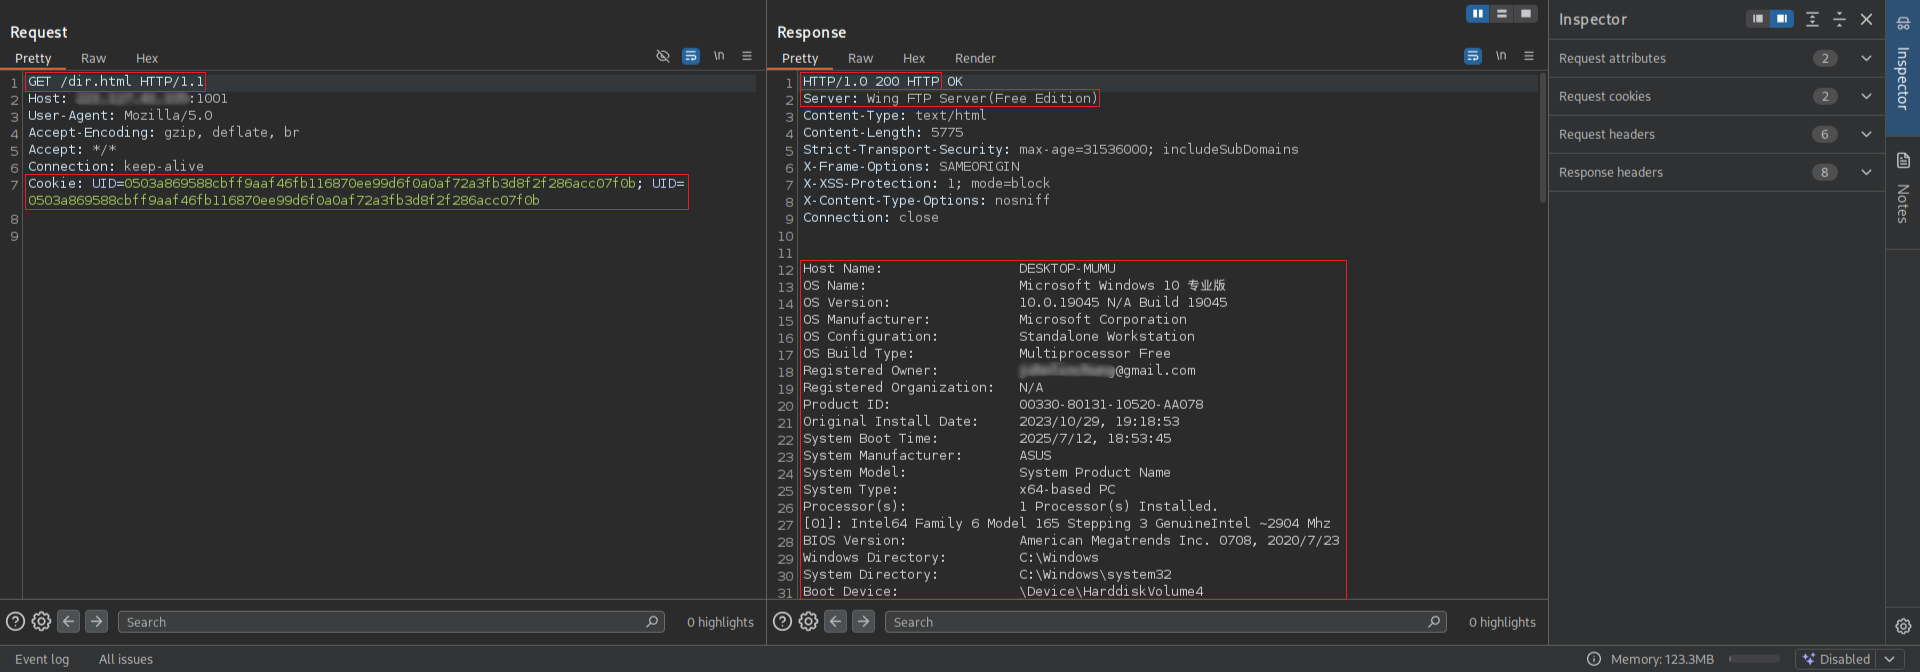 r0otk3r/cve-2025-47812
Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…
 reggyraider/cve-2023-46604-rce
CVE-2023-46604-RCE exploit with Linux reverse shell payload
 kaleth4/cve-2025-69985
PoC exploit for CVE-2025-69985: authentication bypass leading to RCE in FUXA SCADA ≤1.2.8. Includes a modular Python exploit with interactive shell,…
 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
 jf-gondim/mcp-pwn
PoC exploit for CVE-2026-23744 — unauthenticated RCE in MCPJam Inspector via unvalidated serverConfig command injection on /api/mcp/connect, enabling…