
CVE-2025-48461
 joelczk/cve-2025-48461
Technical disclosure of a predictable session cookie vulnerability (CVE-2025-48461) in Advantech WISE-4060 IoT portal, enabling bruteforce…
authenticationexploitationiot-security+3
joelczk/cve-2025-48461Technical disclosure of a predictable session cookie vulnerability (CVE-2025-48461) in Advantech WISE-4060 IoT portal, enabling bruteforce…
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 aseemjakhar/kcmd
Kankun Smart Socket Hijacker and Sniffer. The kankun smart socket and its mobile app use a hardcoded AES 256 bit key to encrypt and decrypt…

 exploitwritter/cve-2022-25064
This script exploits a remote command execution vulnerability in the TPLink WR840N router, using the configure function IPv6 protocol.
 cappricio-securities/cve-2024-5947
Deep Sea Electronics DSE855 - Authentication Bypass
 exploitwritter/cve-2022-25062
This script exploits a vulnerability (IoF) in the TPLink WR840N router, using a field for injecting code in the module DNS.
 str0ng4le/cve-2022-30114
Proof-of-concept exploit for CVE-2022-30114, a heap-based buffer overflow in Fastweb FastGate routers. Sends a crafted HTTP Authorization header to…
 db44k/cve-2020-12124
Proof-of-concept exploit for CVE-2020-12124, a command injection vulnerability in Wavlink WN530H4 routers via the /cgi-bin/live_api.cgi endpoint,…

 vanlam2001/netis-n5vn-ac1200-dos
Proof-of-concept exploit for a buffer overflow vulnerability (CVE-2024-44596) in Netis N5VN AC1200 routers, causing a denial of service by crashing…
 miguelhamal/cve-2019-19393
Proof-of-concept for stored XSS vulnerability in Rittal CMC PU III web management interface, enabling persistent client-side script injection before…
 tpdlshdmlrkfmcla/backdoor.mirai.helloworld
backdoor.mirai.helloworld cve2018-20561, cve-2018-10562 해킹
 oiivr/turvan6rkus-cve-2024-3273
Turvanõrkuse CVE 2024 3273 analüüs: D-Link seadmete käsusüst
 cr0n1c/dlink_shell_poc
Dlink 615/815 shell PoC
 bytereaper77/cve-2025-9090
Command Injection in Tenda AC20 16.03.08.12 (/goform/telnet)
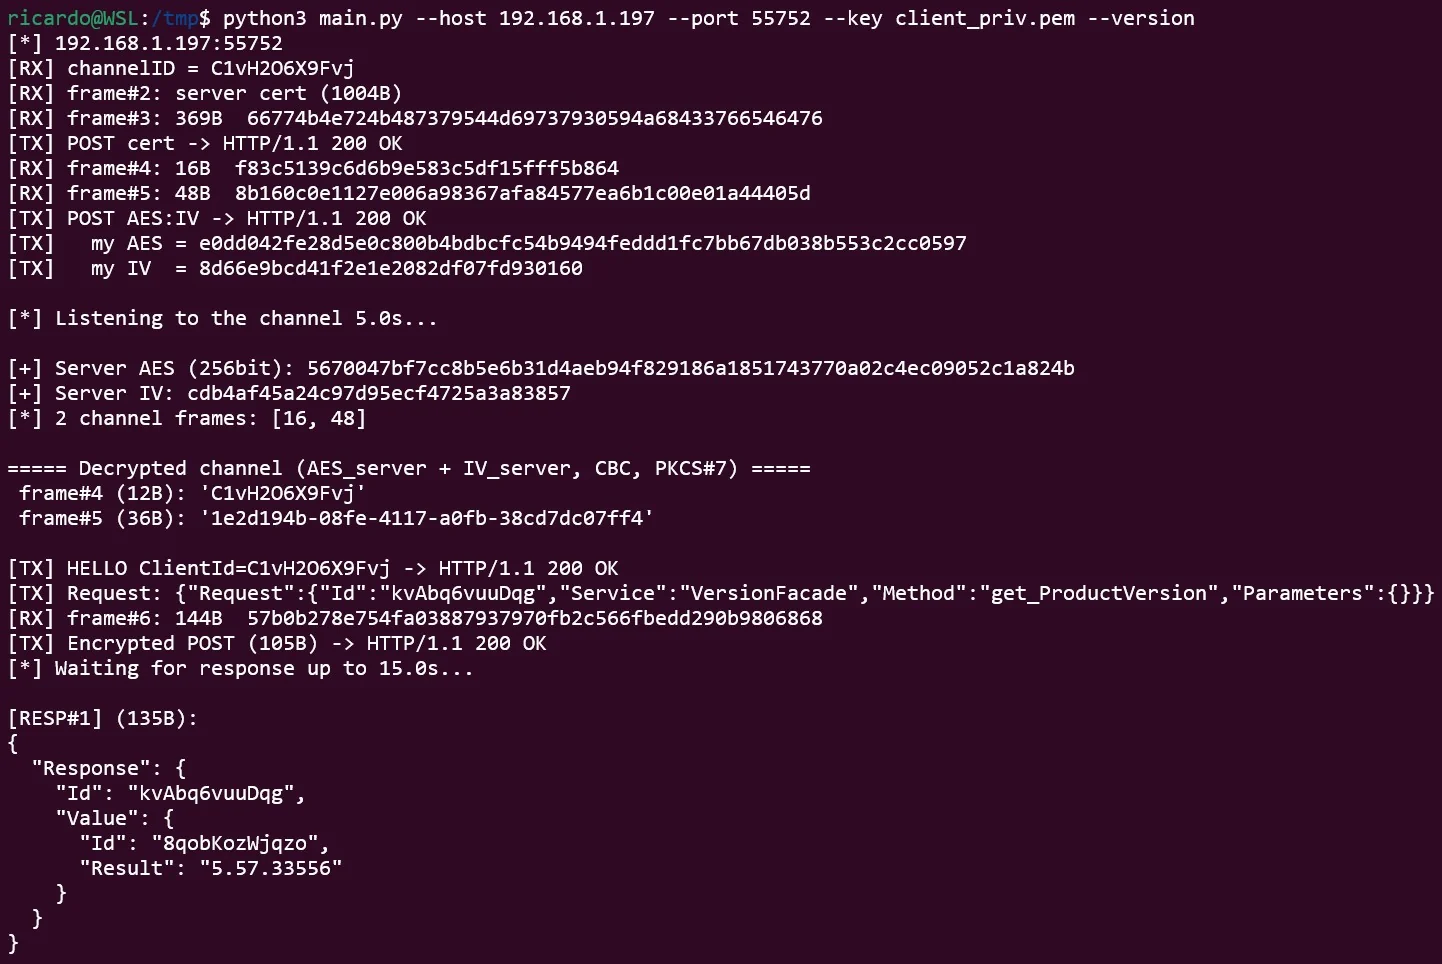 ricardojoserf/axis-rce
Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)