
Drupalgedon3
 1337g/drupalgedon3
POC to test/exploit drupal vulnerability SA-CORE-2018-004 / CVE-2018-7602
exploitationpenetration-testingvulnerability-analysis+2
68 years ago
1337g/drupalgedon3POC to test/exploit drupal vulnerability SA-CORE-2018-004 / CVE-2018-7602
 s1lkys/cve-2021-24884
If an authenticated user who is able to edit Wordpress PHP code in any kind, clicks a malicious link, PHP code can be edited through XSS in…
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 zznop/drow
Injects code into ELF executables post-build
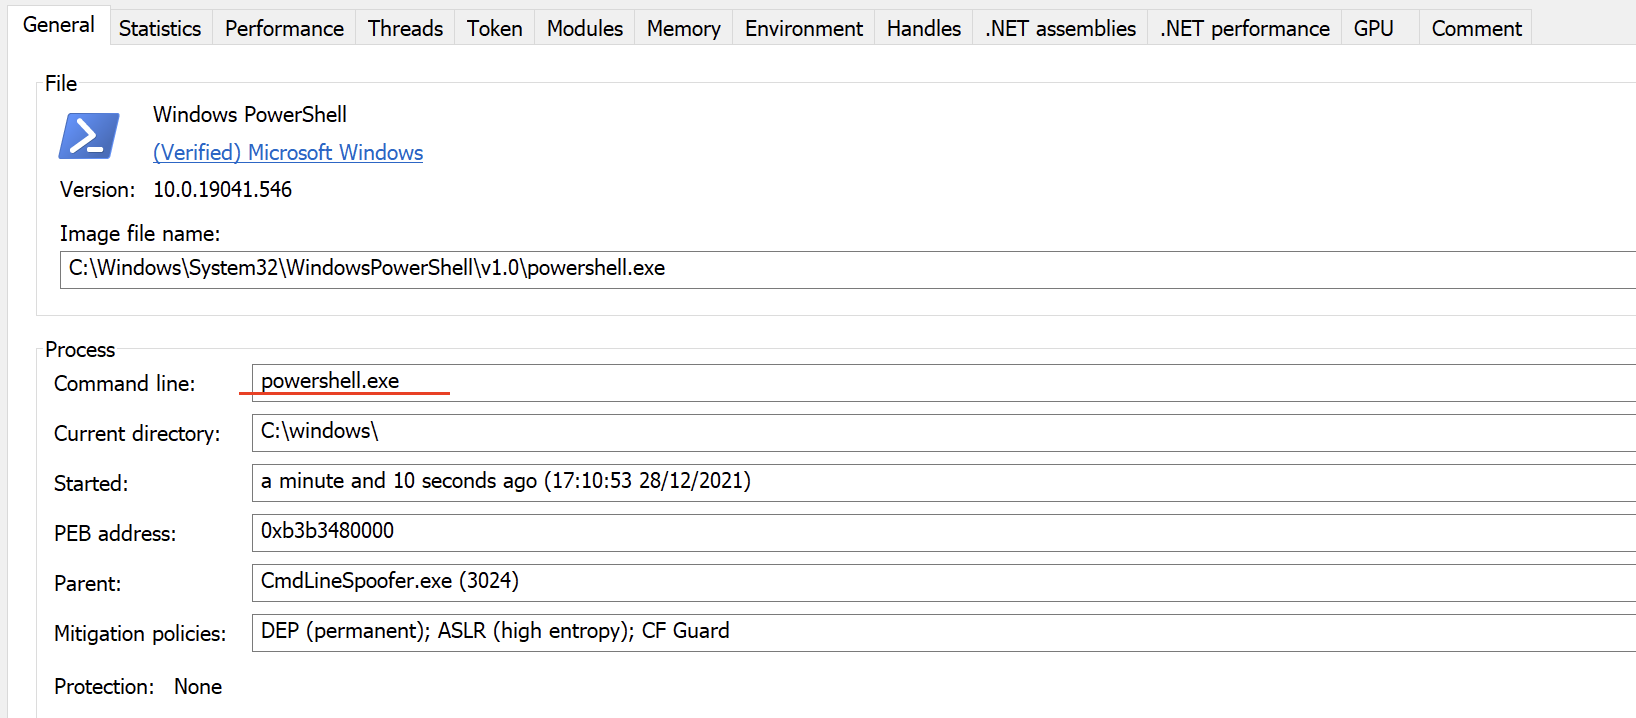 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 0xblackash/cve-2026-72898
CVE-2026-72898
 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
 dnr6419/cve-2022-23046
SQL Injection Vulnerability on PhpIPAM v1.4.4
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 skraft9/cve-2025-29471
Stored XSS in Nagios Log Server 2024R1.3.1
 deepsecurityresearch/cve-2026-2586
Authenticated EL injection exploit for GlassFish/Payara admin console enabling remote command execution via crafted parameters in the virtual server…
 keraattin/cve-2026-35517
Detection scripts for Pi-hole FTLDNS RCE (CVE-2026-35517) via newline injection, including Python scanner and Nmap NSE script for version-based…
 mbadanoiu/cve-2022-23861
CVE-2022-23861: Multiple Stored Cross-Site Scripting in YSoft SafeQ
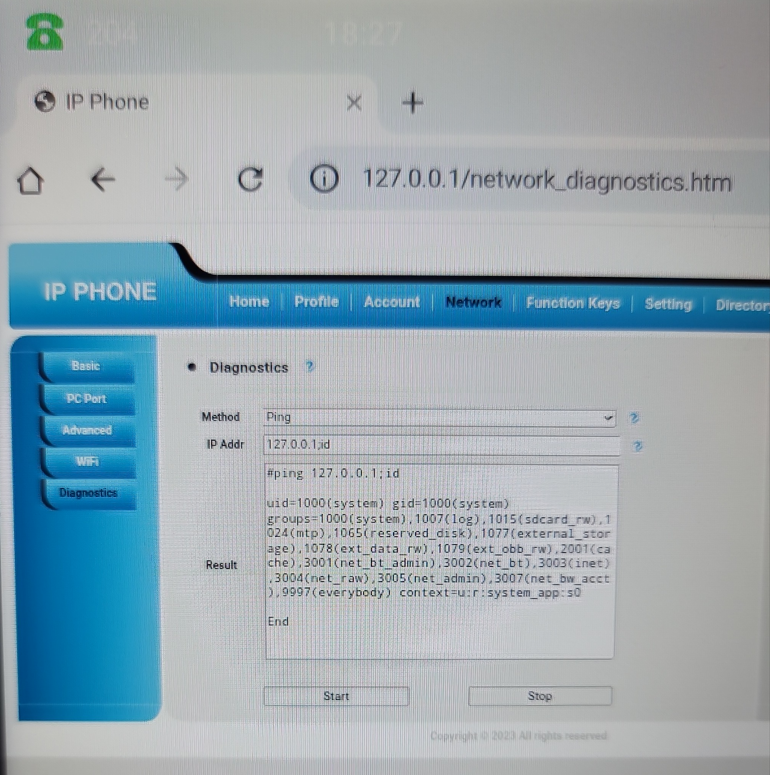 restdone/cve-2025-57457
Proof-of-concept for OS command injection in Curo UC300 IP phone admin panel, demonstrating arbitrary command execution via the IP Addr parameter.
 boroeurnprach/cve-2026-23947-poc
Proof-of-concept demonstrating arbitrary code execution in Orval via malicious OpenAPI fields, with setup, exploit steps, and remediation guidance.
 d34dun1c02n/cve-2023-31705
Proof-of-concept for a reflected XSS vulnerability in Sourcecodester Task Reminder System 1.0, demonstrating authenticated remote code execution via…
