
bug-reaper
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
api-security-testingctfeducation+8
71
shaniidev/bug-reaperWeb2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 dinosn/gitlab-cve-2026-19478-lab
Reproducible A/B lab + safe PoC for GitLab CVE-2026-19478 / CVE-2026-19650 (GraphQL @gl_introduced)
 boreas37/cve-2026-34910-poc
CVE-2026-34910/34909 — UniFi OS unauth RCE + file read via ..%2f auth bypass (CVSS 10.0, KEV, Mirai ITW)
 b0rn2d/spring-cloud-gateway-nacos
Nacos下Spring-Cloud-Gateway CVE-2022-22947利用环境
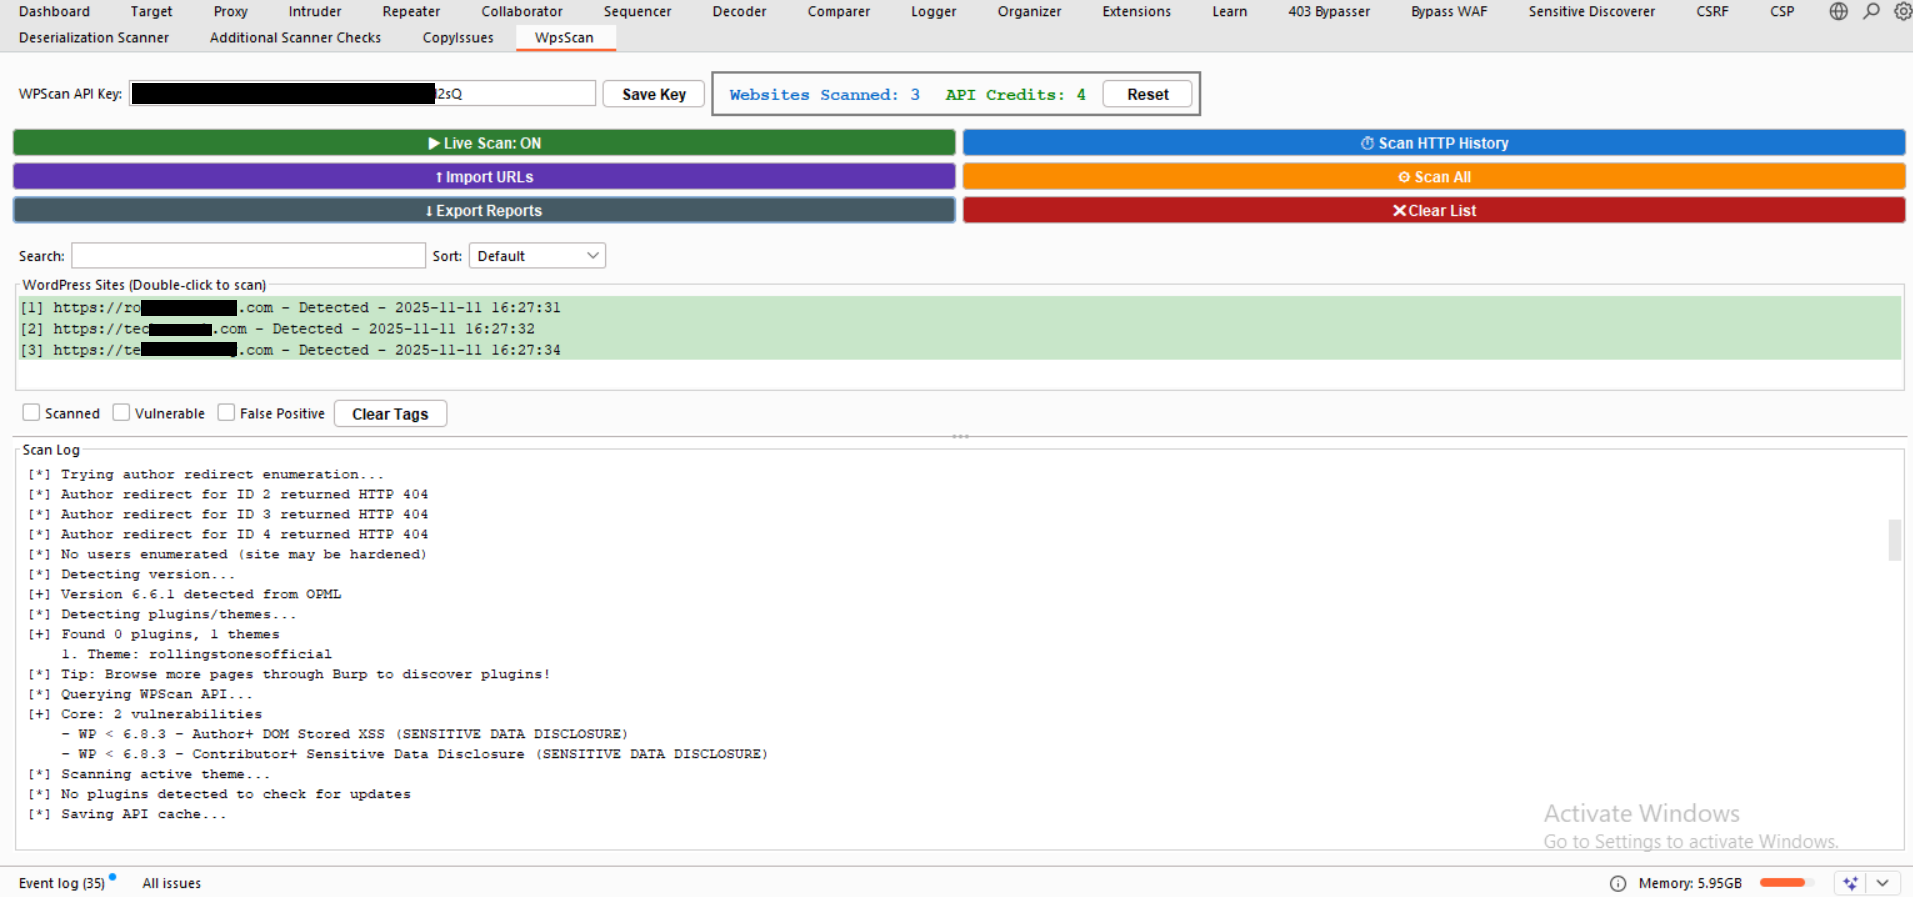 teycir/burpwpsscan
Burp extension for wordpress security scanning
 hunzi0/cve-2022-22947-rce_poc
批量url检测Spring-Cloud-Gateway-CVE-2022-22947
 yutusec/apisix_crack
Apisix系列漏洞:未授权漏洞(CVE-2021-45232)、默认秘钥(CVE-2020-13945)批量探测。
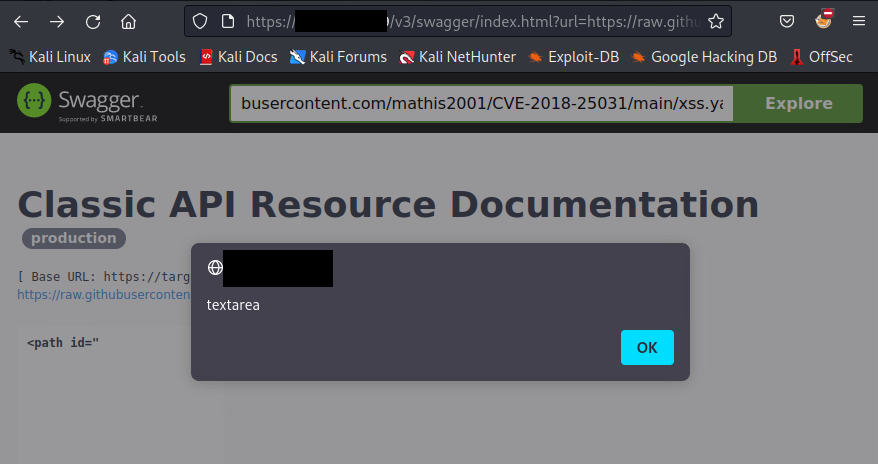 mathis2001/cve-2018-25031
CVE-2018-25031 tests
 randomrobbiebf/cve-2023-32117
Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 yutusec/spel
Spring Cloud Gateway Actuator API SpEL表达式注入命令执行(CVE-2022-22947)批量检测工具
 k3ystr0k3r/cve-2021-4191-exploit
A PoC exploit for CVE-2021-4191 - GitLab User Enumeration.
 punitdarji/gitlab-cve-2026-19478
Dockerized exploit lab and script for CVE-2026-19478, a critical unauthenticated GitLab GraphQL code injection enabling arbitrary Ruby method calls,…
 zavisco/cve-2026-64849.yaml
Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…
 hunt-benito/your-bot-my-inbox-cve-2026-68929-fastgpt-unauthenticated-wechat-channel-hijack
Proof-of-concept exploit for CVE-2026-68929, demonstrating unauthenticated cross-tenant takeover of FastGPT WeChat channels via public shareId,…
 hunt-benito/bring-your-own-key-cve-2026-73678-unauthenticated-rce-in-mindsdb-cowork
PoC exploit for CVE-2026-73678: unauthenticated RCE in MindsDB Cowork via attacker-supplied LLM key and unsandboxed scratchpad exec to run OS…
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…
 kovachvl/cve-2026-54356
Proof-of-concept exploit and advisory for CVE-2026-54356, a Budibase missing-authorization flaw that lets low-privilege users mint S3 pre-signed…