CVE-2019-9053-CMS-Made-Simple-2.2.10---SQL-Injection-Exploit

Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.

Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.

Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…

This repo shows an exploit to CVE-2021-24762. This is an Blind SQLi exploit that, on default config, greps the admin password.

Unauthenticated time-based blind SQL injection exploit for CMS Made Simple <= 2.2.9. Extracts admin credentials and optionally cracks password hashes…

Working Python exploit for CVE-2019-9053 with optional password cracking via wordlist. Targets web applications via HTTP URI for automated…

Exploits Python cve-2019-9053– by HackHeart

This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…

Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…

Improved code of Daniele Scanu SQL Injection exploit

Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…

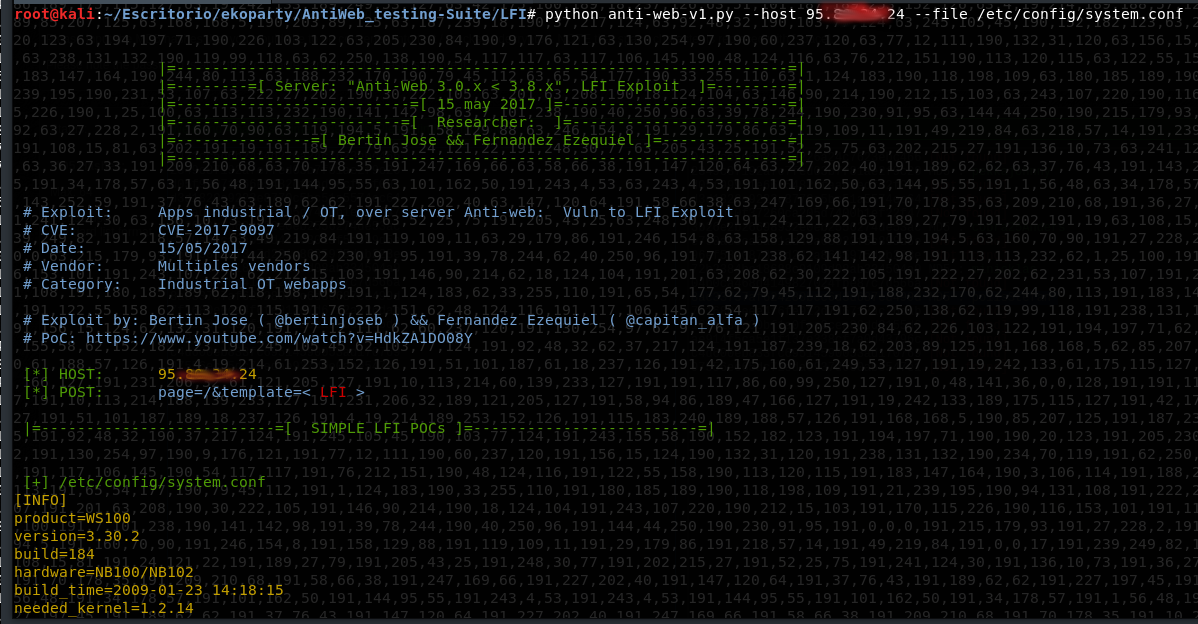
Suite de herramientas que sacan partido del CVE-2017-9097 (+RCE)

Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…

Exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks the…

Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.

This script complements the results obtained through the keepass-password-dumper tool when exploiting the CVE-2023-32784 vulnerability affecting…

Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…

XMLRPC server for password cracking