doublepulsar-usermode-injector

A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…

A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…

Code Execution & Persistence in NETWORK SERVICE FAX Service

An issue in Clementine v.1.3.1 allows a local attacker to execute arbitrary code via a crafted DLL file (DLL Hijacking)

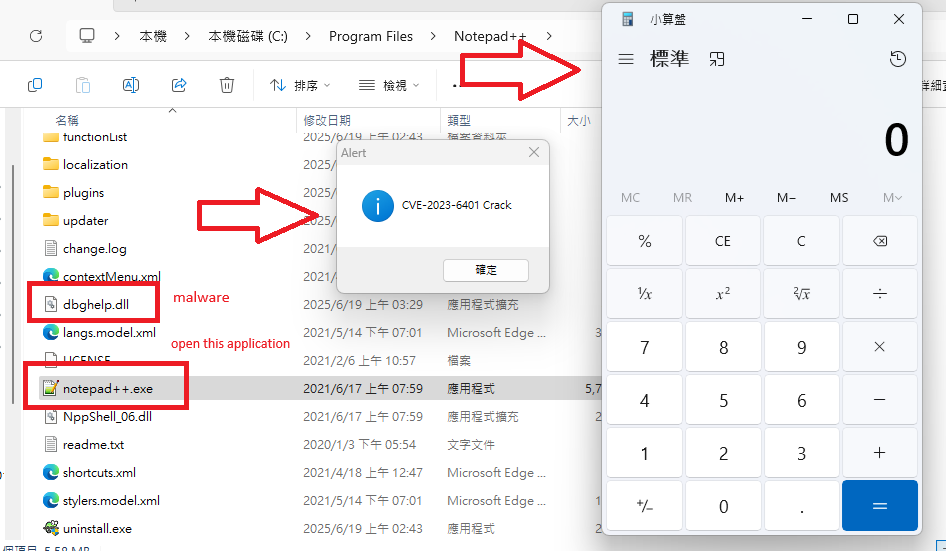
CVE-2023-6401 is a DLL hijacking vulnerability that allows attackers to execute arbitrary code by placing a malicious `dbghelp.dll` file in the…

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…

Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.

Proof-of-concept exploit for Windows local privilege escalation (CVE-2023-21746) abusing NTLM local authentication to gain SYSTEM privileges via SMB…

Automated DLL Sideloading Tool With EDR Evasion Capabilities

DLL Hijacking in Quickheal Total Security/ Internet Security/ Antivirus Pro (Installers)

DLL Planting in the Corsair iCUE v.5.3.102 CVE-2023-38822

DLL Planting in the CoD MW Warzone 2 - CVE-2023-38821

DLL Planting in the Slack 4.33.73 - CVE-2023-38820

C# PrintNightmare (CVE-2021-1675)

A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…

A dll hijacking vulnerability in zoom meeting < 5.1.4. CVE-2020-9767

Proof-of-concept for CVE-2026-89282: proxy DLL search-order hijack in Apache Lounge Windows installs that yields SYSTEM privilege escalation on…

Helakuru Version 1.1 DLL Hijack - CVE-2024-48605

CVE-2024-39069