Penetration-Testing-Walkthrough-Hacksudo-Thor

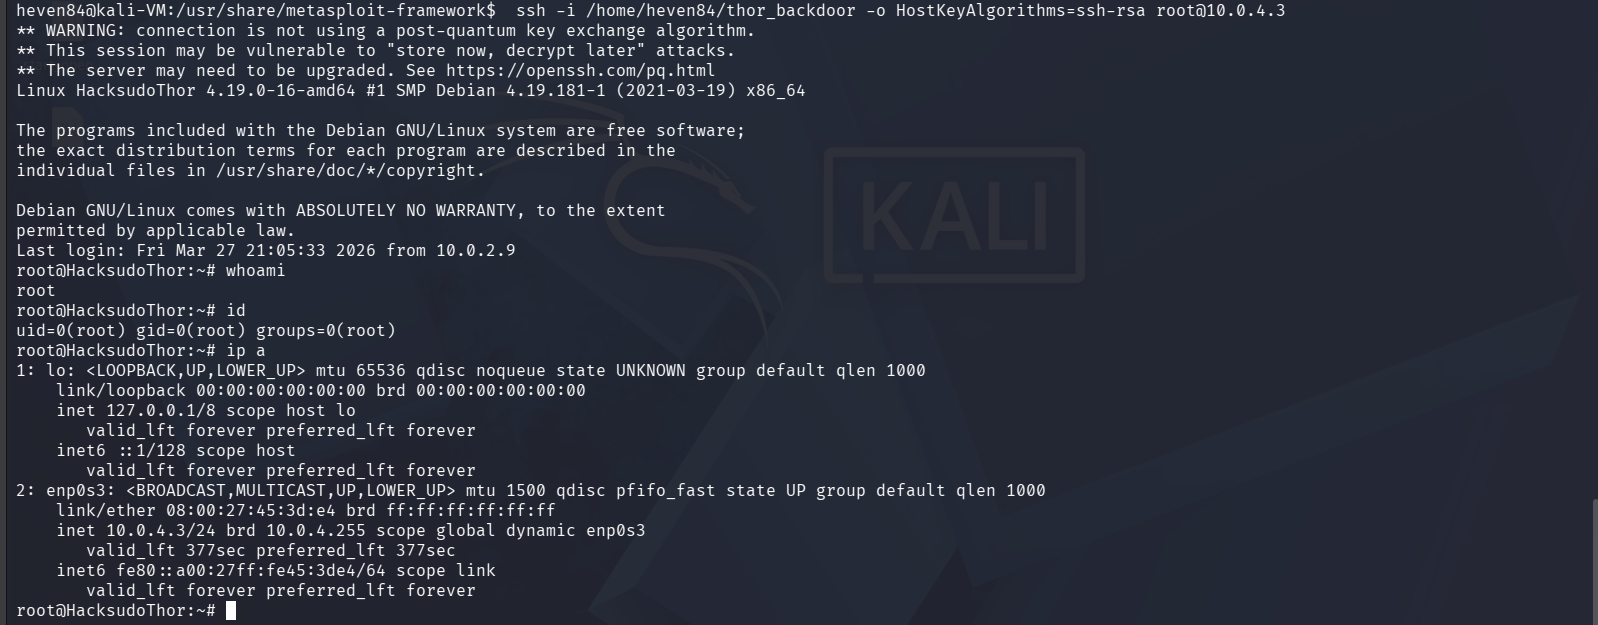
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…

Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…

Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…

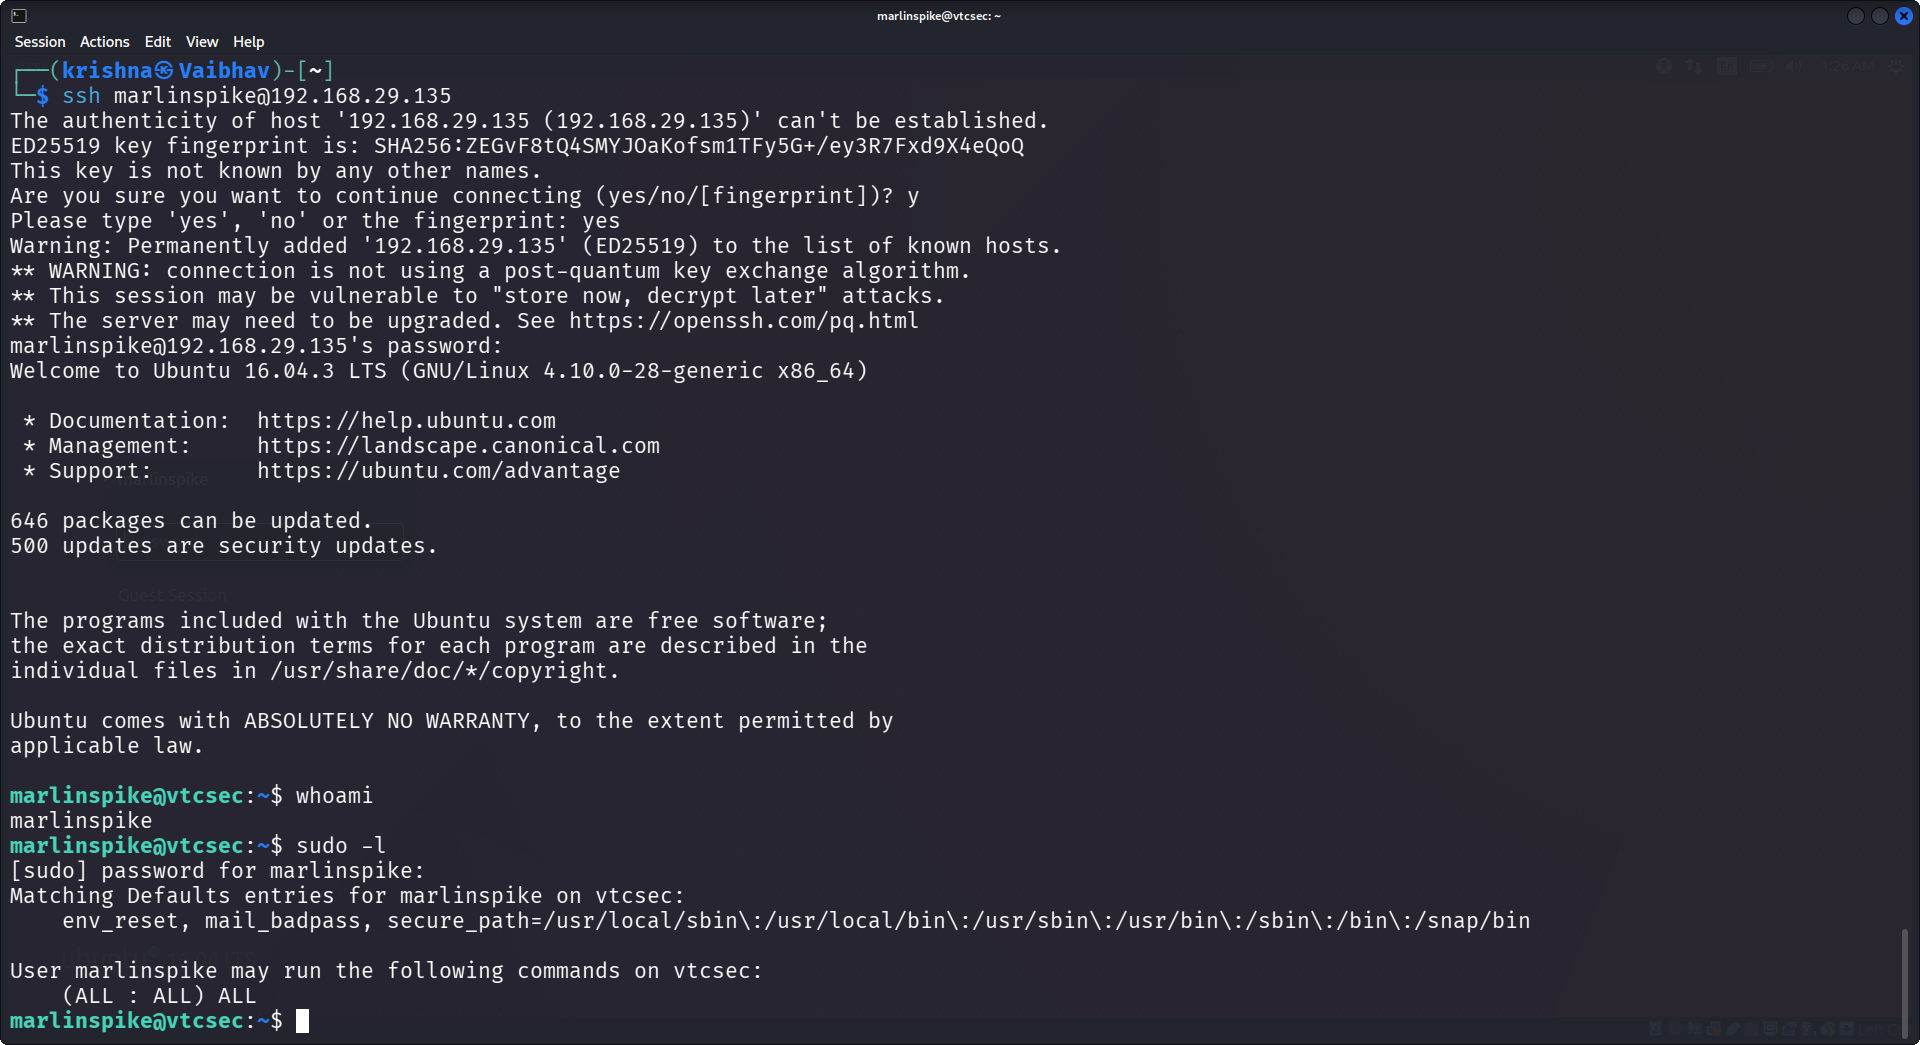
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)

Exploit for CVE-2021-42949 in HotelDruid v3.0.3, demonstrating predictable session token generation and authentication bypass via brute force.

Possible Account Takeover | Brute Force Ability

Bludit 3.9.2 - Auth Brute Force Mitigation Bypass. CVE-2019-17240

Crack any Microsoft Windows users password without any privilege (Guest account included)

Crack and decrypt BLE encryption

Use ESC1 to perform a makeshift DCSync and dump hashes

Exploit for CVE-2021-27342 vulnerability (telnet authentication brute-force protection bypass)

Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…

This is the exploit of CVE-2019-17240.

Bludit <= 3.9.2 - Authentication Bruteforce Mitigation Bypass Exploit/PoC

WordPress Plugin Digits < 8.4.6.1 - OTP Auth Bypass via Bruteforce (CVE-2025-4094)

PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.

Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…

Detailed CVE-2026-8697 writeup with POC exploit for a login rate-limit bypass on TP-Link Archer C64 routers via a debug SSH service, enabling…

There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3