
CVE-2026-48907
 ywh-jfellus/cve-2026-48907
PoC for CVE-2026-48907 - Joomla! JCE extension < 2.9.99.5 unauthenticated RCE
educationexploitationlabs-practice+3
163 months ago
ywh-jfellus/cve-2026-48907PoC for CVE-2026-48907 - Joomla! JCE extension < 2.9.99.5 unauthenticated RCE
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
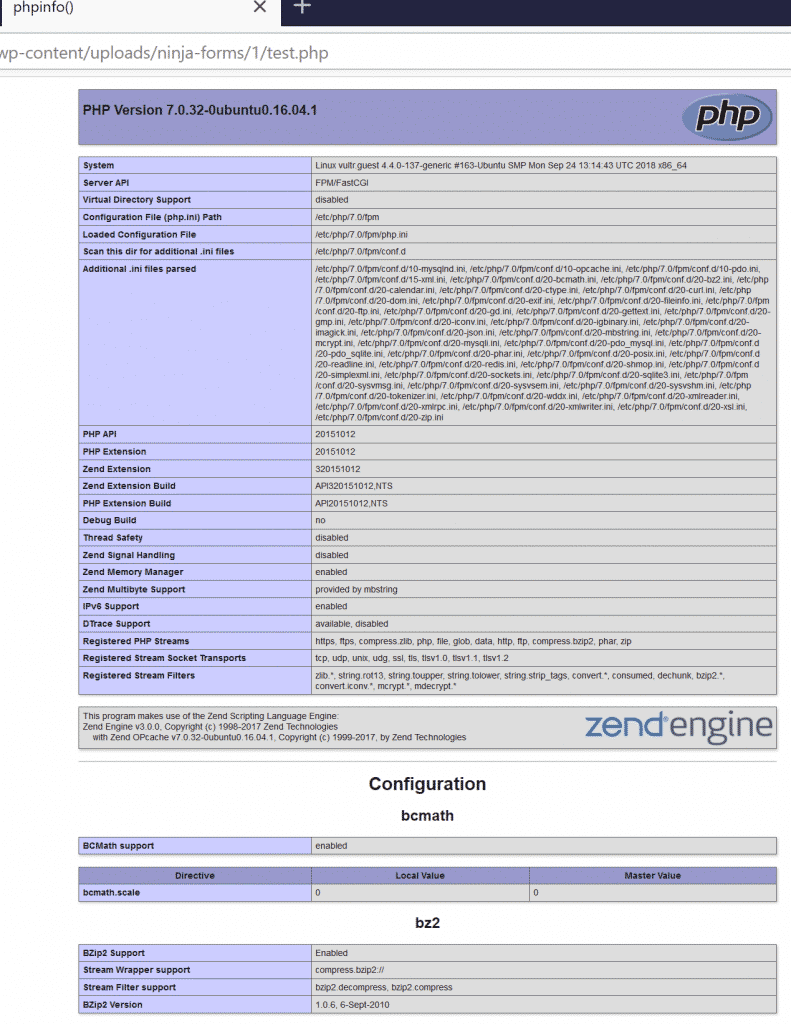 ktn1990/cve-2019-10869
(Wordpress) Ninja Forms File Uploads Extension <= 3.0.22 – Unauthenticated Arbitrary File Upload
 r00tjunip3r1/poc-cve-2024-6778
Proof-of-concept exploit for CVE-2024-6778, a Chromium sandbox escape via a malicious browser extension, achieving code execution on privileged WebUI…
 bigb0x/cve-2024-21514
SQL Injection POC for CVE-2024-21514: Divido payment extension for OpenCart
 fru1ts/cve-2024-44902
Proof-of-concept exploit for CVE-2024-44902, a deserialization vulnerability in ThinkPHP v6.1.3–v8.0.4 enabling remote code execution via crafted…
 e1tex/python-cve-2020-25213
Python Interactive Exploit for WP File Manager Vulnerability. The File Manager (wp-file-manager) plugin before 6.9 for WordPress allows remote…
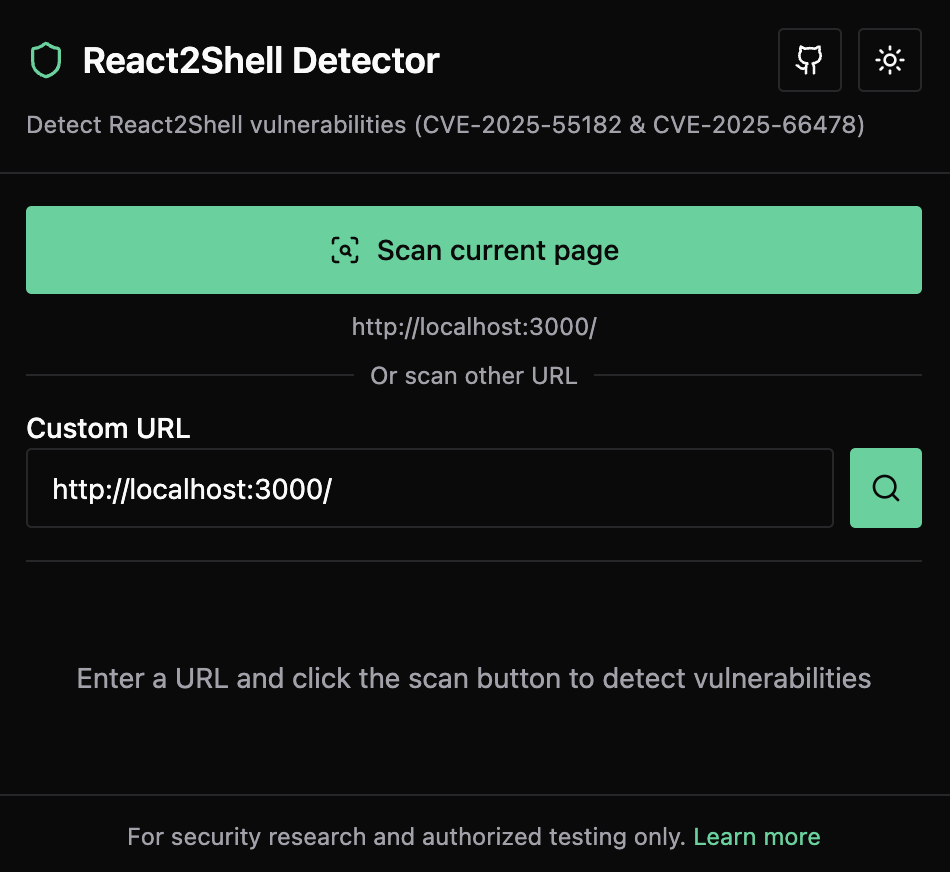 xiaopeng-ye/react2shell-detector
A Chrome extension for detecting React2Shell vulnerabilities (CVE-2025-55182 & CVE-2025-66478) in web applications
 shinthink/cve-2026-48939
Pre-auth arbitrary file upload RCE exploit for iCagenda Joomla extension < 4.0.8 (CVSS 10.0)
 alfazhossain/cve-2025-55182-exploiter
CVE-2025-55182-Exploiter Google Chrome Extension. nextjs vulnerability #nextjscve
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 toanln-cov/cve-2026-66493
The Joomla extension PhocaCommander is vulnerable to Path Traversal in delete, copy, move actions - CVSS 6.4
 toanln-cov/cve-2026-66492
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the file upload action - CVSS 6.1
 toanln-cov/cve-2026-66491
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2
 ghostpels/cve-2026-13001
Exploit for CVE-2026-13001: Unauthenticated RCE in Podlove Podcast Publisher via extension confusion. Includes mass scanning, interactive shell, and…
 wubinworks/magento2-session-reaper-patch
Patch for CVE-2025-54236(a.k.a Session Reaper) which allows customer account takeover and RCE under certain conditions. This patch is actually a…
 chiefyoru/cve-2026-48939_poc
iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…
 chiefyoru/cve-2026-56291_poc
The Joomla extension Balbooa Forms is vulnerable to an unauthenticated arbitrary file upload that allows uploading executable files and leads to full…