
CVE-2017-9554-Exploit-Tool
 ez0-yf/cve-2017-9554-exploit-tool
CVE-2017-9554 Exploit Tool
exploitationinformation-gatheringpenetration-testing+2
ez0-yf/cve-2017-9554-exploit-toolCVE-2017-9554 Exploit Tool
 veids/cve-2020-3452_auto
Automated enumeration and file download tool exploiting CVE-2020-3452 in Cisco ASA devices, with Lua bytecode decompilation support.
 vnyui/cve-2021-44228
Mass recognition tool for CVE-2021-44228
 ialejandrozalles/investigacionaplicacioncve-1999-0517
Research and exploitation tool targeting CVE-1999-0517, enabling vulnerability analysis and penetration testing for web-based security assessments.
 kkyehit/log4j_cve-2021-44228
Exploit tool for CVE-2021-44228 (Log4Shell) targeting vulnerable Log4j instances for remote code execution and security testing.
 nma-io/cve-2024-47176
A simple CVE-2024-47176 (cups_browsed) check tool written in go.
 trustcves/cve-2024-24398
Proof-of-concept or analysis tool for CVE-2024-24398, demonstrating exploitation of a specific vulnerability.

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
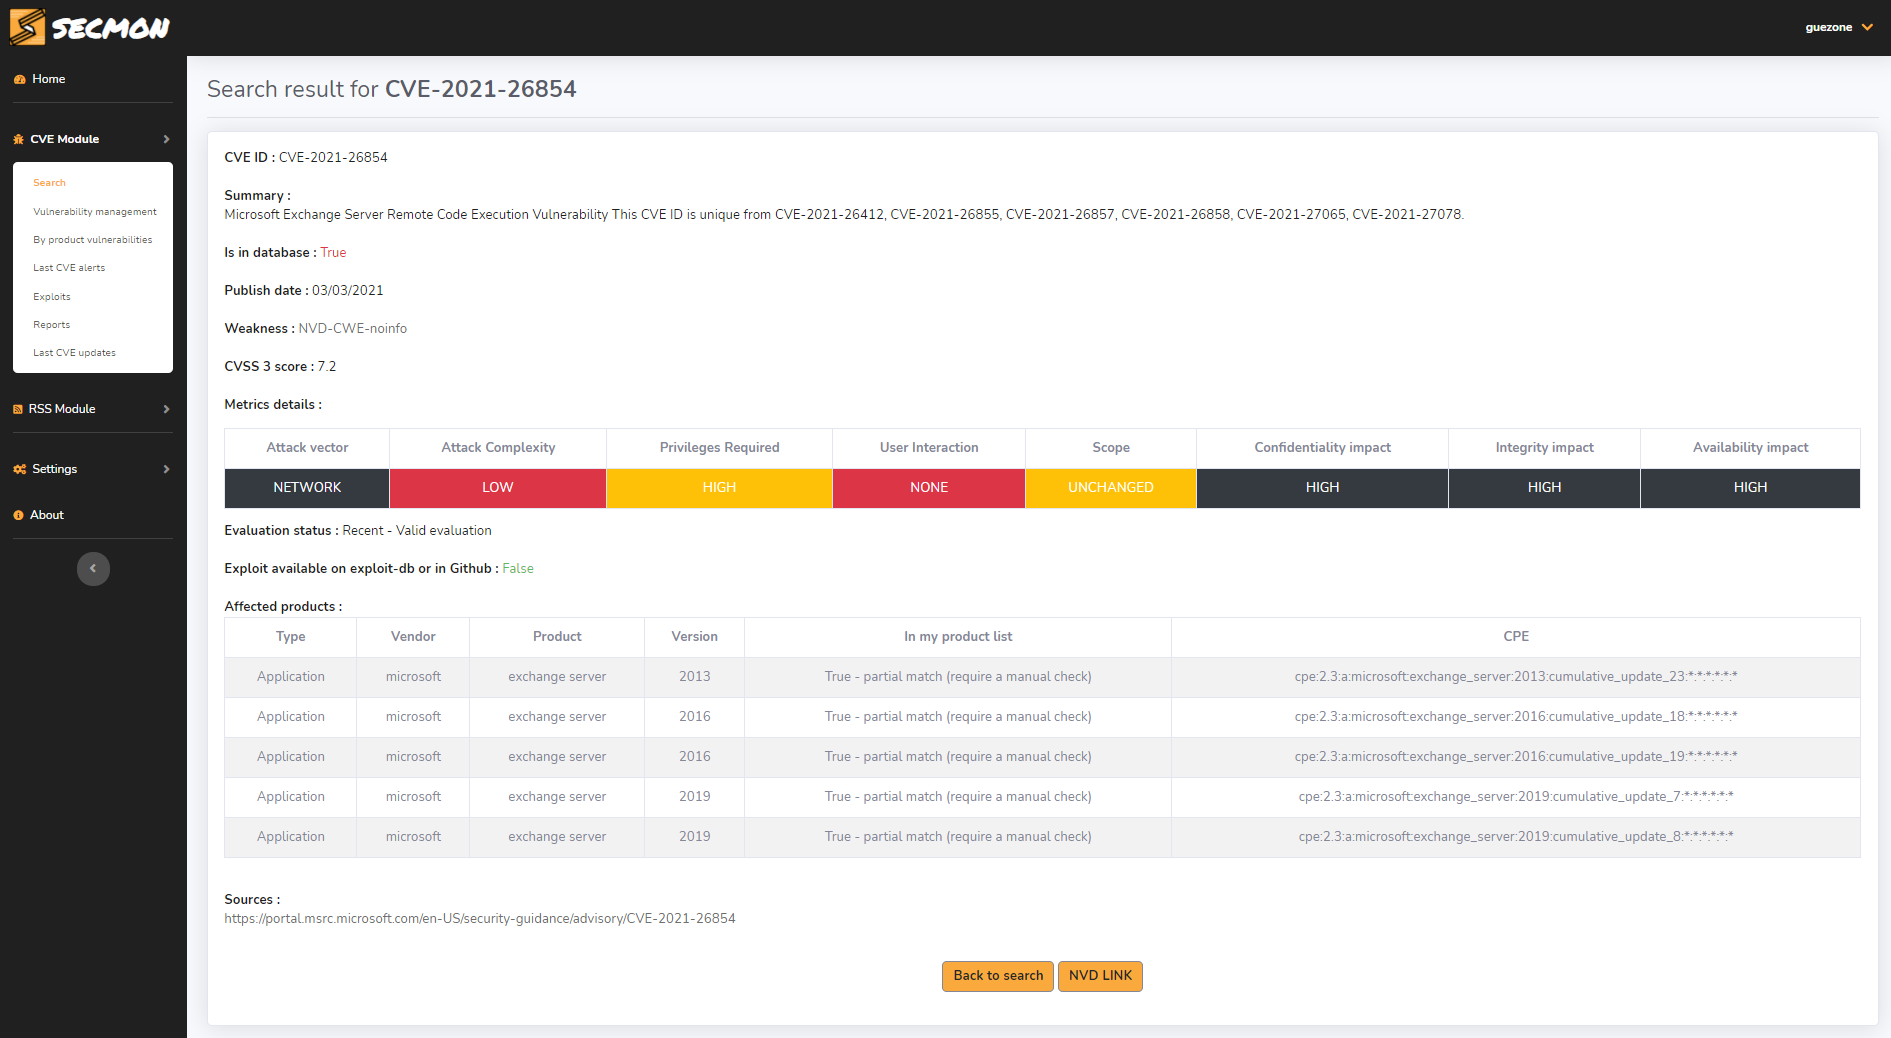 alb-uss/secmon
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
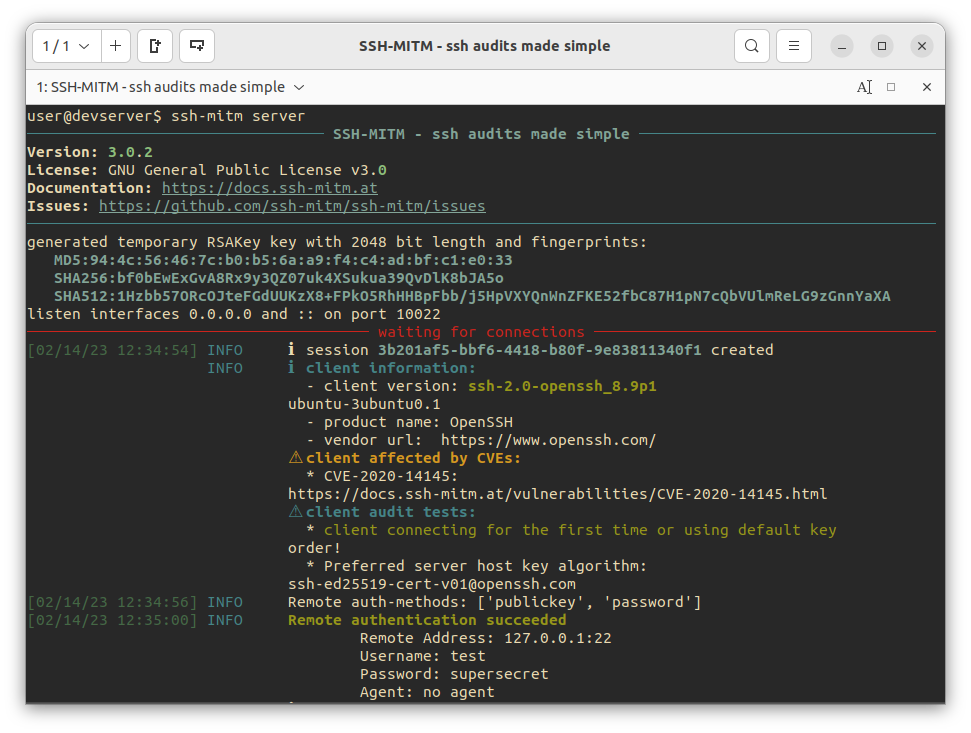 ssh-mitm/ssh-mitm
SSH-MITM - ssh audits made simple
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.

 rajeshmajumdar/ploitkit
The Hacker's ToolBox
 netspi/ad-pathfinder
Attack path mapping for Active Directory, ADCS, SCCM, and MSSQL using BloodHound CE + OpenGraph data.