

CVE-2024-25180
 dustblessnotdust/cve-2024-25180
Python exploit script for CVE-2024-25180, a remote code execution vulnerability in pdfmake, delivering a reverse shell via crafted POST requests.
command-and-controlexploitationpayload-generation+3
dustblessnotdust/cve-2024-25180Python exploit script for CVE-2024-25180, a remote code execution vulnerability in pdfmake, delivering a reverse shell via crafted POST requests.
 passwa11/cve-2023-38646
Python exploit script for CVE-2023-38646, a pre-authentication remote code execution vulnerability in Metabase, delivering a reverse shell to an…
 ivancabrera02/admintosystem-http.sys
Windows Admin-to-SYSTEM privilege escalation PoC that coerces SYSTEM processes to authenticate to a local HTTP.sys listener, captures the NTLM token,…
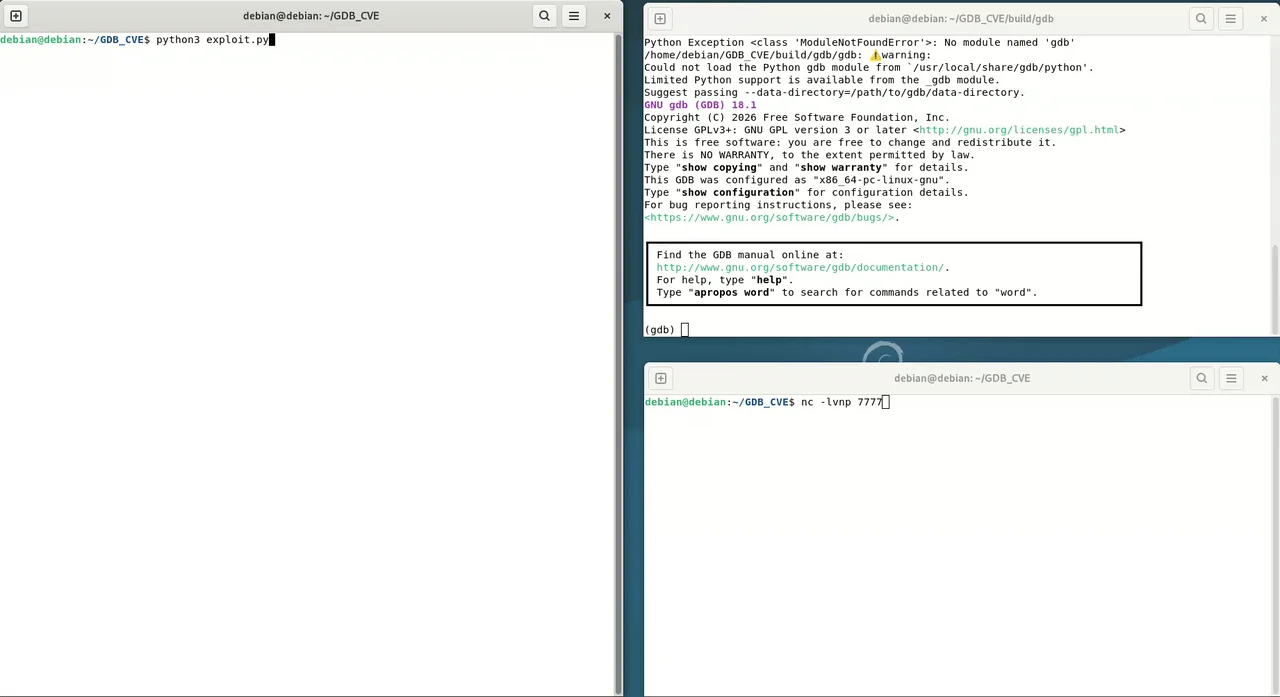 deebumg/cve-2026-121994-poc
Weaponized proof-of-concept for CVE-2026-121994: a fake GDB remote debug stub that sends a malicious p-packet to trigger memory corruption and a…
 synacktiv/samsung-q60t-exploit
Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…
 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 tecxx/cve-2025-59287-wsus
PowerShell proof-of-concept exploit for CVE-2025-59287 targeting WSUS servers. Automates payload generation with ysoserial.net and triggers a reverse…
 ghxstsec/cve-2025-8110
Proof-of-concept exploit for CVE-2025-8110, a Gogs RCE vulnerability exploiting path traversal via symbolic links and sshCommand injection to deliver…
 diemoeve/cve-2024-41570
Automated Reverse Shell Exploit via WebSocket | Havoc-C2-SSRF with RCE
 adhikara13/cve-2023-27350
Exploit for Papercut CVE-2023-27350. [+] Reverse shell [+] Mass checking
 jishino567/cve-2026-73570
Python PoC for CVE-2026-73570, an SMTP command injection in Zimbra. Sends malformed RCPT TO payloads to trigger shell command execution via…
 e4zyy/project-cve-2026-75604
Python-based exploitation framework for CVE-2026-75604, enabling authorized pentesters to validate Next.js Windows cache traversal vulnerabilities…
 rushikesh-a-bhujbal/cve-2010-2075
UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.
 akash0x00/zoneminder-1.29-1.30-rce-exploit
Unauthenticated SQL injection to RCE exploit for ZoneMinder 1.29/1.30 (CVE-2016-10204, EDB-41239). Single-command SQLi to webshell to reverse shell…
 akash7350/cve-2021-22204
Generate malicious JPEG payloads exploiting ExifTool CVE-2021-22204 for arbitrary code execution, with custom commands or reverse shell support.
 hackfutsecroot/cve-2026-87902
Python mass scanner and exploit for CVE-2026-87902, an unauthenticated WordPress core LFI in get_page_template() escalated to RCE via the PEAR gadget…
 tc4dy/cve-2026-85706-poc-toolkit
Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…
 hackerking24/cve-2026-30225-olivetin-rce
Proof-of-concept exploit for OliveTin unauthenticated RCE (CVE-2026-30225) via insecure guest defaults and unvalidated argument types, enabling root…