
 mishakorzik/allhackingtools
All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 suominen/cve-2026-31431
Tracking Copy Fail (CVE-2026-31431), the Linux algif_aead privilege escalation
 suominen/cve-2026-43284
Tracking Dirty Frag (CVE-2026-43284, CVE-2026-43500), the xfrm-ESP and RxRPC page-cache write LPE chain
 suominen/cve-2026-9256
Tracking the nginx CVE-2026-9256 rewrite-module heap overflow
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
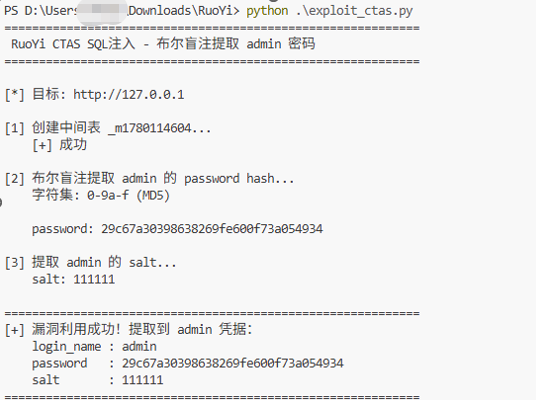 chinesespeople/cve-2026-52614
There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3
 ninajafli/dotcms-cve-2022-45782
Proof-of-concept for CVE-2022-45782: predictable dotCMS password-reset tokens, with a token cracker and full exploit chain.
 kaihaochen04/monikerlinktest
cve-2024-21413
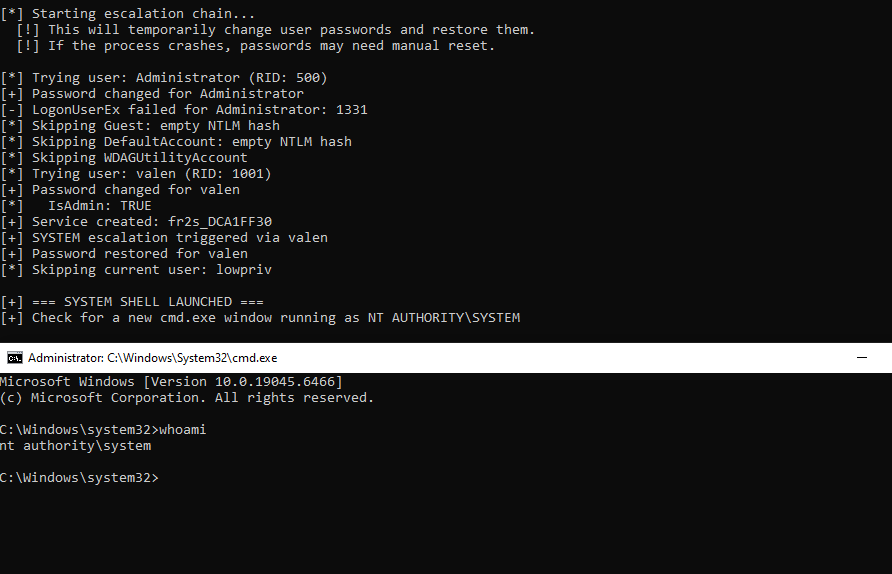
 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
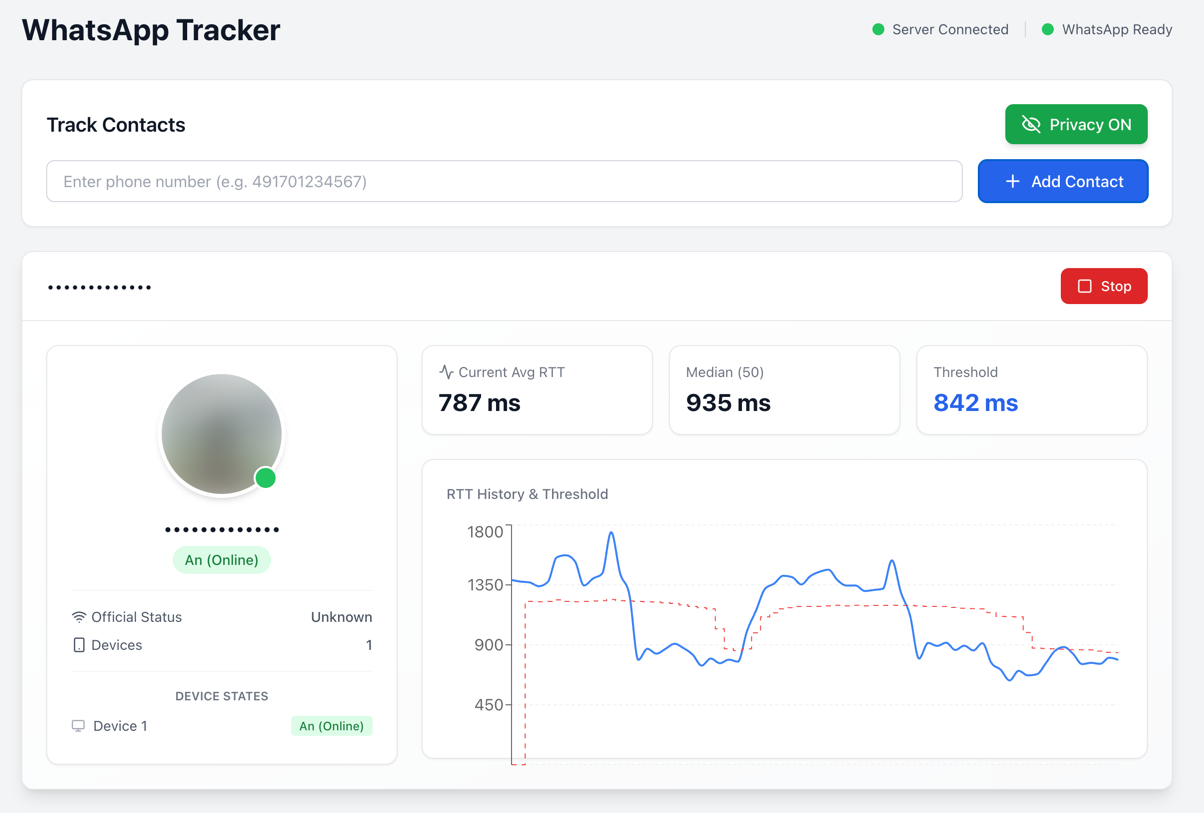 gommzystudio/device-activity-tracker
A phone number can reveal whether a device is active, in standby or offline (and more). This PoC demonstrates how delivery receipts + RTT timing leak…
 x3rx3ssec/cve-2025-2011
Exploit for CVE-2025-2011
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 thepiyushkumarshukla/cve-2022-24707_anukotimetracker_version-1.20.0_poc
Automated SQL injection exploit for CVE-2022-24707 targeting Anuko Time Tracker 1.20.0. Extracts user credentials from tt_users database via…
 c4cnm/exploit_cve-2021-24762
This repo shows an exploit to CVE-2021-24762. This is an Blind SQLi exploit that, on default config, greps the admin password.
 boon-rekcah/cms-made-simple-2.2.9-cve-2019-9053
Python 3 exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks…