
Stuxnet
 sadpainy/stuxnet
Educational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
educationexploitationlateral-movement+4
590
sadpainy/stuxnetEducational reconstruction of the Stuxnet worm for malware analysis and defensive research. Includes modules for privilege escalation, rootkit…
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 mein-0/kaspermeow
Proof-of-concept that exploits a Kaspersky driver vulnerability to leak kernel pointers and bypass KASLR on Windows, enabling kernel exploit chain…
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 kinryulabs/rootpacket-cve-2026-31431
Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…
 anylnk/ksldbyovdark
Exploits a KSLD anti-rootkit driver vulnerability (IOCTL 0x222044) to bypass PPL protection and access sensitive process memory, enabling local…
 daem0nc0re/vectorkernel
PoCs for Kernelmode rootkit techniques research.
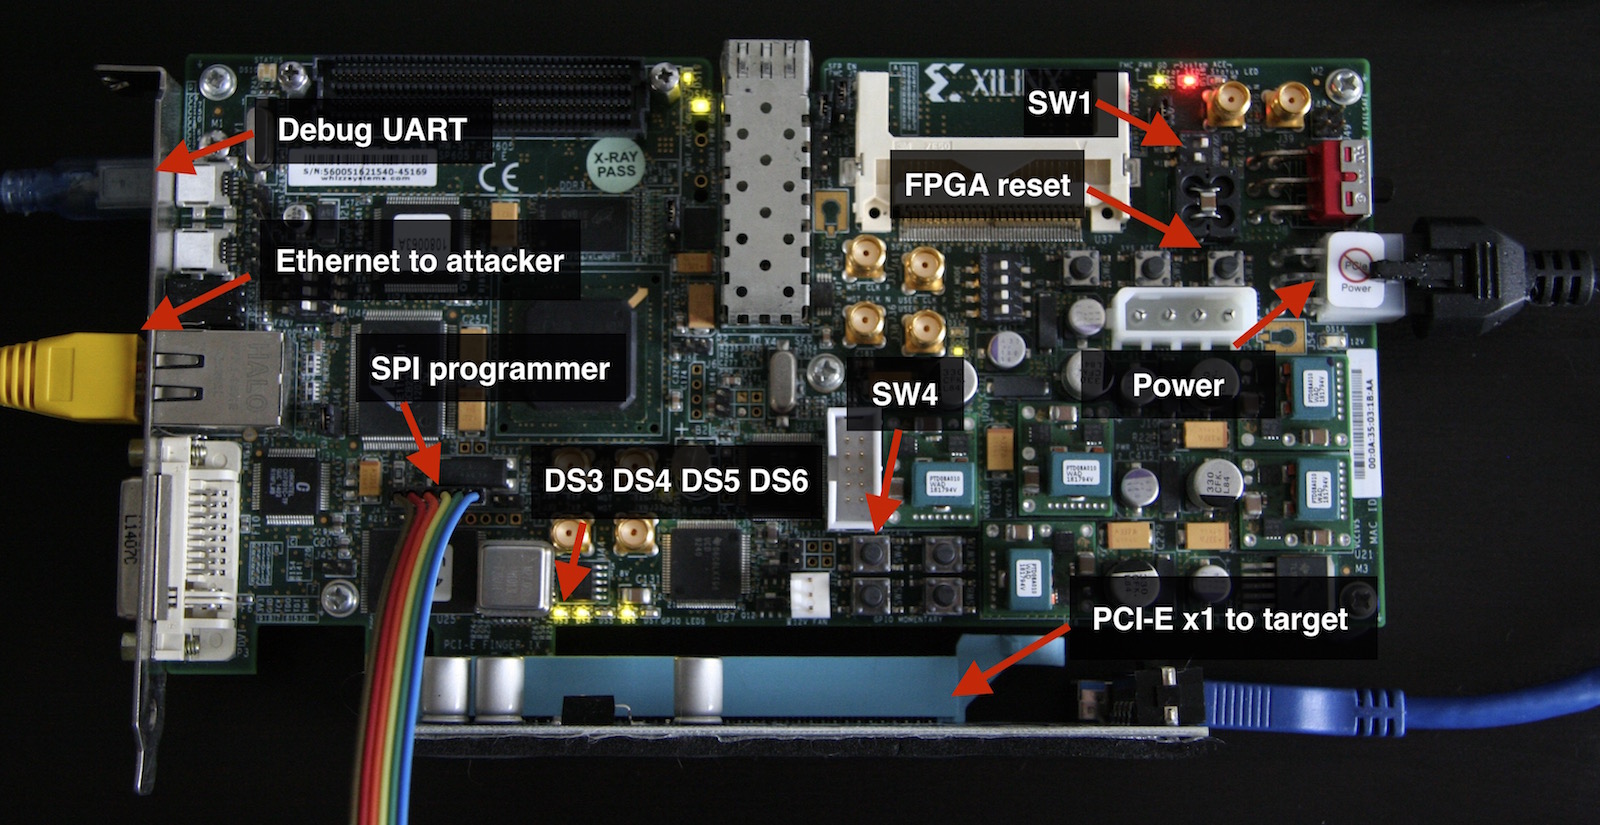 cr4sh/s6_pcie_microblaze
PCI Express DIY hacking toolkit for Xilinx SP605. This repository is also home of Hyper-V Backdoor and Boot Backdoor, check readme for links and info
 nabilboudra/cve-2017-5123
Educational demonstration of CVE-2017-5123 kernel exploit, ICMP-based rootkit command-and-control, and OS command injection vulnerable web…
 m4rm0k/talkingben
UEFI rootkit under development focusing on privilege escalation, C2 integration, and anti-EDR/AV evasion for real-world malware deployment.
 netjbs/cve-2017-0055-poc
This it's a PoC of Departament of justice VDP. By rootkit
 spiralbl0ck/bios-stuff-related-programming
Final OBJECTIVE:BIOS ROOTKIT AND RSHELL USING BIOS NETWORKING STACK
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…
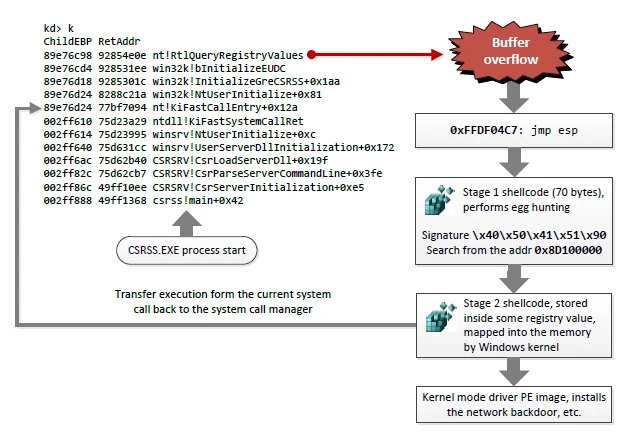 cr4sh/windowsregistryrootkit
Kernel rootkit, that lives inside the Windows registry values data
 malwaretech/fakembr
TDL4 style rootkit to spoof read/write requests to master boot record