devin-cve48384-1789318364-1162143-parent

Authorized reachability probe for CVE-2025-48384, used to verify whether a target is exposed to the vulnerability in a controlled testing context.

Authorized reachability probe for CVE-2025-48384, used to verify whether a target is exposed to the vulnerability in a controlled testing context.

University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…

Demonstrate the unauthenticated remote code execution vulnerability in the RSFiles! Joomla component through an arbitrary file upload.

PoC for CVE-2019-18394: unauthenticated full-read SSRF in Openfire <= 4.4.2 FaviconServlet

CVE-2026-8732 | WP Maps Pro <= 6.1.0 Unauth Admin Creation

Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)

Unauthenticated SSRF in the Chamilo LMS PENS plugin — CVE-2026-34160 / CVSS 8.6

Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2

Exploit for Marimo pre-auth RCE via terminal WebSocket, providing command execution, interactive PTY shell, and reverse shell capabilities for…

CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.

Nuclei template to discover exposed Keycloak reset-credentials endpoints across multiple paths, aiding validation of CVE-2026-18963 exposure.

Detection artifact generator for Ivanti Sentry authentication bypass and RCE vulnerabilities (CVE-2026-10520, CVE-2026-10523). Scans single or…

PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…

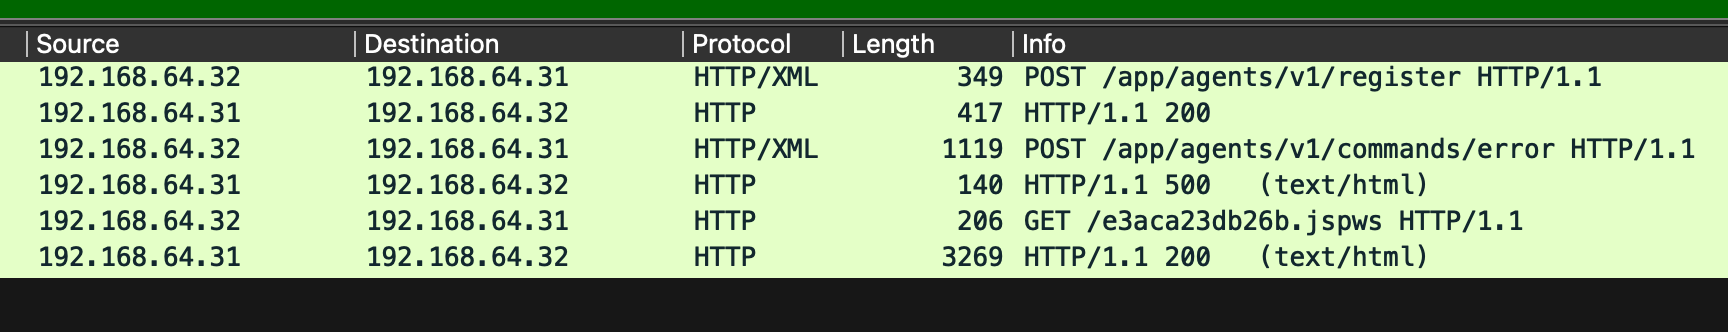
teamcity teamcity-CVE-2026-63077 exploitation pcap

WordPress security scanner that fingerprints versions, detects reflected XSS across multiple targets concurrently, and supports an authenticated…

CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection

CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…

Educational Python PoC for a QUIC address-validation bypass that triggers handshake amplification, including vulnerable server simulation and attack…