
CVE-2026-34197-PoC
 nirvanasec/cve-2026-34197-poc
Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via Jolokia's addNetworkConnector, with technical notes and reverse shell…
exploitationpenetration-testingred-teaming+3
nirvanasec/cve-2026-34197-pocProof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via Jolokia's addNetworkConnector, with technical notes and reverse shell…
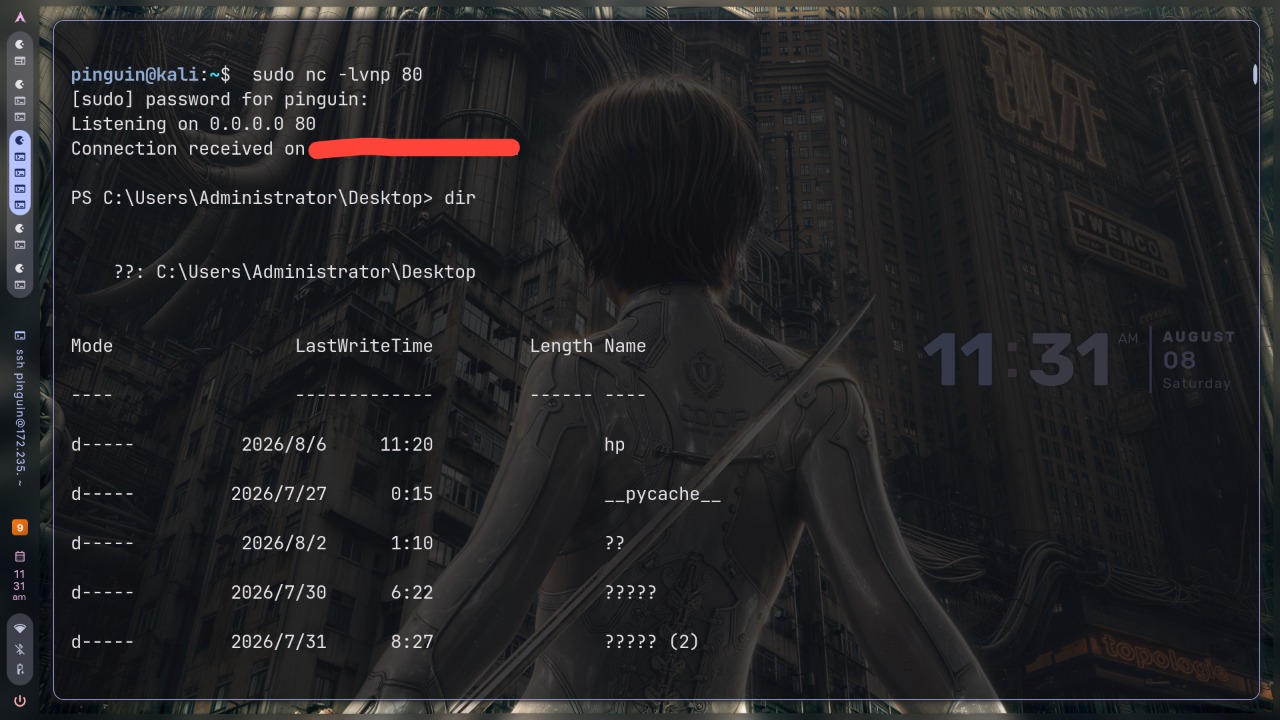 sandimfz/cve-2024-23692
Automates CVE-2024-23692 exploitation against unpatched Rejetto HFS with an in-memory PowerShell reverse shell, HTTP payload staging, and AV/EDR…
 0xdak/cve-2026-67340_exploit
Post-auth RCE exploit for ArcadeDB via JavaScript trigger GraalVM sandbox escape, executing OS commands over HTTP API with reverse shell or blind…
 0x00phantom-hat/cve-2026-5029-exploit
Proof-of-concept exploit for CVE-2026-5029, delivering unauthenticated remote code execution via the run-code MCP tool on exposed HTTP endpoints.…
 ibrahim-sartawi/cve-2026-26718
A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…
 huttwothreefour/cve-2026-5562-exploit
Proof-of-concept exploit for CVE-2026-5562 targeting Kafka UI with automated reverse shell delivery via HTTP PUT request to the smartfilters API…
 s1lentf00thold/cve-2021-21425-rce
Python exploit script for CVE-2021-21425 targeting Grav CMS admin panel, delivering a reverse shell via HTTP POST request with configurable LHOST and…
 mrr0b0t19/cve-2026-23744-poc
Proof-of-concept exploit for CVE-2026-23744, a remote code execution vulnerability in MCPJam Inspector. Demonstrates RCE via crafted HTTP request to…
 afifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744
Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…
 mbanyamer/cve-2026-22553-insat-masterscada-buk-ts-mmadmserv
Unauthenticated OS command injection exploit for InSAT MasterSCADA BUK-TS MMadmServ web interface. Delivers reverse shell with root privileges via…
 murrez/cve-2026-1306
Multi-target PoC runner for CVE-2026-1306 in WordPress midi-Synth plugin: fetches nonce, sends export AJAX request to upload files, and verifies…
 razzlemouse/f5-big-ip-smuggleshell-cve-2023-46747-exploit
#F5-BIG-IP-CVE-2023-46747-Exploit – Unauthenticated RCE Python exploit & Nuclei template by Raguraman ✓ Automated TCP reverse shell (LHOST/LPORT)…
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
 jorge2rubio/cve-2019-0232
Automated exploitation tool for CVE-2019-0232 (Apache Tomcat CGI RCE) with command execution and reverse shell modes, automatic URL encoding, and…
 adrianmafandy/cve-2021-41773
Proof-of-concept exploit for CVE-2021-41773, a path traversal and remote code execution vulnerability in Apache HTTP Server 2.4.49. Automates…
 harutomo-jp/cve-2024-28397-rce
Python exploit script for CVE-2024-28397 targeting js2py <= v0.74. Supports reverse shell and custom command execution via HTTP endpoint.