
spark-history-zip-symlink
 abraxas/spark-history-zip-symlink
Apache Spark 4.2.0 - High - Remote - File read - History zip follows planted symlink
exploitationinformation-gatheringpapers-research+3
abraxas/spark-history-zip-symlinkApache Spark 4.2.0 - High - Remote - File read - History zip follows planted symlink
 abraxas/spark-history-store-path
Apache Spark 4.2.0 - High - Remote - File write - History appStorePath unsanitized App ID
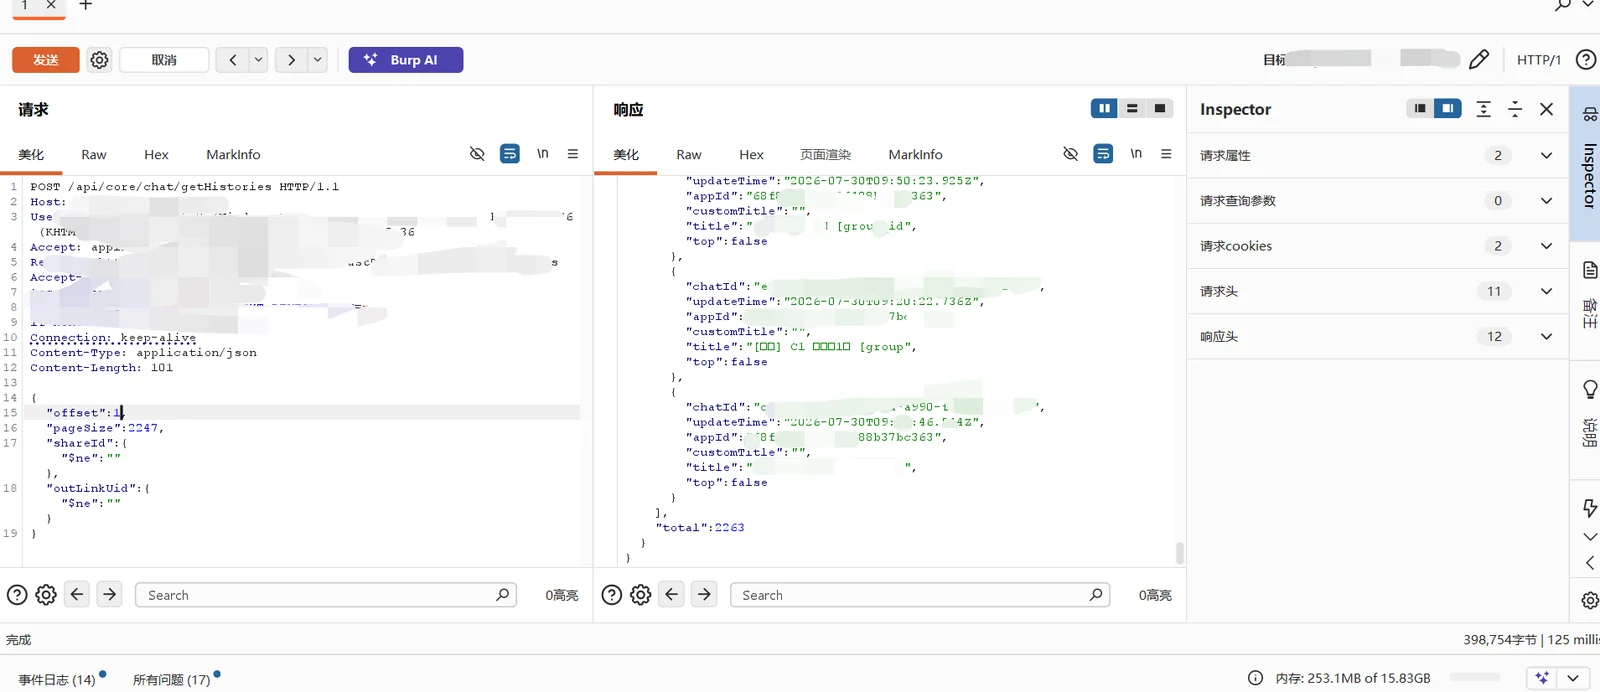 exploreio/cve-2026-79483-fastgpt-nosql-injection
Proof-of-concept for CVE-2026-79483, a NoSQL injection in FastGPT Community Edition allowing unauthenticated access to chat history titles. Includes…
 5kr1pt/glpi-logbleed
PoC for CVE-2026-53629, blind SQL injection in the GLPI history log filter
 izxci/cve-2026-7459
Exploit for CVE-2026-7459 targeting Simple History plugin missing authorization vulnerability, enabling unauthenticated account takeover in WordPress…
 abc1230940/soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
SOC336 - Windows OLE Zero-Click RCE Exploitation Detected (CVE-2025-21298) Walkthrough
 0xn4no/cve-2026-30048
Stored XSS vulnerability in NotChatbot WebChat <=1.5.0 with PoC payloads, impact analysis, and remediation guidance for secure chat history rendering.
 mrr0b0t19/cve-2025-55182-shellinteractive
Interactive RCE exploit for CVE-2025-55182 targeting Next.js/React Server Components deserialization vulnerability. Features automatic detection,…
 livepwn/cve-2025-55616
Exploit for CVE-2025-55616, a local RCE in Zsh via history expression, achieving arbitrary code execution with user privileges.
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
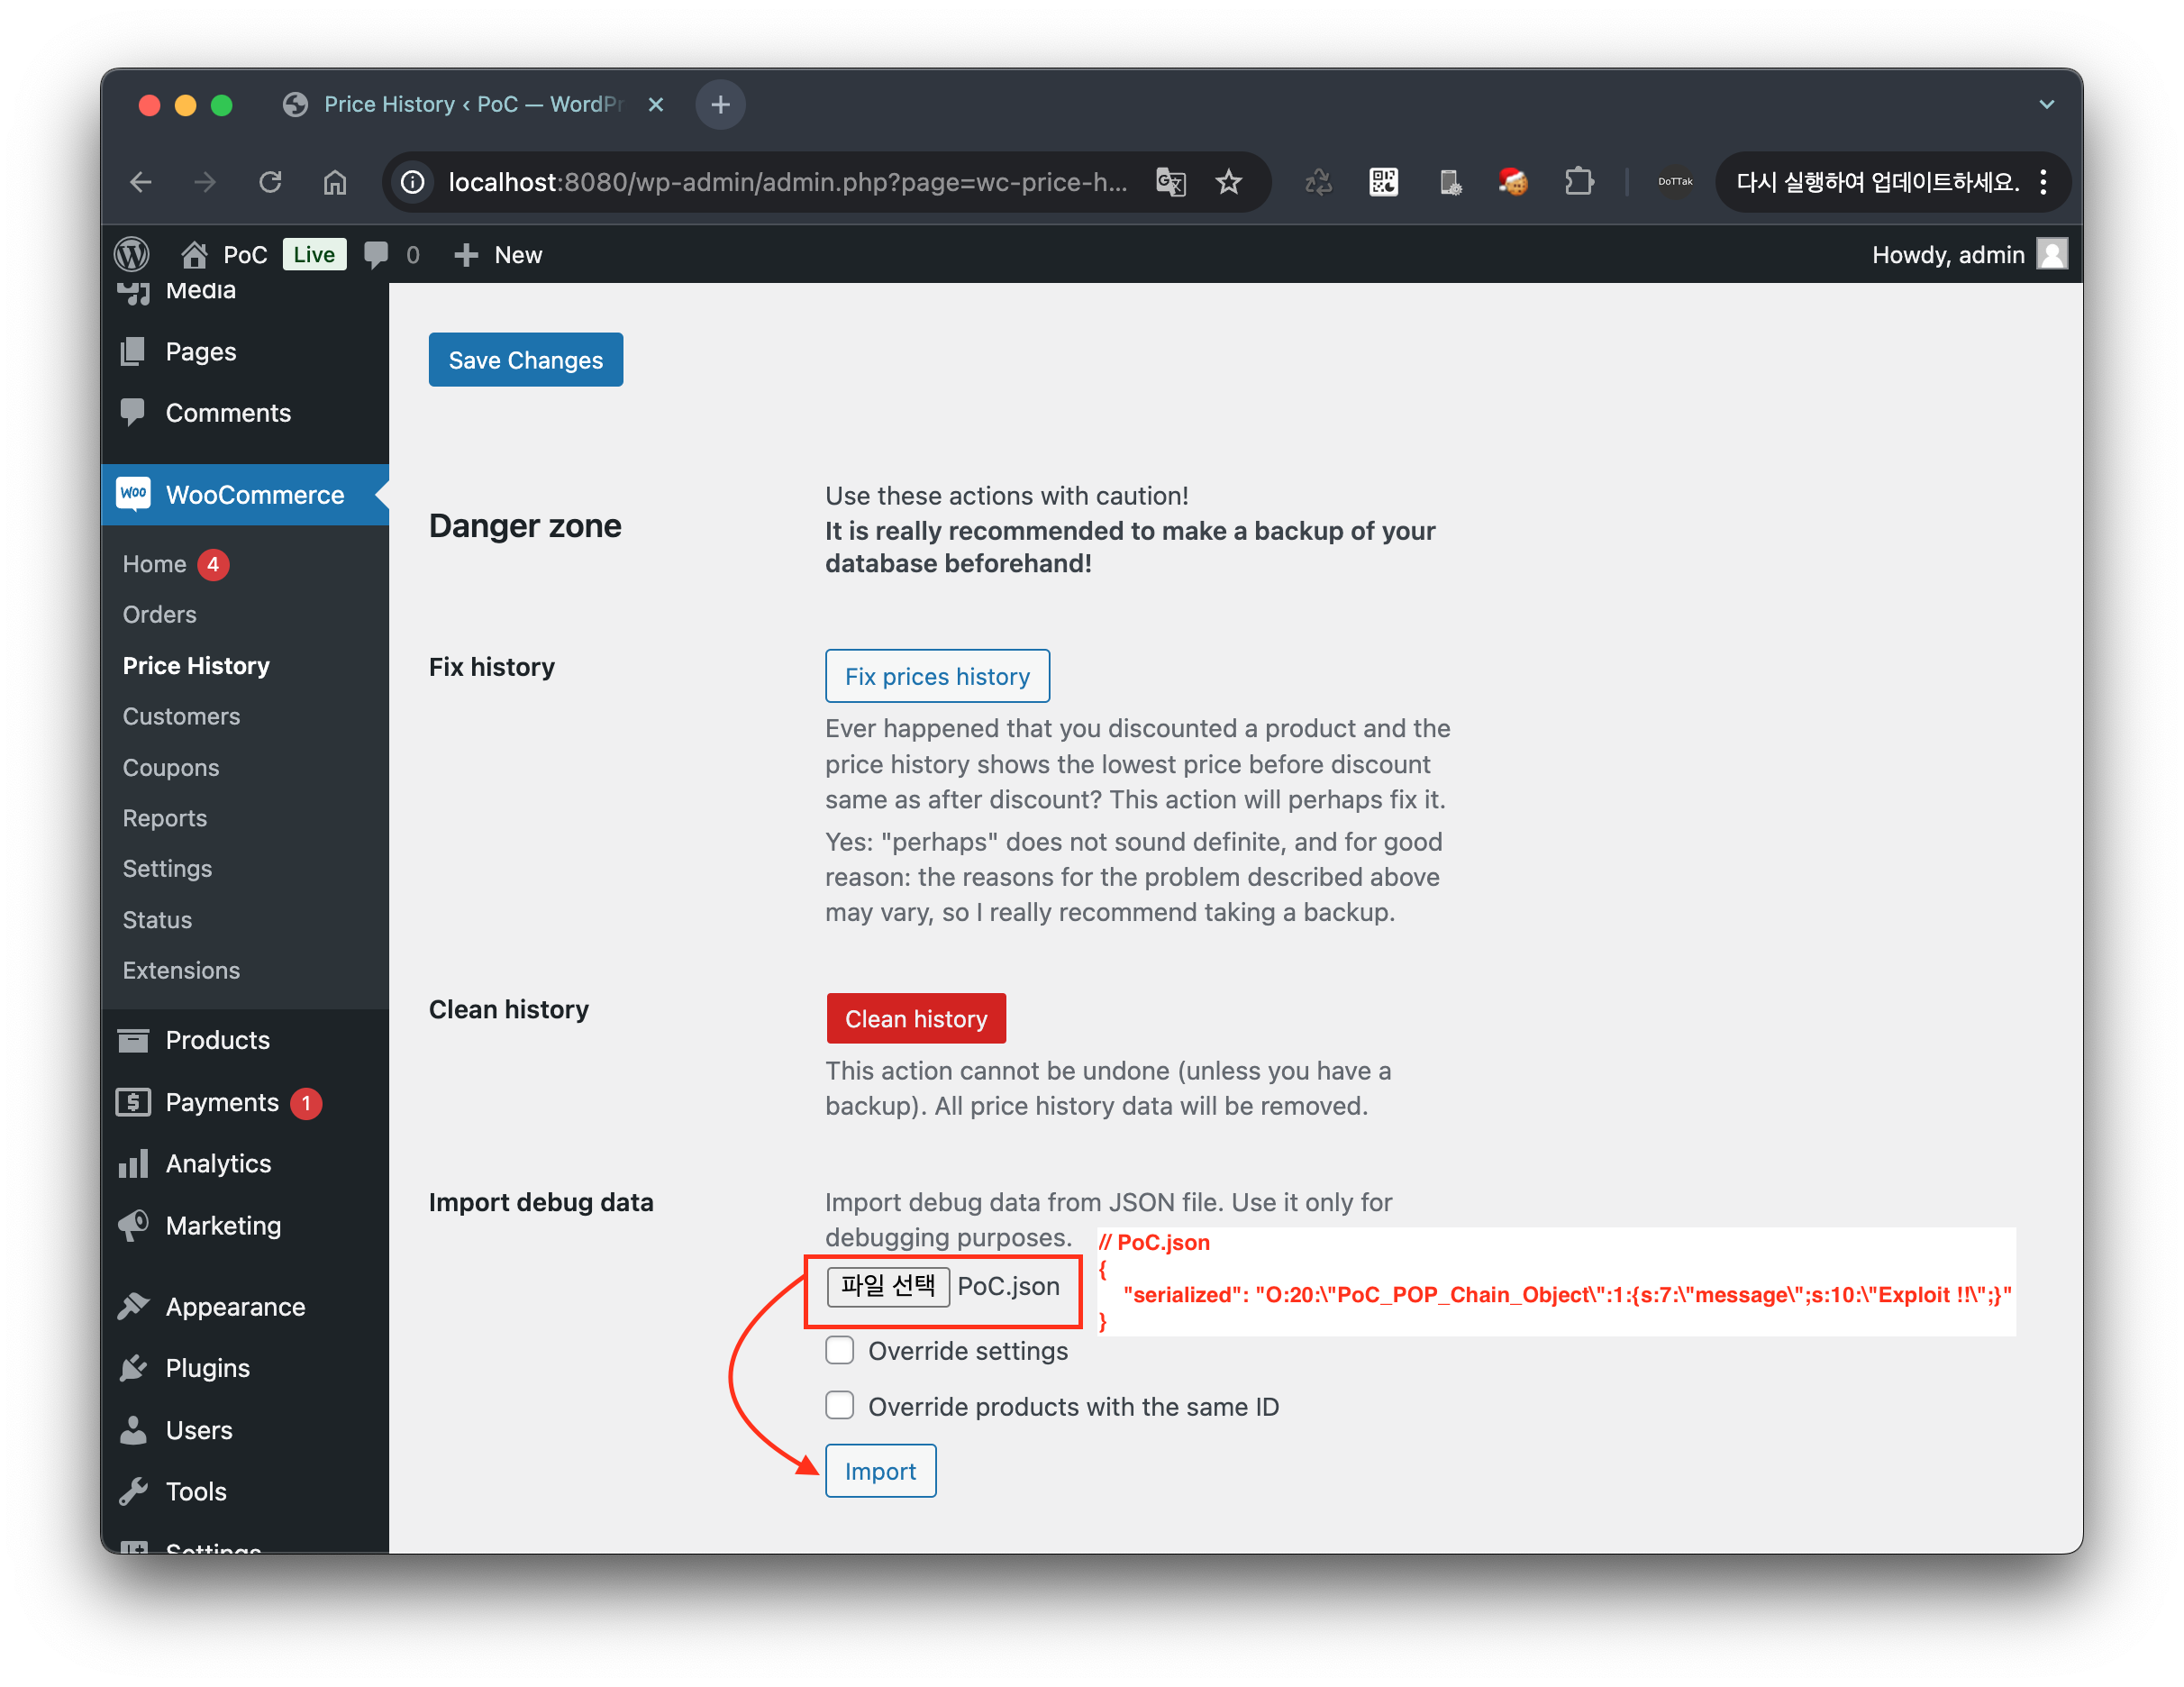 dottak/cve-2025-22510
PoC of CVE-2025-22510
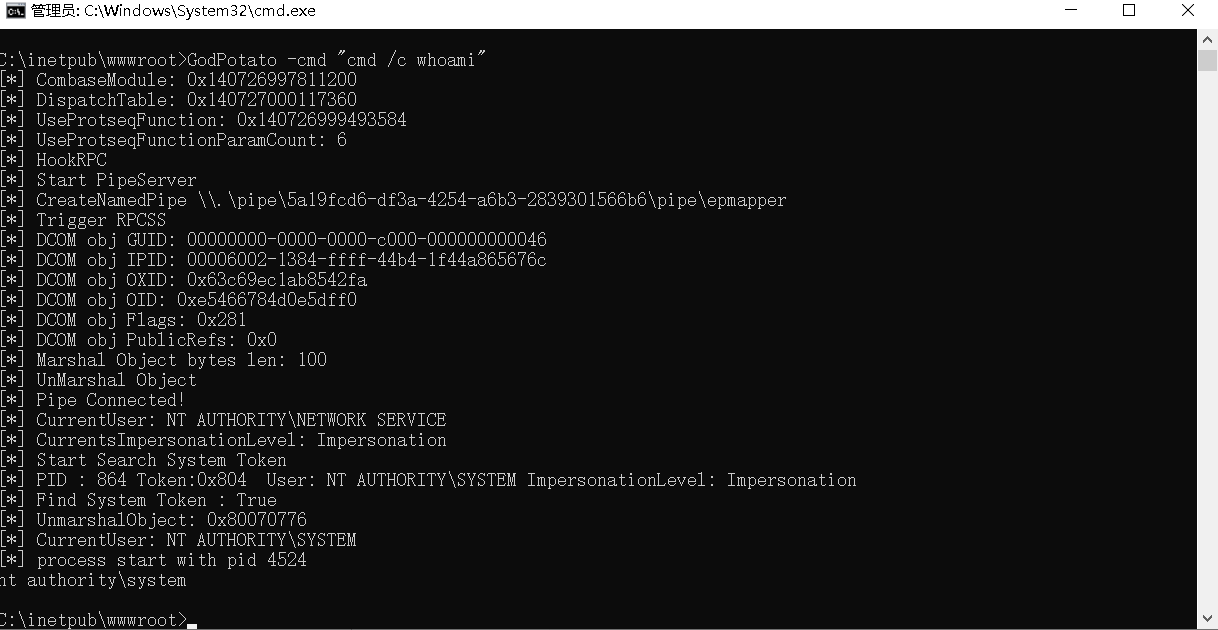 beichendream/godpotato
DCOM-based privilege escalation tool for Windows Server 2012-2022 and Windows 8-11, elevating users with ImpersonatePrivilege to NT AUTHORITY\SYSTEM…
 rapid7/metasploit-javapayload
Obsolete Java payload library for Metasploit, providing Java and Android Meterpreter agents built with Maven. Merged into metasploit-payloads.
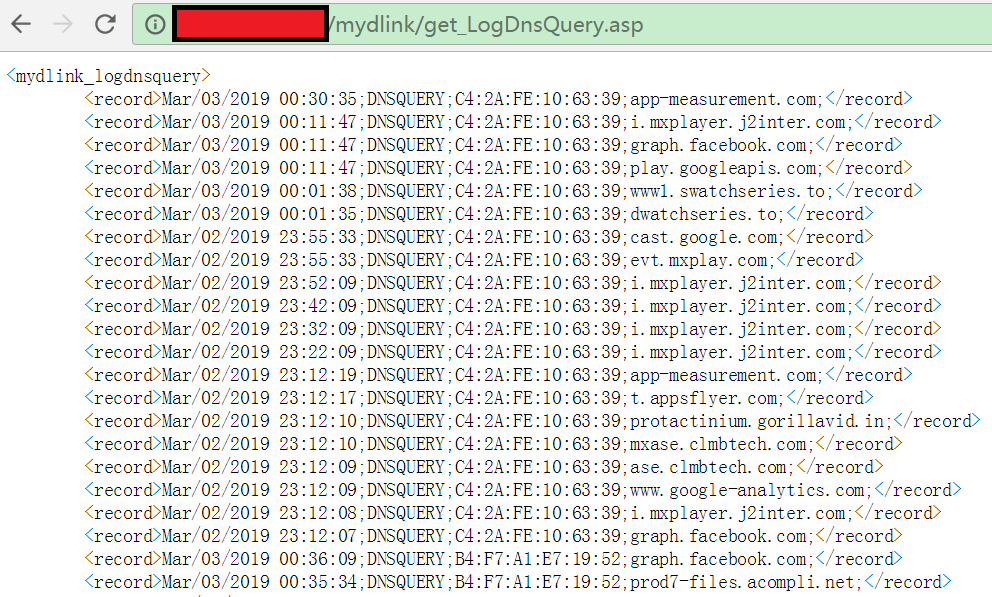 xw77cve/cve-2019-7642
Proof-of-concept exploit for CVE-2019-7642 demonstrating unauthenticated access to DNS query logs and login history on vulnerable D-Link routers via…
 u20024804/bash-3.2-fixed-cve-2014-6271
Patched GNU Bash 3.2 with a fix for CVE-2014-6271 (Shellshock). Provides a standard POSIX shell with command-line editing, job control, and history…