Vulnerability-Disclosures

Curated repository of vulnerability disclosures from Mandiant, including CVEs discovered through internal research, red team assessments, and wild…

Curated repository of vulnerability disclosures from Mandiant, including CVEs discovered through internal research, red team assessments, and wild…

Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Proof-of-concept for CVE-2026-118383, an unauthenticated MongoDB use-after-free in replication catch-up, with wire-protocol exploit scripts, a gdb…

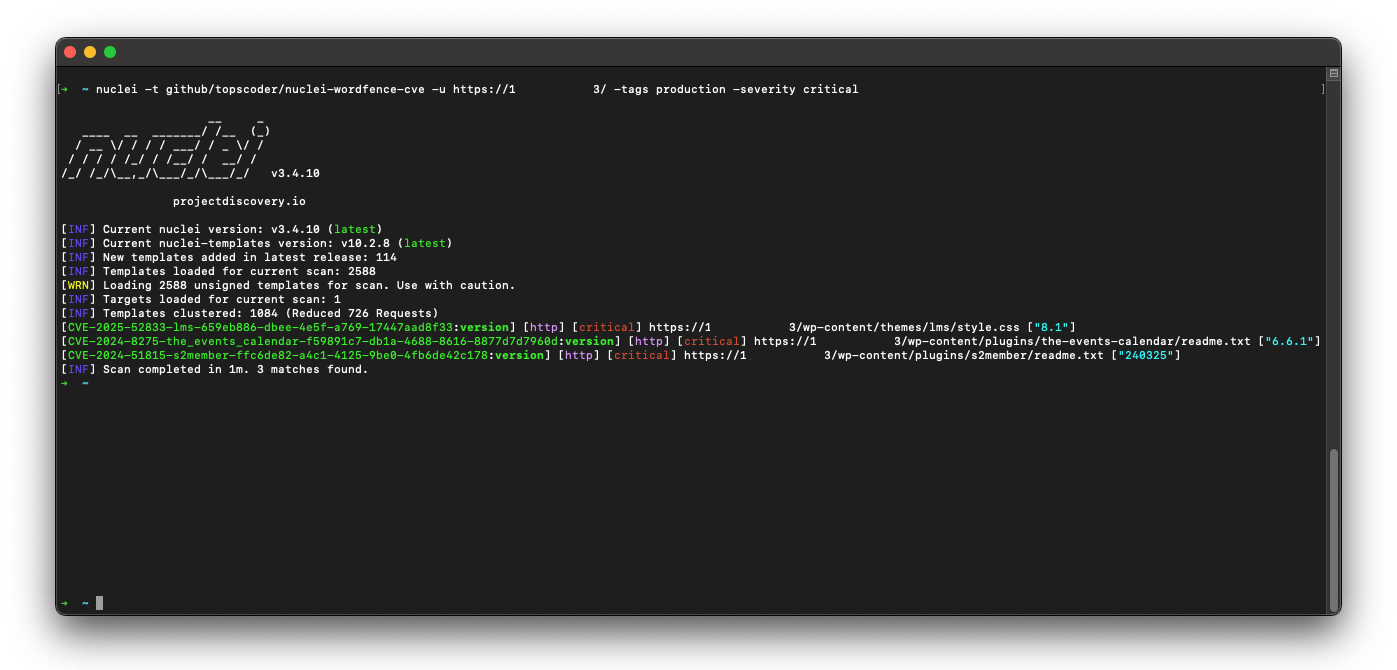
80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

Automatic SQL injection and database takeover tool

📡 PoC auto collect from GitHub. ⚠️ Be careful Malware.

Search public CVE proof-of-concept exploits from GitHub, Nuclei, ExploitDB, Metasploit and Vulhub, with CVSS, EPSS and CISA KEV context.

Mobile Edge-Dynamic Unified Security Analysis

A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24…

Automated Αll-in-One OS command injection exploitation tool.

Curated repository of CVE records with CVSS scoring, providing a structured reference for vulnerability analysis, exploitation research, and security…

The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…

Android kernel POSIX CPU timer use-after-free exploit for 6.12.69 that achieves uid=0 shell or KernelSU late-load via fake credentials.

Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…

UNIX-like reverse engineering framework and command-line toolset.

Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.