CVE-2026-79397-Authenticated-OS-Command-Injection-in-ONT-4GE-RFDW-Ping-Diagnostics

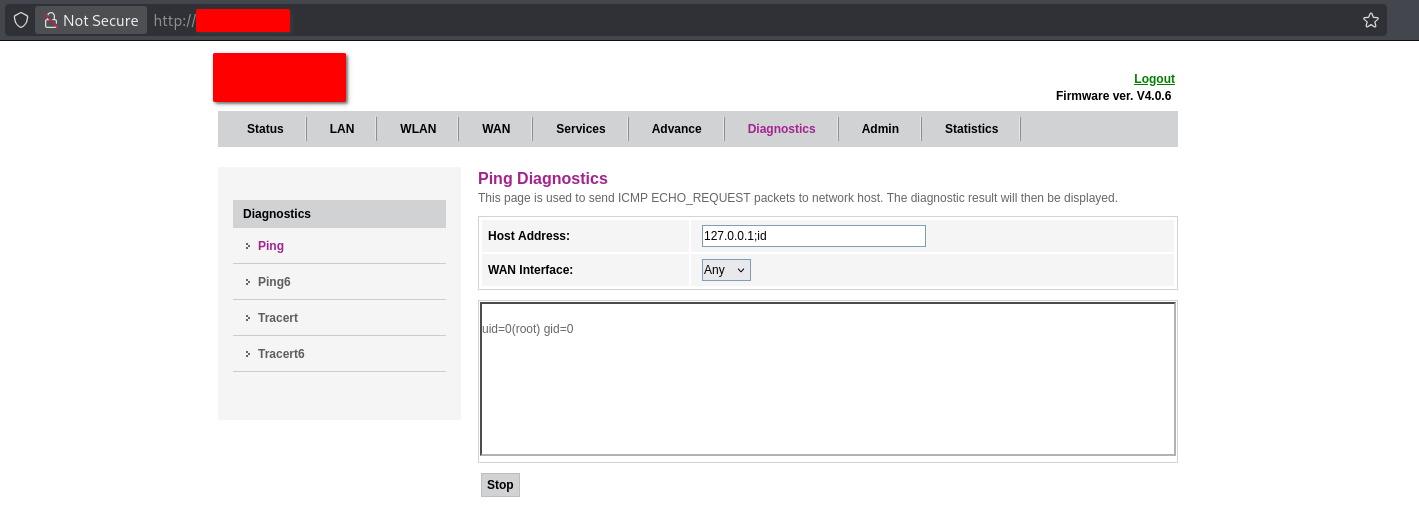
Advisory and proof of concept for an authenticated OS command injection in the ONT-4GE-RFDW web Ping diagnostics, exploitable via default superadmin…

Advisory and proof of concept for an authenticated OS command injection in the ONT-4GE-RFDW web Ping diagnostics, exploitable via default superadmin…

Payload injection tool for Nintendo Switch consoles vulnerable to CVE-2018-6242 ("Fusée Gelée")

This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.

This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices

A tool to manipulate Schneider Electric PLC archive files

Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.

Explotation framework for CVE-2019-11687

RMASmoke main repo. CVE-2025-1122

CVE-2017-5693 Denial of service vulnerability in Puma 6 modems

Go-based brute-force exploit tool targeting Hikvision cameras vulnerable to CVE-2021-36260, with multi-threaded scanning and configurable…

Maxprint Maxlink 1200G v3.4.11E has an OS command injection vulnerability in the "Diagnostic tool" functionality of the device.

Dictionary Brute Force of the Mikrotik RouterOS 6.x Web Interface

Printer Exploitation Toolkit - The tool that made dumpster diving obsolete.

Proof-of-concept exploit for CVE-2023-36143 demonstrating command injection in Maxprint Maxlink 1200G v3.4.11E via the diagnostic tool web interface.

Exploit and tooling for Amlogic-based Sonos devices: dumps OTP/eFUSE via an EL3 exploit, extracts LUKS decryption keys, and fetches/decrypts OTA…

Exploit for CVE-2022-4510 enabling remote command execution in Binwalk firmware analysis tool. Provides proof-of-concept code for security testing…

Long Range Pager Systems pagers and coasters URH and YS1 (yardstick one / cc11xx) information and brute force tool

Exploit tool for CVE-2018-9995 that extracts credentials from vulnerable DVR devices via Google dorking and direct IP access.