
CVE-2019-9053
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
exploitationpassword-crackingpenetration-testing+3
11
4nner/cve-2019-9053Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 applied-risk/loracrack
LoRaWAN session cracker - A PoC for exploiting weak or shared Application Keys
 xv0nfers/v8-sbx-bypass-collection
Curated collection of V8 sandbox escape, bypass, and violation reports with issue tracker links, articles, papers, slides, and design documents for…
 al1ex/php_mt_seed
php_mt_seed is a PHP mt_rand() seed cracker
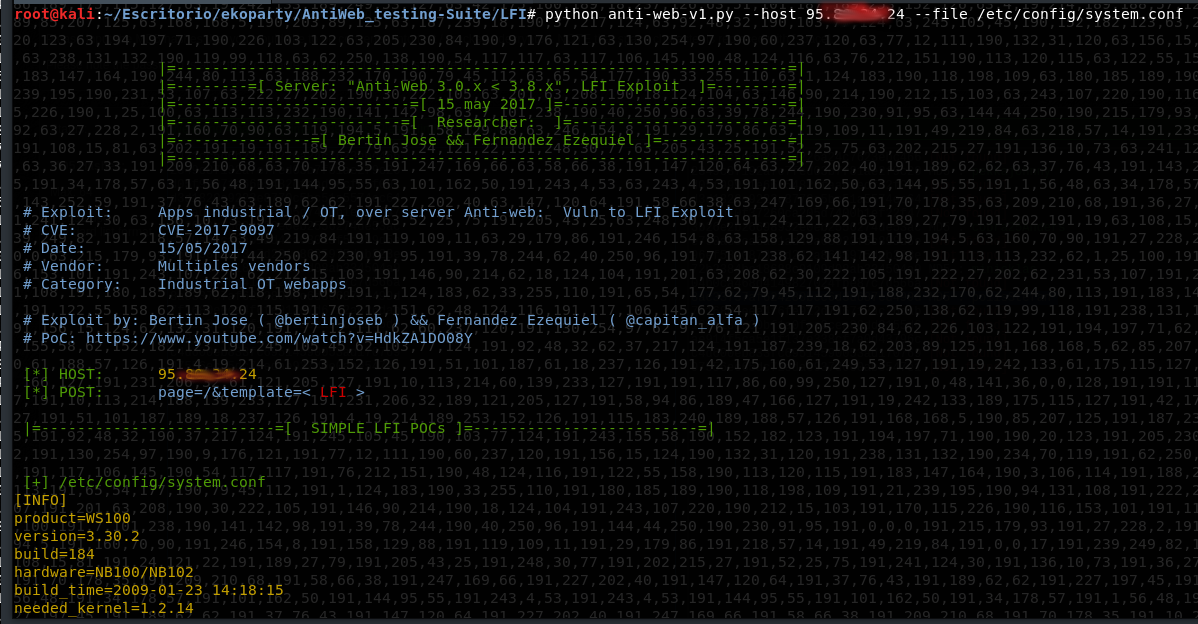 mdudek-ics/antiweb_testing-suite
Suite de herramientas que sacan partido del CVE-2017-9097 (+RCE)
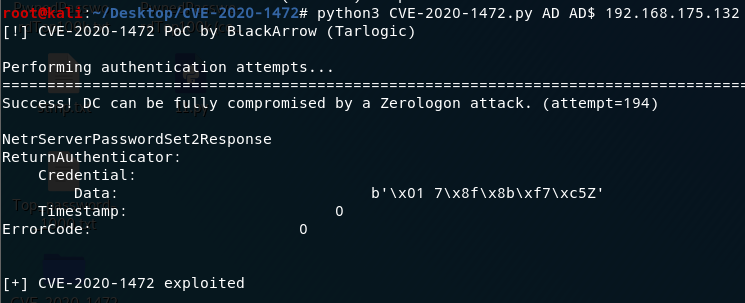
 mstxq17/cve-2020-1472
cve-2020-1472 复现利用及其exp
 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC
 und3sc0n0c1d0/bruteforce-to-keepass
This script complements the results obtained through the keepass-password-dumper tool when exploiting the CVE-2023-32784 vulnerability affecting…
 z-bool/venom-jwt
针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)
 dh4nuj4/simplectf-updatedexploit
This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…
 kaihaochen04/monikerlinktest
cve-2024-21413
 twisted007/mantis_rce
Python script to obtain RCE on Mantis Bug Tracker prior to version 1.2.x Check CVE-2008-4687 for additional information
 hackheart-tech/-exploit-lab
Exploits Python cve-2019-9053– by HackHeart
 ninajafli/dotcms-cve-2022-45782
Proof-of-concept for CVE-2022-45782: predictable dotCMS password-reset tokens, with a token cracker and full exploit chain.
 suominen/cve-2026-9256
Tracking the nginx CVE-2026-9256 rewrite-module heap overflow