
tfo-connect-bypass
 4n4s4zi/tfo-connect-bypass
Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
exploitationids-ips-evasionnetwork-security+3
1
4n4s4zi/tfo-connect-bypassUsing TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
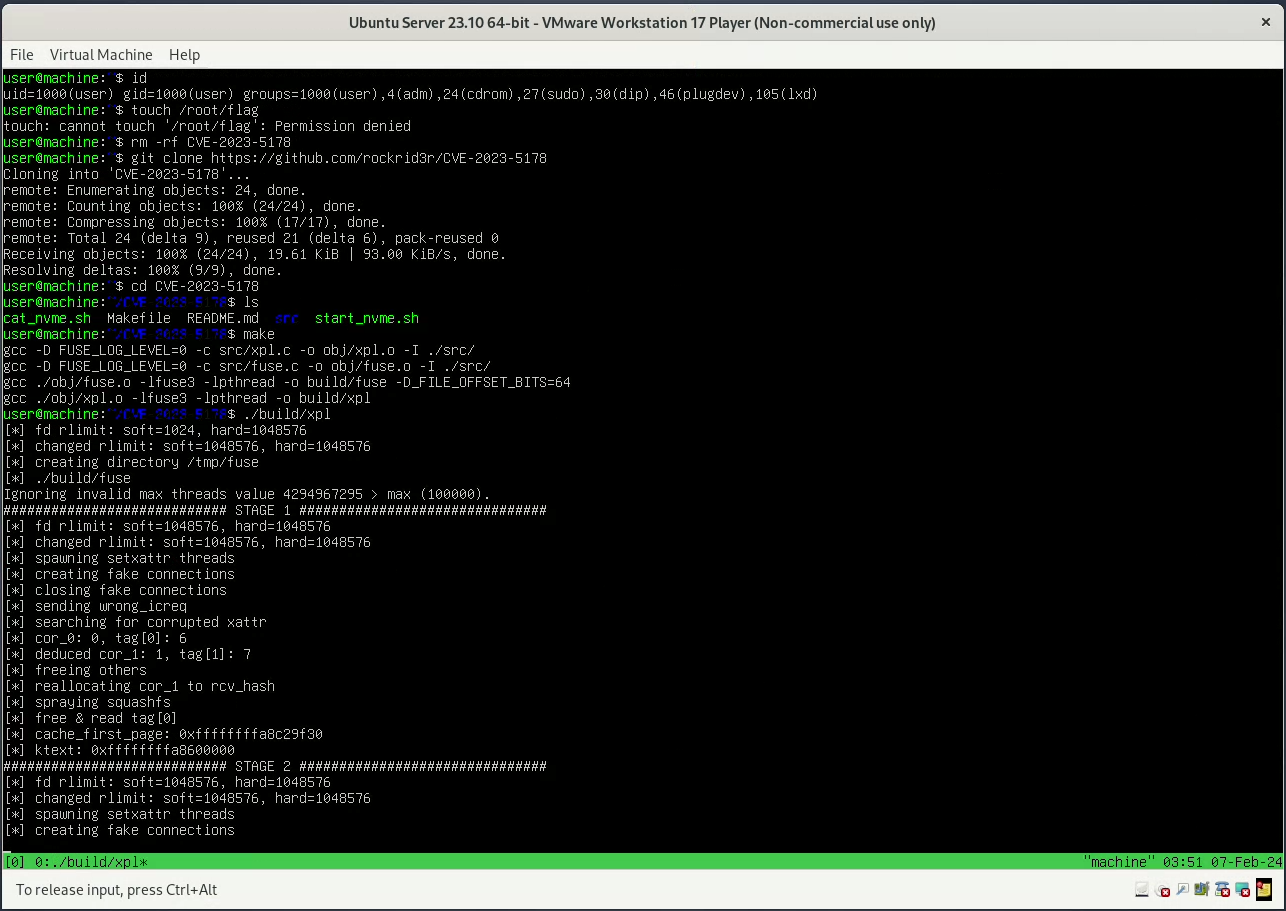 rockrid3r/cve-2023-5178
Exploit for CVE-2023-5178
 speedyfriend433/cve-2026-28867-poc
Kernel info leak Proof of Concept patched in iOS 26.4 / macOS 26.4
 obrige/http2-bomb
CVE-2026-49975 HTTP/2 Stream Amplification — Docker PoC with Web Console
 keymaker-arch/ksmbdrain
Proof-of-concept exploit for CVE-2025-38501 that remotely exhausts KSMBD SMB server connection limits via incomplete TCP handshakes, enabling…