
neo8-ghostlock-adaptation
 mke84/neo8-ghostlock-adaptation
iQOO Neo8 (PD2301, 5.10.246 GKI) CVE-2026-43499 GhostLock 适配 · 48 宏 target.h + offsets.json + 15 轮实测 log · 只缺 write layer
android-securitybinary-exploitationexploitation+5
1
mke84/neo8-ghostlock-adaptationiQOO Neo8 (PD2301, 5.10.246 GKI) CVE-2026-43499 GhostLock 适配 · 48 宏 target.h + offsets.json + 15 轮实测 log · 只缺 write layer
 cxlfhx/ghostlock-pfem10
GhostLock (CVE-2026-43499 / IonStack) research for OPPO Find X5 Pro (PFEM10): exploit chain, progress, blocker log, and OPPO 5-series kernel notes
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 mein-0/kaspermeow
Proof-of-concept that exploits a Kaspersky driver vulnerability to leak kernel pointers and bypass KASLR on Windows, enabling kernel exploit chain…
 juanpoch/cve-2026-73570
Zimbra Collaboration Suite RCE — SMTP log poisoning → swatchdog → OS Command Injection (CVSS 8.9, CISA KEV)
 nhh9905/cve-2026-62735
Proof-of-concept for CVE-2026-62735, an integer overflow in http.sys leading to heap overflow and SYSTEM shell. Includes crash log and stack trace…
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
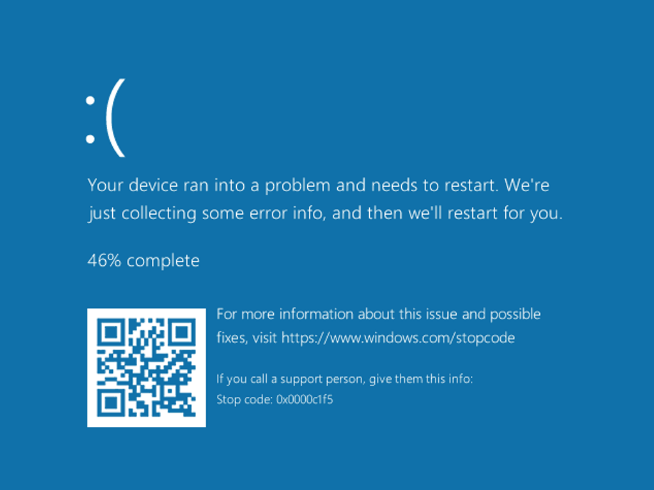 oxfemale/cve-2026-2636_poc
Proof-of-concept for CVE-2026-2636, a Windows CLFS.sys vulnerability causing BSoD via ReadFile on CreateLogFile handle, enabling unprivileged denial…
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
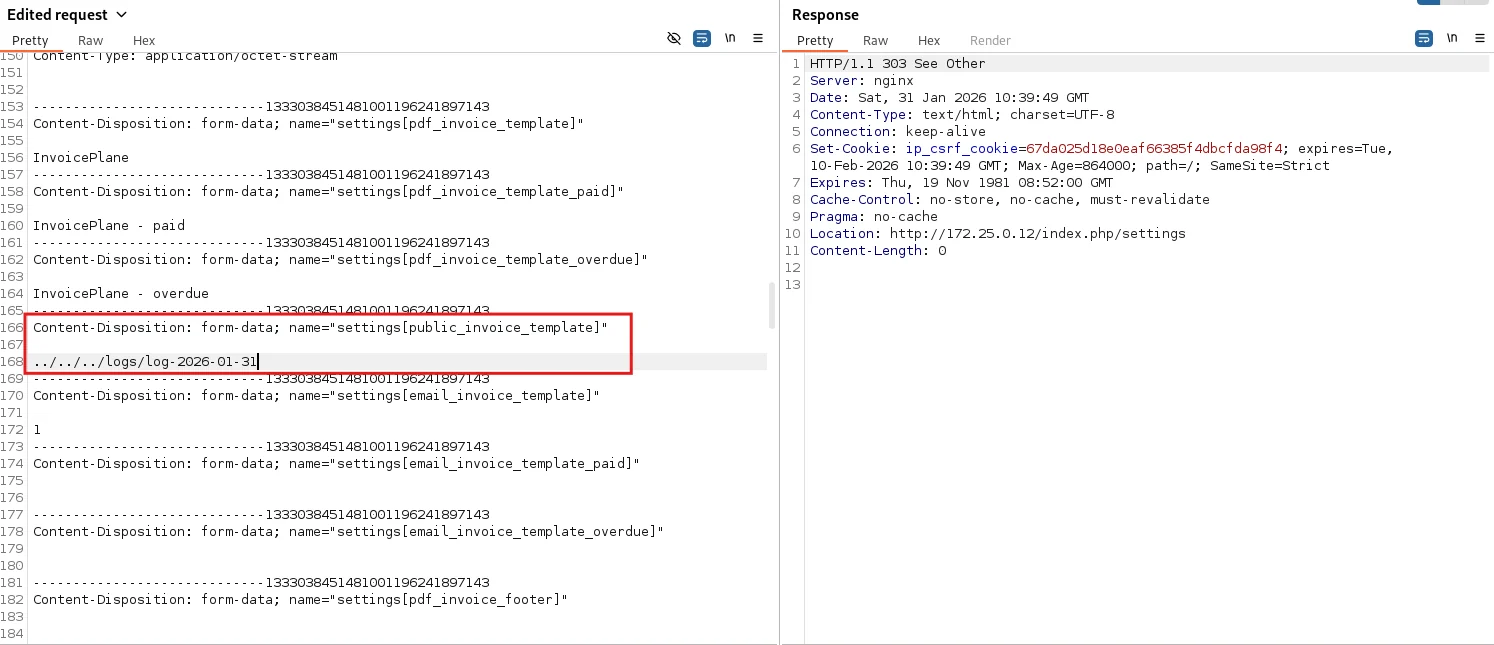 lagathos/cve-2026-25548
Detailed technical write-up and proof-of-concept for CVE-2026-25548, a critical RCE in InvoicePlane 1.7.0 via LFI and log poisoning, including attack…
 snipersmaster/cve-2026-0709
Python proof-of-concept for authenticated command injection in Hikvision wireless APs, enabling remote code execution testing with customizable…
 adityabhatt3010/cve-2025-61882-oracle-e-business-suite-pre-auth-rce-exploit
A critical pre-authentication Remote Code Execution (RCE) flaw in Oracle E-Business Suite (versions 12.2.3 - 12.2.14) allows attackers to gain full…
 zmkeh/cve-2025-29824-clfs-local-privilege-escalation
Local privilege escalation exploit for CVE-2025-29824 targeting the Windows Common Log File System (CLFS) driver, providing proof-of-concept code for…
 nhh9905/cve-2026-34344
PoC for CVE-2026-34344, a Windows afd.sys type confusion causing a kernel crash via AfdQueryProviderInfo. Provides trigger code, crash log, and…
 s0/rsyslog-librelp-cve-2018-1000140-fixed
Patch for CVE-2018-1000140 in rsyslog's librelp library, fixing a remote code execution vulnerability in the reliable event logging protocol…
 s0/rsyslog-librelp-cve-2018-1000140
Pinned version of rsyslov vulnerable to CVE-2018-1000140
 kaleth4/cve-2026-64638
Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…
 biutrap/cve-2026-59310
Proof-of-concept exploit for CVE-2026-59310, demonstrating remote path traversal via crafted syslog messages to write arbitrary log files on VMware…