

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
313 results
confirmesc preview

confirmesc

GitHubcapture0x/confirmesc

Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…

ai-securitycommand-and-controlctf+7
1
20 days ago
AdStrike preview

AdStrike

GitHubcapture0x/adstrike

AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…

ai-securitycommand-and-controlexploitation+7
3704 months ago
external-c2-experiments preview

external-c2-experiments

GitHubvulncheck-oss/external-c2-experiments

Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…
command-and-controlexploitationexploit-frameworks+6
11 year ago
CVE-2026-41089-PoC preview

CVE-2026-41089-PoC

GitHub1posix/cve-2026-41089-poc

CVE-2026-41089 LongLogon: pre-auth CLDAP (UDP/389) stack buffer overflow crasher for unpatched Windows Server 2025 Netlogon (lsass 0xc0000409).…
exploitationnetwork-securitypenetration-testing+2
26 days ago
CVE-2026-49975 preview

CVE-2026-49975

GitHubyym8538/cve-2026-49975

Proof-of-concept HTTP/2 Bomb exploit for CVE-2026-49975, a cookie-header memory exhaustion DoS in Apache HTTP Server 2.4.17-2.4.67, with Docker lab…

exploitationnetwork-securityred-teaming+2
12 months ago
CVE-2026-65660-Poc preview

CVE-2026-65660-Poc

GitHubshadowforge-cyber/cve-2026-65660-poc

Malicious Register Directive Code Injection Exploit
command-and-controldata-exfiltrationexploitation+8
127 days ago
CVE-2026-50369 preview

CVE-2026-50369

GitHubmofarthim/cve-2026-50369

PoC reproducer for CVE-2026-50369, a TOCTOU race condition in rdpcorets.dll on Windows Server 2025 RDS Session Hosts causing TermService DoS via RDP…
exploitationpenetration-testingred-teaming+1
3 months ago
CVE-2026-24061-payload preview

CVE-2026-24061-payload

GitHubilokaas/cve-2026-24061-payload

A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass
authenticationexploitationpenetration-testing+3
1 month ago
CVE-2025-55182-poc preview

CVE-2025-55182-poc

GitHubuwugreed/cve-2025-55182-poc

I know you are probably here from Hack the Box, if so, yes this one actually works.
exploitationpayload-developmentpenetration-testing+3
1 month ago
weblogic preview

weblogic

GitHubhyderpwn/weblogic

Unauthenticated authentication bypass and remote code execution exploit for Oracle WebLogic Server, targeting CVE-2020-14882 and CVE-2020-14750.
exploitationpenetration-testingred-teaming+2
11 month ago
msdt-follina preview

msdt-follina

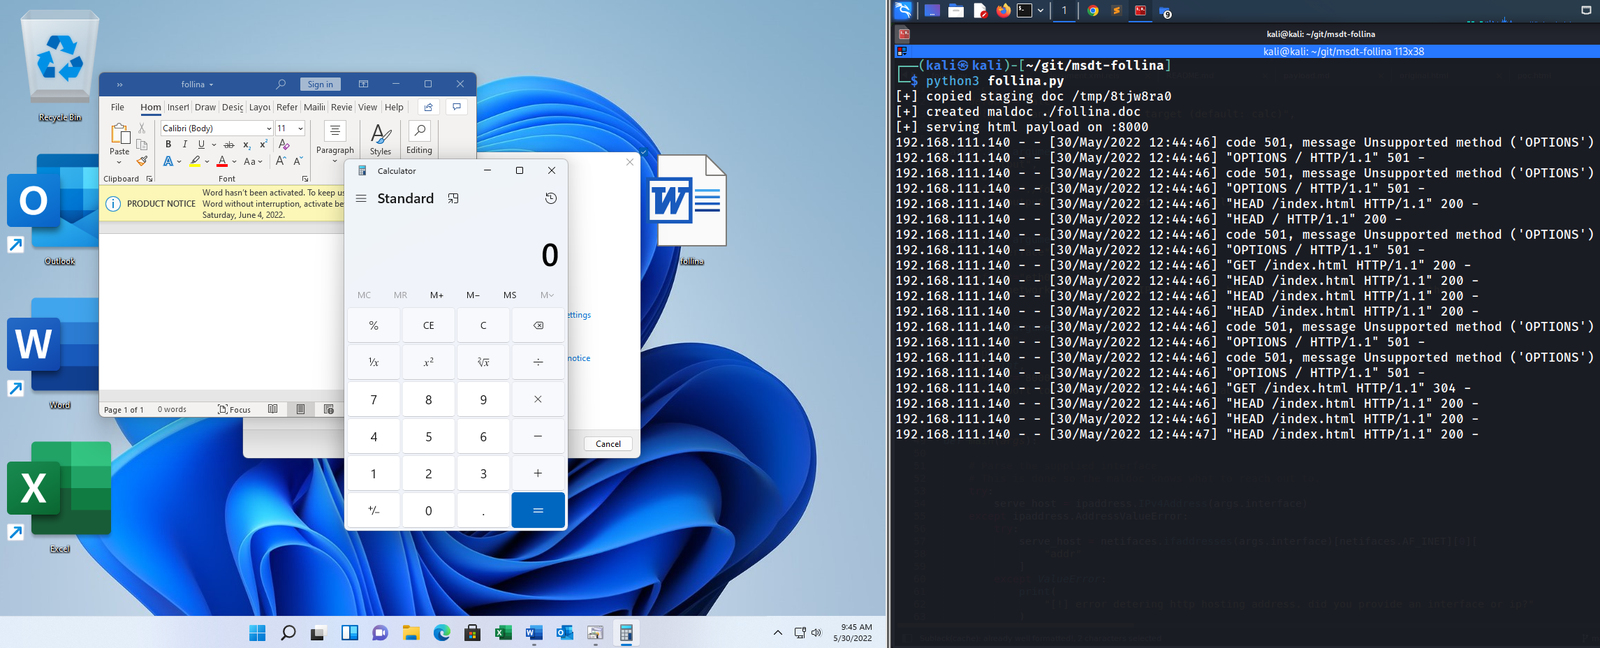
GitHubjohnhammond/msdt-follina

Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
command-and-controlexploitationpayload-development+2
1.6k4 years ago
CVE-2026-21962 preview

CVE-2026-21962

GitHubzeetee1235/cve-2026-21962

Verified PoC and analysis for CVE-2026-21962, an access-control bypass in Oracle HTTP Server/WebLogic Proxy Plug-in via URI normalization…
exploitationpenetration-testingred-teaming+3
31 month ago
CVE-2026-34227 preview

CVE-2026-34227

GitHubskoveit/cve-2026-34227

Proof-of-concept demonstrating CORS to CSRF chain on Sliver's unauthenticated MCP interface, enabling silent interaction with C2 from any webpage.
command-and-controlexploitationred-teaming+2
16 months ago
CVE-2026-29781 preview

CVE-2026-29781

GitHubskoveit/cve-2026-29781

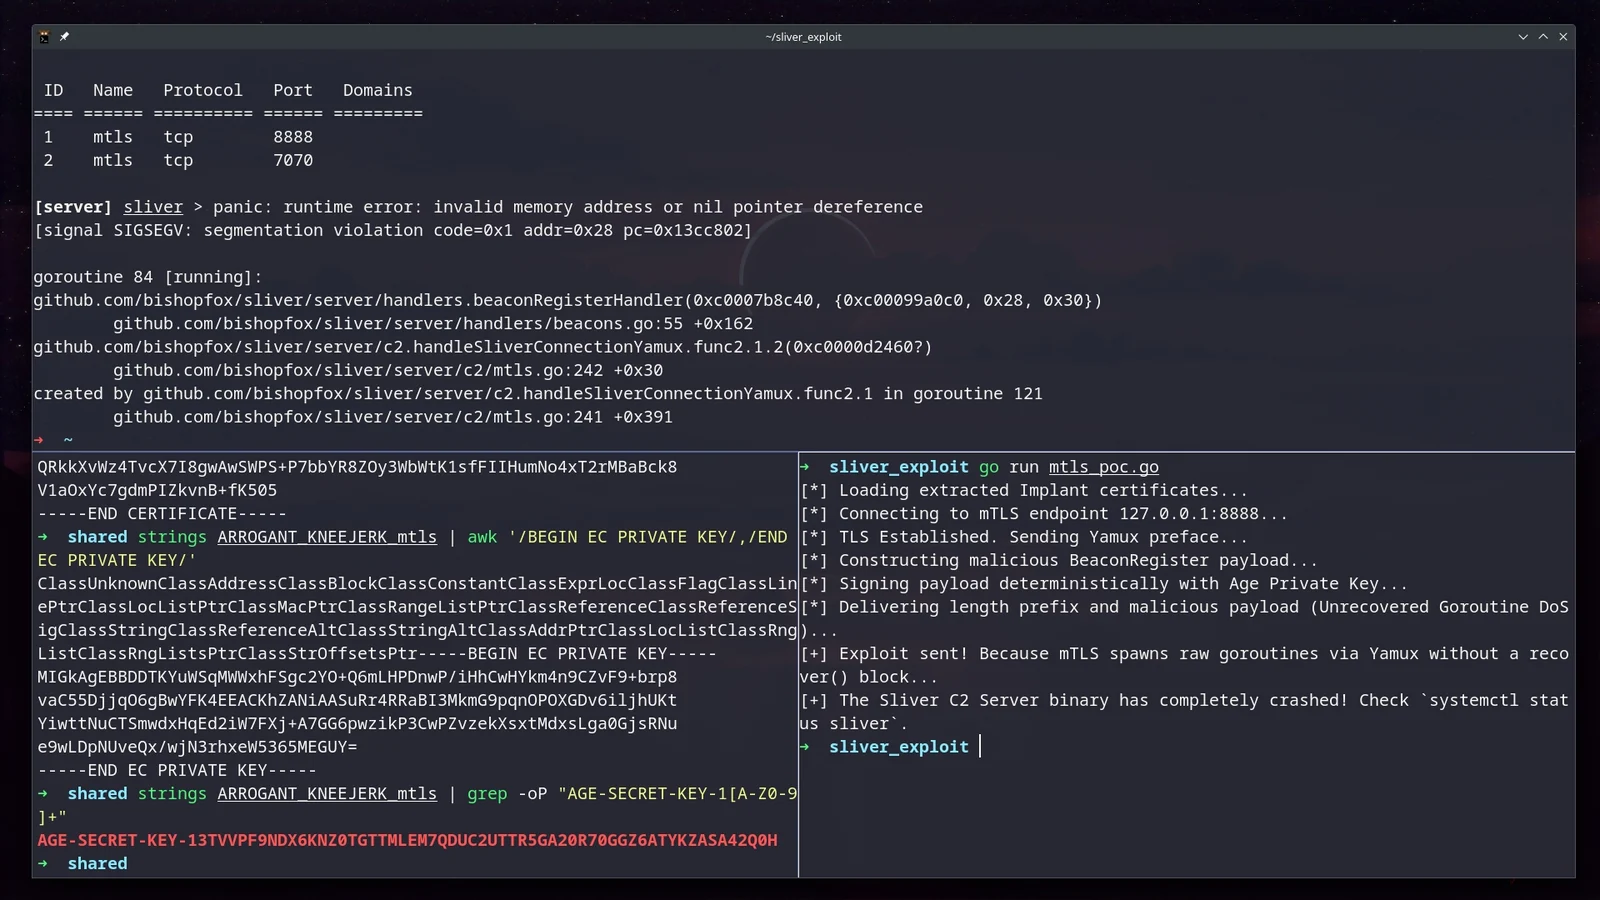
Proof-of-concept exploit for CVE-2026-29781, weaponizing captured Sliver implant credentials to trigger a nil-pointer panic and crash the C2 server…
command-and-controlexploitationpenetration-testing+2
47 months ago
CVE-2026-27180-MajorDoMo-unauthenticated-RCE preview

CVE-2026-27180-MajorDoMo-unauthenticated-RCE

GitHubmbanyamer/cve-2026-27180-majordomo-unauthenticated-rce

Proof-of-concept exploit for CVE-2026-27180, an unauthenticated RCE in MajorDoMo via update URL poisoning, delivering a webshell to the web root.
exploitationpayload-developmentpenetration-testing+3
8 months ago
CVE-2023-22515-joaoviictorti preview

CVE-2023-22515-joaoviictorti

GitHubkillvxk/cve-2023-22515-joaoviictorti

Rust-based exploit for CVE-2023-22515 that creates unauthorized administrator accounts in Confluence Server and Data Center via broken access control.
exploitationpenetration-testingred-teaming+2
2 years ago
cve-2026-21962 preview

cve-2026-21962

GitHubgregk4sec/cve-2026-21962

Proof-of-concept exploit for CVE-2026-21962, a critical path traversal vulnerability in Oracle OHS and WebLogic Server proxy plugins leading to…
exploitationpenetration-testingred-teaming+2
47 months ago
CVE-2023-22527_Confluence_RCE preview

CVE-2023-22527_Confluence_RCE

GitHubga0we1/cve-2023-22527_confluence_rce

CVE-2023-22527 - RCE (Remote Code Execution) Vulnerability In Confluence Data Center and Confluence Server PoC

exploitationpenetration-testingred-teaming+2
12 years ago
Previous12…18Next