
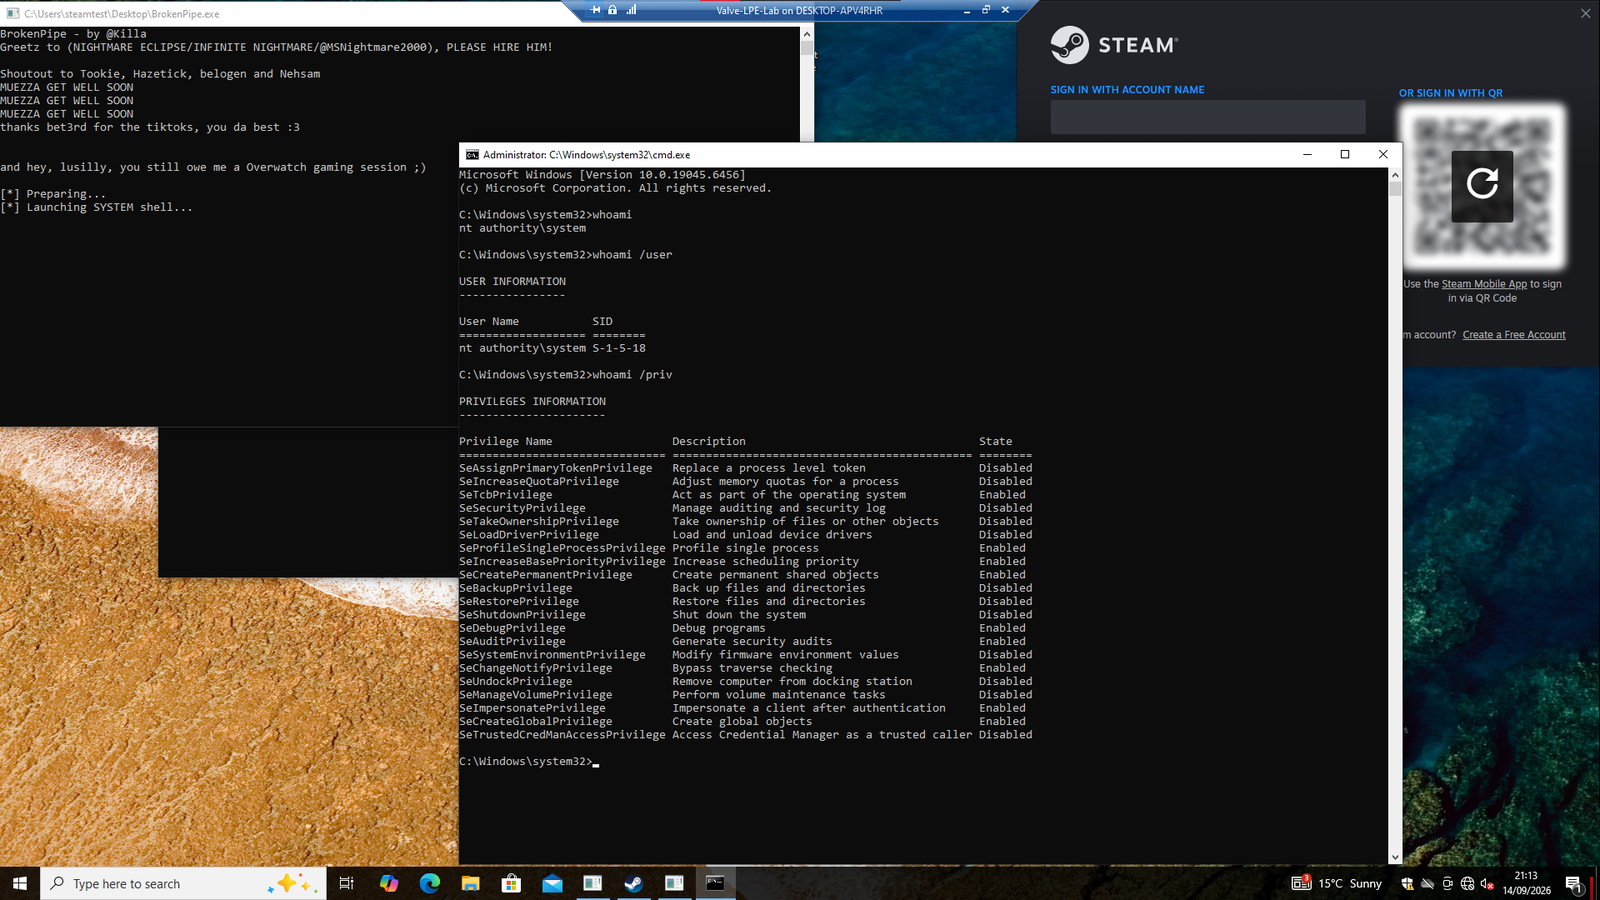
BrokenPipe
 killaboi/brokenpipe
Steam Client Service Local Privilege Escalation Vulnerability
exploitationpenetration-testingpost-exploitation+3
159
killaboi/brokenpipeSteam Client Service Local Privilege Escalation Vulnerability
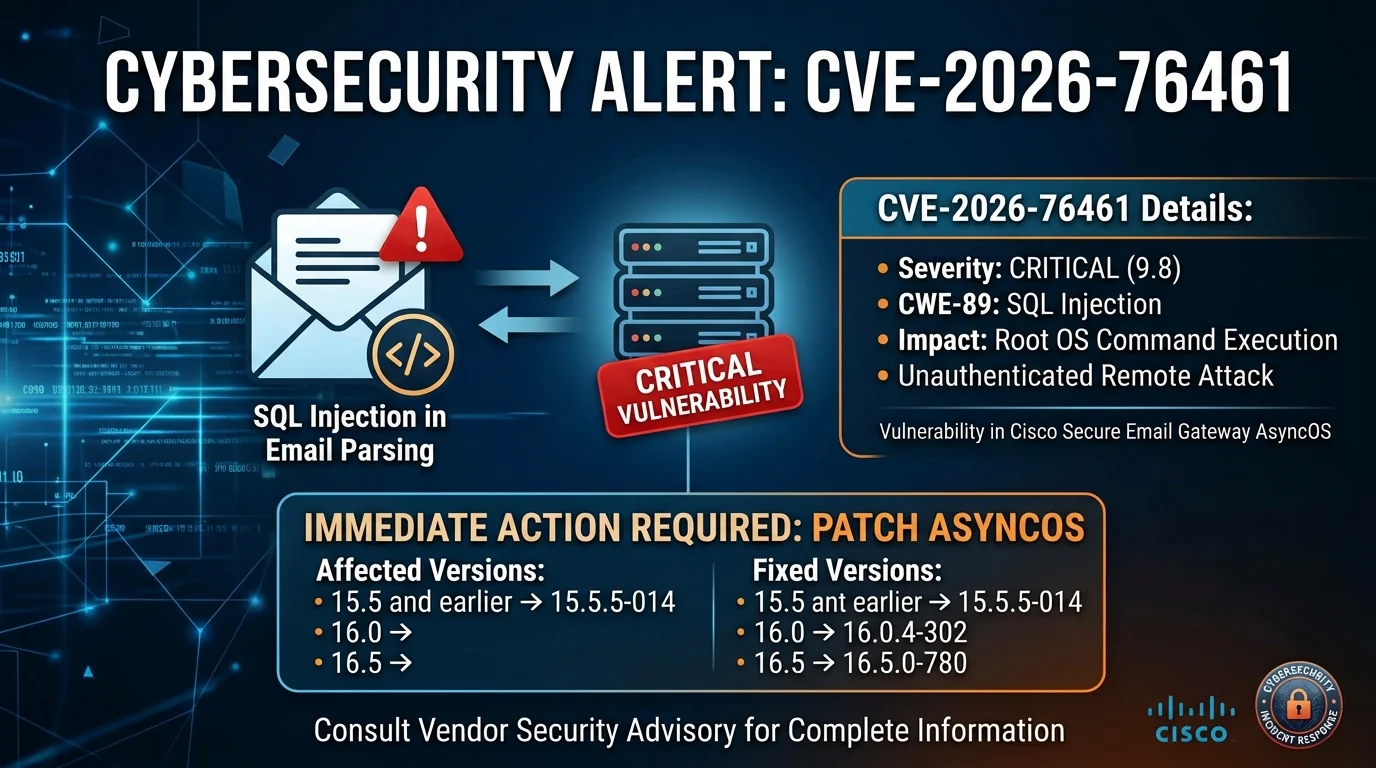 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
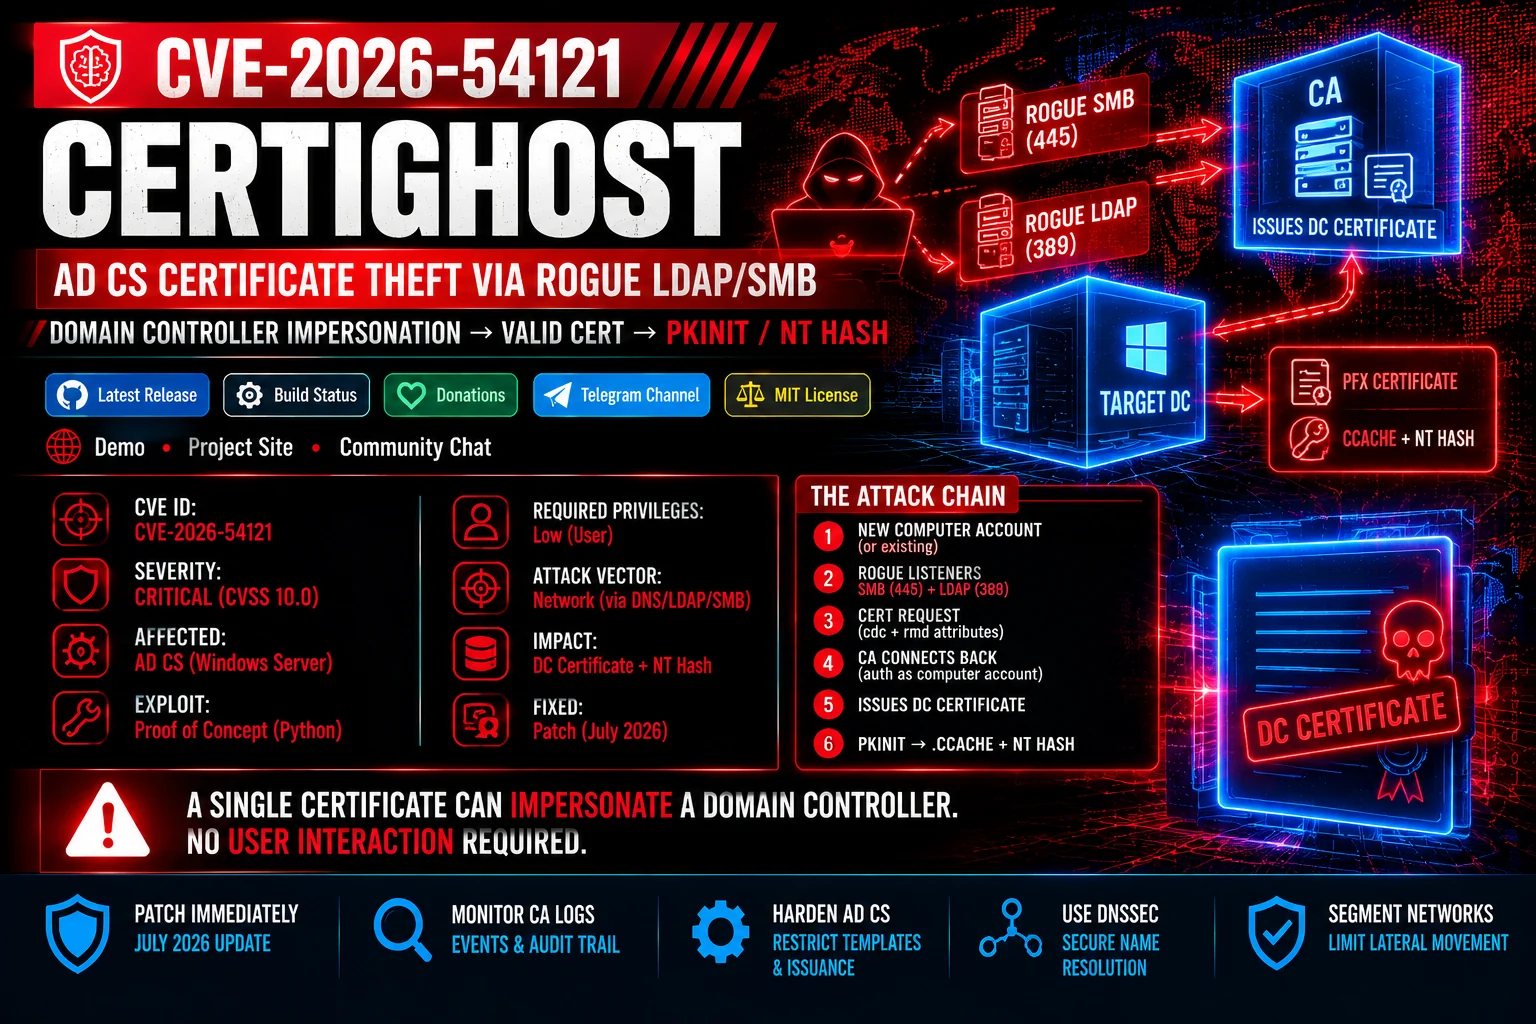 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 foxglovesec/potato
Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 ivanesk315/cve-2026-18963
Docker-based lab and Python exploit for CVE-2026-18963, a Keycloak reset-credentials flow bypass enabling account takeover via email verification…
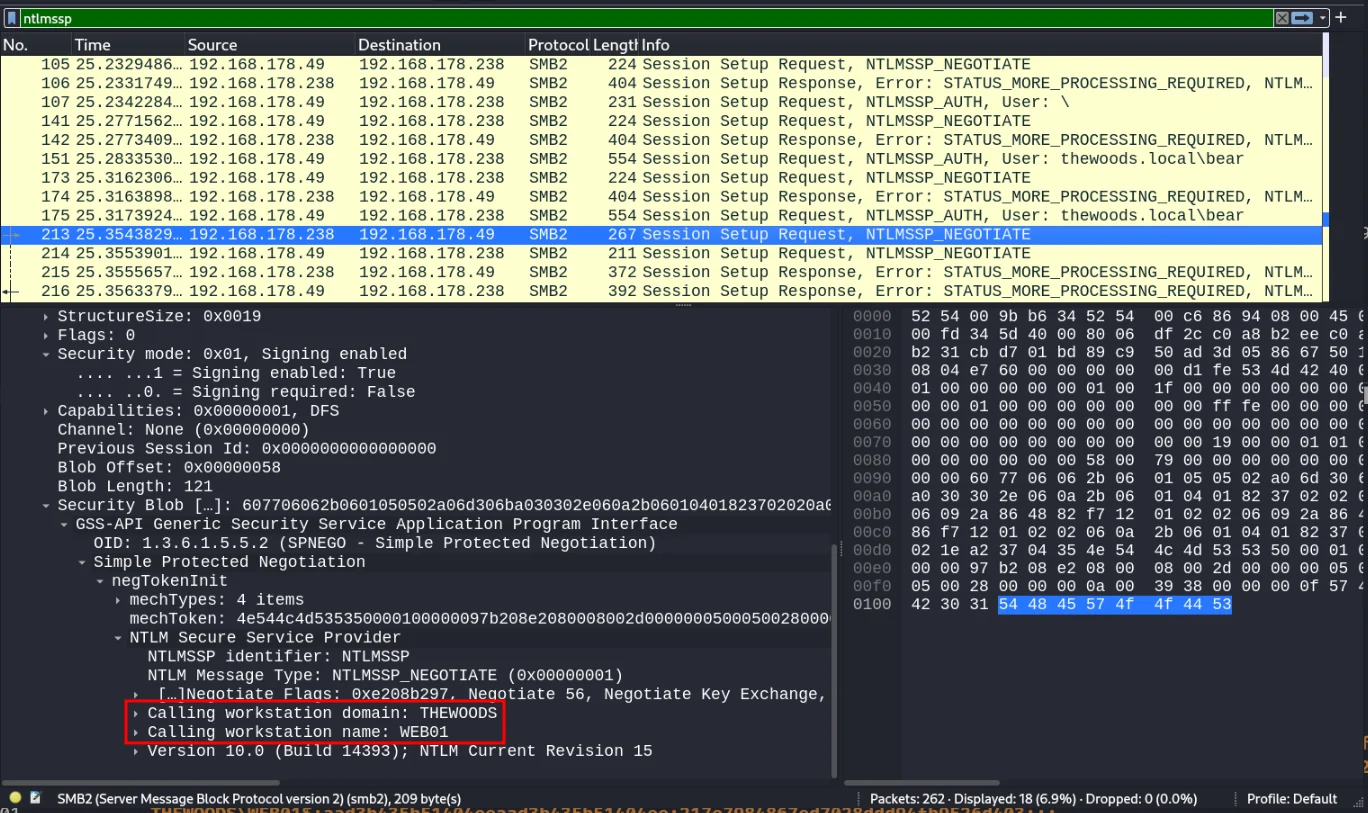 starscow/cve-2025-33073
PoC Exploit for the NTLM reflection SMB flaw.
 feartheploto/gitlab-cve-2023-7028
Mock vulnerable GitLab instance reproducing CVE-2023-7028 password reset hijack. Demonstrates array-based email parameter exploitation and account…
 aerchy/cve-2024-2876
Proof-of-concept exploit for CVE-2024-2876, a critical SQL injection in Email Subscribers by Icegram Express WordPress plugin, allowing…
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
 blackhatexploitation/exploit-for-cve-2026-18963
Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…
 polosss/by-poloss..-..cve-2026-18080
Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 romain-deperne/cve-2026-34975
CRLF email header injection in Plunk raw MIME construction — CVE-2026-34975 / CVSS 8.5
 romain-deperne/cve-2026-33715
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
 prot0tw/keycloak_cve-2026-18963_poc
This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).