
GoGhost
 deepsecurity-pe/goghost
High Performance, lightweight, portable Open Source tool for mass SMBGhost Scan
exploitationnetwork-securityvulnerability-scanners
deepsecurity-pe/goghostHigh Performance, lightweight, portable Open Source tool for mass SMBGhost Scan
 j4ck3lsyn-gen2/cve-2026-63030-wp2r00t
A fully red-team(offensive security) weaponized variant of wp2shell, built for authorized penetration testing & educational purposes.
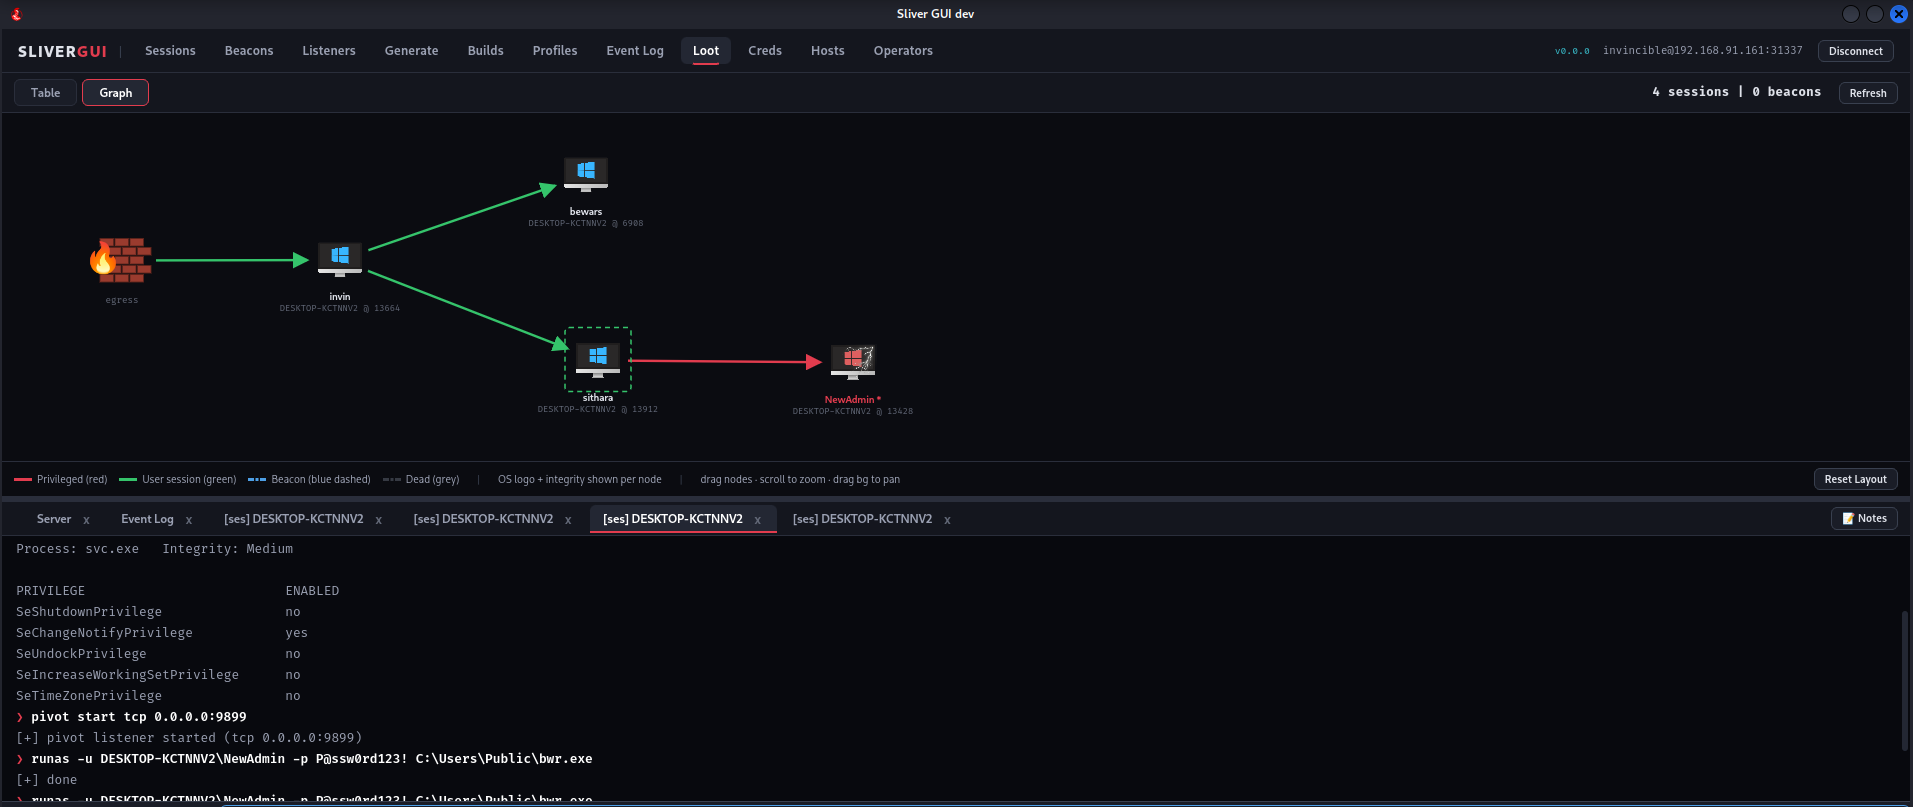 mr-in4inci3le/sliver-gui
A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…
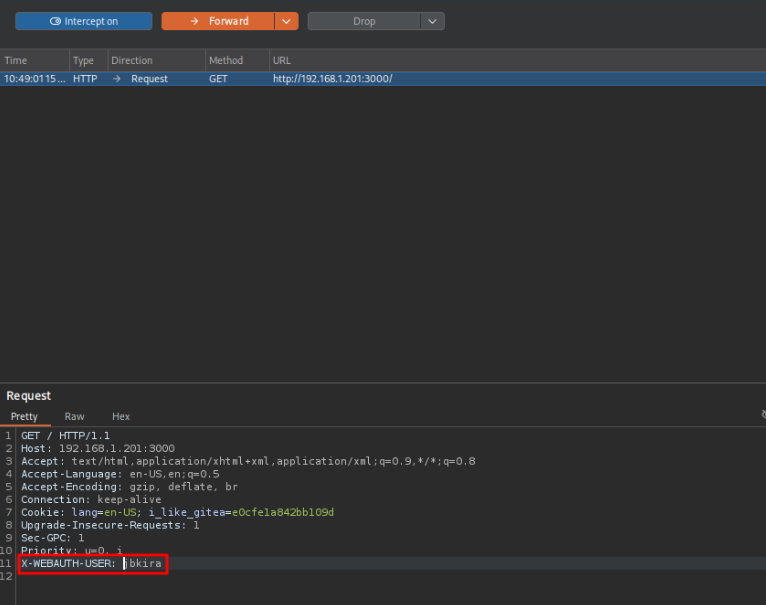 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 deathvu/cve-2024-9474
Proof-of-concept exploit for CVE-2024-9474 targeting Palo Alto PAN-OS. Lightweight Python script for testing vulnerability against specified URLs.
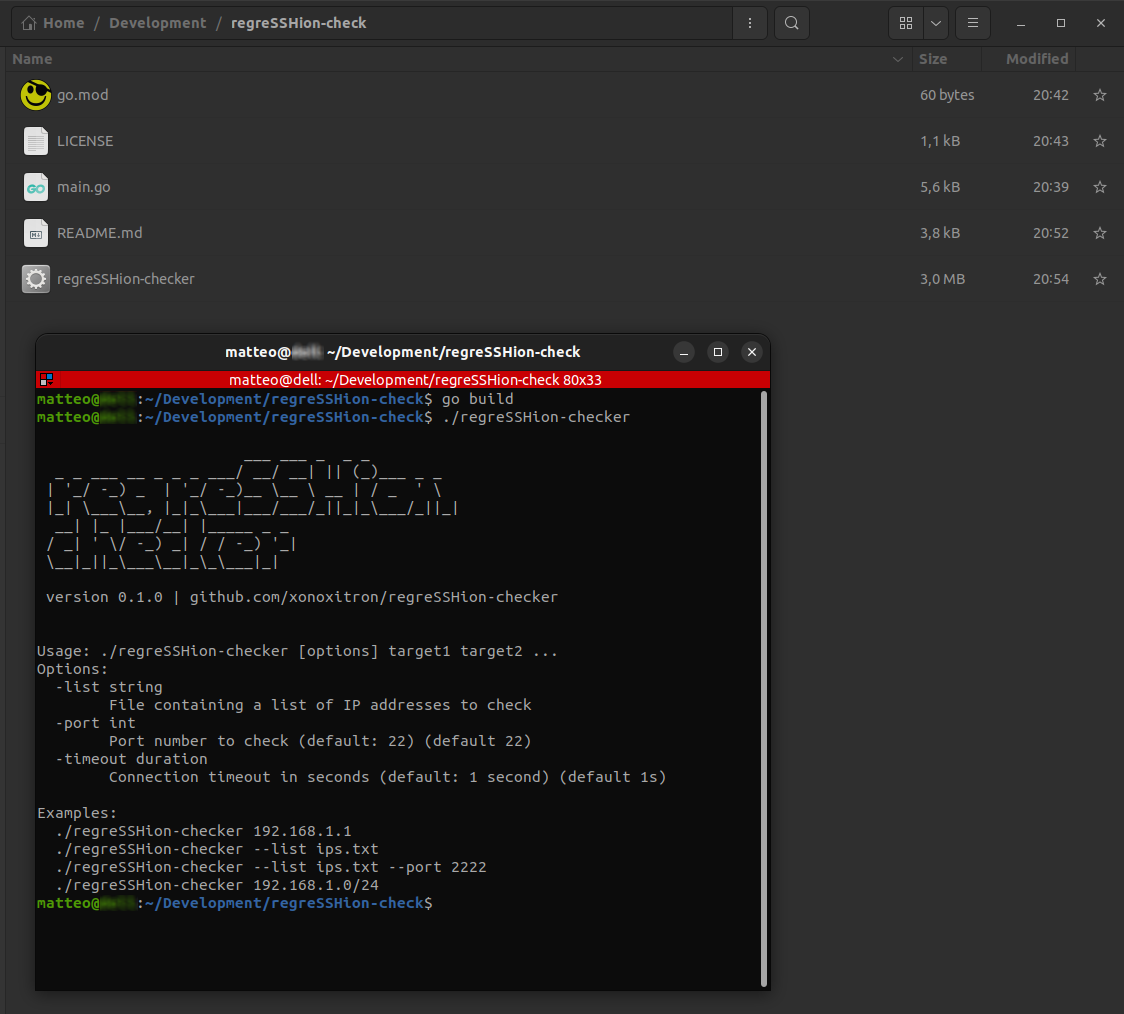 xonoxitron/regresshion-checker
Quickly identifies servers vulnerable to OpenSSH 'regreSSHion' (CVE-2024-6387).
 slayerkkkk/cve-2025-46817-poc
C-based exploit for CVE-2025-46817, a Redis integer overflow vulnerability, enabling crash detection and potential RCE via Lua unpack() payload.
 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
 renukaselvar/lua_cve-2020-24370_afterpatch
Lightweight embeddable scripting language with a C API, supporting procedural, functional, and data-driven programming.
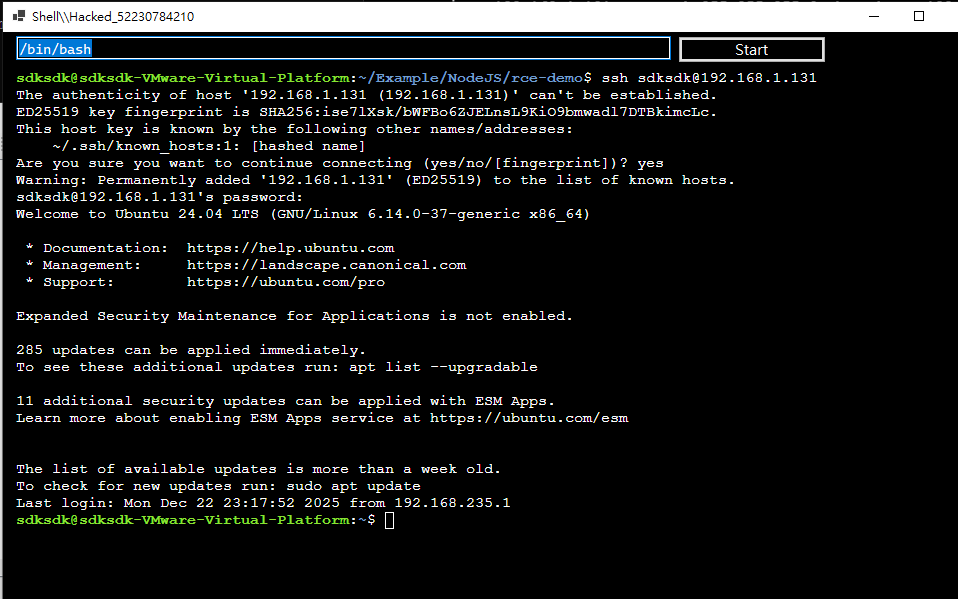 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
 renukaselvar/lua_cve-2020-24370
Lightweight, embeddable scripting language with a fast interpreter, supporting procedural, functional, and object-oriented programming.
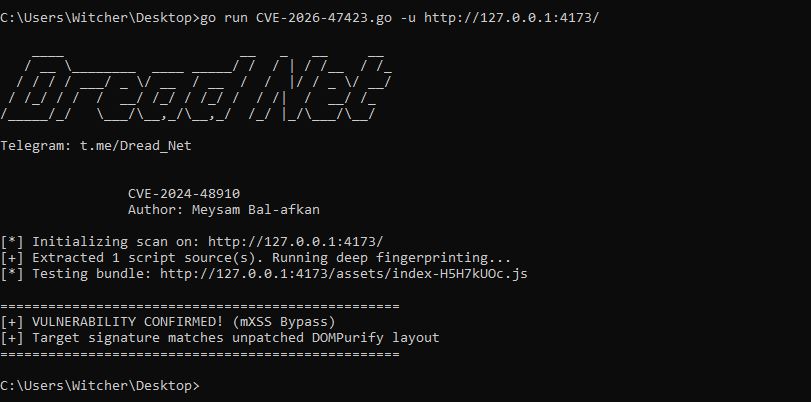 galaxy-sc/cve-2026-47423-dompurify-xss-detector
Go-based scanner that detects DOMPurify sanitizer bypass (CVE-2026-47423) via logic fingerprinting on minified production JavaScript bundles,…
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…
 vanigori/cve-2023-38545-sample
Dockerfile containing all the necessary setup files to demo the exploit
 mrmahile/massscanning-cve-2025-55182
A lightweight orchestrator and worker scanner setup for running large/continuous scans across split input files. This repository contains…
 codiobert/log4j-scanner
Lightweight bash script to quickly scan systems for the Log4j CVE-2021-44228 vulnerability via a one-liner command.
 fan-67/local-mcp
A lightweight stdio-based MCP server for local file system operations — read, write, edit, search, exec for AI assistants. Specially optimized for…
 furkankayapinar/reactnext2shell
CVE-2025-55182 and CVE-2025-66478