CVE-2026-91097-CVE-2026-91106

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

Proof-of-concept exploit for a buffer overflow vulnerability in Tenda routers. Sends crafted unauthenticated POST requests to trigger a crash and…

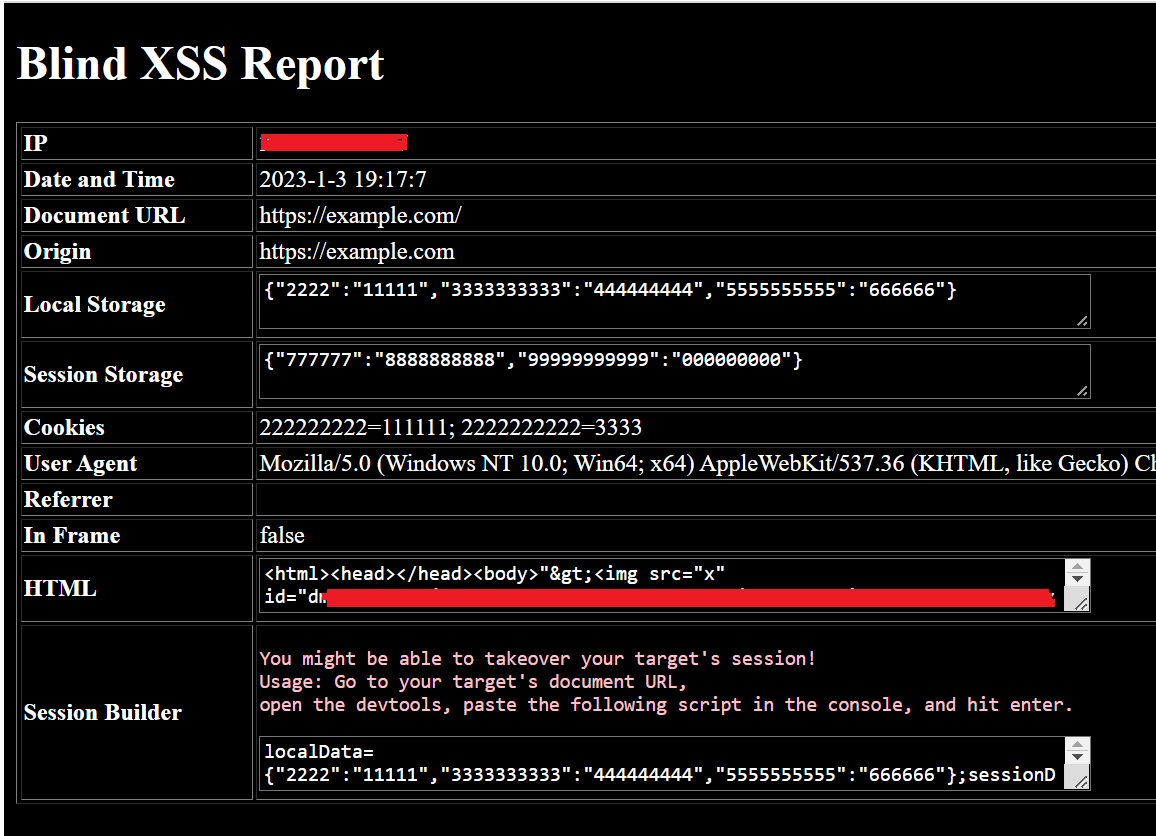
A standalone Blind XSS Script.

Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…

Proof of Concept (PoC) for CVE-2024-7014 (EvilVideo) Exploit

A vehicle network analysis and attack tool.

Frida-based proof-of-concept demonstrating authentication bypass in Telegram Android by hooking SharedConfig.checkPasscode to always return true,…

Exploit script for CVE-2026-41940, an authentication bypass in cPanel/WHM using CRLF injection to gain admin access and change root password, with…

AI Engine <= 3.1.3 - Unauthenticated Sensitive Information Exposure to Privilege Escalation

telegram bug that discloses user's hidden phone number (still unpatched) (exploit included)

GravityForms < 2.9.23.1 - Unauthenticated Arbitrary File Upload

Exploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )

Detailed analysis and PoC for CVE-2025-67887/86 RCE in 1C-Bitrix Translate module, including exploit chain, CVSS scoring, and mitigation…

Bot for Telegram on WooCommerce <= 1.2.4 - Authenticated (Subscriber+) Telegram Bot Token Disclosure to Authentication Bypass

Migration, Backup, Staging <= 0.9.123 - Unauthenticated Arbitrary File Upload

Automated vulnerability scanner for CVE-2023-28121 that checks a list of targets concurrently and delivers results via Telegram notifications.

Telegram Bot to manage botnets created with struts vulnerability(CVE-2017-5638)

LiveHelperChat <=4.61 - Stored Cross Site Scripting (XSS) via Telegram Bot Username