
govuln-CVE-2023-47108
 bahe-msft/govuln-cve-2023-47108
Analyzes and addresses CVE-2023-47108, providing vulnerability assessment and remediation guidance for affected systems.
code-analysisexploitationpenetration-testing+2
bahe-msft/govuln-cve-2023-47108Analyzes and addresses CVE-2023-47108, providing vulnerability assessment and remediation guidance for affected systems.
 christophe.duvernois/usb-spy
Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…
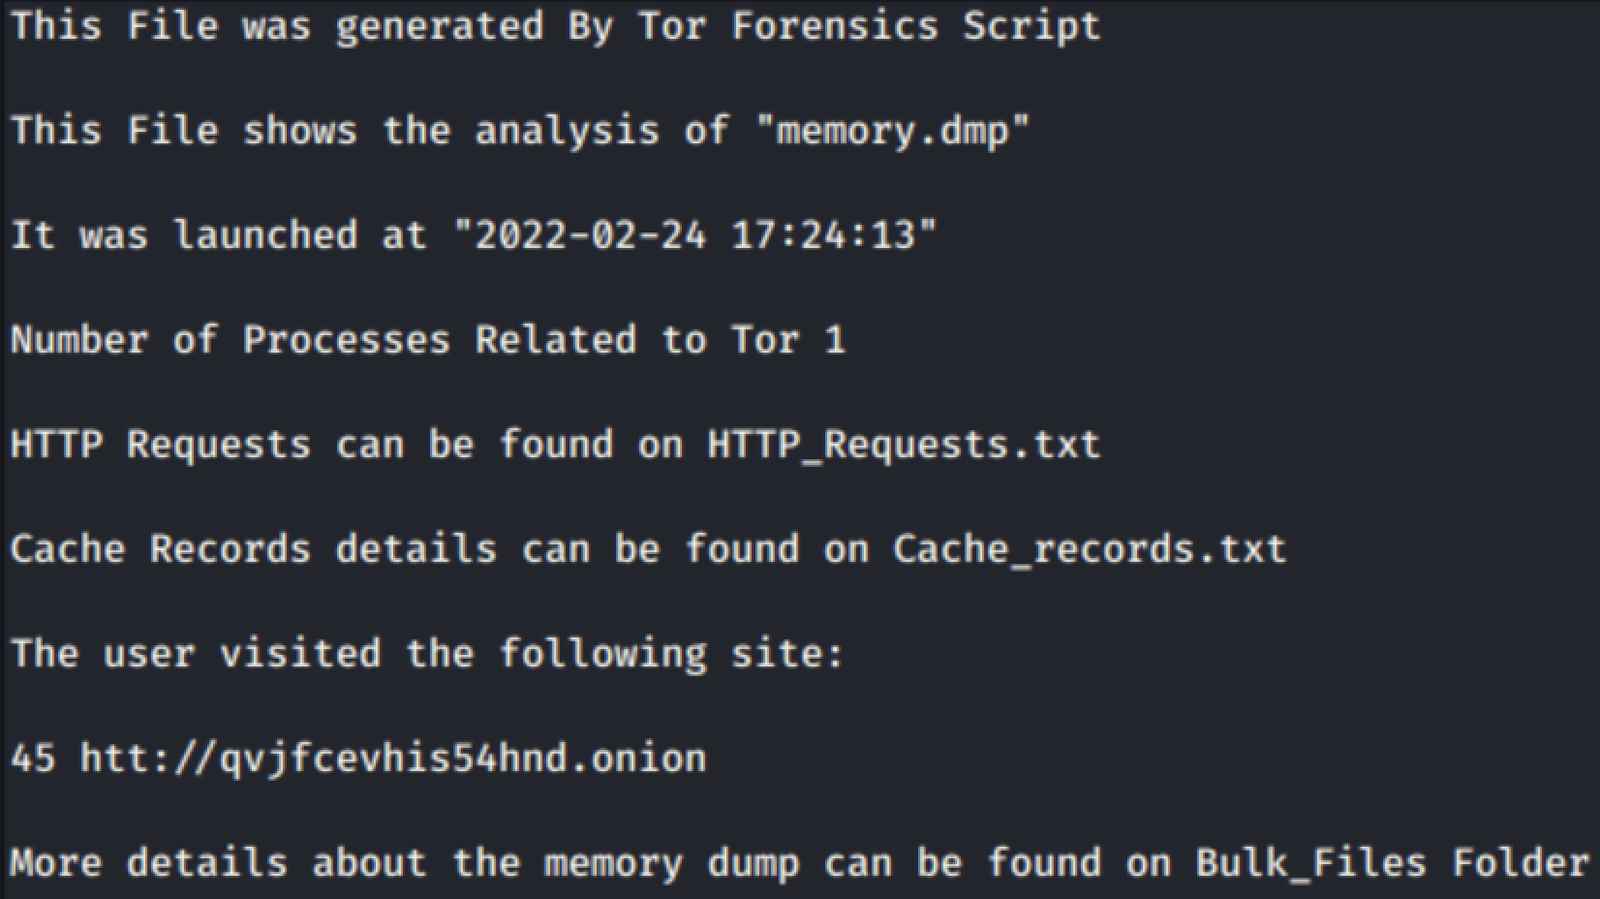 exmak-s/cve-2021-46702
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
 error-inside/cve-2026-39808
Fortinet FortiSandbox 4.4.0-4.4.8 - OS Command Injection via tracer-behavior Endpoint
 miscusi-peek/cheatengine-mcp-bridge
Connect Cursor, Copilot & Claude AI directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using…
 s4dhulabs/vimana-framework
Vimana is a modular security framework for auditing Python APIs and Web applications. The plugin-based architecture enables security professionals to…
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 helgesverre/livewire-honeypot
High-interaction honeypot mimicking a vulnerable Laravel/Livewire app. Captures RCE exploits and webshells targeting CVE-2024-47823, CVE-2025-54068,…
 cobbbex/cisco-asa-vulnerability-research
Systematic reverse engineering of Cisco ASA's lina binary to discover and analyze memory corruption vulnerabilities, including CVE-2025-20333 and…
 yezzfusl/cve_2023_38831_scanner
This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.
 exploitcn/cve-2021-1732-exp-
Analyzes and debugs the CVE-2021-1732 Windows privilege escalation exploit, providing commented code for educational purposes.
 googleprojectzero/sandbox-attacksurface-analysis-tools
Set of tools to analyze Windows sandboxes for exposed attack surface.
 demining/scalar-venom-attack
Exploit and research repository analyzing CVE-2025-60013, a critical HSM initialization vulnerability enabling Bitcoin private key recovery via…
 ir-huntguardians/cve-2023-38831-hunt
PowerShell-based tool to detect and analyze exploitation attempts targeting CVE-2023-38831, aiding incident response and forensic investigations.
 trinadh465/platform_art_cve-2021-0394
Analyzes and demonstrates the Android Runtime vulnerability CVE-2021-0394, providing code-level insights for security researchers and developers.
 ideaslocas/adll
Automated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…
 valeriot30/cve-2024-3094
A XZ backdoor vulnerability explained in details
 thunderstrike9090/conflicker_analysis_scripts
Scripts to analyze conflicker worm which exploits famous netapi vulnerability (CVE-2008-4250) i.e MS08-067