
WPAxFuzz
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
exploitationfuzzingvulnerability-analysis+2
efchatz/wpaxfuzzA full-featured open-source Wi-Fi fuzzer
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
 alt3kx/cve-2023-24055_poc
CVE-2023-24055 PoC (KeePass 2.5x)
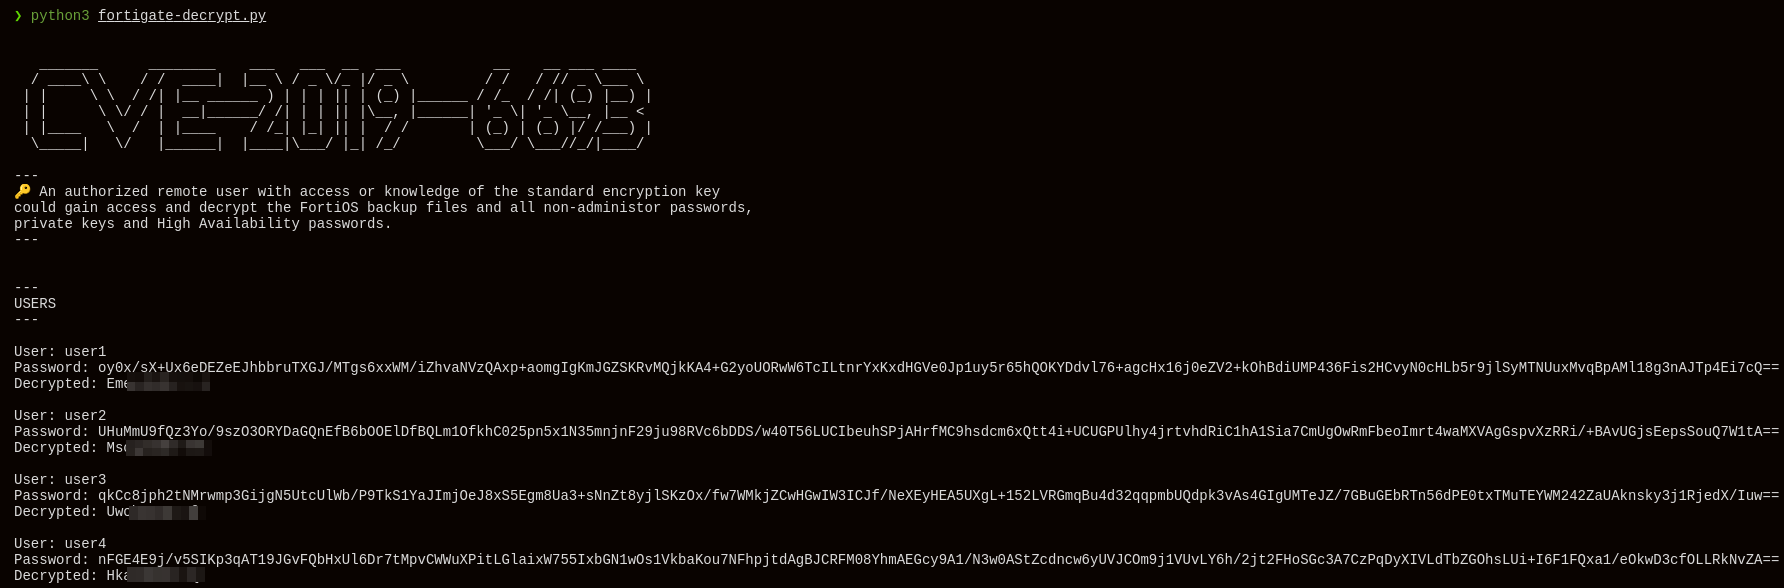 saladandonionrings/cve-2019-6693
An authorized remote user with access or knowledge of the standard encryption key can gain access and decrypt the FortiOS backup files and all…
 und3sc0n0c1d0/bruteforce-to-keepass
This script complements the results obtained through the keepass-password-dumper tool when exploiting the CVE-2023-32784 vulnerability affecting…
 s0c5/remotepasswordwifi
Script in Ruby. Break Remote router wifi passwords.
 ghcohu/decrypt-passwords-for-huawei-routers-and-switches-cve-2012-4960
Decrypts Huawei router and switch passwords using DES ECB mode, exploiting CVE-2012-4960 weak encryption. Python script for password recovery from…
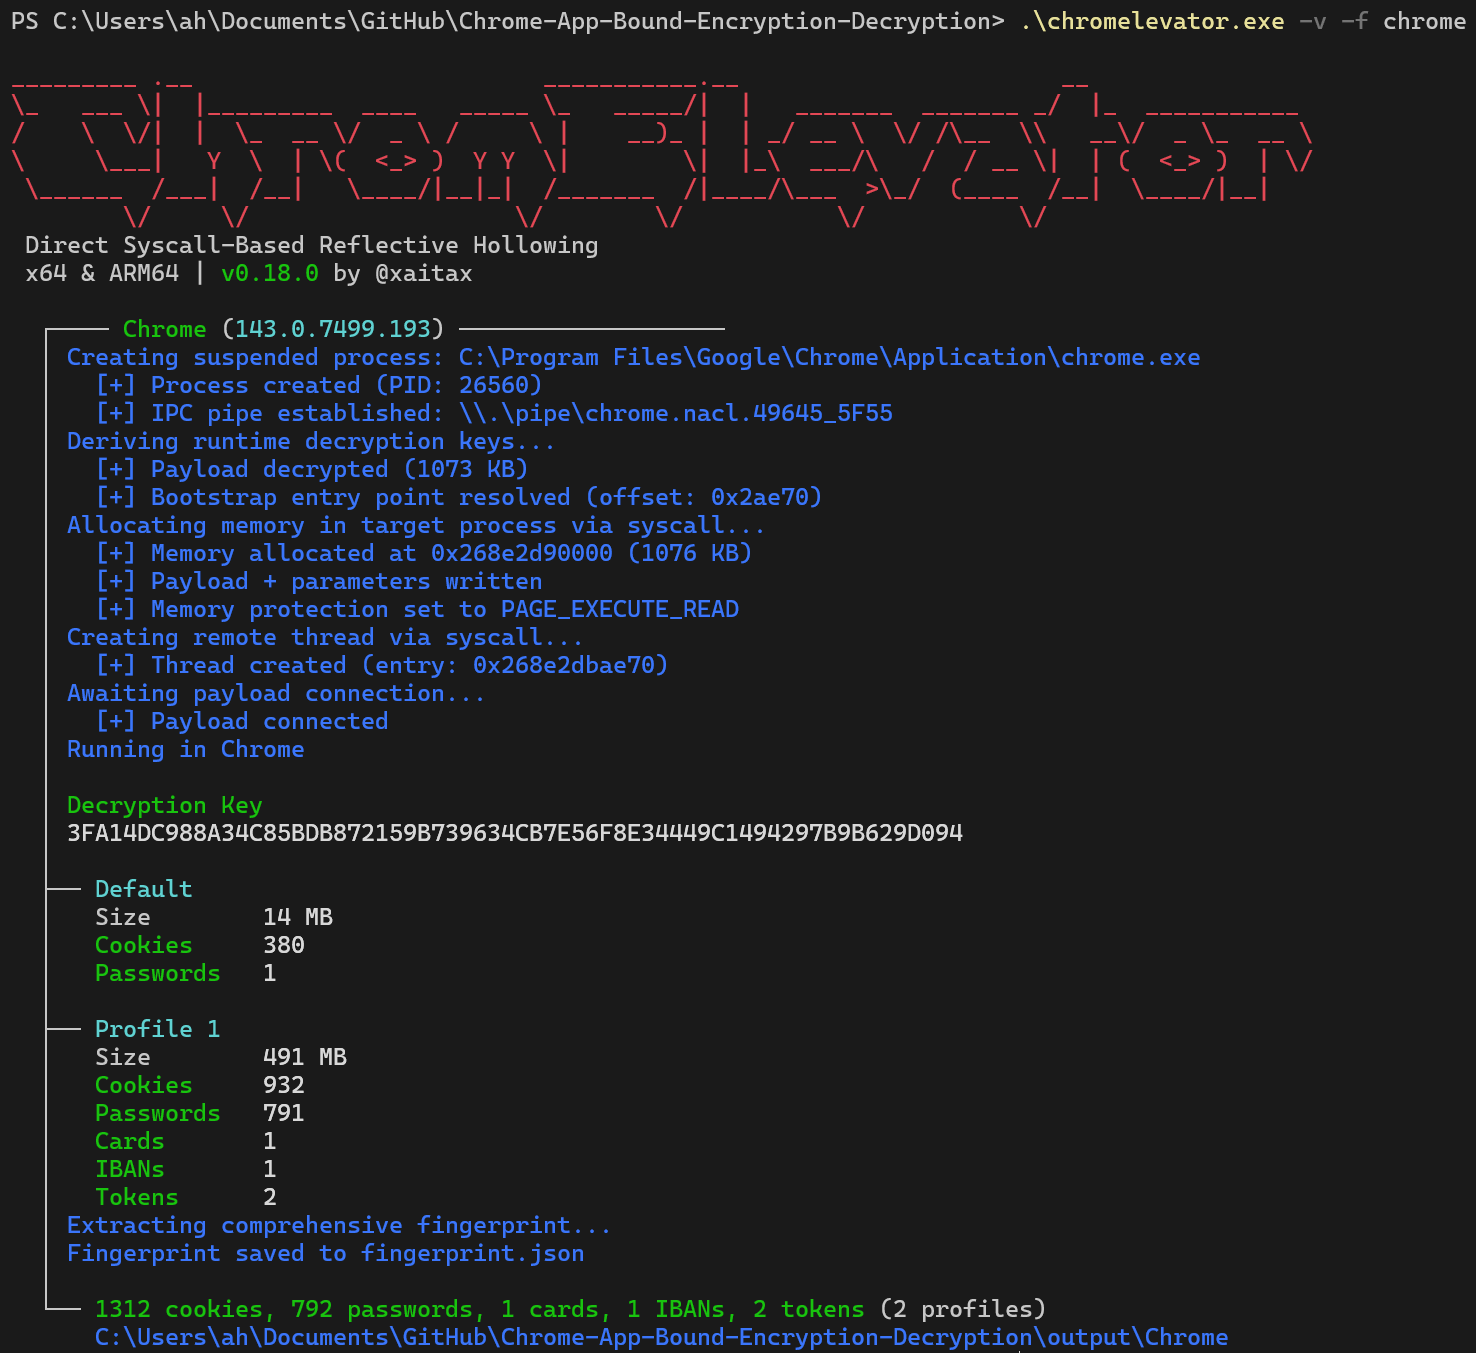 xaitax/chrome-app-bound-encryption-decryption
Bypass Chromium's App-Bound Encryption via Direct Syscall-based Reflective Process Hollowing. Extract cookies, passwords, payment methods & tokens…
 jas502n/grafana-cve-2021-43798
Grafana Unauthorized arbitrary file reading vulnerability
 hacker30468/mikrotik-router-hack
Proof-of-concept exploit for CVE-2018-14847 (MikroTik WinBox vulnerability) enabling arbitrary file read and plaintext password extraction via TCP/IP…
 reidmefirst/moxapass
Small script to retrieve passwords from many types of Moxa device, including NPort, OnCell, MGate, etc.
 b4shfire/stegcrack
Exploit script for CVE-2021-27211
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
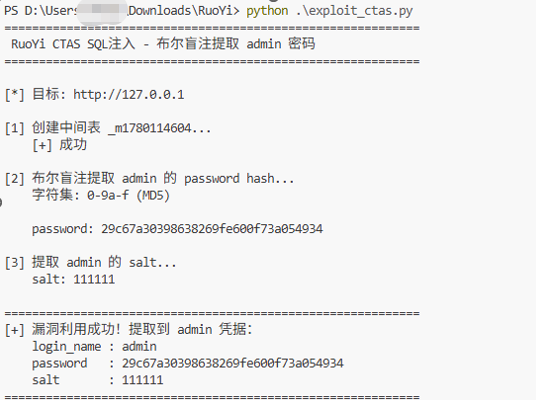 chinesespeople/cve-2026-52614
There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3