

qyvora-toha3ee
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
exploitationnetwork-securityosint+9
4
qyvora/qyvora-toha3eeGo-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
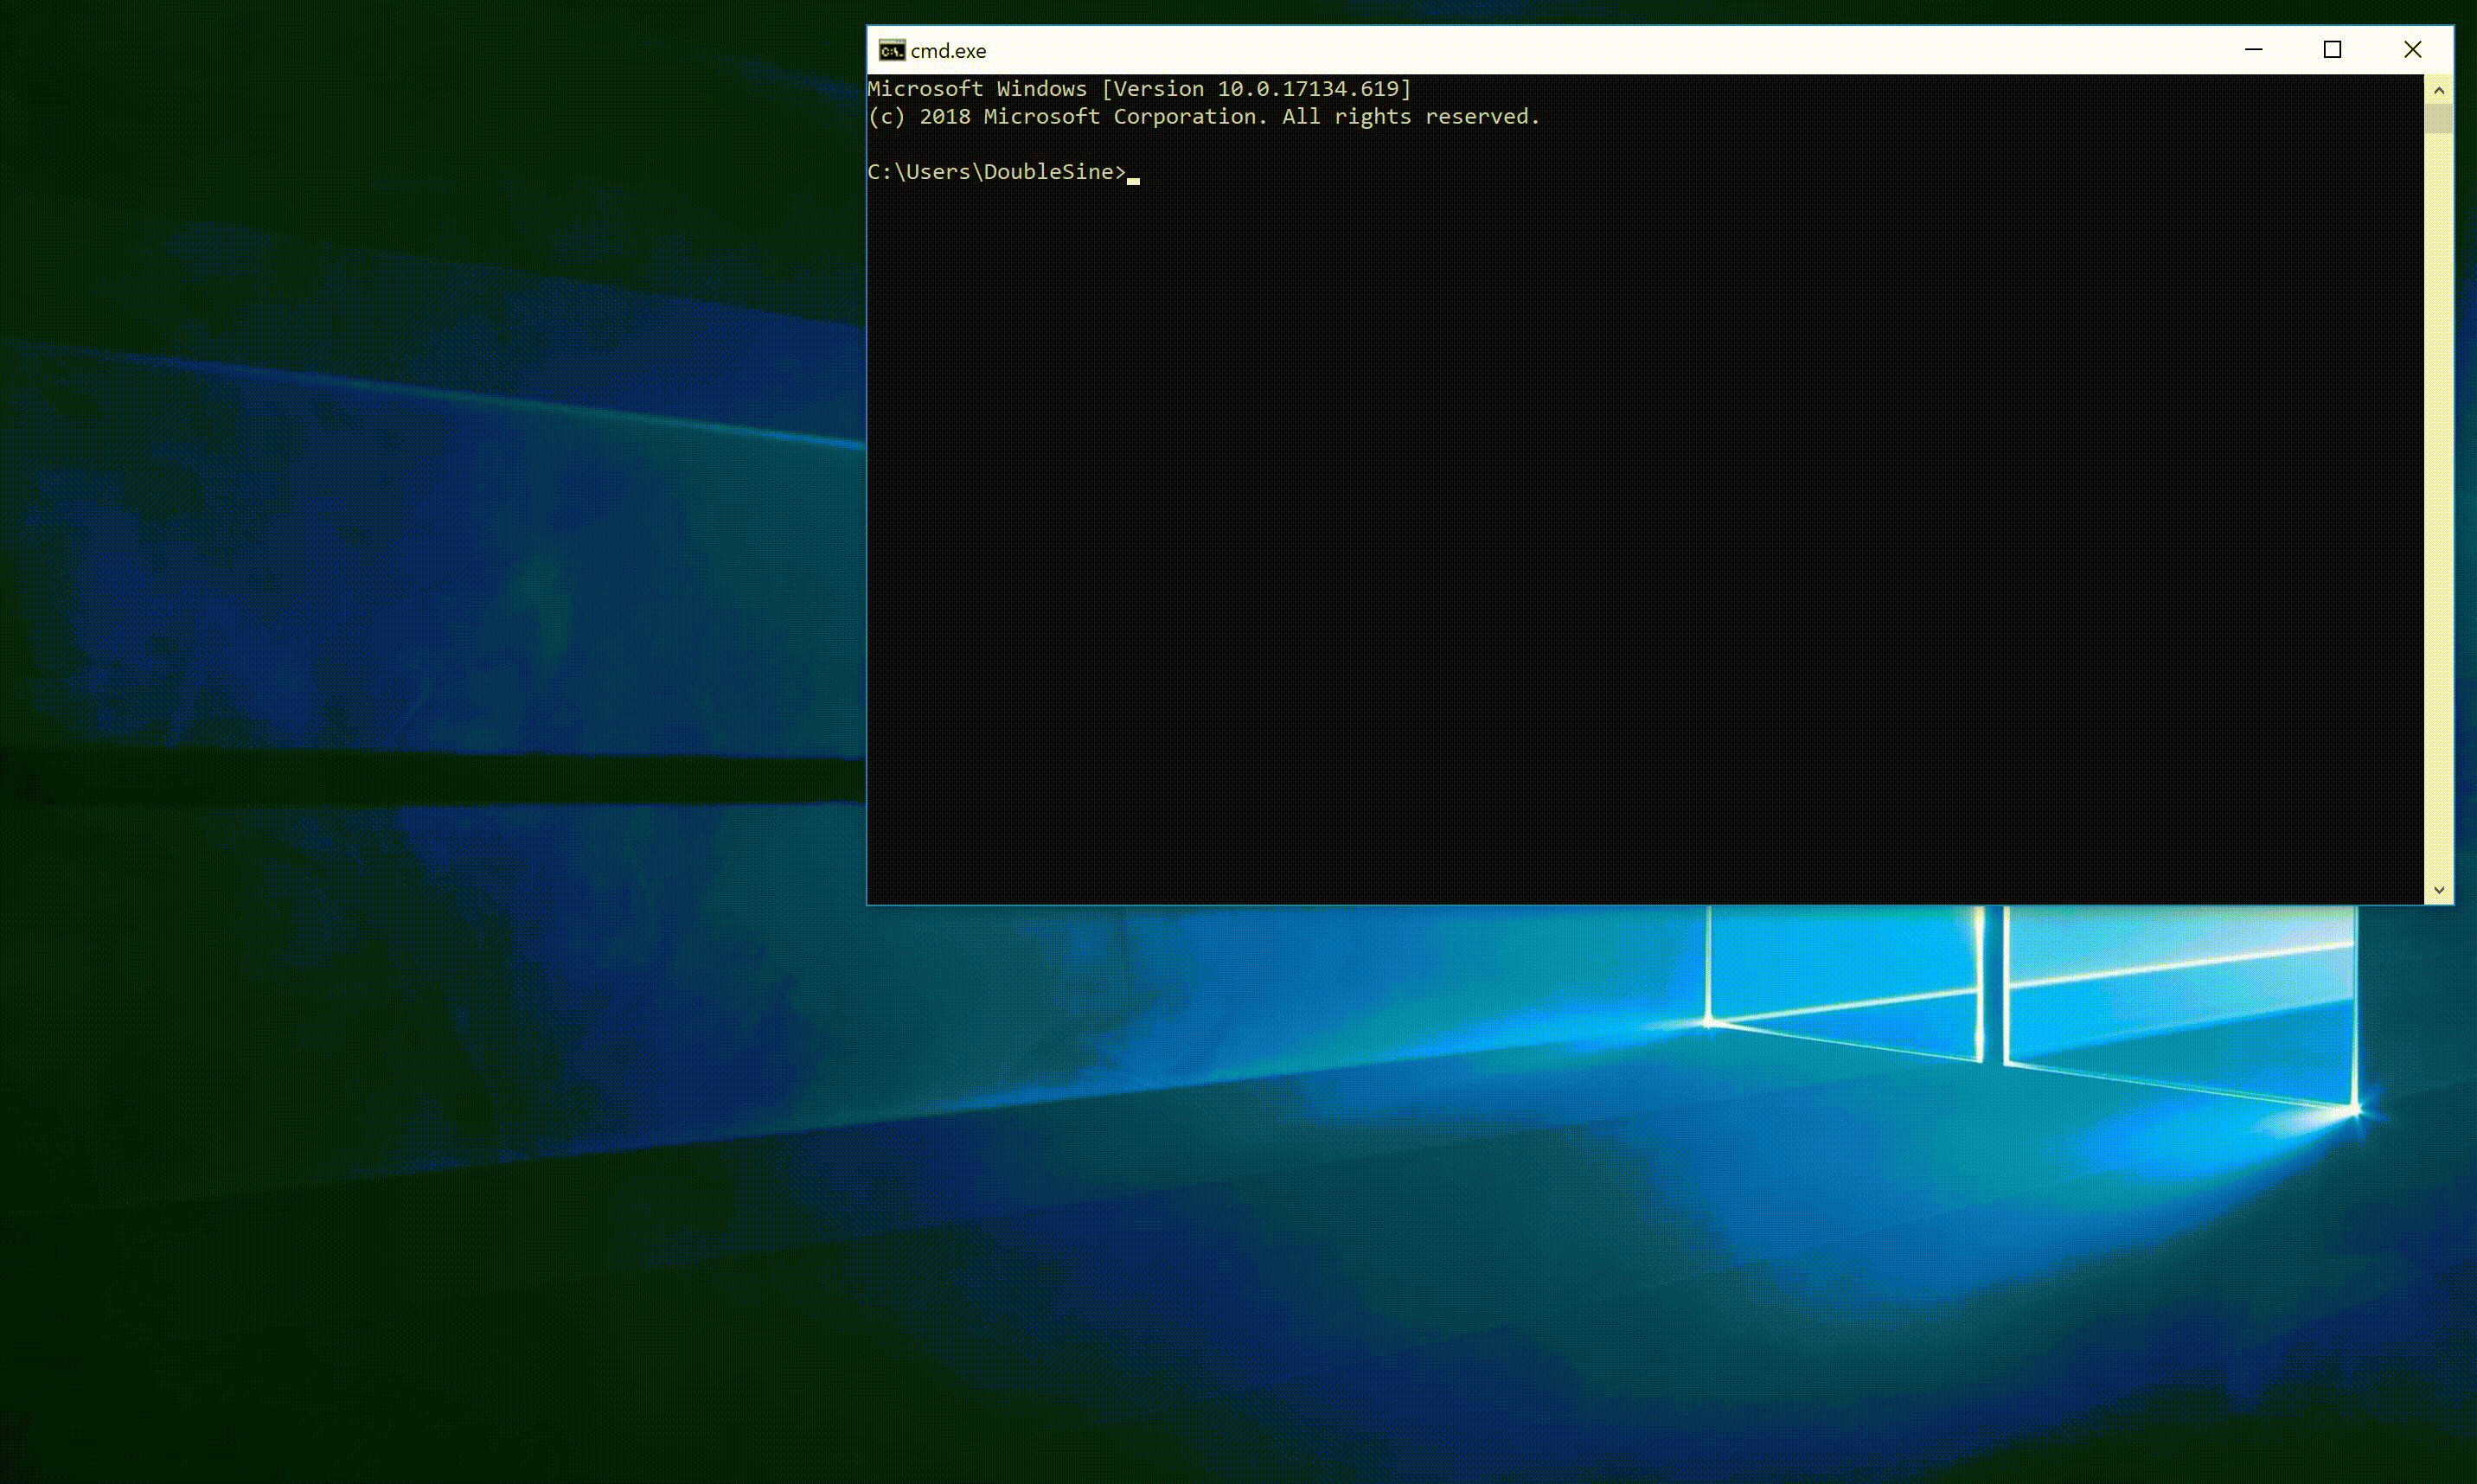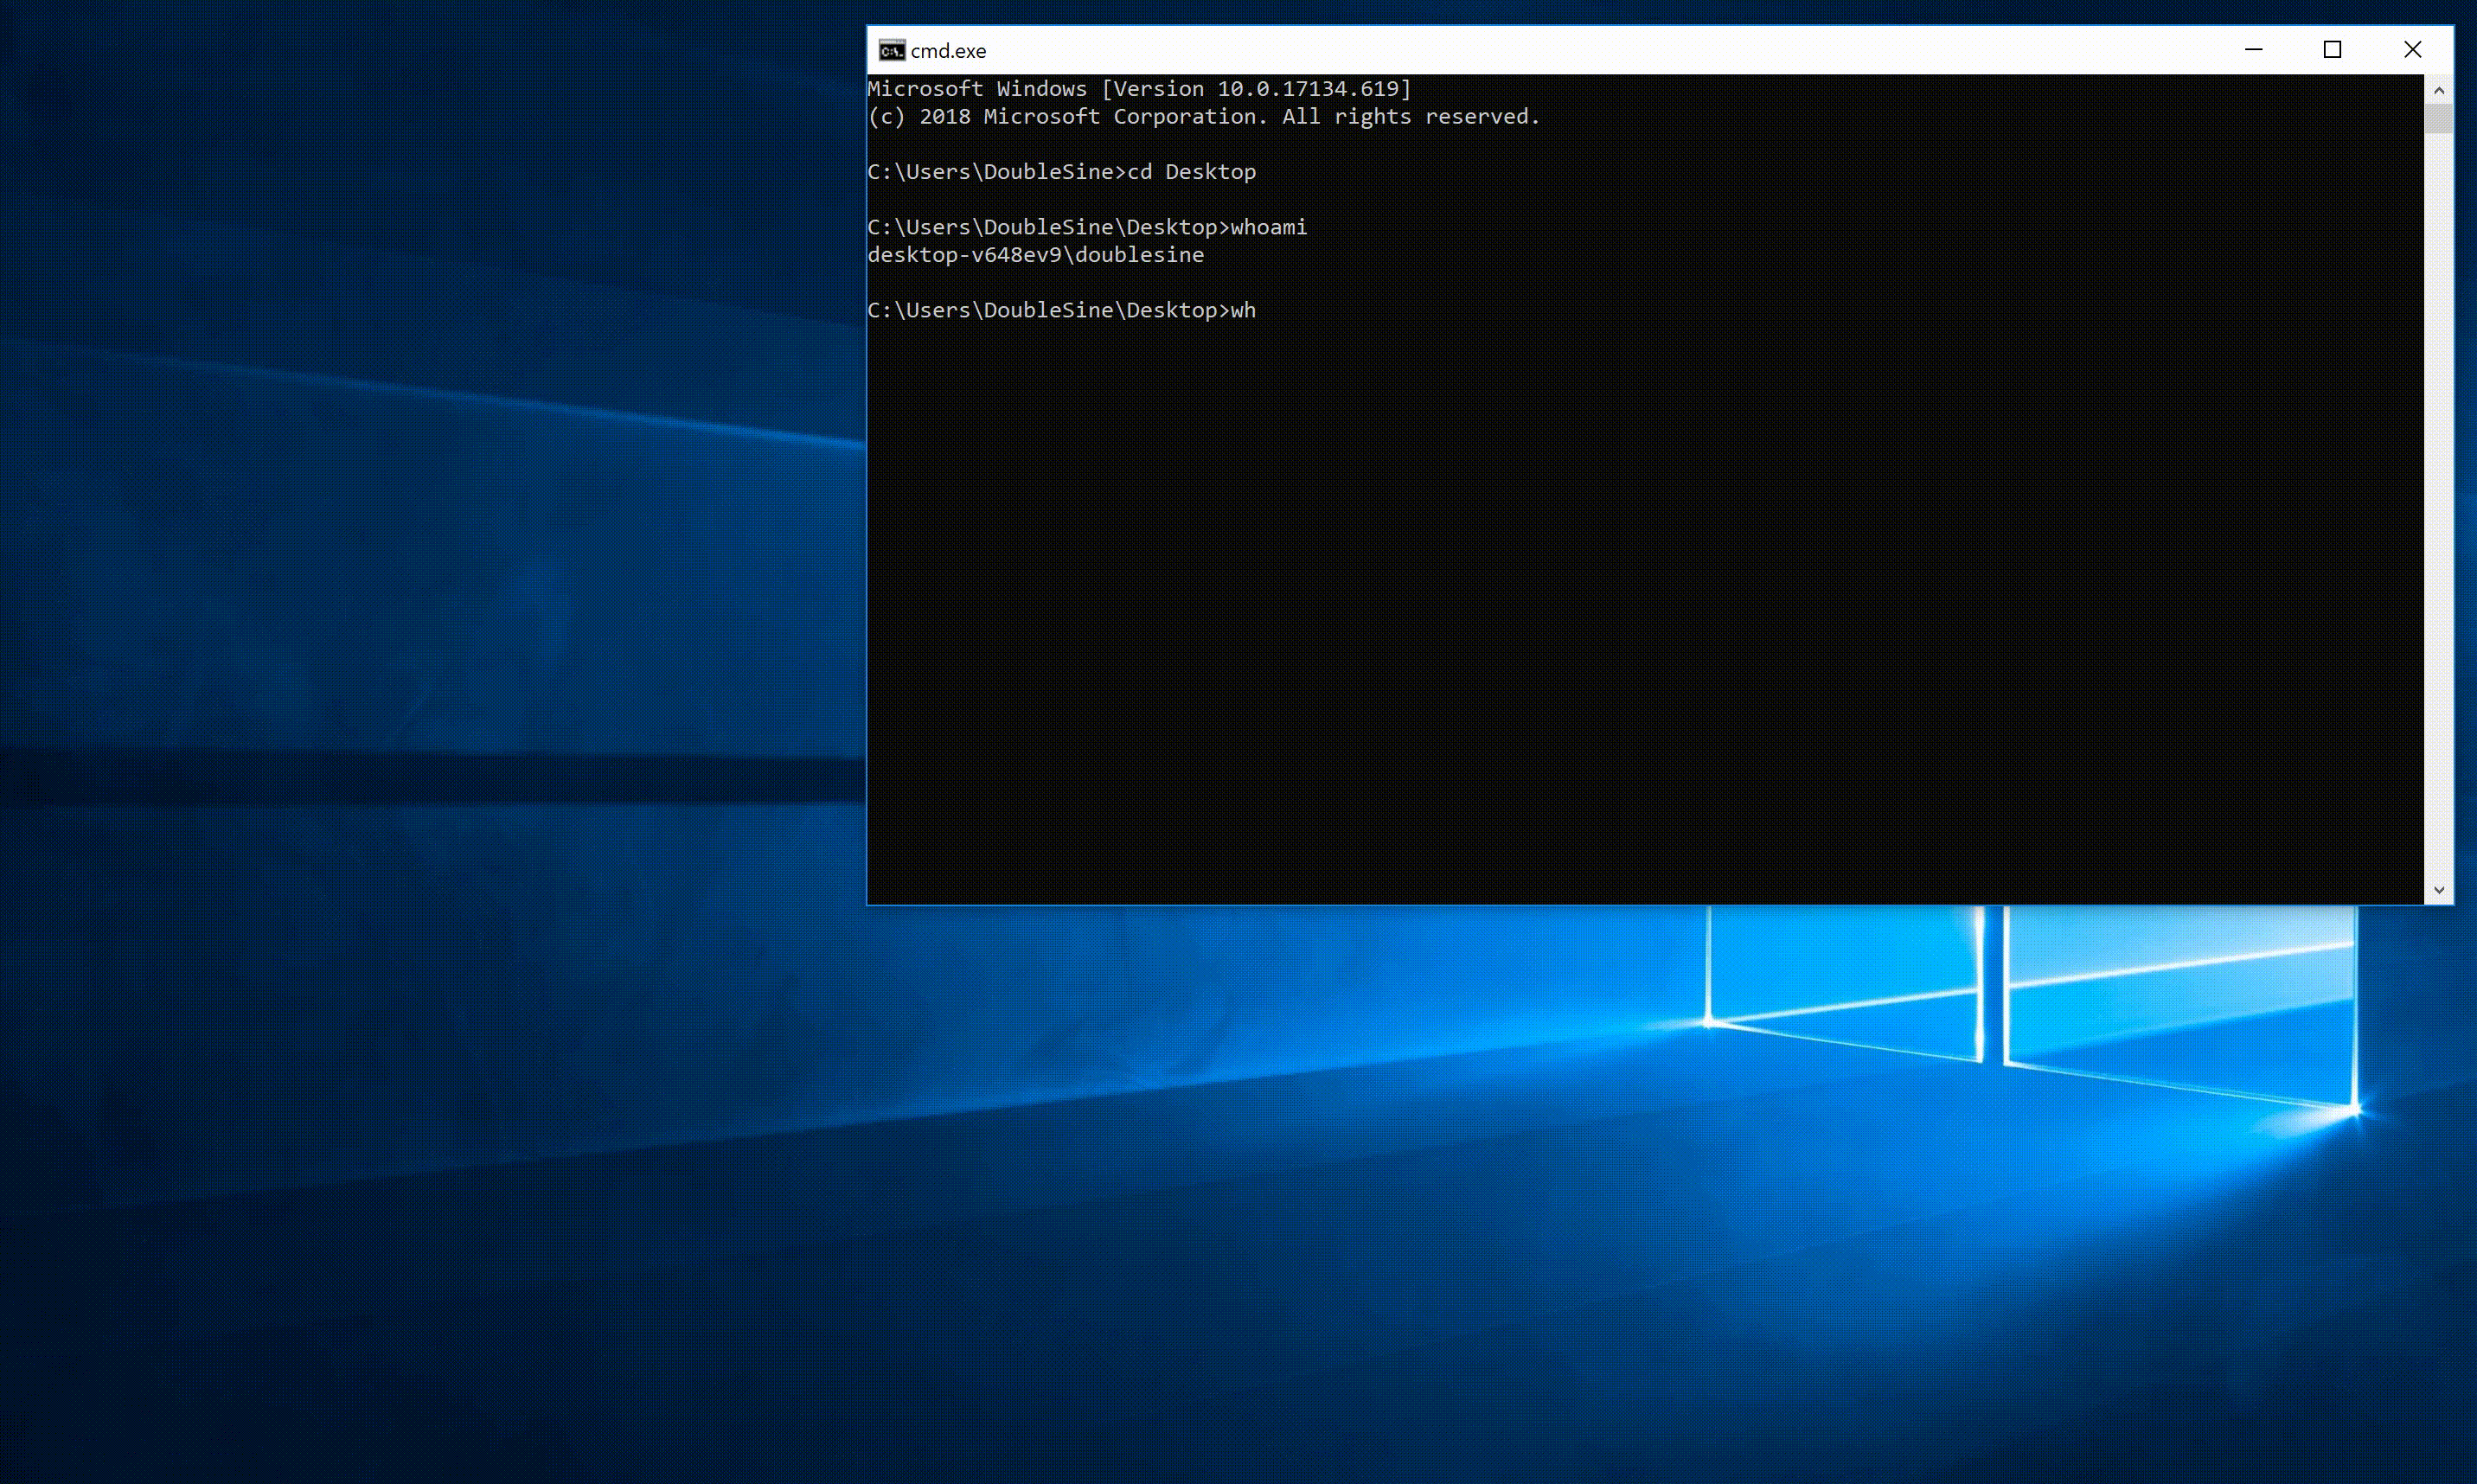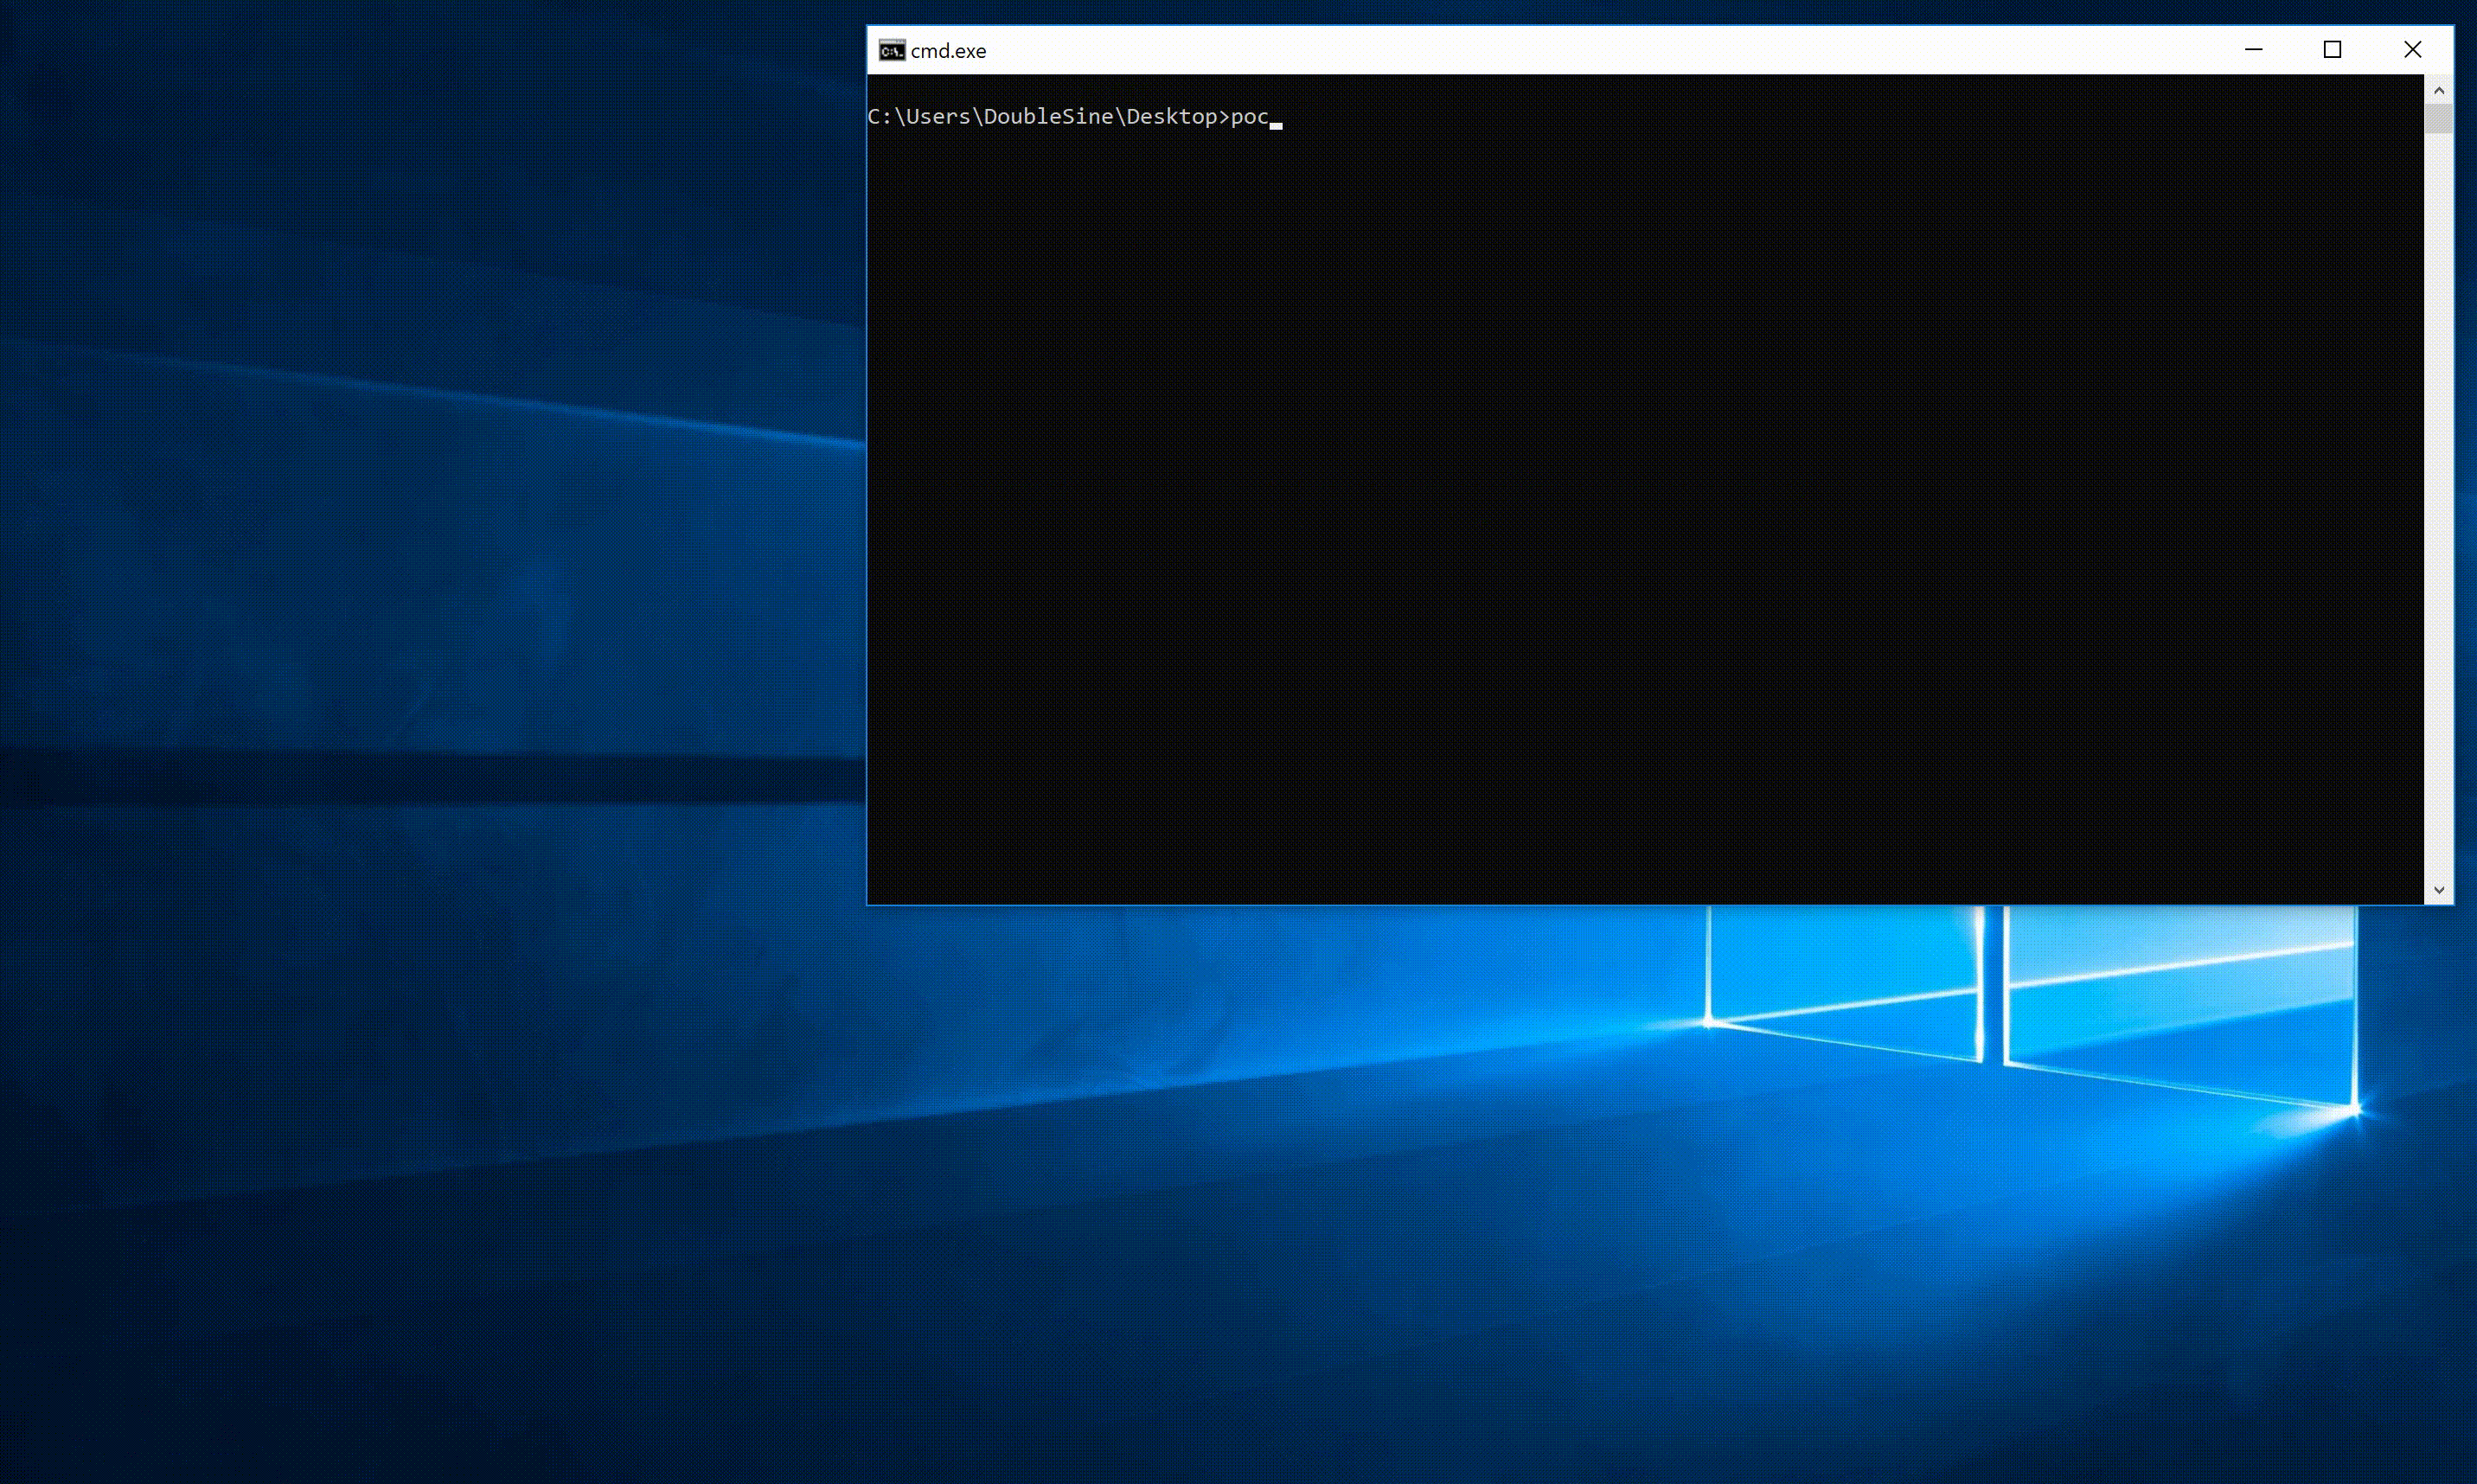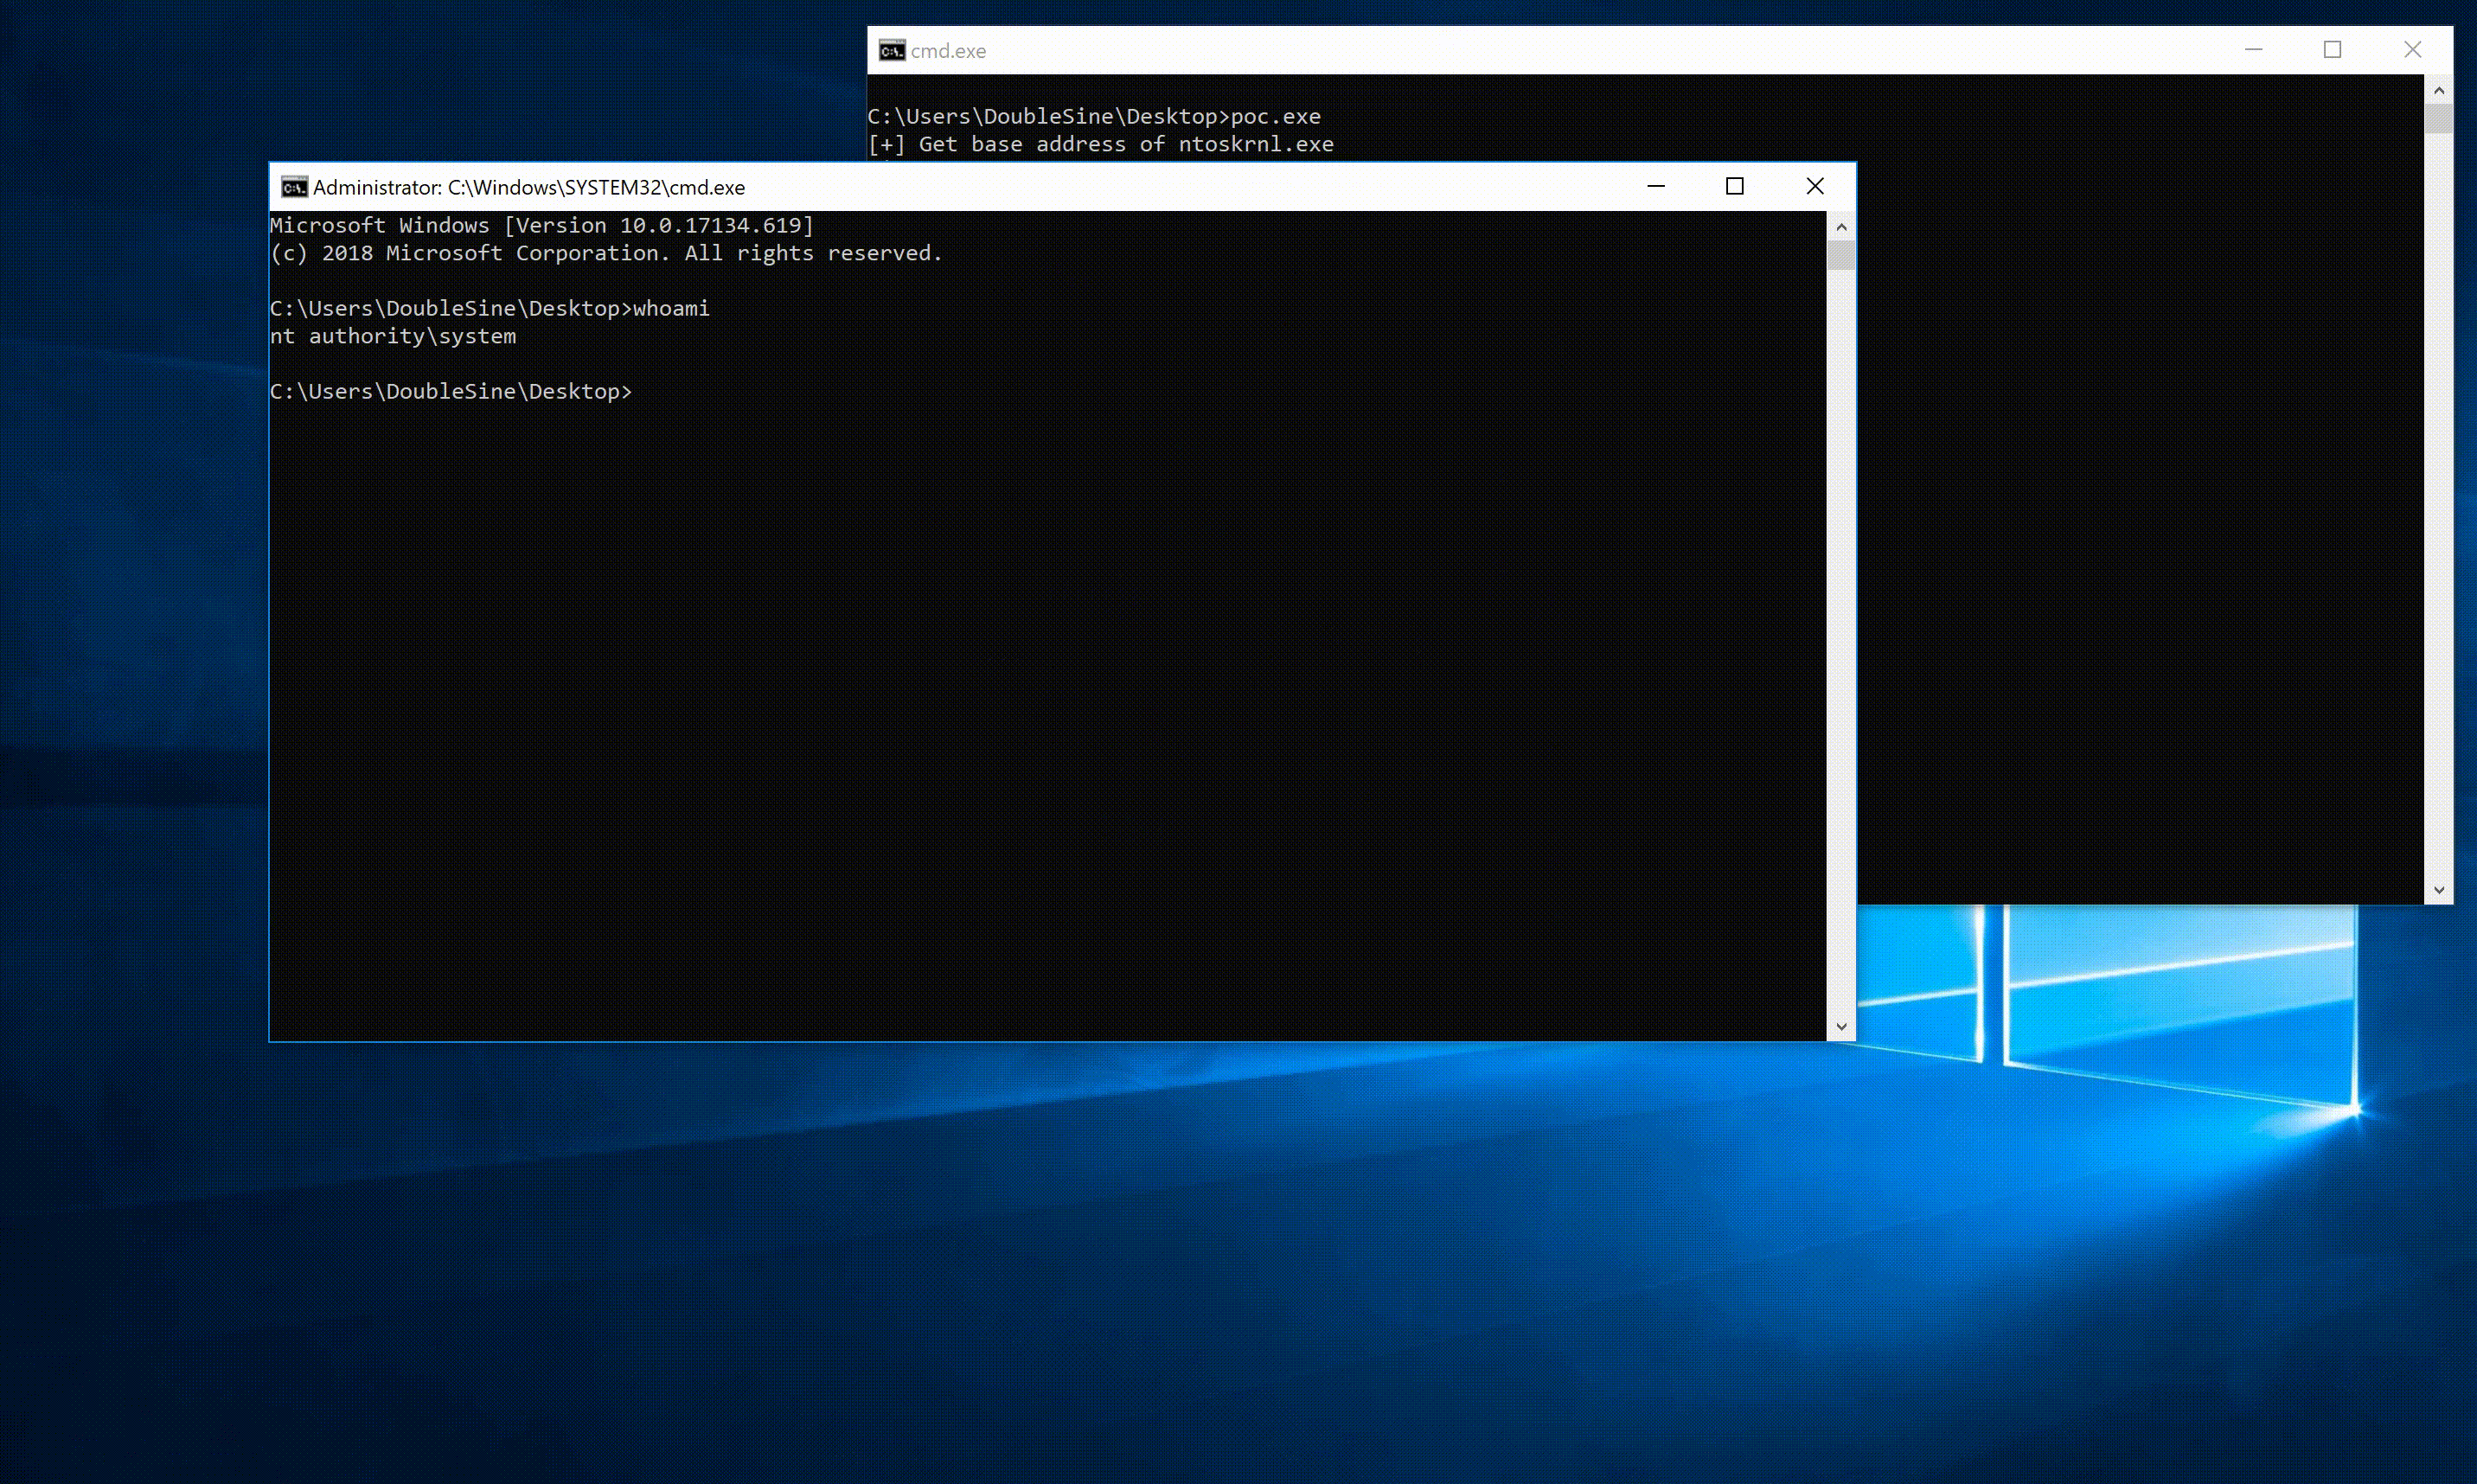 hypersine/sdokeycrypt-sys-local-privilege-elevation
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
 giardinas-dev/audit-xss-cve-2020-7934
Docker-based XSS exploit for CVE-2020-7934 targeting Liferay portal. Demonstrates stored cross-site scripting via user profile fields to steal admin…
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
 ajmal101/cve-2024-57175
Stored XSS proof-of-concept for PHPGURUKUL Online Birth Certificate System v1.0, demonstrating authenticated JavaScript injection via profile name…
 yasinyilmaz/vuln-chm-hijack
Potential malicious code execution via CHM hijacking (CVE-2019-9896)
 t6x/reaver-wps-fork-t6x
Brute-force attack tool against WPS registrar PINs to recover WPA/WPA2 passphrases, supporting online brute force and offline Pixie Dust attacks on…
 0xdeku/cve-2021-42666
CVE-2021-42666 - SQL Injection vulnerability in the Engineers online portal system.
 crussella0129/tricorne
a Fedora remix focused on pentesting and purple hat tooling
 morzan6/cve-2026-77276-poc
CVE-2026-77276 pre-auth macro RCE via convert-to on Collabora Online
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 0xdeku/cve-2021-42667
CVE-2021-42667 - SQL Injection vulnerability in the Online event booking and reservation system.
 ashemery/exploitation-course
Offensive Software Exploitation Course
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.
 theexploiters/cve-2024-27115-exploit
Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)
 akhlak2511/cve-2024-50970
Proof-of-concept demonstrating time-based SQL injection in Itsourcecode Online Furniture Shopping Project 1.0 via the id parameter in orderview1.php,…
 m4xiq/cve-2025-51970
SQL Injection in Online Shopping System Advanced (CVE-2025-51970)