

SSTImap
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
code-analysiscommand-and-controldynamic-code-analysis+6
vladko312/sstimapAutomatic SSTI detection tool with interactive interface
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
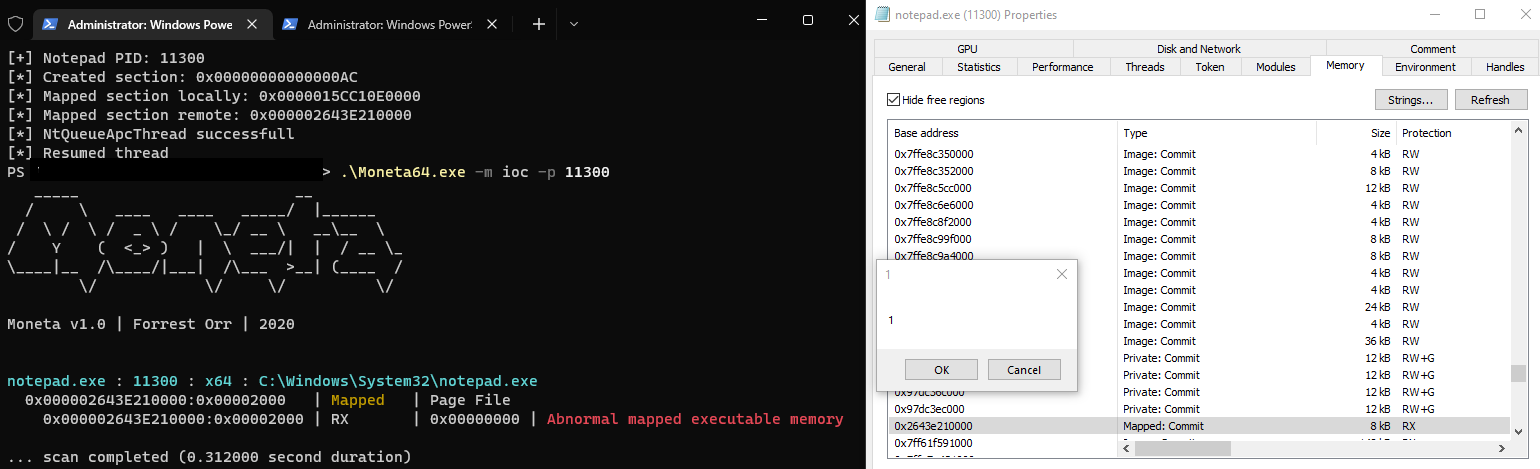 theflink/deepsleep
A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
 hoav18/cve-2021-22941
Python exploit for CVE-2021-22941 targeting Citrix ShareFile RCE with shell and ping options for remote command execution and network probing.
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 thiasap/oppo-pgem10-ghostlock
OPPO Find X6 Pro GhostLock (CVE-2026-43499) exploit adaptation
 laliea/cve-2021-46398
A Proof of Concept for the CVE-2021-46398 flaw exploitation
 blacksnufkin/credshunter
PoC for CVE-2026-3609 - XIGNCODE3 xhunter1.sys handle leak enabling PPL bypass and LSASS dumping
 learningdisordercapital35/cve_2025_24257----not-mine
Demonstrate CVE-2025-24257 with a public PoC for IOGPUFamily kernel heap OOB read/write and panic analysis
 0linear/cve-2026-62958
Proof-of-concept for CVE-2026-62958: crafts a malformed ELF to trigger an out-of-bounds read in Libriscv and crash the sandbox with SIGSEGV.
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
 delsploit/cve-2022-2078
Proof-of-concept exploit for CVE-2022-2078 demonstrating kernel memory leak via buffer manipulation, with leaked kernel address disclosure.
 ngtuonghung/cve-2021-3156
POC for CVE-2021-3156 - Heap-based buffer overflow in sudo
 0xblackash/cve-2026-23111
CVE-2026-23111
 0vercl0k/cve-2021-32537
PoC for CVE-2021-32537: an out-of-bounds memory access that leads to pool corruption in the Windows kernel.
 kosmicowl045/ict287-cve-2022-42889
Setup and exploit recreation for CVE-2022-42889 Text4Shell.
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 fixyourface/springbreakpoc
PoC for SpringBreak (CVE-2017-8046)